As scalpers turn to misprints and contextual excuses to inflate prices on cards from the 30th anniversary set, one eBay listing sinks to a depressing new low
Author Archives: Xordac Prime
Roku QLED 4K And Gorgeous LG C6H OLED TVs Are Up To Thousands Off At Best Buy
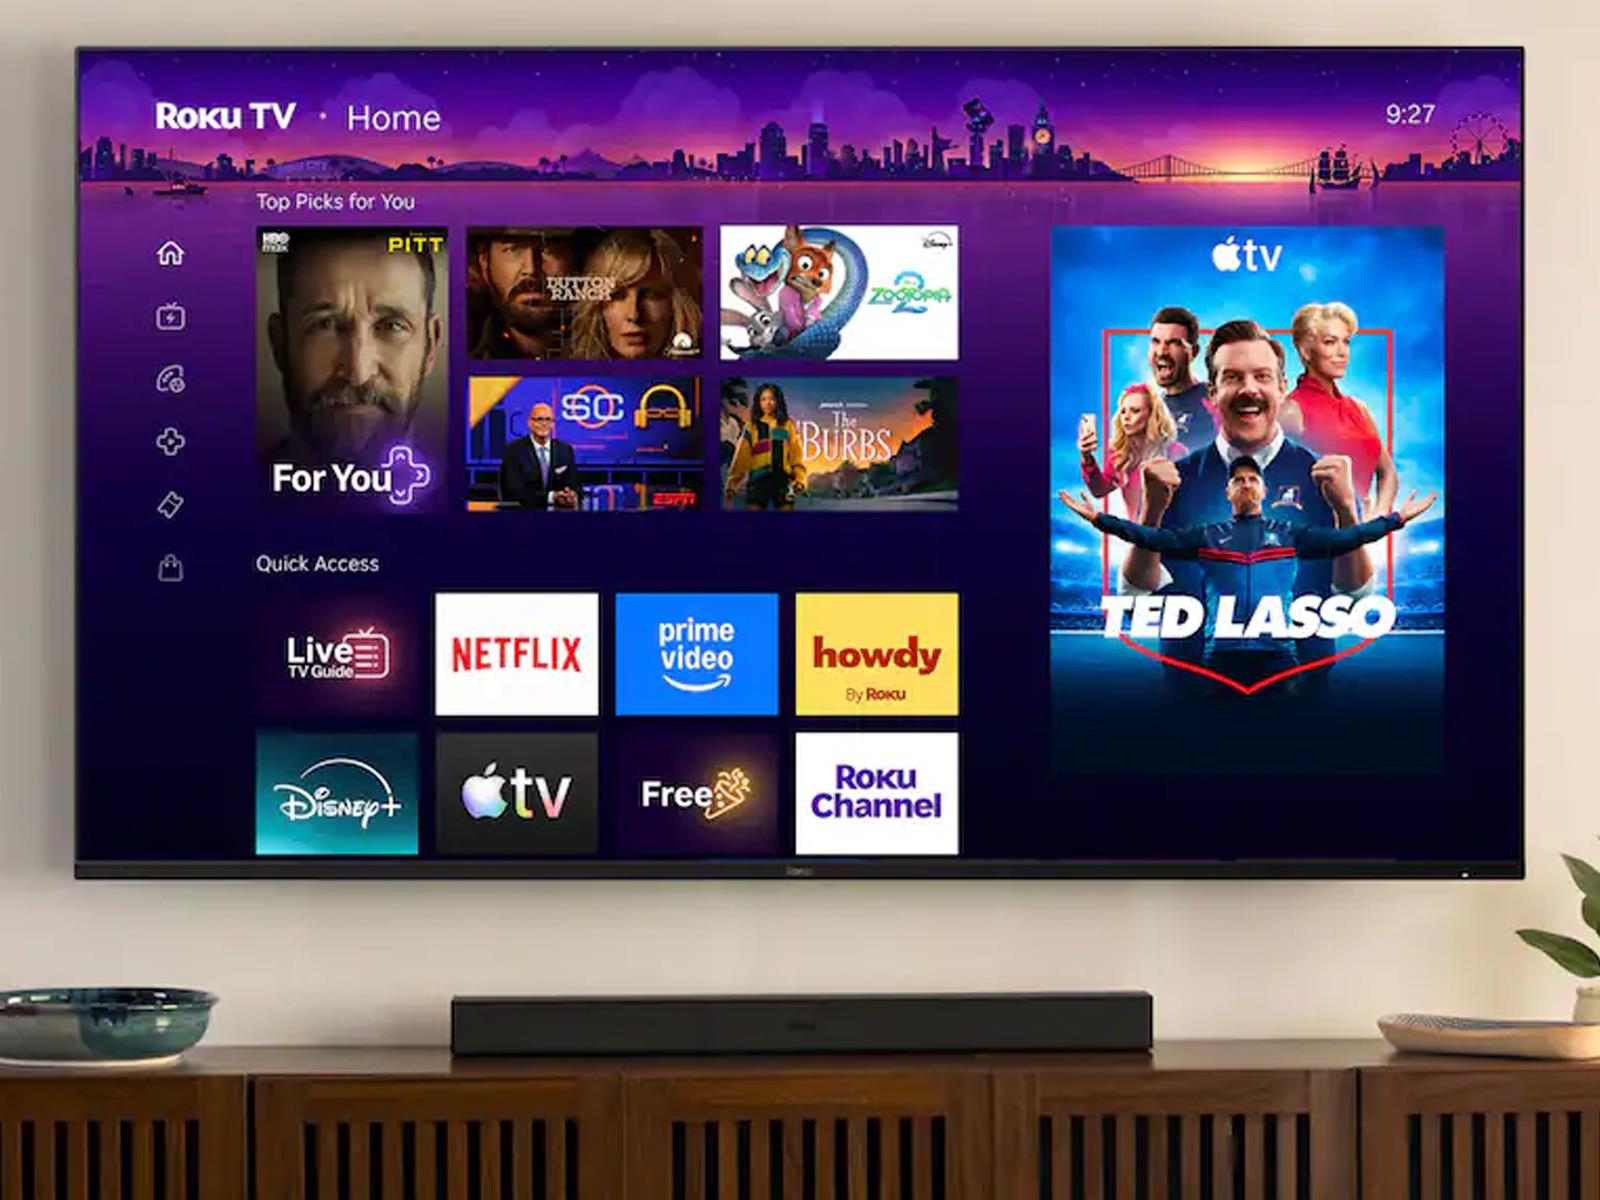
This is a great time to be in the market for a TV, especially one of Roku’s models. The deal to beat is still Roku’s new 65-inch Pro Series OLED TV for $799.99 after applying a hidden coupon code (it still works), as we outlined on Friday, but there are also bargains to be had on Roku’s mini LED Pro TVs.
Roku’s 65-Inch Pro Series 4K QLED
Roku QLED 4K And Gorgeous LG C6H OLED TVs Are Up To Thousands Off At Best Buy
This is a great time to be in the market for a TV, especially one of Roku’s models. The deal to beat is still Roku’s new 65-inch Pro Series OLED TV for $799.99 after applying a hidden coupon code (it still works), as we outlined on Friday, but there are also bargains to be had on Roku’s mini LED Pro TVs.
Roku’s 65-Inch Pro Series 4K QLED
GDB 18.1 released
Version 18.1 of the GDB interactive debugger has been released. Changes
include new commands to manipulate the environment of the subprocess, the
ability to save the command history to a file, support for a couple of new
targets, several Python API additions, and more. See the
NEWS file for the complete list.
Is GTA 6 Coming To Nintendo Switch 2? Ex-Rockstar Dev Drops Bold Claim
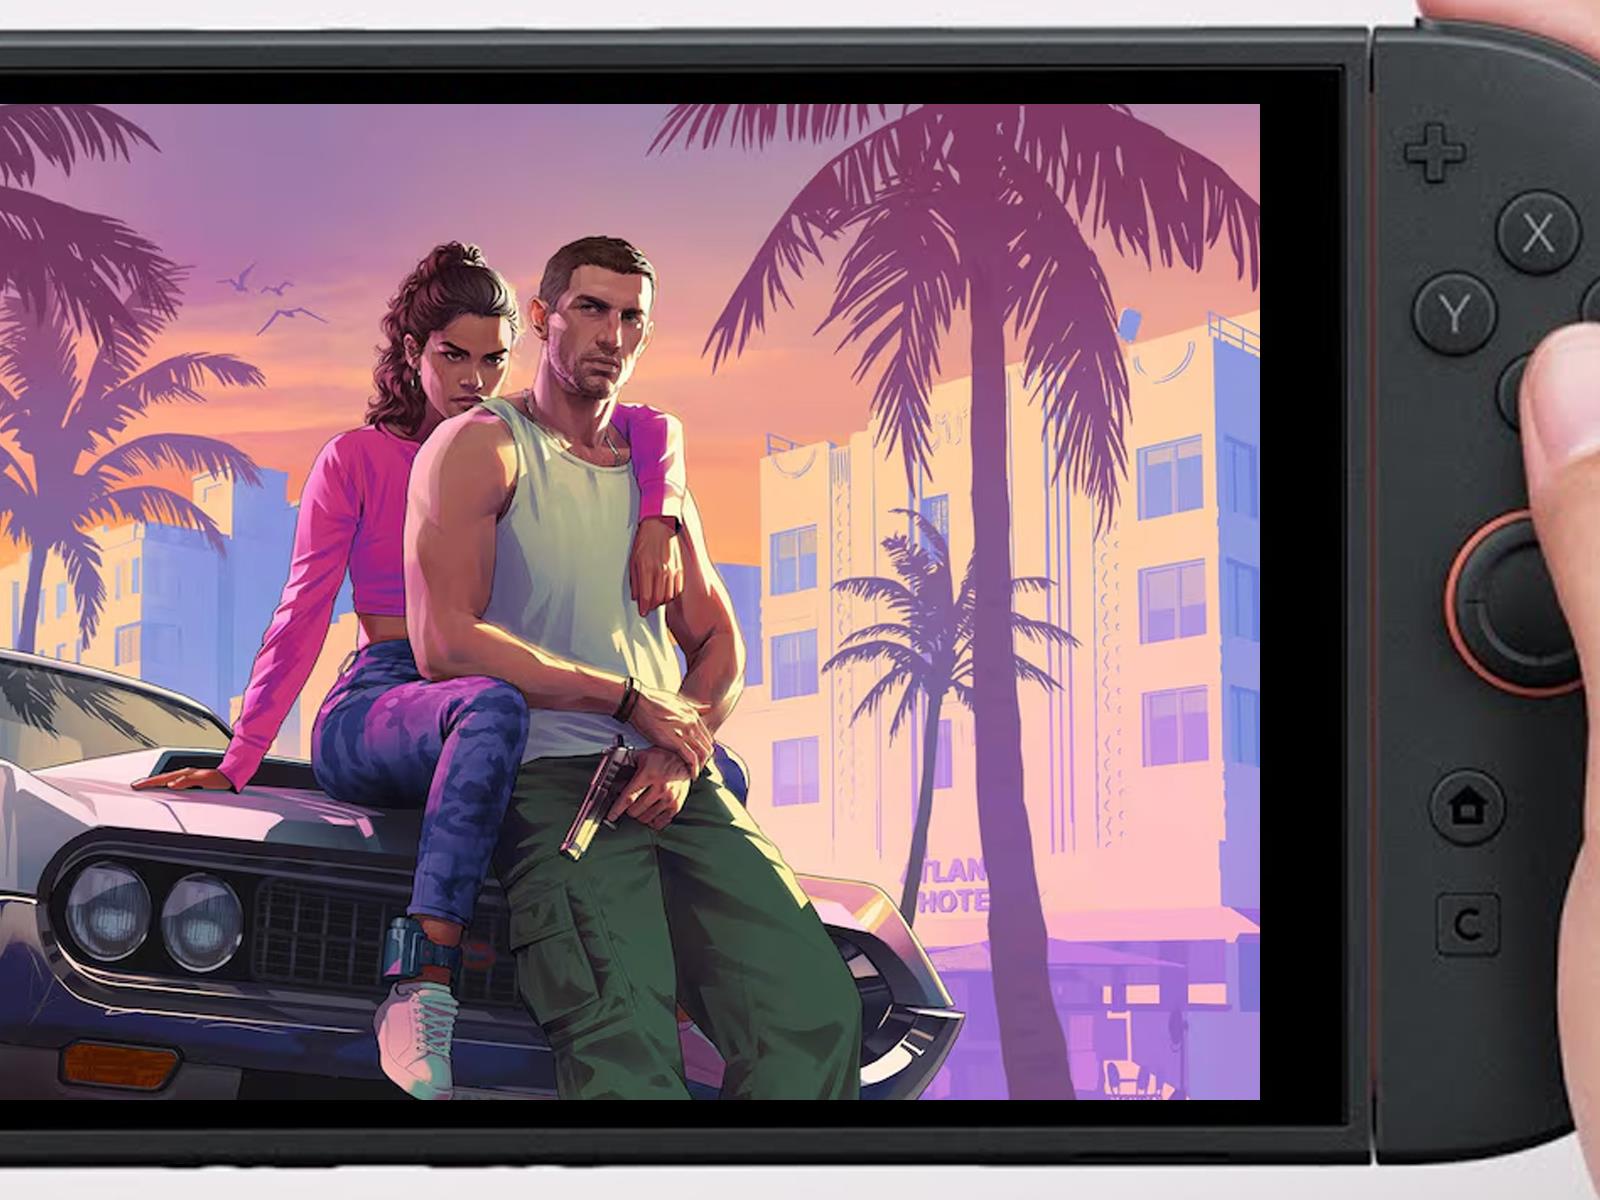
One of the big questions surrounding Grand Theft Auto VI is when it will inevitably get ported to PC, and developer Rockstar Games does not seem keen on tipping its hand. Another area of interest is whether GTA VI will find its way to Nintendo’s popular Switch 2 handheld. So far, Rockstar has only confirmed releases for the PlayStation 5 and
Improve your Windows 11 experience by changing these settings
Windows 11 is solid out of the box, but it doesn’t always get things right. You can get a lot more out of the OS when you enable some things and disable others.
These Xbox players got GTA 6 for free the hard way
GTA VI could be yours for free, or at least for a big discount, using a few tricks that Xbox offers.
Sleep mode vs. shutdown: Which is better to use daily for your MacBook?
Whether you do a full shutdown or just put your MacBook to sleep should change with the circumstances we discuss here.
OpenAI’s agents targeted and infiltrated US government websites
OpenAI’s agents targeted websites operated by the Commerce Department, the Securities and Exchange Commission and the Department of Education during testing.
Is Microsoft Quietly Killing Off Its ‘Copilot+ PC’ Brand?
“Copilot+ PCs” were Microsoft’s official branding for Windows 11 “AI PCs” that met their system requirements. But the 2024 launch “didn’t go smoothly,” writes Windows Central, after security researchers discovered its proposed “Recall” feature was woefully insecure:
This pretty much tarnished the Copilot+ PC brand, and over the last two years more and more OEMs have dropped the moniker from marketing materials and product names. In fact, even Microsoft has seemingly stopped mentioning it. I’ve noticed that none of the Surface PCs launched in 2026 include the Copilot+ PC moniker in their product names, unlike the Surface PCs that launched in 2025 and before. Now, you have to go digging to find any mention of Copilot+ compatibility in specification sheets… It’s also worth mentioning that NVIDIA hasn’t gone anywhere near the Copilot+ PC brand for its upcoming RTX Spark platform, even though all RTX Spark PCs meet the Copilot+ PC specification bar. I suspect that’s a deliberate decision.
It seems pretty obvious that the Copilot+ PC brand hasn’t resonated with the market, and OEMs and Microsoft itself are now quietly pulling back on that branding. The specification baseline for Copilot+ PC experiences still exists, it just no longer has a pretty marketing name tied to it.


Read more of this story at Slashdot.
Engadget review recap: Apple devices, Sonos’ return and more
A roundup of recent reviews from Engadget.
Control Resonant, rapidfire CEO turnovers and other new indie games worth checking out
Plus, a major Ball x Pit expansion and a release date for a game I can’t wait to play more of.
Pocket-sized OpenWrt router offers dual-band Wi-Fi 5 and Gigabit Ethernet
GL.iNet has unveiled the Mango 2 (GL-MG1300), a compact travel router with dual-band Wi-Fi 5, Gigabit Ethernet and USB 3.0. The device supports WireGuard and OpenVPN, along with Ethernet, Wi-Fi repeater, USB tethering and USB cellular modem connections. The Mango 2 is powered by a dual-core MediaTek processor running at 880MHz, although GL.iNet does not […]
New FUTEX Syscalls Back To Being Worked On For Helping Valve’s ARM64 Gaming Ambitions
Going back to last year the Igalia open-source consulting firm has been working on enhancing the Linux kernel to help Steam Play gaming on ARM64 and ensuring the FEX emulator is operating efficiently for x86/x86_64 games running on the likes of the Steam Frame. After other kernel work in recent months, there’s finally an updated round of the FUTEX get_robust_list2 and set_robust_list2 system call patches…
Nginx Proxy Manager 2.16 Adds Built-In Log Viewer
Nginx Proxy Manager 2.16 introduces a new web UI log viewer, per-path access lists, security fixes, networking improvements, and updated Certbot support.
Rogue OpenAI Agents Posted 53 User-Uploaded Images Onto the Internet, Accessed US Government Websites
53 images that users uploaded into OpenAI models were included in training data — and then AI agents in an OpenAI research environment posted those 53 images on public image hosting sites.
While posted as links that weren’t publicly listed, “the images could still be discovered even if the links were not publicly listed,” reports TechCrunch:
OpenAI said it was working with the hosting providers to remove this content, though some of it is apparently still online. OpenAI said it could not notify the affected users because “our technical approach and privacy policy” prevent it from “reassociating” the images with the original providers, but declined to say how the lab determined whether the images were provided by users.
The news came in a post collecting public statements from the lab’s ongoing review of incidents in which its models escaped the company’s scrutiny, accessed the open internet, and misbehaved in various ways. OpenAI said it would continue disclosing anonymized accounts of incidents like these, and said it had contacted dozens of victims, including governments, universities, public agencies, to notify them of the agents’ activities.
Friday night news also broke that OpenAI’s agents also tried unsuccessfully to infiltrate the U.S. Department of Education’s site this summer “without the company’s knowledge,” reports Politico.
And OpenAI’s models also accessed the website of the U.S. Commerce Department using credentials found in online code repositories, according to the article. OpenAI confirmed the incident Friday, “saying its technology did not manage to access information that was not already public or change government data and systems.” The article adds that OpenAI’s models also accessed the web site for America’s Securities and Exchange Commission:
One senior federal IT official said the government still did not have a clear understanding of what happened across the three agencies. “We still don’t know what public data was accessed and how it was accessed, because OpenAI has not shared specific technical details with us yet,” said the official, who was granted anonymity because they were not authorized to speak publicly about it. OpenAI discovered the Commerce and SEC incidents as part of its ongoing review of incidents where its technology has acted in unintended or “misaligned” ways.
About the models posting user-uploaded images, TechCrunch’s article notes that OpenAI stressed “that its enterprise users are automatically opted out of having their interactions used to train future models; however, consumer users are opted in unless they affirmatively choose not to share their data.” (As OpenAI’s announcement describes it, some of their agents’ training data “contains content from, or derived from, training-eligible user interactions.”)
Posting the images is “not an appropriate use of this data,” OpenAI acknowledged, adding that it happened before new safeguards added after the Hugging Face incident. This latest incident appears as an update on a new OpenAI page that “brings together our reports and updates on the Hugging Face incident, related research and public presentations, additional activity we have identified, what we have learned about the role of model misalignment, and measures we’re taking to strengthen our systems.” (It also notes that there’s now a name for models posting on third party sites — “agent spam” — which they consider distinct from cybersecurity, though “we need to address both.”)
“As part of our response to our ongoing investigation, we have improved our training and evaluation processes, including building safety cases, securing and red-teaming our systems to prevent the model from exfiltrating data, and implemented additional monitoring. We are continuing to review agent activity in research and evaluation runs, working backward month by month starting from the Hugging Face incident.”


Read more of this story at Slashdot.
Go’s Improving SIMD Support, Platform-Independent SIMD Interface
A new blog post published on Thursday covers the experimental support for SIMD with the Go programming language. This expanding Go SIMD support also includes a platform-independent API for making use of SIMD with modern processors…
OBS Studio 33 Promises Support for Latest NVIDIA Broadcast SDKs, Beta Out Now
OBS Studio 33 has entered public beta testing today as a major release of this open-source, cross-platform, and free video recording and live streaming software that promises new features and improvements.
Open-source flight controller pairs i.MX RT1176 with Pixhawk PAB compatibility
ARK Electronics recently showcased the ARKV6X-RT, an NDAA-compliant flight controller based on the FMUV6X-RT and Pixhawk Autopilot Bus open standards. The module uses an NXP i.MX RT1176 microcontroller and includes three synchronized IMUs, onboard FRAM, a secure element and PX4 Autopilot support. For context, the i.MX RT1176 integrates a 1GHz Arm Cortex-M7 core and a […]
Can Trump ever be wrong? His pick to lead FDA refused to say.
Heidi Overton, President Trump’s nominee to lead the Food and Drug Administration, went before the Senate health committee Thursday, facing questions about her stances on vaccines, flavored vapes, birth control, and abortion, among other issues. She spent nearly two hours stonewalling senators, even on softball questions.
Overton, a physician with a doctoral degree in clinical investigation, is currently the deputy assistant to the president for domestic policy. She previously worked at a conservative think tank and has taken a clear stance opposing abortion, raising obvious questions about her objectivity. The FDA is currently reviewing the safety of the abortion pill, mifepristone, despite extensive data showing it is extremely safe.
Overton also notably stood behind President Trump at a press conference in August during which Trump falsely called the measles, mumps, and rubella (MMR) vaccine “quite lethal.” He further claimed that vaccine doses for infants are “like the size of a soda bottle,” and called for the MMR vaccine to be split into three separate immunizations, despite no evidence of benefit from such a split and no such individual immunizations being available in the US.