
Between the evening of 12 November and the afternoon of 13 November 2026, Microsoft 365 services (Exchange Online, Outlook, Teams, Copilot) were unavailable or degraded in at least 70 countries for almost 24 hours. According to Microsoft, the cause was a network capacity upgrade, not a cyber attack. Public bodies
There’s One Thing I’ll Admit The Ocarina Of Time Remake Made Worse
Not every change is for the best
US now “comfortable” with children dying of measles as death toll hits 10
Health officials in Pennsylvania and Wisconsin announced two more measles deaths late last week, bringing the national tally of confirmed measles deaths this year to 10. The total includes the deaths of at least four infants: two in Pennsylvania, one in New York, and one in Wisconsin.
Wisconsin health officials said the latest measles death—the second for the state—was in a child. Pennsylvania’s health department did not reveal the age or other details of the latest death—the state’s seventh—besides revealing it was of an unvaccinated resident in Montour County. Overall, the seven deaths in Pennsylvania include two in Jefferson County, three in Lancaster County, and one in Mifflin, in addition to the new death in Montour. An eighth death was reported in Franklin County, but state health officials have not confirmed it.
For all the states with deaths so far, health officials have noted that they’re the first deaths in decades. Multiple outbreaks are underway across the country, pushing the national tally of cases to nearly 5,500 across 47 states and jurisdictions, according to the Centers for Disease Control and Prevention. Pennsylvania’s case count alone is over 1,500 and Wisconsin is reporting nearly 650.
Android XR Gets Spatial Container Support To Enable Multi-Engine Apps
Android XR now supports the recently standardized OpenXR Spatial Container extensions on devices with Spatial API Level 4 or higher, though notably limited to apps running in Full Space mode.
The recently released OpenXR Spatial Container extensions standardize system-managed spaces in which applications can display volumetric 3D content, similar to how traditional systems place 2D content within windows on a desktop.
OpenXR Spatial Container Extensions Standardize Volumetric App Multitasking
The newly released OpenXR Spatial Container extensions standardize system-managed spaces for volumetric 3D apps, similar to how traditional systems place 2D content in desktop windows.
 UploadVRLuna
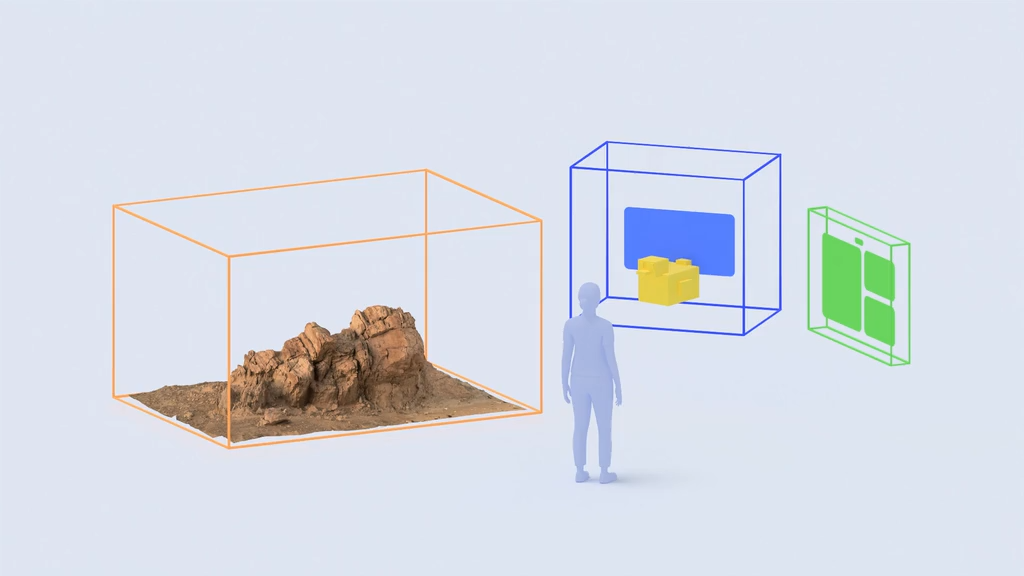
Previously, an OpenXR session on Android XR took exclusive control of the device’s display. Now, Spatial Containers on Android XR let apps render 3D content inside a bounded 3D volume or transition into an unbounded, immersive mode similar to a conventional OpenXR app.
Android XR handles each Spatial Container’s window controls and placement. When a container is focused and interactive, you can interact directly with the 3D content inside the volume using hand tracking, eye gaze, or 6DoF controllers.
0:00
/0:13
This new integration makes it possible to combine Jetpack Compose UI, standard 2D Android activities, and OpenXR-based 3D content in a single app. The 3D content can be rendered using game engines such as Unity or Godot, or implemented directly with native OpenXR.
The NBA app is among the first to demonstrate this new functionality, leveraging it to provide a feature called Court View.
The app’s main interface is built with Jetpack Compose, while select games now feature volumetric 3D court scenes rendered using Unity. This is similar to the feature introduced as Tabletop in the NBA app for Apple Vision Pro, which is now also called Court View.
0:00
/0:19
The NBA app’s Court View feature as shown at Google I/O 2026.
0:00
/0:18
The NBA app’s Court View feature as shown at the Android Dev Summit 2026.
At the standards level, Spatial Containers could enable apps broadly similar to those made possible by visionOS on Apple Vision Pro. Apple’s “Shared Space” architecture and RealityKit framework allow for both windowed and volumetric 3D apps to run alongside each other in a system-managed environment and transition into “Full Space” immersive experiences.
However, Android XR’s initial implementation has a significant limitation in that Spatial Containers require apps to run in “Full Space Managed” mode, rather than “Home Space”, the mode Android XR uses to allow for multitasking with other apps.
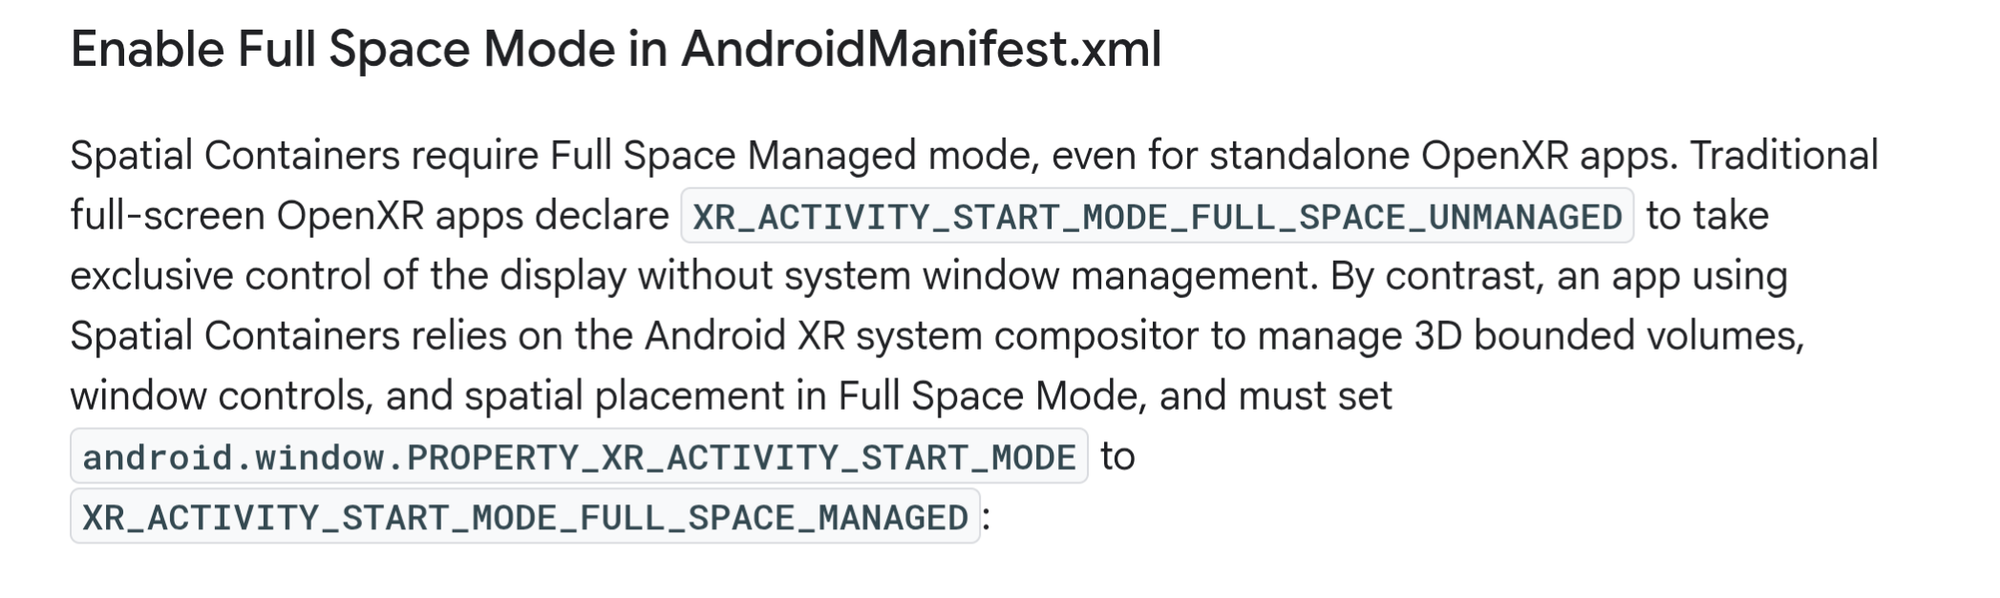
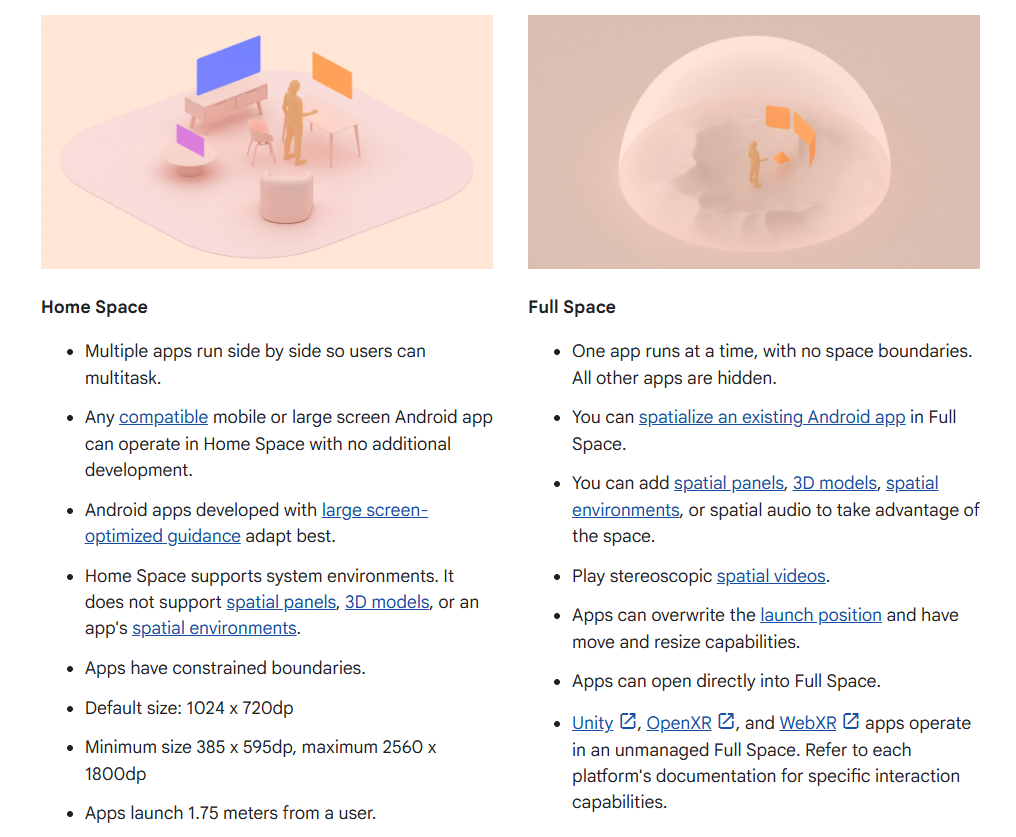
In practice, this means that an app running in Full Space can display multiple Spatial Containers with volumetric 3D content, but they cannot be displayed alongside content from other apps. This follows Android XR’s existing architecture, which limits spatialized app components to Full Space.
0:00
/0:57
Demo of Android XR’s current implementation of Spatial Containers via the hello_xr sample, using an XR Headset in the Android Emulator with configuration patches. Note how the Chrome and Files windows are hidden.
This distinction means Android XR’s current implementation of the Spatial Container extensions is best described as enabling multi-engine apps rather than cross-app spatial multitasking. Google had previously described the underlying functionality as supporting “multi-engine experiences” when previewing it at the company’s I/O conference earlier this year.
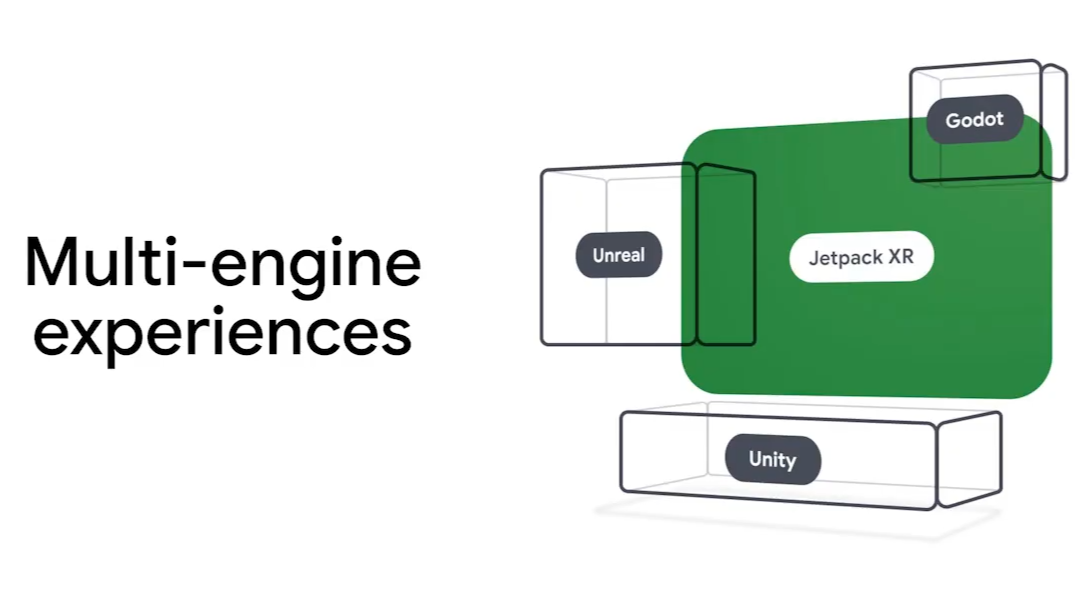
While Spatial Containers are a step forward for Android XR, this initial implementation still leaves a gap between its capabilities and the full spatial multitasking offered by operating systems like visionOS on Apple Vision Pro and Pico OS 6 on the upcoming Pico Space Pro.
Microsoft Blames Monster Email Outage On Software Defect Introduced In July Fix
Microsoft says last week’s massive Microsoft 365 outage was caused by a software defect introduced in a July update that remained dormant until a Teams failover and a simultaneous 14% reduction in gateway capacity triggered a cascading failure. More than 80% of the affected gateway servers became unresponsive at the outage’s worst point, and because the months-old change could not simply be rolled back, engineers spent roughly 15 hours developing and deploying a patch that restored the previous code path. The Register reports: According to a preliminary post incident report published by Microsoft on November 15, the defect was introduced in July 2026. The update looked fine at the time, Microsoft says, having passed load testing and been deployed without any impact. However, the testing wasn’t good enough. Microsoft’s report states: “Our load testing tended to focus on weaker hardware with fewer cores.” The defect caused “lock contention inside an internal Windows process which caused the machine’s resources (CPU & memory) to be exhausted.”


“The contention issue is worsened on machines with more cores and newer hardware.” The fix containing the defect was prepared specifically for Microsoft 365 network gateway servers. Then two things happened at once. Teams failed over to the “primary” gateway that supports Exchange Online, creating a surge in load that was not, in itself, particularly unusual. At the same time, almost 14 percent of server capacity for the networking gateway was out of service, which wasn’t a problem by itself either: it was on its way to being restored and, according to Microsoft, “the service had sufficient capacity headroom.” Together, they pushed the gateway into the defect and chaos ensued. It was a classic cascading failure scenario. When a server loses connectivity, traffic gets routed to the next healthy endpoint. Which encountered the same problem. So traffic was rerouted again and… you can see where this was going. Within two hours, the defect was encountered across Microsoft’s fleet. “At its lowest,” the report states, “more than 80 percent of servers were unresponsive.”
So, what to do? Bringing servers back to service didn’t help — they were immediately overwhelmed and fell over again. “Our normally automated recovery processes were not designed to restore service from this broad unresponsive state.” A straightforward rollback was also not possible because the defect was months old. Instead, engineers developed patch for the patch or, in Microsoft’s words, “an update that returned the code path to the previously known good state in Windows.” The patch was applied to groups of servers and service was gradually restored.
Read more of this story at Slashdot.
MRDIMM 8800 MT/s vs. 12800 MT/s Memory Performance With AMD EPYC Venice
With last week’s AMD EPYC 9006 SP7 availability and the AMD EPYC 9686F and EPYC 9996 processor reviews, one of the most frequent questions/comments was around the impact that the new MRDIMM-12800 memory had on these Zen 6 server processors compared to prior gen and the Intel/NVIDIA server competition. Given that curiosity over the MRDIMM-12800 impact, here are the EPYC 9686F 2P benchmarks when re-testing at 8800 MT/s memory speeds.
Intel Talks Up GPU D270 Performance & Open-Source Software Support
For Supercomputing 2026 week, Intel published a blog post talking up their Intel GPU D Series “Crescent Island” hardware based on Xe3P…
Why Microsoft is ditching a few of its 365 companion apps in 2026
These apps are being shut down after just 14 months.
Googlebook Goes Detachable As Lenovo Duet 13 Leaks With Slick 2-In-1 Design
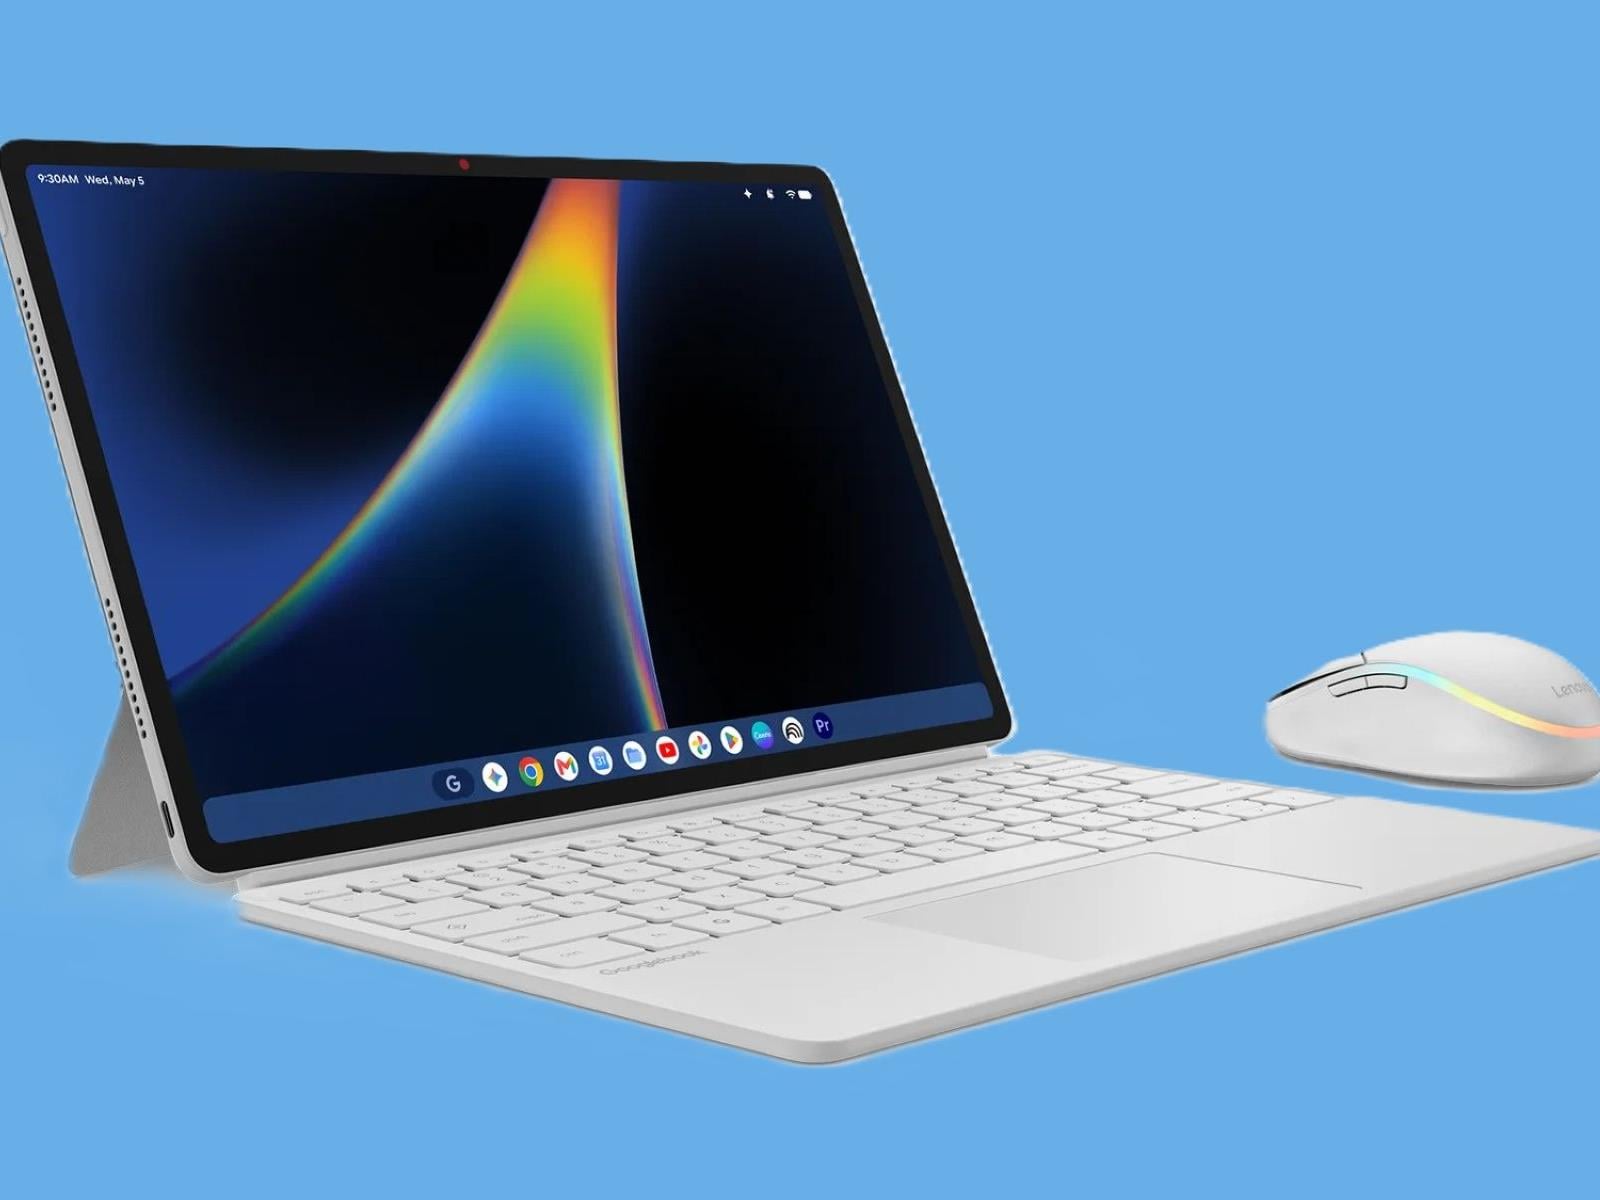
Prominent leaker Evan Blass has given us a better idea on what the upcoming Lenovo Googlebook Duet 13 (slated for January) will look like. The new 2-in-1 tablet carries much of the prior Duet’s external aesthetics but brings more powerful guts
Samsung’s Flagship Dolby Atmos Soundbar Gets A Big 57% Cut Ahead Of Black Friday
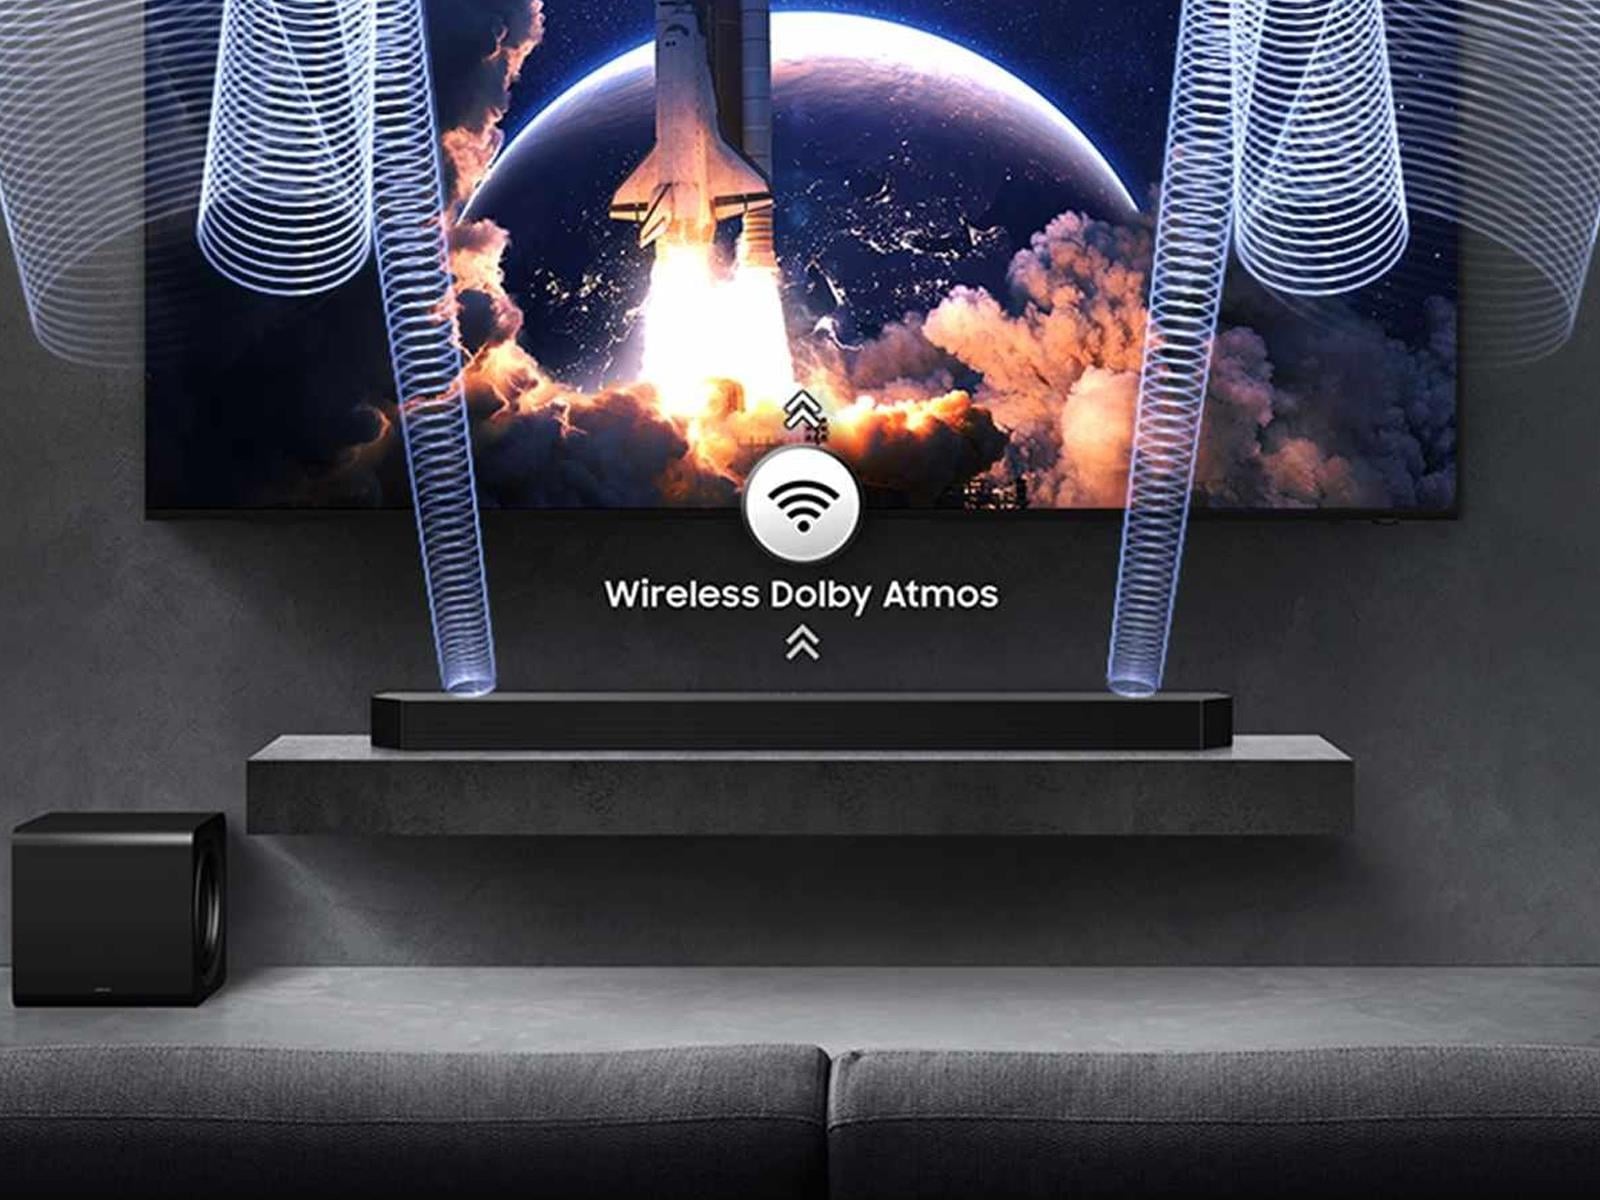
Why wait for Black Friday when big savings are already there for the taking? Such is the case if you’re in the market for a home theater audio upgrade, as Samsung’s flagship Dolby Atmos soundbar is currently more than half off its MSRP at Amazon’s
Google Killed Its Dark Web Report, but You Can Still Monitor Data Breaches
Google’s Dark Web Report used to be the only consumer-focused platform that let users scan major data breaches, dark web marketplaces, and private forums to see if their personal information had ended up in the hands of hackers. But the company discontinued the service at the start of 2026, with new scans stopping on Jan. 15 and all accounts deleted on Feb. 16.
Google says it sunsetted Dark Web Report because, although the information it provided was generally useful, the service failed to provide “helpful next steps” for users whose data was found on the dark web. Google promised a new service that would provide more actionable intel, but that service has yet to materialize, and there haven’t been any further announcements about it yet.
Dark Web Report may not have been perfect, but it was the only early warning system of its kind that was available for personal use and let users run scans free of cost. Now that it’s gone, however, there are plenty of other services that offer the same service at varying costs and levels of effectiveness. Let’s talk through the nature of the insight that Google’s reports offered, how it collected that information in the first place, and what options exist in the market to replace it.
How the Dark Web Report worked
Google launched the Dark Web Report in March 2023 as a premium feature available to Google One users, but later extended it for free to anyone with a Google account and moved it to the “Results about you” dashboard.
You’d set up a monitoring profile with your name, date of birth, physical address, phone number, emails, and Social Security Number if you lived in the U.S. After that, you could head to the dashboard anytime you wanted to run a free scan across dark web forums and marketplaces, publicly disclosed corporate data breaches, and other hidden online spaces to see if any of your personal information had shown up there. It was easy to use—but not a lot of people knew it existed in the first place.
What made Google pull the plug on Dark Web Report
It’s unclear what prompted the internal decision at Google, but in the absence of concrete next steps, it is reasonable to think the reports could create panic for the uninitiated. There’s no way to remove your information from the dark web once it’s already in circulation there. Still, having an early warning so you could reset 2FA or self-lock your SSN isn’t without merit.
But perhaps more importantly, most people with Google accounts didn’t know and hadn’t heard of the Dark Web Report’s existence. Google has likely taken it as a hint that users want more active remediation tools than simple alerts, which is why it’s now directing users to the Password Manager, Passkeys, and “Results about you” dashboard instead—though, again, the company hasn’t followed through on a direct replacement for Dark Web Report, despite teasing such a feature.
A few alternatives to Google’s Dark Web Report
| Tool | Starting Cost | Monitoring Features |
|---|---|---|
| Have I Been Pwned | Free | Email addresses, passwords, domain names |
| Mozilla Monitor | Free | Up to 20 email addresses |
| Google Password Checkup / Apple Passwords | Free | Saved passwords |
| Proton Pass Plus | $1.99/month billed annually | Proton addresses, aliases, up to 10 other emails |
| NordVPN Dark Web Monitor | $1.69/month billed annually | Up to 5 emails, phone, cards, and national ID |
| Surfshark Alert | $2.99/month billed annually | Emails, cards, personal ID numbers |
| Microsoft Defender | $99.99/year | 64 identity data types, plus credit score monitoring |
Many of the top dark web scanners draw from the same well of information, scanning against major data breaches and dark web spaces. Several also offer breach notifications that send you email alerts when your details show up in a periodic scan. However, none of that is worth paying for because Have I Been Pwned or Mozilla Monitor cover those features quite well for free. Even the default password managers from Google and Apple come with some ability to monitor leaked credentials.
As for paid options like Surfshark Alert or NordVPN Dark Web Monitor, these services earn their keep when you need to track phone numbers, credit cards, SSNs, and other national IDs—in addition to emails and passwords. NordVPN also has a separate service called Threat Protection Pro, which monitors dark web channels for stolen session cookies. If you’re already on a Microsoft 365 plan, Defender’s identity theft monitoring tools are nice to have because they don’t require a separate subscription, but they’re not currently available to users outside the United States.
What to do when you get a dark web breach alert
There isn’t an easy way to scrub your information from the dark web once it ends up getting leaked. But you can take steps to protect sensitive information or financial data once you know there’s been a leak. If a password has been compromised, reset it immediately. Also, enable 2FA on the affected account for added security. Even better, switch to a passkey if that account supports it. If not, authenticator apps are a safer way to receive 2FA codes than standard SMS.
If your Social Security number has been leaked, freeze your credit with Equifax, Experian, and TransUnion. You can do this by contacting each agency separately. Freezing your credit will prevent unauthorized credit withdrawals and protect your credit score from abuse by attackers. If one of your credit or debit card numbers has ended up in a breach, call your bank to freeze transactions on that card immediately.
Finally, get in the habit of using email aliases instead of sharing your actual email address with every platform and service provider. Addy.io and Proton’s SimpleLogin are both popular services that let you generate temporary email aliases that point to your inbox.
‘Actively Makes The Game Worse’: Fans Are Furious With Pikmin 4′s Paid Nintendo Switch 2 ‘Upgrade’
‘This is essentially a paid downgrade’
Dictate into any app on Fedora with TuxTalk
TuxTalk is a free voice dictation tool for Linux. You hold a key, talk, and let go. What you say appears wherever your cursor is located: a document, an email, a chat box or a terminal. The speech model runs on your own computer, so your voice never leaves it and there is no account…
Apple is making a bigger push into video podcasts
You’ll soon be able to watch video podcasts through the Apple TV app.
Samsung’s Galaxy S27 Camera Leak Puts Upgraded Pro RAW Controls In Focus
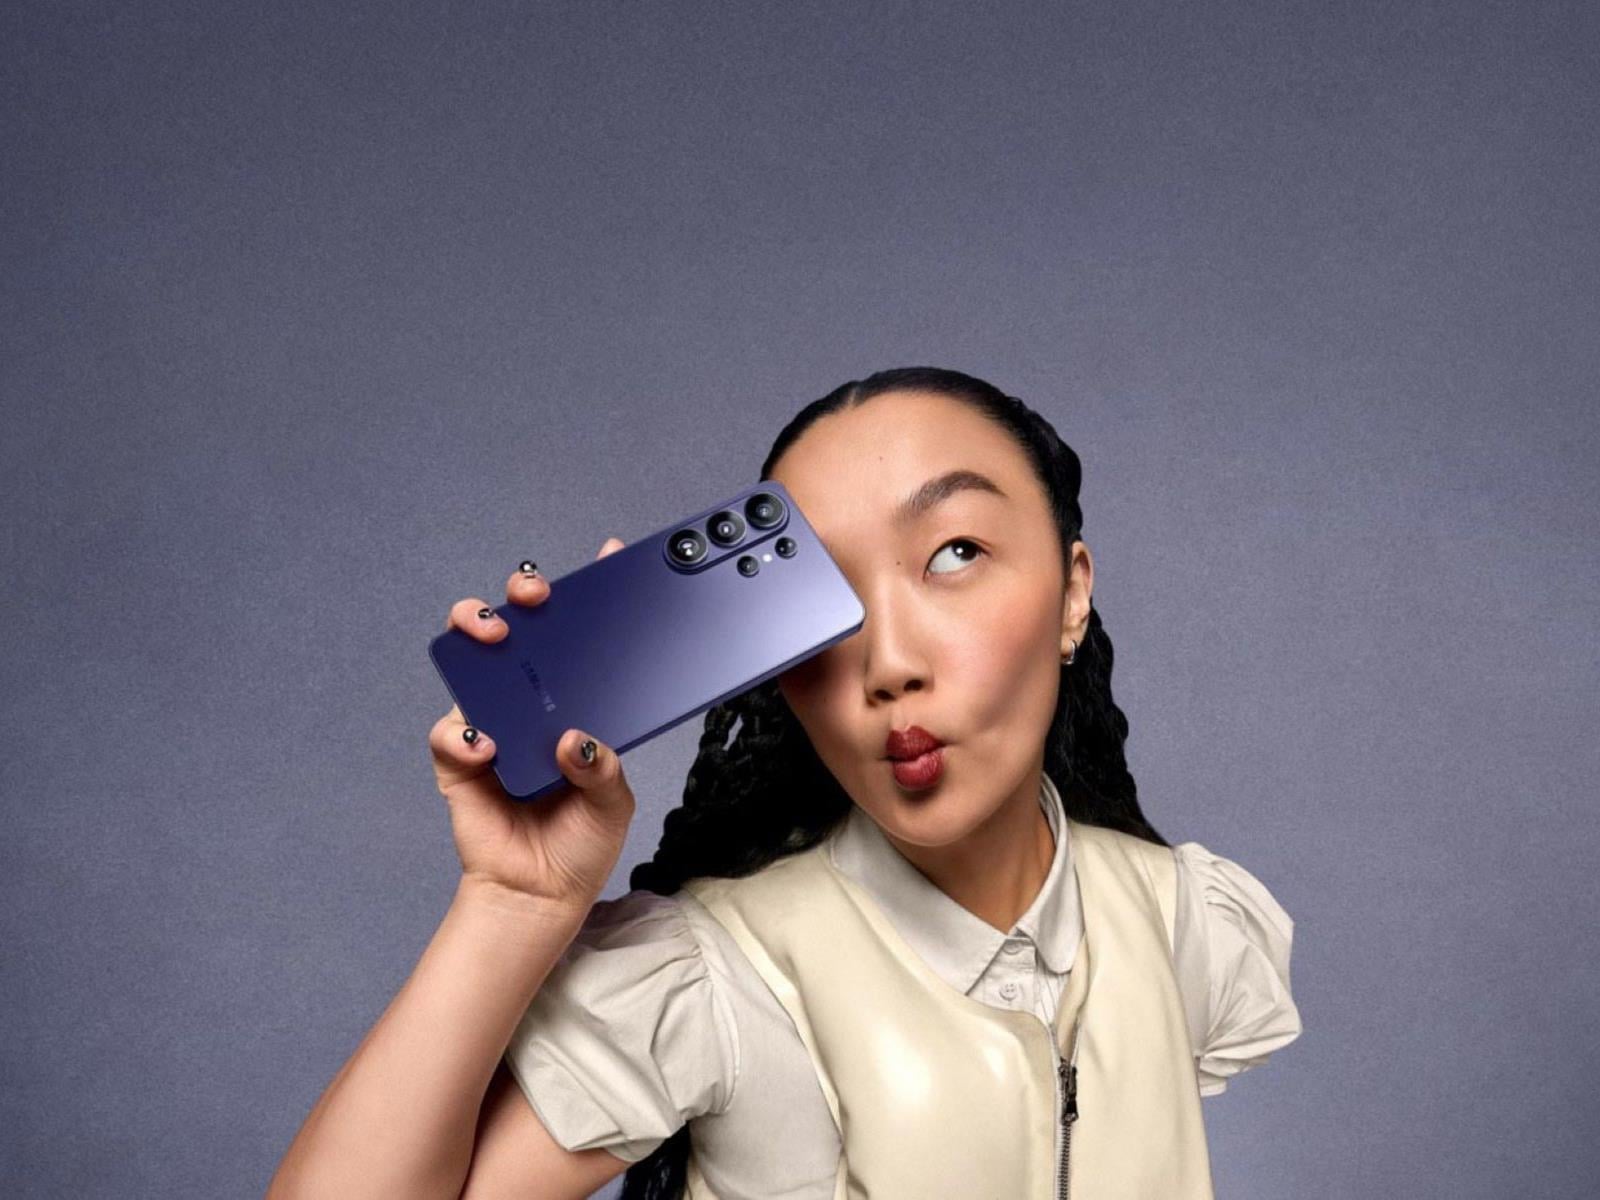
Early build leaks hint at a possible overhaul for Samsung’s Expert RAW camera app for One UI 9.5 and the Galaxy S27 series, bringing meaningful upgrades for mobile photographers who prefer shooting in RAW.
If you love squeezing every ounce
The 15 Best Early Black Friday Video Game Deals
Black Friday is officially two weeks away, but Amazon has decided to kick things off early this year with some fantastic video game deals. It’s an excellent opportunity for players to bolster their backlogs, especially as gaming hardware continues
Call It A Comeback? Jensen Returning To NVIDIA Is Not Off The Board
A petition calling for the reinstatement of Jensen Huang as NVIDIA’s CEO following his resignation amid revelations of multiple extramarital affairs, including one involving a woman suspected of ties to Chinese intelligence, has amassed over
Robert Pattinson Is Officially The New James Bond
The Odyssey and Batman star steps into the role after Daniel Craig’s 15-year run
[$] A new generation of futexes
Futexes
are a kernel subsystem that provides support for fast mutexes
in user space. While futexes can indeed be fast, they are not fast enough
for a number of users. Partly as a result of that, the implementation of
futexes has grown in complexity over the years, with two basic variants
on offer. The desire for faster futexes remains, though, and that inspires
new patches, including this series
from Suleiman Souhlal adding a third futex class called “futex PING”
for “priority inheritance next generation”.
are a kernel subsystem that provides support for fast mutexes
in user space. While futexes can indeed be fast, they are not fast enough
for a number of users. Partly as a result of that, the implementation of
futexes has grown in complexity over the years, with two basic variants
on offer. The desire for faster futexes remains, though, and that inspires
new patches, including this series
from Suleiman Souhlal adding a third futex class called “futex PING”
for “priority inheritance next generation”.
Mercedes’ clever new driving assist handles complex traffic like a champ
SAN FRANCISCO—When Ars first drove the new Mercedes-Benz CLA last year, the automaker also gave us a sneak preview of its next driver assist. Called Drive Assist Pro, it’s for collaborative partially assisted driving, and from the passenger seat at the time, the demo was impressive. Now the automaker is getting ready to start rolling out Drive Assist Pro to customers with cars running the new MB.OS operating system here in the US and in Germany, and it let us have some time behind the wheel.
While most automakers want a reputation associated with safety, Mercedes has long used passive and active technology to do so in its products. It was one of the first OEMs to introduce airbags, then a decade later started adding active safety systems like antilock brakes, electronic stability control, and adaptive cruise control. And so, by giving the car’s electronics the ability to control the brakes, and throttle, we arrive at the first level of assisted driving—called “level 1” in automotive engineerspeak.
“Level 2” assisted driving, where the car also controls the steering as well as the acceleration and braking, got famous with Tesla Autopilot. But the first lane-keeping assists predate it by almost a decade in passenger cars, when Toyota introduced a system in 2004. The human driver behind the wheel is still in charge, responsible for situational awareness (and anything that arises from a lack thereof), with the idea that long drives become less tiring and a little more effortless when the car does the boring job of keeping a constant speed or a constant distance to the car ahead and between the white lines.