PoCL 5.0 has been officially released as the latest version of this “Portable Computing Language” implementation that provides OpenCL support for CPU-based execution as well as various other LLVM-based hardware back-ends like for NVIDIA PTX and oneAPI Level Zero. With PoCL 5.0 is also a new experimental back-end for targeting OpenCL support distributed across networked systems…
Source: Phoronix – PoCL 5.0 Released With Transparent OpenCL Over Networked Systems Capability
Monthly Archives: December 2023
Pokémon Scarlet And Violet’s Legacy Is Squandered Potential
Entire generations of Pokémon history often feel defined by a single game. As wide-ranging as this franchise is—games, anime, trading cards, lifestyle merchandise—Game Freak’s video games provide the single creative wellspring from which everything else springs forth. As such, games like Scarlet and Violet often…
Source: Kotaku – Pokémon Scarlet And Violet’s Legacy Is Squandered Potential
India's Flooded Farmlands Mask a Water Crisis Deep Underground
India consumes more groundwater. That’s testing India’s ability to feed itself and much of the world. From a report: The South Asian nation is already the world’s largest guzzler of groundwater. Cheap power has encouraged routine overreliance on finite riches. India overwhelmingly grows some of the thirstiest crops: rice, wheat and sugar cane. Over the last half century, farm productivity has leapt forward, but so, too, has water usage — up 500% over that period, according to the World Bank. Erratic monsoons and brutal heat waves are only making the problem more acute. Farmers are digging deeper wells because existing ones are no longer refilling. Some regions may run out of groundwater entirely — Punjab, a major wheat producer, could go dry within the next 15 or so years, according to a former state official. States in southern India are battling over water rights in areas where rampant urban development has drained thousands of lakes.
The government is not blind to the crisis. But with a national election on the horizon next year, there’s little to gain in pushing actively for change among farmers, one of the most important voting blocs in the country. Any long-term solution will involve tinkering with farm subsidies or the minimum price set for water-intensive crops. Prime Minister Narendra Modi’s ruling party is all too aware that farmers from India’s grain-growing northern regions dominated months of protests against proposed agrarian reforms from late 2020. Modi was forced to withdraw the proposals. For now, it’s clear the water math does not add up.
Modi has promised piped water to all Indian households by 2024. Yet nearly half of India’s 1.4 billion residents already face high-to-extreme water stress, and the world’s most populous nation is expected to add more than 200 million more people by 2050. Agriculture, meanwhile, accounts for 90% of water use, helping to explain why Indian officials say the clearest strategy for preserving supplies is modernizing the industry. The government has tried to convince farmers to adopt different irrigation technologies, return to traditional rain harvesting and plant less thirsty crops like millets, pulses and oilseeds. Nothing has yet made a substantial difference, in a country where subsidies supporting wheat and rice persist, and farming is dominated by smallholders.


Read more of this story at Slashdot.
Source: Slashdot – India’s Flooded Farmlands Mask a Water Crisis Deep Underground
How to Use Your Credit Card Rewards to Spend Less on Holiday Gifts
If you’re feeling squeezed by the inflation-addled cost of holiday shopping this year, but still want to buy gifts for family and friends, your hard-earned credit card rewards can come in handy.
As The Points Guy and others point out, you almost always get the best value out of your rewards when you spend them on travel, such as airfare and hotel bookings, versus redeeming points and miles for cash back or non-travel purchases. However, if you’re looking for ways to reduce the out-of-pocket cost of presents this holiday season (and don’t have an imminent travel-related use for your rewards), consider strategically spending some of those points and miles on the people you care about.
Gift your points and miles
One way to get great value out of your credit card rewards is to gift them to someone else to use for travel. This will usually require you to transfer your points to a partner airline or hotel loyalty program before you can pass them on to someone else (an exception being Chase Ultimate Rewards members in the same household). Some airlines will charge a miles transfer fee, while most hotels allow points transfers to another member at no cost.
To get around fees and transfer limits, you could offer to book travel for the recipient using your rewards—just don’t do so before confirming they’re on board.
Redeem points for cash or statement credits
Some rewards programs allow you to pay yourself back with your points—either by redeeming them for a statement credit or cash rewards, such as a direct deposit or mailed check. This can help offset the cost of gifts you plan to or have already purchased. Your mileage may vary, however: Chase Ultimate Rewards typically offers the best per-point value through its Pay Yourself Back statement credit (1–1.5 cents per point redeemed), while American Express Membership Rewards allows just 0.6 cents per point spent on statement credit.
Shop with points at specific retailers
Another non-travel redemption option is spending credit card rewards on merchandise from retailers like Amazon, Apple, Walmart, and Best Buy as well as through PayPal. (Airline and hotel points can sometimes be used on merch as well as media subscriptions.) If you’re shopping at these stores anyway, you can apply points to purchases at checkout rather than charging costs to your card.
Again, the value varies significantly across rewards programs and retailers. Chase Ultimate Rewards are worth 1 cent per point at Apple but 0.8 cents per point at Amazon; transactions made with Citi ThankYou Rewards may have exclusions and minimum purchase requirements.
Use points to purchase gift cards
Finally, most rewards programs have a selection of gift cards available for purchase with points. You can give gift cards as gifts or use them to buy presents at retailers that aren’t eligible for shopping with points. Be sure to read the fine print, as the delivery options may range from a physical card sent to your address on file to an e-card.
And again, the value of your points will depend on the rewards program—it probably isn’t a surprise at this point that Chase Ultimate Rewards redemption rates top the list with the biggest selection, while airline and hotel rewards get the lowest value when applied to gift cards. American Express Membership Rewards allows you to buy Amex gift cards (not merchant-specific), though at a rate of only 0.5 cents per point.
Source: LifeHacker – How to Use Your Credit Card Rewards to Spend Less on Holiday Gifts
What's New on Disney+ in January 2024
After a packed December, Disney+ has a lighter load of original content planned for January. Continuing from last month, there are additional episodes (premiering weekly on Wednesdays) of the fantasy series Percy Jackson and the Olympians, as well as the final two parts of the docuseries BTS Monuments: Beyond the Star.
Your monthly dose of Marvel centers on Echo (January 9), a gritty, action-filled (TV-MA) series named after the titular character, a deaf superhero. THe trailer suggests a tone and feel that evoke Netflix’s Daredevil. (You may recognize the antagonist from that soon-to-be-rebooted series.) If you like the show itself, the behind-the-scenes Assembled: The Making of Echo is streaming on January 31.
And on the documentary front, there’s A Real Bug’s Life (January 24), an original series from National Geographic—narrated by Awkwafina—that takes viewers into the environment of real bugs around the world as well as Choir (January 31), a six-part docuseries that captures the Detroit Youth Choir’s performance preparation.
Here’s everything coming to Disney+ in January 2024.
Disney Plus series with new episodes premiering weekly in January 2024
-
BTS Monuments: Beyond the Star—Wednesdays, finale on January 10
-
Percy Jackson and the Olympians—Wednesdays
Movies and complete series/seasons coming to Disney Plus in January 2024
Arriving January 3
-
Alice’s Wonderland Bakery (S2, 6 episodes)
-
Ax Men (S10, 10 episodes)
-
Forged in Fire (S7, 37 episodes and S8, 45 episodes)
-
History’s Greatest Mysteries (S3, 13 episodes)
-
Modern Marvels (S20, 2 episodes and S21, 12 episodes)
-
Storage Wars (S12, 16 episodes and S13, 36 episodes)
Arriving January 5
-
X-Men (2000)
Arriving January 7
-
The Incredible Pol Farm (S1, 14 episodes)
Arriving January 9
-
Marvel Studios’ Echo—Disney+ Originals premiere
Arriving January 10
-
Hamster & Gretel (S1, 3 episodes)
-
Kiya & the Kimoja Heroes (S1, 12 episodes)
Arriving January 12
-
Bluey (Season 3)
Arriving January 17
-
America’s Funniest Home Videos: Global (S24 22 episodes, S25 23 episodes and S26 22 episodes)
-
The Ghost and Molly McGee (S2, 2 episodes)
-
Minnie’s Bow-Toons: Camp Minnie (S1, 5 episodes)
-
Siempre Fui Yo (Season 2)—Disney+ Originals premiere
Arriving January 23
-
The Last Repair Shop
Arriving January 24
-
A Real Bug’s Life—Disney+ Originals premiere
Arriving January 31
-
Me & Mickey shorts (S2, 17 episodes)
-
Mickey Mouse Funhouse (S2, 4 episodes)
-
Choir—Disney+ Originals premiere
-
Assembled: The Making of Echo—Disney+ Originals premiere
Source: LifeHacker – What’s New on Disney+ in January 2024
Xfinity breach may have affected as many as 35.8 million customers
Xfinity says a data breach likely led to attackers obtaining customers’ usernames and hashed passwords. Other personal information may have been exposed, such as names, contact information, the last four digits of social security numbers, dates of birth and secret questions and answers. The company added that its analysis of the attack is ongoing and it has informed law enforcement about the incident.
In a filing with Maine’s attorney general’s office, Xfinity owner Comcast disclosed that the intrusion has impacted 35.8 million people. As TechCrunch points out, Comcast had 32.3 million broadband customers as of the end of September, indicating that the vast majority of Xfinity customers have been affected by the breach.
On October 10, Citrix disclosed a vulnerability in software that Xfinity and many other businesses use. It provided guidance on how to mitigate the vulnerability on October 23 and Xfinity said it swiftly patched the problem. However, while carrying out a routine cybersecurity check two days later, Xfinity spotted suspicious activity in its systems. It later determined that bad actors accessed its internal network between October 16 and 19.
Xfinity says it’s informing customers of the incident via its website, email and by other means. It’s urging them to change their passwords, to make sure they don’t use the same passwords on different accounts and to enable two-factor or multi-factor authentication. Xfinity also suggested that folks who use the same login credentials on other accounts change their passwords on those.
This isn’t the first security incident Xfinity has had to deal with. Back in 2018, it emerged there was a bug in a Comcast website used to activate Xfinity routers. The issue led to some customers’ home addresses being exposed, along with the name and password for their Wi-Fi networks.
Update 12/19 8:00AM ET: Updated to note the number of people who were impacted by the breach.
This article originally appeared on Engadget at https://www.engadget.com/xfinity-suffered-a-data-breach-but-doesnt-know-quite-how-bad-it-was-100711214.html?src=rss
Source: Engadget – Xfinity breach may have affected as many as 35.8 million customers
Daily Telescope: James Webb zooms in on Uranus
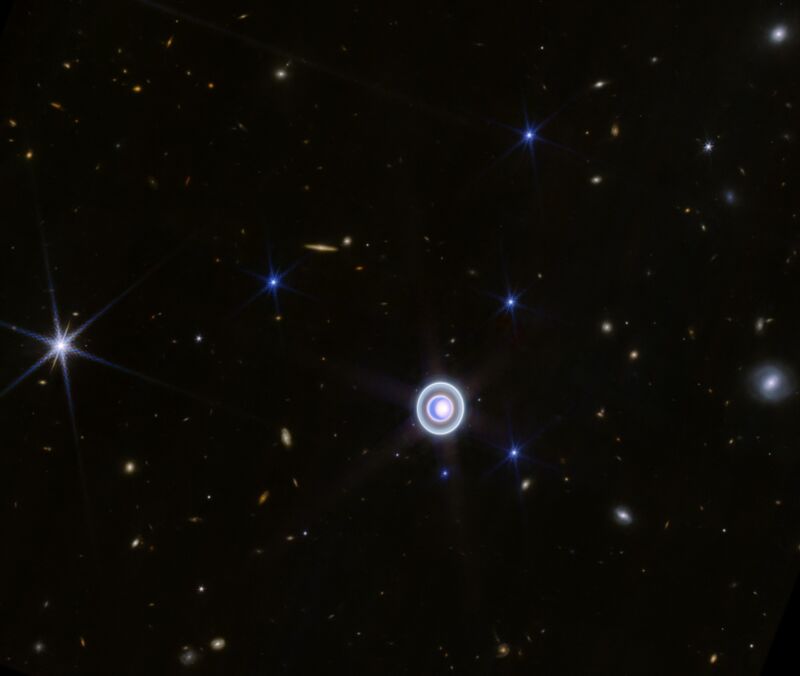
Enlarge / James Webb Space Telescope captures a wide view of Uranus. (credit: NASA, ESA, CSA, STScI)

Good morning. It’s December 19, and as we get closer to the year-end holidays your humble space correspondent is starting to get a little stir-crazy. Hence the reason for today’s abdominal, I mean abominable, headline.
This amazingly cool image of Uranus comes from the Near-Infrared Camera on the James Webb Space Telescope. This wide-field image shows Uranus with an assortment of background galaxies and 14 of its 27 moons, including Oberon and Titania. We can also see the north polar cap gleaming a bright white, as well as the planet’s rather faint (in visible light) inner and outer rings.
I’ve also included the close-up image of Uranus, which is really quite stunning with all of its various rings.
Read 3 remaining paragraphs | Comments
Source: Ars Technica – Daily Telescope: James Webb zooms in on Uranus
Ex-Amazon Engineer Pleads Guilty To Hacking Crypto Exchanges
An anonymous reader quotes a report from BleepingComputer: Former Amazon security engineer Shakeeb Ahmed pleaded guilty this week to hacking and stealing over $12.3 million from two cryptocurrency exchanges in July 2022. The two affected companies are Nirvana Finance, a decentralized crypto exchange, and an unnamed exchange on the Solana blockchain platform that Ahmed hacked using his blockchain audit and smart contract reverse engineering skills. He first targeted the undisclosed crypto exchange by manipulating a smart contract to introduce false pricing data, generating roughly $9 million worth of inflated fees. Ahmed later withdrew the funds and offered to return all but $1.5 million on the condition that the exchange refrained from involving law enforcement.
Although not explicitly named by the Justice Department, the details of the attack match those of a July 2022 breach impacting the Crema Finance decentralized finance (DeFi) platform. Shortly after this first hack, Ahmed exploited a Nirvana Finance DeFi protocol smart contract loophole to take a flash loan of ANA cryptocurrency tokens at a low price and sell it back at a higher rate, yielding him approximately $3.6 million. Despite being offered a $300,000 bounty to return the stolen crypto assets, Ahmed kept everything he stole (representing all the funds owned by Nirvana Finance) after demanding $1.4 million and not reaching an agreement, forcing the exchange to shut down.
Seeking to conceal his actions and obscure the digital trail of the stolen funds, Ahmed used several cryptocurrency mixers (including Samourai Whirlpool), the Solana and Ethereum blockchains, and foreign exchanges to convert the millions he stole into Monero, a cryptocurrency known for its enhanced privacy and anonymity. Wary of being apprehended, Ahmed actively sought ways to elude detection and extradition. His online searches revealed his interest in strategies to flee the United States, thwart asset seizures, and secure citizenship in different nations, clearly showcasing Ahmed’s intention to sidestep legal repercussions for his actions. […] Ahmed entered a guilty plea for a single computer fraud charge, an offense with a maximum imprisonment term of five years. Additionally, he committed to compensating his victims with a sum totaling $5,071,074.23.


Read more of this story at Slashdot.
Source: Slashdot – Ex-Amazon Engineer Pleads Guilty To Hacking Crypto Exchanges
Faux Stroopwafels Are the Laziest Christmas Treat
Real stroopwafels are a Dutch treat. They look like thin, finely waffled cookies filled with a stripe of caramel. Faux stroopwafels could be described the same way. But while real stroopwafels take skill and a steady hand to make, the faux variety can be made perfectly by the most careless person in the world.
This is the ideal Christmas treat to make if you’re deathly allergic to baking, cooking, chores, pulling your weight, or “effort” in any sense of the word. You can make faux stroopwafels with just two storebought ingredients: pizzelles and dulce de leche.
What are stroopwafels?
Stroopwafels are composed of a thin, sugary dough that is waffled in a special mold. The ultra thin waffles must then be split in half, coated with caramel, and sandwiched back together. The caramel solidifies, and the resultant confection is a malty, chewy treat. They can be consumed as-is or softened over a steaming mug of coffee or tea. Fresh stroops are absolutely splendid, but you can see how making waffle dough, taking care to not burn something thin and fragile, and then making and filling them with caramel can be a bit “involved.”
So I combined two delicacies from Italy and many parts of Latin America to make the cheater’s version of this Dutch treat. It’s possibly the laziest hack of all time. Head to the grocery store and grab a jar of dulce de leche and a container of pizelles. They usually come in packs of 24. I’ve seen vanilla, anise, and chocolate pizelles, and while they’d all be good with milk caramel, vanilla will most resemble a classic stroop. They’re usually available in the cookie section of grocery stores, and dulce de leche is often in the “international aisle,” or over by the condensed and evaporated milks.
Crack open the jar (or can) of dulce de leche, and rip open a packet of pizzelles. Use the back of a spoon to smear a spoonful of dulce de leche over one pizzelle, spreading the caramel out almost to the edge of the cookie in a thing layer. (You should be able to see the pizzelle pattern through parts of it.) Then put another pizzelle on top. Gently press and shift the waffles until the caramel is pushed out to the edge.
If you’re making these for yourself, proceed to consume your crunchy, caramel-y creation. If you’re making them for friends or family (and you are willing to expend a tiny bit of effort), dust them with powdered sugar to add a pinch of sophistication.
Source: LifeHacker – Faux Stroopwafels Are the Laziest Christmas Treat
9to5Linux Weekly Roundup: December 17th, 2023
The 167th installment of the 9to5Linux Weekly Roundup is here for the week ending on December 17th, 2023, keeping you guys up to date with the most important things happening in the Linux world.
Source: LXer – 9to5Linux Weekly Roundup: December 17th, 2023
The Morning After: Apple pauses Apple Watch Series 9 and Ultra 2 sales
Some holiday misery for Apple: It will soon pause sales of its latest Apple Watches in the US due to an International Trade Commission (ITC) ban. The company will suspend sales online this week and at Apple retail locations after December 24. Ho ho ho.
It’s all down to a patent dispute over the wearables’ blood oxygen sensor. Cast your minds back: Medical tech company Masimo sued Apple in 2021 for alleged violations of light-based blood-oxygen monitoring patents. In October, the ITC upheld a judge’s ruling from earlier this year that the Apple Watch did violate Masimo’s patents. The ITC’s order blocks all Apple Watch Series 9 and Ultra 2 imports to the US after December 25.
The case went to the White House for a 60-day Presidential Review Period. Although President Biden has one more week to decide whether to veto the ITC ruling, Apple has pre-emptively complied with the commission’s decision.
President Biden reportedly owns an Apple Watch – but also a load of other watches too.
— Mat Smith
You can get these reports delivered daily direct to your inbox. Subscribe right here!
The biggest stories you might have missed
An electric car completed the world’s first-ever drive from the North to the South Pole
Adobe terminates its $20 billion Figma acquisition amid regulatory scrutiny
Beats headphones and earbuds are up to 49 percent off right now
2023 in review: The year the economics of tech caught up with reality
Here’s everything you should do to up your digital security before next year
Our top gadgets of 2023
The ones we bought.
Engadget
We test and review tons of gadgets every year, and (for some reason) we also buy a lot of things for ourselves. This year, those purchases included coffee-making upgrades, fancy keyboards and even pricey digital pianos. But there are plenty of other things we’ve bought and loved this year that have yet to make it on the site. Here, our staff looks back at the things that were worth the money.
A new picture of Uranus looks like a sci-fi portal
The Webb telescope’s NIRCam filters are to thank for this.
NASA / ESA / CSA
The James Webb Space Telescope (JWST) has a treat to celebrate the upcoming second anniversary of its launch: an image of the icy planet Uranus. The picture, resembling a glowing blue marble rippling in a black ocean, was funneled through the telescope’s infrared filters to capture wavelengths we wouldn’t see with the naked eye.
Yeah, it looks like the CBS logo.
US lawmakers call for DOJ probe into Apple’s blocking of Beeper’s iMessage app
They asked an assistant attorney general to determine whether Apple violated antitrust laws.
More socks for Apple’s legal department this Christmas. A bipartisan group of US senators and representatives have urged the Department of Justice to investigate whether Apple violated antitrust laws by attempting to block Beeper Mini’s access to iMessage. Senators have asked an assistant attorney general to look into Apple’s “potentially anticompetitive conduct.”
Hopefully, senators will have learned lessons from the other times they’ve tried to grill technology companies without the technical expertise for their questions to make sense.
This article originally appeared on Engadget at https://www.engadget.com/the-morning-after-apple-pauses-apple-watch-series-9-and-ultra-2-sales-121539726.html?src=rss
Source: Engadget – The Morning After: Apple pauses Apple Watch Series 9 and Ultra 2 sales
The XPG Core Reactor II 1200W PSU Review: XPG Goes for the Gold
An increasingly common face in the power supply market, the bulk of XPG’s work thus far has been on high-end, high-margin power supplies, such as their 80Plus Platinum-rated Cybercore II. But as the company has become better established in the PSU market on the back of multiple successful products, the company is looking to expand their footprint by venturing into the mid-range segment.
Spearheading that effort is the new XPG Core Reactor II series. Looking to maintain their competitive edge with, what’s frankly, a cheaper power supply design, XPG needs to walk a very tight rope, where where the equilibrium between performance, quality, and cost is crucial. In this category, PSUs must support a range of computing setups while maintaining a focus on value for money. The Core Reactor II series represents XPG’s dedication to this segment, illustrating their capability to cater to a broad spectrum of users who seek a blend of reliable performance and economic viability.
As an 80Plus Gold certified unit and without too many bells and whistles, the Core Reactor II stands out for its practical design, tailored to deliver consistent performance without the premium cost. In examining the details of the XPG Core Reactor II series, we will evaluate how well these PSUs align with XPG’s commitment to affordable quality and whether they meet the diverse needs of mid-range computing environments.
Source: AnandTech – The XPG Core Reactor II 1200W PSU Review: XPG Goes for the Gold
Vulkan 1.3.274 Released With Video Encode Extensions Promoted
As what’s likely to be the last Vulkan API spec update before Christmas, Vulkan 1.3.274 was released today with the Vulkan Video encode extensions promoted as well as adding some other new extensions as a nice end-of-year gift…
Source: Phoronix – Vulkan 1.3.274 Released With Video Encode Extensions Promoted
Blue Origin Is Blasting Off To Space After A Yearlong Hiatus And You Can Watch Live
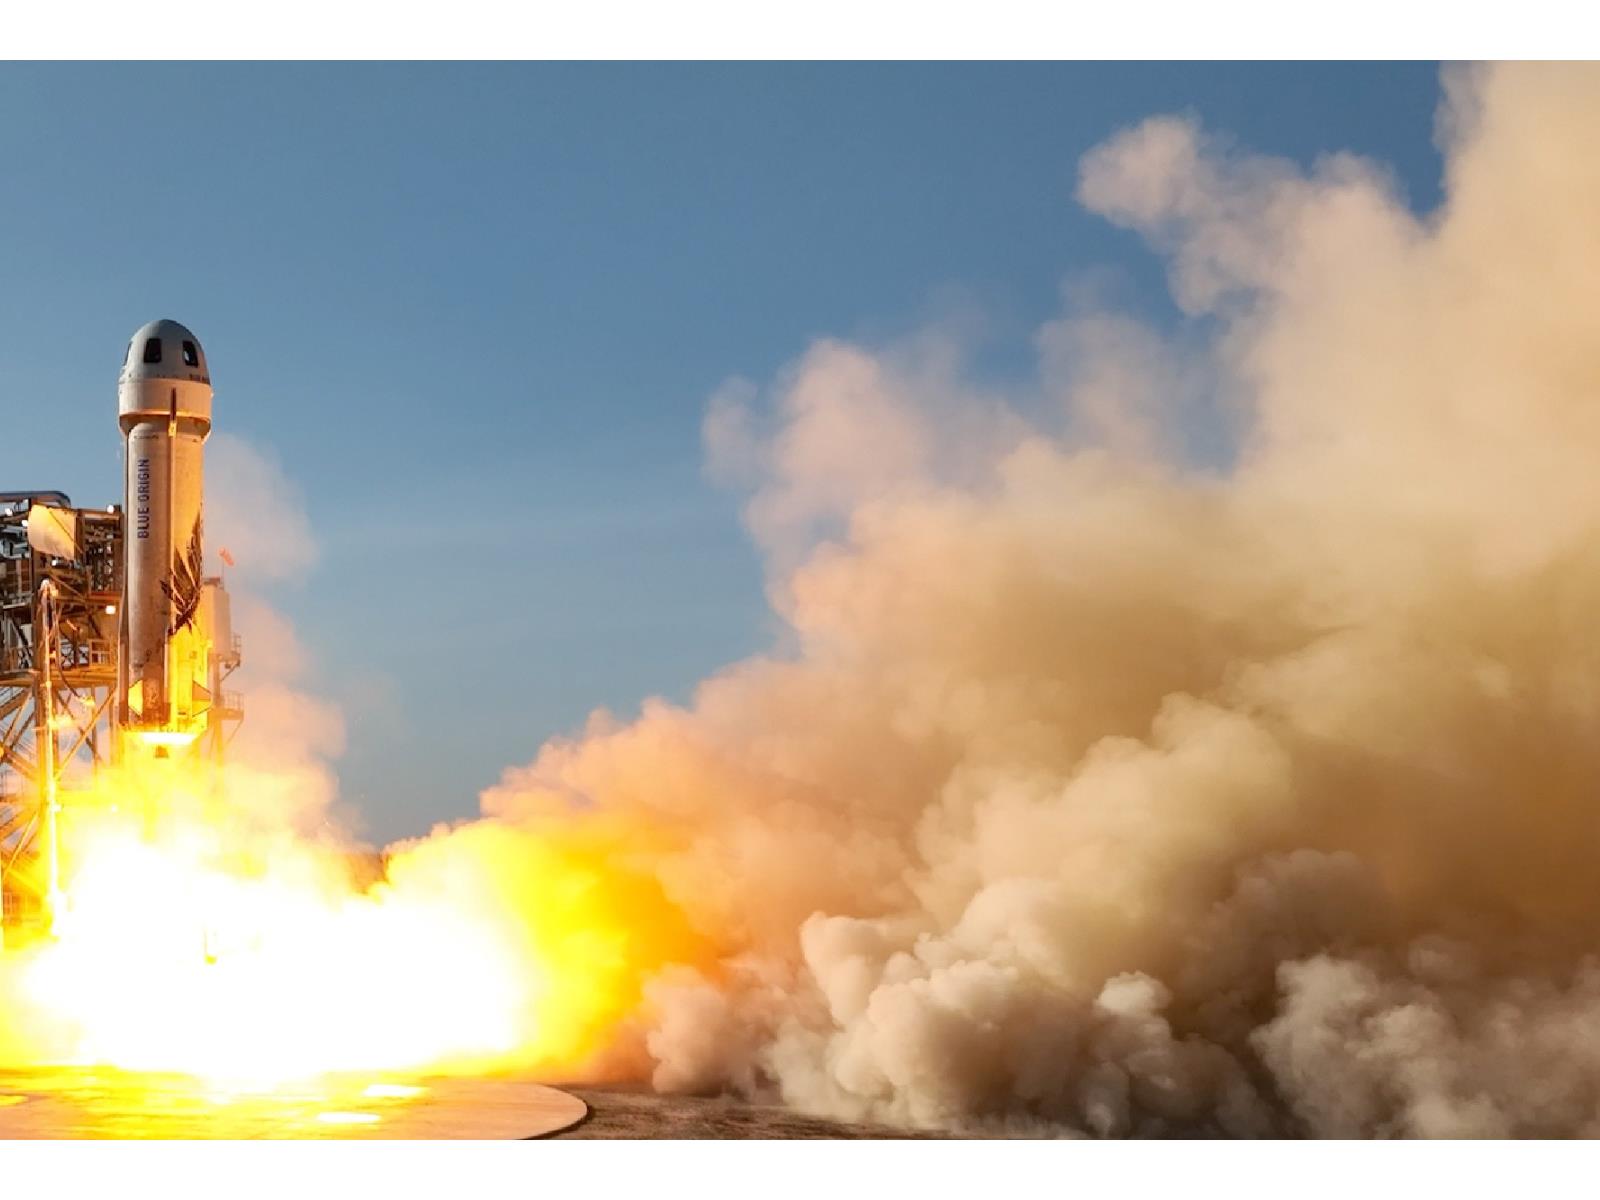
Blue Origin’s New Shepard spacecraft has received a new launch date and time, and you can watch live. New Shepard is the space company’s reusable suborbital rocket system designed to take astronauts and research payloads past the recognized boundary of space.
Mission NS-24 was initially scheduled to launch yesterday, but Blue Origin posted
Source: Hot Hardware – Blue Origin Is Blasting Off To Space After A Yearlong Hiatus And You Can Watch Live
The Mainline Linux Kernel To Finally Support The Google Tensor GS101 SoC & Pixel 6
The Google Tensor GS101 SoC launched in 2021 with the Google Pixel 6 smartphone. More than two years later the mainline Linux kernel is finally to see upstream support with the forthcoming Linux 6.8 kernel cycle…
Source: Phoronix – The Mainline Linux Kernel To Finally Support The Google Tensor GS101 SoC & Pixel 6
Intel IAA Crypto Compression Driver To Be Merged For Linux 6.8
Set to be merged for the upcoming Linux 6.8 kernel cycle is the IAA crypto compression driver for allowing users of the Linux kernel’s compression API to make use of the Intel Analytics Accelerator (IAA) found with Sapphire Rapids and Emerald Rapids Xeon server processors…
Source: Phoronix – Intel IAA Crypto Compression Driver To Be Merged For Linux 6.8
Meta's automated tools removed Israel-Hamas war content that didn't break its rules
Meta’s Oversight Board has published its decision for its first-ever expedited review, which only took 12 days instead of weeks, focusing on content surrounding the Israel-Hamas war. The Board overturned the company’s original decision to remove two pieces of content from both sides of the conflict. Since it supported Meta’s subsequent move to restore the posts on Facebook and Instagram, no further action is expected from the company. However, the Board’s review cast a spotlight on how Meta’s reliance on automated tools could prevent people from sharing important information. In this particular case, the Board noted that “it increased the likelihood of removing valuable posts informing the world about human suffering on both sides of the conflict in the Middle East.”
For its first expedited review, the Oversight Board chose to investigate two particular appeals that represent what the users in the affected region have been submitting since the October 7th attacks. One of them is a video posted on Facebook of a woman begging her captors not to kill her when she was taken hostage during the initial terrorist attacks on Israel. The other video posted on Instagram shows the aftermath of a strike on the Al-Shifa Hospital in Gaza during Israel’s ground offensive. It showed dead and injured Palestinians, children included.
The Board’s review found that the two videos were mistakenly removed after Meta adjusted its automated tools to be more aggressive in policing content following the October 7 attacks. For instance, the Al-Shifa Hospital video takedown and the rejection of a user appeal to get it reinstated were both made without human intervention. Both videos were later restored with warning screens stating that such content is allowed for the purpose of news reporting and raising awareness. The Board commented that Meta “should have moved more quickly to adapt its policy given the fast-moving circumstances, and the high costs to freedom and access to information for removing this kind of content…” It also raised concerns that the company’s rapidly changing approach to moderation could give it an appearance of arbitrariness and could put its policies in question.
That said, the Board found that Meta demoted the content it reinstated with warnning screens. It excluded them from being recommended to other Facebook and Instagram users even after the company determined that they were intended to raise awareness. To note, a number of users had reported being shadowbanned in October after posting content about the conditions in Gaza.
The Board also called attention to how Meta only allowed hostage-taking content from the October 7th attacks to be posted by users from its cross-check lists between October 20 and November 16. These lists are typically made up of high-profile users exempted from the company’s automated moderation system. The Board said Meta’s decision highlights its concerns about the program, specifically its “unequal treatment of users [and] lack of transparent criteria for inclusion.” It said that the company needs “to ensure greater representation of users whose content is likely to be important from a human-rights perspective on Meta’s cross-check lists.”
“We welcome the Oversight Board’s decision today on this case. Both expression and safety are important to us and the people who use our services. The board overturned Meta’s original decision to take this content down but approved of the subsequent decision to restore the content with a warning screen. Meta previously reinstated this content so no further action will be taken on it,” the company told Engadget in a statement. “As explained in our Help Center, some categories of content are not eligible for recommendations and the board disagrees with Meta barring the content in this case from recommendation surfaces. There will be no further updates to this case, as the board did not make any recommendations as part of their decision.”
This article originally appeared on Engadget at https://www.engadget.com/oversight-board-says-metas-automated-tools-took-down-israel-hamas-war-content-that-didnt-break-its-rules-110034154.html?src=rss
Source: Engadget – Meta’s automated tools removed Israel-Hamas war content that didn’t break its rules
Google's multi-state lawsuit settlement will cost it $700 million
On top of fighting (and losing to) Epic Games over Play Store antitrust concerns, Google has been fighting a similar lawsuit filed by 36 states and the District of Columbia in 2021. A settlement for that suit was announced in September, but a judge still had to confirm the terms. Now, Google has announced that it will pay a $700 million fine and make what amounts to fairly minor changes to the Play Store.
Of that sum, Google will distribute $630 million to consumers who may have overpaid for apps or in-app purchases on Google Play (after taxes, lawyers’ fees, etc.). That covers around 102 million people, according to The Washington Post. It will also pay $70 million into a “fund that will be used by the states,” according to Google’s blog.
The other major change is that Google must allow developers to steer consumers toward sideloading to avoid Google’s Play Store fees on subscriptions and the like. It’ll do that via updated “language that informs users about these potential risks of downloading apps directly from the web for the first time.” However, these actions will be time limited to seven years for the sideloading and five years for the updated language, according to settlement’s wording spotted by The Verge.
Google will also include language stating that “OEMs can continue to provide users with options out of the box to use Play or another app store.” Starting with Android 14, third-party stores will be allowed to handle future app updates, including automatic installs. It’s also expanding user choice billing that will allow Android apps and games to offer their own payment system in the US. “Developers are also able to show different pricing options within the app when a user makes a digital purchase,” Google states.
The company will only be required to make these changes for five or six years maximum (seven years for alternate means to download apps). In other words, it could feasibly cut off access to sideloading or third-party app stores after that point, or make it harder for the average consumer to find the option.
Another big thing missing is exterior payment links. “Google is not required to allow developers to include links that take a User outside an app distributed through Google Play to make a purchase,” the settlement agreement reads.
The settlement sum represents a miniscule portion of Google’s turnover and the other terms are relatively minor changes over what it already does. It also doesn’t include Epic Games, which won its own lawsuit against Google earlier this month (Google has vowed to appeal). A court still needs to formally approve the states’ settlement.
Google also argued at its Epic trial that consumers were able to get games by sideloading and other means, but that failed to sway the jury. When the settlement with the states was announced in September, Epic CEO Tim Sweeny said that if it “left the Google tax in place” his company would fight on. “Consumers only benefit if antitrust enforcement not only opens up markets, but also restores price competition,” he said at the time.
This article originally appeared on Engadget at https://www.engadget.com/googles-multi-state-lawsuit-settlement-will-cost-it-700-million-103512109.html?src=rss
Source: Engadget – Google’s multi-state lawsuit settlement will cost it 0 million
Arcan Display Framework Receives Funding As Innovative Wayland Alternative
While much of the focus by Linux desktops as we roll into 2024 is polishing off their Wayland support, there does exist a rather innovative display server out there that’s been in the works for years: Arcan. Arcan is the open-source project built atop a game engine and provides a display server paired with a real-time multimedia framework for audio and video. Arcan can be used from embedded purposes through full desktop solutions and can also interact with Wayland and X11 as well as embracing VR. Arcan 0.6.3 was released today along with the announcement that they’ve taken on some funding…
Source: Phoronix – Arcan Display Framework Receives Funding As Innovative Wayland Alternative
Insomniac Games hackers leak 1.3 million files after demanding $2 million ransom
On December 12, Rhysida, a ransomware group, announced it had taken 1.67 terabytes of data — over 1.3 million files — from Sony’s Insomniac Games and requested $2 million. Now, the one-week deadline for Insomniac Games to pay Rhysida has passed, and the group has made good on its threat to release the stolen information, Cyber Daily reports.
The data includes internal HR documents, screenshots of employees’ Slack conversations, and more, but the main focus is the yet-to-be-released Wolverine video game. The released files contain details about level design, characters and actual screenshots from the game. There’s also a signed publishing agreement between Sony and Marvel that lays out three upcoming X-Men games, the first being Wolverine, with the other two still unnamed. However, it details that Sony — which plans to spend $120 million per game — must release Wolverine by September 1, 2025, with the others due by the end of 2029 and 2033, respectively.
Rhysida claims that it took the group only 20 to 25 minutes to get the domain administrator and that money was their sole motivation. “We knew that developers making games like this would be an easy target,” a Rhysida spokesperson told Cyber Daily. “Sony has launched an investigation, but it would be better in the backyard.”
Notably, Rhysida’s initial ransom notice allowed anyone to bid on the data, not just Insomniac Games, and it appears some of it was bought. The ransomware group stated that any unsold data was released — but only 98 percent of stolen information is publicly available. Rhysida stipulated that any data purchased must not be resold, but who knows if the new owners will follow that rule.
Rhysida only targeted Insomniac Games within Sony, but in May, a separate attack gained access to 6,800 current and former employees’ personal data. The attack, which ransomware group CLOP took credit for, became public knowledge in October.
This article originally appeared on Engadget at https://www.engadget.com/insomniac-games-hackers-leak-13-million-files-after-demanding-2-million-ransom-102134429.html?src=rss
Source: Engadget – Insomniac Games hackers leak 1.3 million files after demanding million ransom