
One version’s edgier than the other. Whether you prefer your Cinnamon in Ubuntu or Debian flavor, the Mint developers have something new for you to try.…
Source: LXer – Mint freshens up its Linux garden for Ubuntu and Debian fans
Monthly Archives: October 2023
3D Printer Uses Magnets To Break Speed Limits
An anonymous reader quotes a report from Tom’s Hardware: Resin printer company Peopoly created quite a buzz with the unveiling of a prototype beltless FDM 3D printer, the Magneto X, at the East Coast RepRap Festival. The new printer is a desk top machine with a huge 400 x 300 x 300 mm build volume and print speeds up to 800mm/s. It borrows a design feature seen on CNC machines: magnetic linear motors. Normally, 3D printers move their components with rotating stepper motors attached to gears and pulleys. The linear motor can be thought of as a flat, unrolled motor with the “rotor” attached to the moving component — the tool head — and the stator forming a track along one axis. Dubbed the “MagXY” system, the tool head seems to levitate across the gantry without obvious means. It has a top print speed of 800 mm/s with a max acceleration of 22,000 mm/s, which would make it faster than modern Core XY printers from Bambu Lab.
Peopoly is using and supporting both Klipper firmware and OrcaSlicer, which founder Mark Peng said greatly helped speed up their development time. […] Peopoly is leaning hard into the Open Source community. Not only have they become backers of Klipper firmware, they are also using — and supporting — Open Source OcraSlicer. The Magneto X’s nozzles are compatible with the popular E3D’s V6 volcano which suggests the machine will be open to modification by users. Peopoly also states its machine can be used without joining a cloud-based system and promises customer data will not be collected.


Read more of this story at Slashdot.
Source: Slashdot – 3D Printer Uses Magnets To Break Speed Limits
TikTok Myth of the Week: ‘Bone Smashing’ Will Make You Beautiful

Welcome to another TikTok Myth of the Week—one that I really, truly wish I were making up. Today we’re talking about “bone smashing,” sometimes known by similar names such as “bone mashing.” It’s when you hit your face with a hammer, but gently. To make yourself prettier.
Source: LifeHacker – TikTok Myth of the Week: ‘Bone Smashing’ Will Make You Beautiful
How to Install Python 3.12 in Ubuntu and Other Linux
Planning to get Python 3.12 installed for your project work? Here’s how to install Python 3.12 in Ubuntu and other Linux distributions.
Source: LXer – How to Install Python 3.12 in Ubuntu and Other Linux
USFWS Is Creating a Frozen Library of Biodiversity To Help Endangered Species
Kiley Price writes via Inside Climate News: In a new initiative announced on Tuesday, the U.S. Fish & Wildlife Service is working with the nonprofit Revive & Restore and other partners to create a “genetic library” of the country’s endangered species — before it’s too late. Through a process called biobanking, FWS field staff are gathering biological samples such as blood, tissues and reproductive cells from animals to be cryogenically preserved at extremely low temperatures (at least -256 degrees Fahrenheit) and stored at a USDA facility in Colorado. The samples will also be genetically sequenced and this information will be uploaded to a publicly available database called GenBank, where researchers can study them and compare their genomes to other members of their species.


Read more of this story at Slashdot.
Source: Slashdot – USFWS Is Creating a Frozen Library of Biodiversity To Help Endangered Species
Kidnapped By a Runaway Electric Car
Long-time Slashdot reader RockDoctor writes: Regardless of their other potential benefits, modern cars, and modern electric cars in particular, involve complex networks of computer code, hardware, and servo systems cooperating (?) to deliver services to the user, like acceleration, steering and braking. Slashdot nerderati know better than most that such complex networks can never show unexpected, non-designed behavior, due to the infallibility of hardware, program coders and system designers… Yeah. Right. “I’ll have some of what he’s been smoking!” That’s Musk-grade optimism.
On Sunday evening, a middle-aged driver in a “brand new” vehicle found it would not decelerate below 30mph (50kmph). He retained steering control, and avoided crashing until police vehicles “boxed in” his vehicle and helped him exit into a police van (most have sliding side doors) from the moving vehicle. The police then “carried out a controlled halt” on the unmanned vehicle, stopping it from driving away with the van’s brakes until a roadside assistance technician arrived 3 hours later and managed to shut it down. “[W]hen the [technician] got to me […] later, he plugged in the car to do a diagnostic check and there was pages of faults,” said the “kidnapped” driver from Glasgow. “He said he had never seen anything like it and decided he was not willing to turn the engine on to see what was wrong.”
By inference, the vehicle did not have a mechanical brake (“hand brake”: English; “parking brake”: American), which should have been able to keep the vehicle halted regardless of the motor’s actions (even if a “clutch” did get burned out). From the only time I’ve been inside an electric car, I can’t say if that is normal; it’s certainly something I’ll look for if I ever rent another. Had the failure happened at 10 a.m. in the morning, not 10 p.m. in the evening, the body count could have been … substantial.
A dumb question, stemming from my only use of an electric car: do they have a weight sensor under the driver’s seat that locks-out the main motor unless there is (say) 30kg in the driver’s seat? Most have some such sensors — they trigger the “seatbelt not fastened” alarm or silence it for empty seats — but whether they can override the drive system … ?


Read more of this story at Slashdot.
Source: Slashdot – Kidnapped By a Runaway Electric Car
[$] LWN.net Weekly Edition for October 5, 2023
The LWN.net Weekly Edition for October 5, 2023 is available.
Source: LWN.net – [$] LWN.net Weekly Edition for October 5, 2023
X starts removing headlines from posted links
Posts on X might look quite different, especially if you mainly follow news and media publications. The website formerly known as Twitter has started removing headlines and snippets from posted links, implementing a change Fortune reported in August. Back then, website owner Elon Musk said that the idea came from him directly and that it will “greatly improve the [platform’s] esthetics.” We tested it out by posting one of our stories, and only the article’s image with an overlay of its URL show up when it’s viewed on iOS. On the web, we still see the article snippet and a truncated version of its headline.
Advertisers reportedly didn’t like the new format when they were shown a preview of it, but the change is clearly still pushing through. X’s main reason for the format switch is apparently to make posts look more compact by fitting more of them in the portion of the timeline that appears on screen. In addition, Musk reportedly thinks that it could help lessen instances of clickbait, which rely on headlines with shock value, on the website.
While Musk publicly claims that the primary driving force for the change in format is the website’s aesthetic, it’s no secret that he’s been trying to encourage more people to post long-form pieces directly on X. The website expanded Blue subscribers’ post limit to 25,000 characters under his leadership, and he previously tweeted that journalists who want “more freedom to write and a higher income” should “publish directly” on the platform. More recently, he encouraged “more citizen journalism” on X and said that people can do “live video easily” from their phone.
This article originally appeared on Engadget at https://www.engadget.com/x-starts-removing-headlines-from-posted-links-011446351.html?src=rss
Source: Engadget – X starts removing headlines from posted links
Today’s NYT Connections Hints (and Answer) for Thursday, October 5, 2023

If you’re looking for the Connections answer for Thursday, October 5, 2023, read on—I’ll share some clues, tips, and strategies, and finally the solutions to all four categories. Beware, there are spoilers below for October 5, NYT Connections #116! Read on if you want some hints (and then the answer) to today’s…
Source: LifeHacker – Today’s NYT Connections Hints (and Answer) for Thursday, October 5, 2023
How to Install OpenMRS on Ubuntu 22.04
OpenMRS is an efficient electronic medical record (EMR) storage and retrieval system released as open-source software. This tutorial will explain how to install OpenMRS on Ubuntu 22.04.
Source: LXer – How to Install OpenMRS on Ubuntu 22.04
Researchers Say Current AI Watermarks Are Trivial To Remove
Researchers from the University of Maryland (UMD) were able to easily evade the current methods of AI watermarking during testing and found it even easier to add fake emblems to images that weren’t generated by AI. “But beyond testing how easy it is to evade watermarks, one UMD team notably developed a watermark that is near impossible to remove from content without completely compromising the intellectual property,” reports Engadget. “This application makes it possible to detect when products are stolen.” From the report: In a similar collaborative research effort (PDF) between the University of California, Santa Barbara and Carnegie Mellon University, researchers found that through simulated attacks, watermarks were easily removable. The paper discerns that there are two distinct methods for eliminating watermarks through these attacks: destructive and constructive approaches. When it comes to destructive attacks, the bad actors can treat watermarks like it’s a part of the image. Tweaking things like the brightness, contrast or using JPEG compression, or even simply rotating an image can remove a watermark. However, the catch here is that while these methods do get rid of the watermark, they also mess with the image quality, making it noticeably worse. In a constructive attack, watermark removal is a bit more sensitive and uses techniques like the good old Gaussian blur.
Although watermarking AI-generated content needs to improve before it can successfully navigate simulated tests similar to those featured in these research studies, it’s easy to envision a scenario where digital watermarking becomes a competitive race against hackers. Until a new standard is developed, we can only hope for the best when it comes to new tools like Google’s SynthID, an identification tool for generative art, which will continue to get workshopped by developers until it hits the mainstream. Further reading: Researchers Tested AI Watermarks — and Broke All of Them


Read more of this story at Slashdot.
Source: Slashdot – Researchers Say Current AI Watermarks Are Trivial To Remove
Japan is studying a reusable rocket, but it won’t fly before 2030
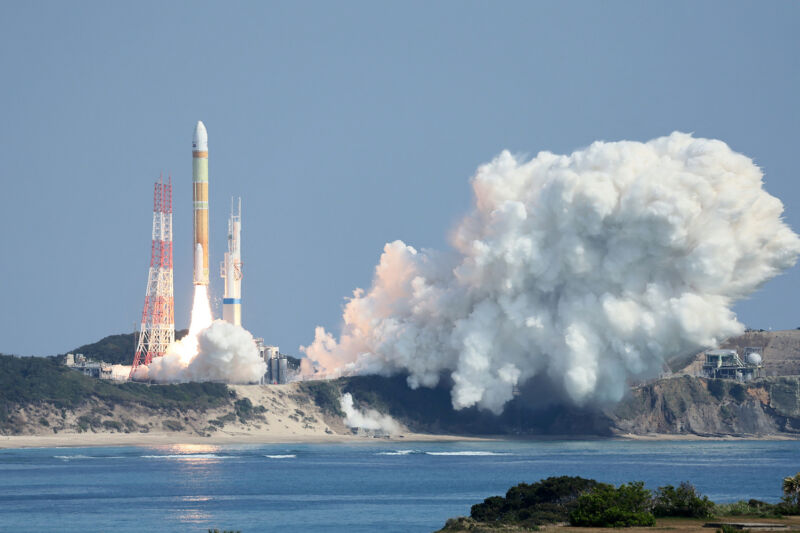
Enlarge / Japan’s first H3 rocket lifted off from the Tanegashima Space Center on a failed test flight in March. (credit: Photo by STR/JIJI Press/AFP via Getty Images)
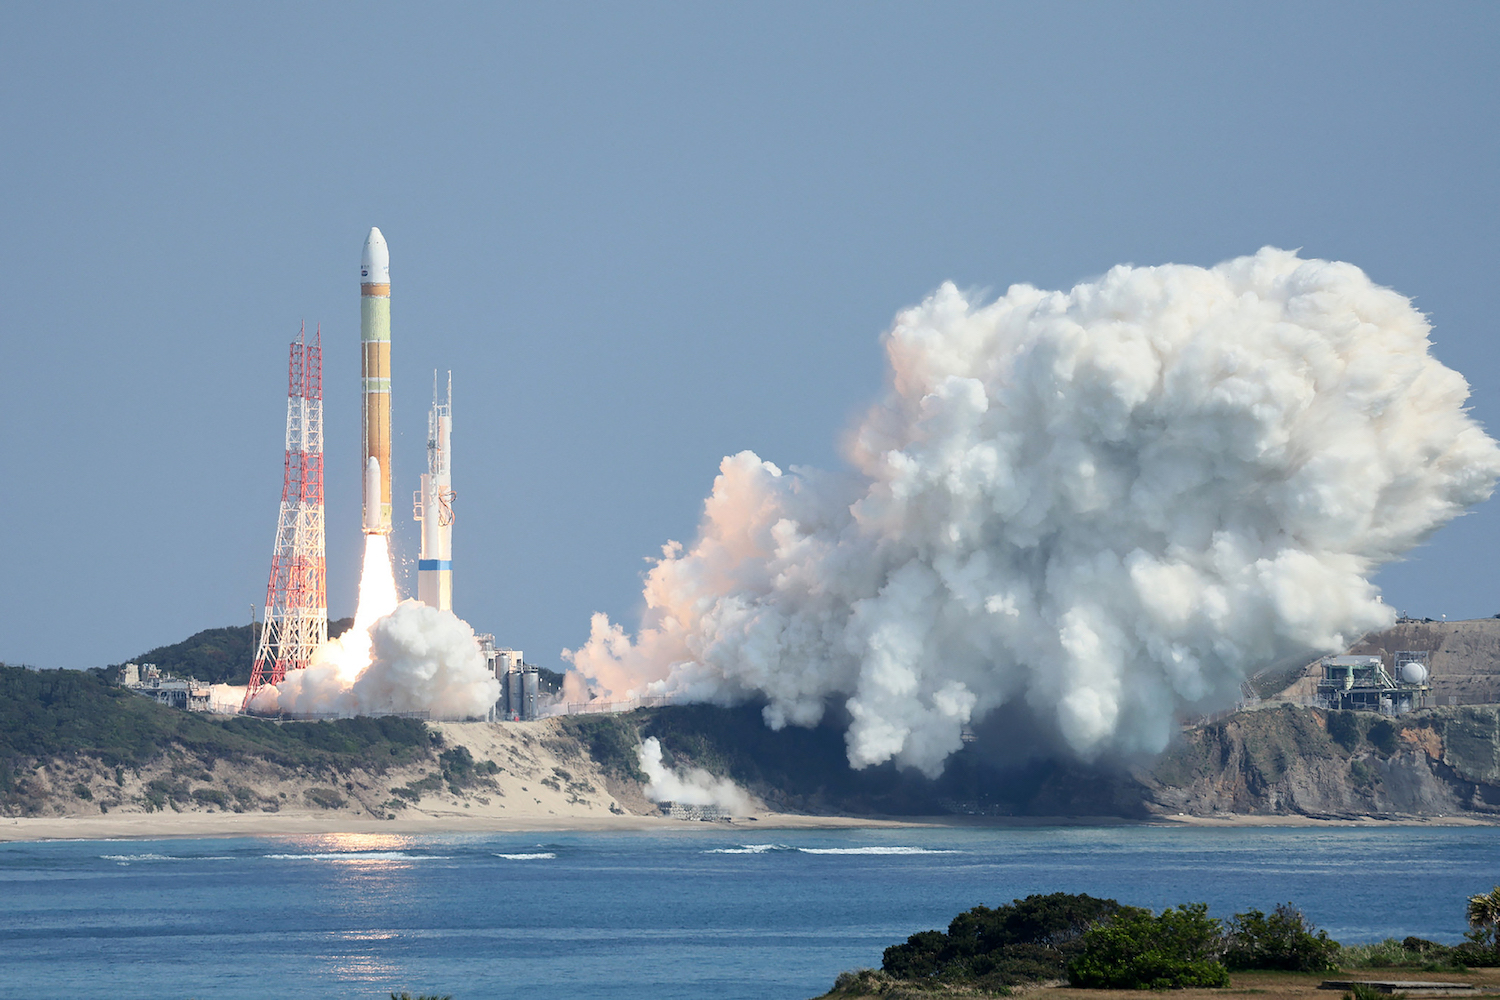
Japan debuted the new flagship H3 rocket in March, capping a decade-long, nearly $1.5 billion development effort to replace a launch vehicle that has been in service for more than 20 years. The H3’s upper stage failed to ignite a few minutes after liftoff, causing the rocket and its Earth observation payload to crash into the Pacific Ocean.
Officials in the Japanese government are already plotting the replacement for the H3 rocket, which had a goal of cutting in half the cost per launch of the H-2A launcher, a workhorse for Japan’s space program. But the H3 is based on a single-use, expendable design, like nearly all legacy rockets. The H3 design aims to achieve these cost savings through modernized manufacturing techniques and commonality in hardware with Japan’s smaller Epsilon rocket family.
The Japanese government updated its basic plan on space policy in June with language endorsing the development of a reusable rocket to follow the H3. Now, the Japan Aerospace Exploration Agency (JAXA) has tapped Mitsubishi Heavy Industries for joint studies on the next-generation launcher, which would have a recoverable and reusable first-stage booster, Space News reported this week.
Read 16 remaining paragraphs | Comments
Source: Ars Technica – Japan is studying a reusable rocket, but it won’t fly before 2030
Linux Tries To Dump Windows' Notoriously Insecure RNDIS Protocol
An anonymous reader quotes a report from ZDNet: Microsoft’s proprietary protocol, Remote Network Driver Interface Specification (RNDIS), started with a good idea. It would enable hardware vendors to add networking support to USB devices without having to build them from scratch. There was only one little problem. RNDIS has no security to speak of. As Greg Kroah-Hartman, the Linux Foundation fellow responsible for stable Linux kernel releases, wrote in November 2022 on the Linux Kernel Mailing List (LKML), “The Microsoft RNDIS protocol is, as designed, insecure and vulnerable on any system that uses it with untrusted hosts or devices. Because the protocol is impossible to make secure, just disable all RNDIS drivers to prevent anyone from using them again.”
He added, in another message, “The protocol was never designed to be used with untrusted devices. It was created, and we implemented support for it, when we trusted USB devices that we plugged into our systems, AND we trusted the systems we plugged our USB devices into.” That’s no longer the case. Kroah-Hartman concluded, “Today, with untrusted hosts and devices, it’s time just to retire this protocol. As I mentioned in the patch comments, Android disabled this many years ago in their devices, with no loss of functionality.”
[…] But now, sick and tired of having a built-in Windows security exploit in Linux, Kroah-Hartman has decided that enough was enough. He’s disabled all the RNDIS protocol drivers in Linux’s Git repository. That means that while the RNDIS code is still in the Linux kernel, if you try to build Linux using this new patch, all your RNDIS drivers will be broken and won’t build. This is one step short of purging RNDIS from Linux.


Read more of this story at Slashdot.
Source: Slashdot – Linux Tries To Dump Windows’ Notoriously Insecure RNDIS Protocol
DIY Tinkerer Invents MacBook Tool That Breaks Apple's Repair Locks
Jason Koebler writes via 404 Media: An independent repair shop in Germany has invented a tool that can break through anti-repair locks Apple has put on a specific sensor on the MacBook Pro and MacBook Air. The Nerd.Tool.1 was invented by Stephan Steins of Dortmund’s Notebook Nerds repair shop. It is specifically designed to allow independent repair shops to replace the display angle sensor on broken MacBook Pro and MacBook Air laptops. This was formerly a replacement that only Apple could do because the replacement part had to be “calibrated” with the specific device, which only Apple could do, until now. This sensor detects when the laptop lid is closed, and turns the screen and fan off, and puts the laptop to sleep. If it’s broken, the laptop’s screen will remain on even when the lid is closed, which drains the battery, can keep the fans running, and generally shorten the life of the computer.
The Nerd.Tool.1 recalibrates replacement sensors, allowing repair techs to replace them without any fuss. “We are calibrating new sensors nearly the same way Apple does,” Steins told me. “They can do it via their T2 [security chip] or their M1/M2 chips. We are using the nerd.tool.1 for this task. The sensor holds all the data. It is not serialized or paired to the logic board so we are just calibrating it.” “We broke Apple’s lock,” independent repair advocate and repair pro Louis Rossmann explained in a YouTube video demoing the Nerd.Tool.1. “To whoever it is at Apple who decided to not make this available to technicians, ‘Fuck you, we win,'” Rossman said.
“We are selling the nerd.tool.1 to be able to spend time in developing other solutions,” added Steins. “We will do our best to get nerd.tool.2 to fix other issues which repair shops are facing. The response has been awesome! The community is very kind, which shows how painful these missing tools are for many independent repair shops.”


Read more of this story at Slashdot.
Source: Slashdot – DIY Tinkerer Invents MacBook Tool That Breaks Apple’s Repair Locks
Quantum Leap's Exec Producer Teases Season 2's Time-Travel Adventures

Quantum Leap returns to NBC this week to catch up with Dr. Ben Song (Raymond Lee), a time-traveler who has no control over where or when he’s going to end up next, but who fortunately has the help of a Los Angeles-based team of badasses and geniuses helping him through each mission.
Source: Gizmodo – Quantum Leap’s Exec Producer Teases Season 2’s Time-Travel Adventures
California's Reservoirs Runneth Over in Astounding Reversal From Last Year

A stormy, wet year for California has brought its perilously depleted reservoirs back to life. The state’s “water year” ended this past Saturday, with officials noting that reservoirs throughout California are at 128% of their historical average, the Associated Press reports.
Source: Gizmodo – California’s Reservoirs Runneth Over in Astounding Reversal From Last Year
Gmail Unleashes 'Email Emoji Reactions' Onto an Unsuspecting World
An anonymous reader quotes a report from Ars Technica: You can now reply to an email just like it’s an instant messaging chat, tacking on a “crying laughing” emoji to an email instead of replying. Google has a whole support article detailing the new feature, which allows you to “express yourself and quickly respond to emails with emojis.” Like a messaging app, a row of emoji reaction counts will appear below your email now, and other people on the thread can tap to add to the reaction count. Currently, it’s only on the Android Gmail app, but it’s presumably coming to other Gmail clients.
Of course, email is from the 1970s and does not natively support emoji reactions. That makes this a Gmail-proprietary feature, which is a problem for federated emails that are expected to work with a million different clients and providers. If you send an emoji reaction and someone on the email chain is not using an official Gmail client, they will get a new, additional email containing your singular reactive emoji. Google is not messing with the email standard, so people not using Gmail will be the most affected.
Another weird quirk is that because emoji reactions are just emails (that Gmail sends to other clients and hides for itself), any emoji reactions you send can’t be taken back. There’s only Gmail’s “Undo send” feature for taking back reactions, which delays sending emails for about 30 seconds, so you can second-guess yourself. After that, you’re creating a permanent emoji reaction paper trail. […] If the idea of emoji reactions to email has you selecting the puke emoji, as far as we can tell, there’s no way to just turn this off. The report notes that this new feature won’t work on business or school accounts. “Emoji reactions also aren’t available for group email lists, messages with more than 20 recipients, emails on which you’re BCC’d, encrypted emails, and emails where the sender has a custom reply-to address.”


Read more of this story at Slashdot.
Source: Slashdot – Gmail Unleashes ‘Email Emoji Reactions’ Onto an Unsuspecting World
Jonathan Majors' Role in the MCU Remains Unchanged in Loki Season 2

Jonathan Majors’ trial starts this month just as Loki season two is set to debut on Disney+, but the actor’s place in the Marvel Cinematic Universe remains unchanged for now.
Source: Gizmodo – Jonathan Majors’ Role in the MCU Remains Unchanged in Loki Season 2
Richard Stallman in Prague: Unyielding Spirit Amidst Health Challenges
The Free Software community witnessed a blend of resilience and unwavering dedication as Richard Stallman made a poignant appearance at the Hackers Congress Paralelní Polis 2023 in Prague on October 1, 2023. Despite battling a severe health condition, Stallman’s presence at the congress underscored his enduring commitment to the Free Software ideology.
Source: LXer – Richard Stallman in Prague: Unyielding Spirit Amidst Health Challenges
Vulnerabilities in Supermicro BMCs could allow for unkillable server rootkits
Enlarge (credit: Getty Images)
If your organization uses servers that are equipped with baseboard management controllers from Supermicro, it’s time, once again, to patch seven high-severity vulnerabilities that attackers could exploit to gain control of them. And sorry, but the fixes must be installed manually.
Typically abbreviated as BMCs, baseboard management controllers are small chips that are soldered onto the motherboard of servers inside data centers. Administrators rely on these powerful controllers for various remote management capabilities, including installing updates, monitoring temperatures and setting fan speeds accordingly, and reflashing the UEFI system firmware that allows servers to load their operating systems during reboots. BMCs provide these capabilities and more, even when the servers they’re connected to are turned off.
Code execution inside the BMC? Yup
The potential for vulnerabilities in BMCs to be exploited and used to take control of servers hasn’t been lost on hackers. In 2021, hackers exploited a vulnerability in BMCs from HP Enterprise and installed a custom rootkit, researchers from Amnpardaz, a security firm in Iran, reported that year. ILObleed, as the researchers named the rootkit, hid inside the iLO, a module in HPE BMCs that’s short for Integrated Lights-Out.
Read 13 remaining paragraphs | Comments
Source: Ars Technica – Vulnerabilities in Supermicro BMCs could allow for unkillable server rootkits