Comcast Keeps Losing Customers Despite Price Guarantee, Unlimited Data

Comcast’s attempt to slow broadband customer losses still isn’t stopping the bleeding as fiber and fixed wireless competition intensifies. In Q4 2025 alone, Comcast lost 181,000 broadband subscribers, even as it leans harder into wireless bundling and other business lines like Peacock and theme parks. Ars Technica reports: The Q4 net loss is more than the 176,000 loss predicted by analysts, although not as bad as the 199,000-customer loss that spurred [Comcast President Mike Cavanagh’s] comment about Comcast “not winning in the marketplace” nine months ago. The Q4 2025 loss reported today is also worse than the 139,000-customer loss in Q4 2024 and the 34,000-customer loss in Q4 2023.

“Subscriber losses were 181,000, as the early traction we are seeing from our new initiatives was more than offset by continued competitive intensity,” Comcast CFO Jason Armstrong said during an earnings call today, according to a Motley Fool transcript. Comcast’s residential broadband customers dropped to 28.72 million, while business broadband customers dropped to 2.54 million, for a total of 31.26 million.

Armstrong said that average revenue per user grew 1.1 percent, “consistent with the deceleration that we had previewed reflecting our new go-to-market pricing, including lower everyday pricing and strong adoption of free wireless lines.” Armstrong expects average revenue per user to continue growing slowly “for the next couple of quarters, driven by the absence of a rate increase, the impact from free wireless lines, and the ongoing migration of our base to simplified pricing.” Comcast Connectivity & Platforms chief Steve Croney said the firm is facing “a more competitive environment from fiber” and continued competition from fixed wireless. “The market is going to remain intensely competitive,” he said.


Read more of this story at Slashdot.

Cory Doctorow On Tariffs and the DMCA In Canada

Longtime Slashdot reader devnulljapan writes: In 2012, Canada passed anti-circumvention law Bill C-11, cut-and-pasted from the U.S. DMCA, in return for access to U.S. markets without tariffs. Trump has tariffed Canada anyway, so Cory Doctorow suggests it sounds like like a good idea to ditch Bill C-11 and turn Canada into a “Disenshittification Nation” and go into the business of “disenshittify[ing] America’s defective tech exports.” Some of the specific ways Canada could respond include legalize jailbreaking, allow alternative app stores/clients, force companies to offer repair tools, and open firmware that break monopoly lock-ins. Cory’s pitch is equal parts economic strategy (capture the rents Big Tech extracts) and national security (reduce dependence on U.S. tech stacks that can be switched off or weaponized).


Read more of this story at Slashdot.

Linux Gaming Developers Join Forces To Form the Open Gaming Collective

A group of Linux gaming-focused distros and developers have formed the Open Gaming Collective to pool work on shared components like kernels, input systems, and Valve tooling. The Verge reports: Universal Blue, developer of the gaming-focused Linux distribution Bazzite, announced on Wednesday that its helping to form the OGC with several other groups, which will collaborate on improvements to the Linux gaming ecosystem and âoecentralize efforts around critical components like kernel patches, input tooling, and essential gaming packages such as gamescope.” The other founding members of the OGC include Nobara, ChimeraOS, Playtron, Fyra Labs, PikaOS, ShadowBlip, and Asus Linux.

[…] It’s worth noting that this will mean some changes to Bazzite, which is switching to the OGC kernel, replacing HHD with InputPlumber as its input framework, and integrating features like RGB and fan control into the Steam UI. Bazzite also added that, “We’ll be sharing patches we’ve made to various Valve packages with the OGC and attempting to upstream everything we can.”


Read more of this story at Slashdot.

An AI Toy Exposed 50K Logs of Its Chats With Kids To Anyone With a Gmail Account

An anonymous reader quotes a report from Wired: Earlier this month, Joseph Thacker’s neighbor mentioned to him that she’d preordered a couple of stuffed dinosaur toys for her children. She’d chosen the toys, called Bondus, because they offered an AI chat feature that lets children talk to the toy like a kind of machine-learning-enabled imaginary friend. But she knew Thacker, a security researcher, had done work on AI risks for kids, and she was curious about his thoughts.

So Thacker looked into it. With just a few minutes of work, he and a web security researcher friend named Joel Margolis made a startling discovery: Bondu’s web-based portal, intended to allow parents to check on their children’s conversations and for Bondu’s staff to monitor the products’ use and performance, also let anyone with a Gmail account access transcripts of virtually every conversation Bondu’s child users have ever had with the toy.

Without carrying out any actual hacking, simply by logging in with an arbitrary Google account, the two researchers immediately found themselves looking at children’s private conversations, the pet names kids had given their Bondu, the likes and dislikes of the toys’ toddler owners, their favorite snacks and dance moves. In total, Margolis and Thacker discovered that the data Bondu left unprotected — accessible to anyone who logged in to the company’s public-facing web console with their Google username — included children’s names, birth dates, family member names, “objectives” for the child chosen by a parent, and most disturbingly, detailed summaries and transcripts of every previous chat between the child and their Bondu, a toy practically designed to elicit intimate one-on-one conversation. More than 50,000 chat transcripts were accessible through the exposed web portal. When the researchers alerted Bondu about the findings, the company acted to take down the console within minutes and relaunched it the next day with proper authentication measures.

“We take user privacy seriously and are committed to protecting user data,” Bondu CEO Fateen Anam Rafid said in his statement. “We have communicated with all active users about our security protocols and continue to strengthen our systems with new protections,” as well as hiring a security firm to validate its investigation and monitor its systems in the future.


Read more of this story at Slashdot.

Apple just reported its best-ever quarter for iPhone sales

Apple shared its latest quarterly financial results today and the news is once again very, very good for the Cupertino company. The quarter ending December 27, 2025 marked “the best-ever quarter” for iPhones, which generated a record high revenue of nearly $85.27 billion for the business. Apple doesn’t disclose the number of devices sold any more, but even with the prices for many of its latest generation of smartphones surpassing $1,000 a pop, that’s still got to be a heck of a lot of iPhones. 

“The demand for iPhone was simply staggering,” CEO Tim Cook said on the conference call to discuss the results. “This is the strongest iPhone lineup we’ve ever had and by far the most popular.”

That wasn’t the only massive number in the earnings report. Services revenue also logged its biggest quarter yet, growing 14 percent over the same period last year to reach just over $30 billion. It was also Apple’s biggest quarter to date for total revenue, which was nearly $143.76 billion for the already fabulously wealthy company.

This article originally appeared on Engadget at https://www.engadget.com/mobile/smartphones/apple-just-reported-its-best-ever-quarter-for-iphone-sales-234135513.html?src=rss

Having that high-deductible health plan might kill you, literally

Having a health insurance plan with a high deductible could not only cost you—it could also kill you.

A new study in JAMA Network Open found that people who faced those high out-of-pocket costs as well as a cancer diagnosis had worse overall survival and cancer-specific survival than those with more standard health plans.

The findings, while perhaps not surprising, are a stark reminder of the fraught decisions Americans face as the price of health care only continues to rise, and more people try to offset costs by accepting insurance plans with higher deductibles—that is, higher out-of-pocket costs they have to pay before their health insurance provider starts paying its share.

Read full article

Comments

US spy satellite agency declassifies high-flying Cold War listening post

The National Reconnaissance Office, the agency overseeing the US government’s fleet of spy satellites, has declassified a decades-old program used to eavesdrop on the Soviet Union’s military communication signals.

The program was codenamed Jumpseat, and its existence was already public knowledge through leaks and contemporary media reports. What’s new is the NRO’s description of the program’s purpose, development, and pictures of the satellites themselves.

In a statement, the NRO called Jumpseat “the United States’ first-generation, highly elliptical orbit (HEO) signals-collection satellite.”

Read full article

Comments

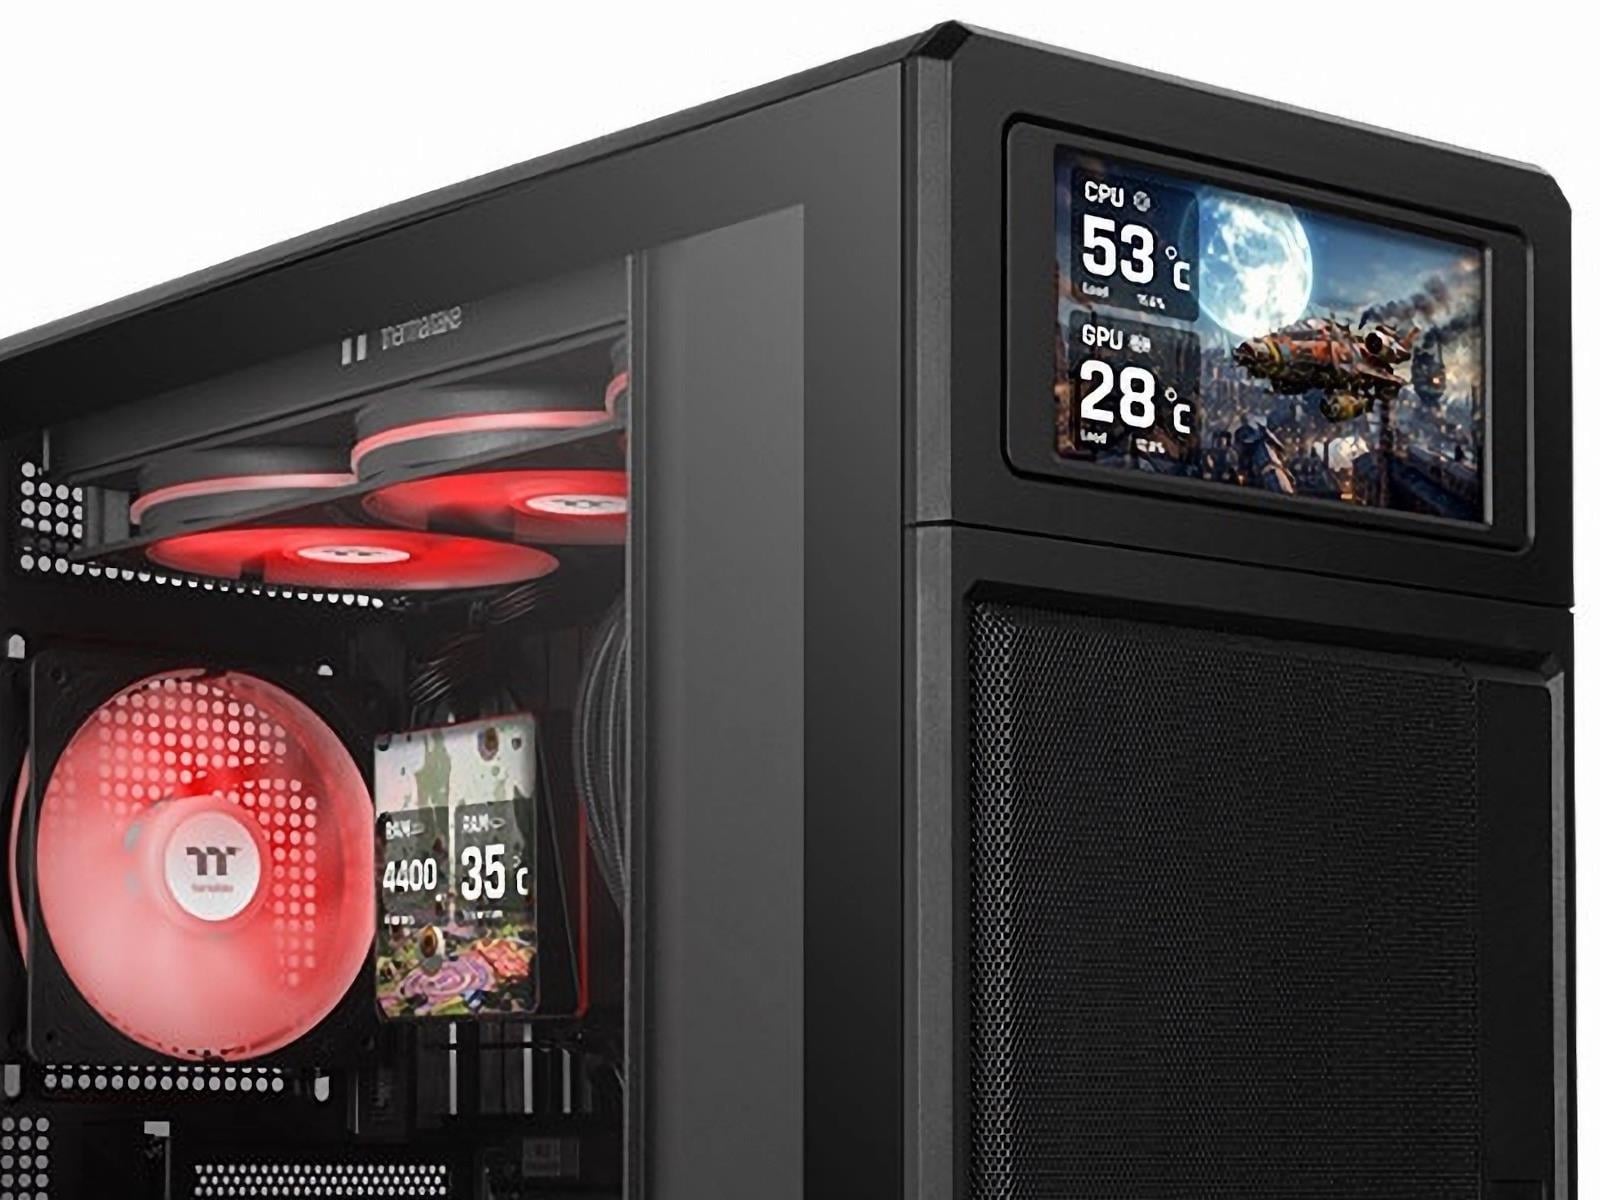
Thermaltake TR300 Case Brings A Front PSU Mount And Big Display To Gaming PCs

Thermaltake TR300 Case Brings A Front PSU Mount And Big Display To Gaming PCs
With its latest TR300 Series TG (and WS) cases, Thermaltake includes a 6-inch 1480 x 720 display for users that want to take their customization to the next level. We’ve seen case mods integrate mini-monitor before, and ASRock even sold an entire 1080p monitor made to be attached to your case, but this is one of the more practical solutions

Amazon discovered a ‘high volume’ of CSAM in its AI training data but isn’t saying where it came from

The National Center for Missing and Exploited Children said it received more than 1 million reports of AI-related child sexual abuse material (CSAM) in 2025. The “vast majority” of that content was reported by Amazon, which found the material in its training data, according to an investigation by Bloomberg. In addition, Amazon said only that it obtained the inappropriate content from external sources used to train its AI services and claimed it could not provide any further details about where the CSAM came from. 

“This is really an outlier,” Fallon McNulty, executive director of NCMEC’s CyberTipline, told Bloomberg. The CyberTipline is where many types of US-based companies are legally required to report suspected CSAM. “Having such a high volume come in throughout the year begs a lot of questions about where the data is coming from, and what safeguards have been put in place.” She added that aside from Amazon, the AI-related reports the organization received from other companies last year included actionable data that it could pass along to law enforcement for next steps. Since Amazon isn’t disclosing sources, McNulty said its reports have proved “inactionable.”

“We take a deliberately cautious approach to scanning foundation model training data, including data from the public web, to identify and remove known [child sexual abuse material] and protect our customers,” an Amazon representative said in a statement to Bloomberg. The spokesperson also said that Amazon aimed to over-report its figures to NCMEC in order to avoid missing any cases. The company said that it removed the suspected CSAM content before feeding training data into its AI models. 

Safety questions for minors have emerged as a critical concern for the artificial intelligence industry in recent months. CSAM has skyrocketed in NCMEC’s records; compared with the more than 1 million AI-related reports the organization received last year, the 2024 total was 67,000 reports while 2023 only saw 4,700 reports. 

In addition to issues such as abusive content being used to train models, AI chatbots have also been implicated in several dangerous or tragic cases involving young users. OpenAI and Character.AI have both been sued after teenagers planned their suicides with those companies’ platforms. Meta is also being sued for alleged failures to protect teen users from sexually explicit conversations with chatbots.

This article originally appeared on Engadget at https://www.engadget.com/ai/amazon-discovered-a-high-volume-of-csam-in-its-ai-training-data-but-isnt-saying-where-it-came-from-224749228.html?src=rss

People complaining about Windows 11 hasn’t stopped it from hitting 1 billion users

Complaining about Windows 11 is a popular sport among tech enthusiasts on the Internet, whether you’re publicly switching to Linux, publishing guides about the dozens of things you need to do to make the OS less annoying, or getting upset because you were asked to sign in to an app after clicking a sign-in button.

Despite the negativity surrounding the current version of Windows, it remains the most widely used operating system on the world’s desktop and laptop computers, and people usually prefer to stick to what they’re used to. As a result, Windows 11 has just cleared a big milestone—Microsoft CEO Satya Nadella said on the company’s most recent earnings call (via The Verge) that Windows 11 now has over 1 billion users worldwide.

Windows 11 also reached that milestone just a few months quicker than Windows 10 did—1,576 days after its initial public launch on October 5, 2021. Windows 10 took 1,692 days to reach the same milestone, based on its July 29, 2015, general availability date and Microsoft’s announcement on March 16, 2020.

Read full article

Comments

Nvidia GeForce NOW Is Now Available Natively On Linux

NVIDIA has officially launched a native GeForce NOW client for Linux as a Flatpak, giving Linux gamers access to cloud-rendered RTX gaming. Phoronix reports: While confined to a Flatpak, for now NVIDIA is just “officially” supporting it on Ubuntu 24.04 LTS and later. Granted, thanks to Flatpak it should run on other non-Ubuntu distributions too but in terms of the official support and where they are qualifying their builds they are limiting it just to Ubuntu 24.04 LTS and later. […] At launch the Flatpak build is also just for x86_64 Linux with no AArch64 Linux builds or similar at this time.

Running GeForce NOW on Linux while games are rendered in NVIDIA’s cloud with Blackwell GPUs, you still need to be using a modern GPU with H.264 or H.265 Vulkan Video support NVIDIA isn’t yet supporting Vulkan Video AV1 with GeForce NOW on Linux but just H.264/H.265. If you are using NVIDIA graphics the NVIDIA R580 series or newer is recommended while using the X.Org session. If you are using Intel or AMD Radeon graphics, Mesa 24.2+ is recommended and using the Wayland session.

When you are up and running with GeForce NOW on Linux, you have access to over 4,500 games. The free tier of GeForce NOW provides standard access to the gaming servers and limited session caps for an introductory-level experience. It’s with the performance tier where you can enjoy RTX ray-tracing and 1440p @ 60 FPS performance and up to six hour sessions. With GeForce NOW’s Ultimate tier is where you are running on GeForce RTX 5080 GPU servers with support for up to 5K @ 120 FPS gaming or 1080p @ 360 FPS with up to eight hour gaming sessions in length.


Read more of this story at Slashdot.

Thief VR: Legacy of Shadow Refines Gameplay Mechanics In Latest Update

In its fourth major update since release, Thief VR: Legacy of Shadow refines its gameplay mechanics for a smoother experience.

Available now on all major platforms, Thief VR: Legacy of Shadow launched its 4.0 update, focusing on refining the gameplay experience for an overall smoother feel. As its 3.0 patch was released just shy of two weeks ago, it is clear developer Maze Theory and publisher Vertigo Games are on top of things, quick to apply any feedback shared to deliver a better game. Other improvements include more flexible customization options for the Steam version, such as higher-quality dynamic shadows and character models, and general quality-of-life bug fixes.

One of the flagship upgrades to this new patch is revamped crouch mechanics. As a marquee ability, players are supposed to spend a lot of time doing so while hiding in the shadows. While never broken since its initial release, it did feel that certain aspects of the game could have done with more time in the oven, as we mentioned in our review: “Sometimes objects fail to load in properly, like a treasure chest going transparent whenever I face it from the front—or an entire basement visually deloading momentarily if I walk too close to an adjoining wall.”

0:00

/0:38

A gameplay video recorded by UploadVR showcasing patch 4.0.

Previous upgrades mainly brought visual improvements and continued stability to the experience. No DLC or sequel has been mentioned as yet, but this ongoing support is at least a step in the right direction.

Thief VR: Legacy of Shadow is available now on Meta Quest, PlayStation VR2, and Steam.

Official Firefox RPM Package Now Available for Fedora-Style Linux Distributions

Mozilla has taken a notable step toward improving Firefox distribution on Linux. An official Firefox RPM package is now available directly from Mozilla for Fedora-style distributions, including Fedora, RHEL-compatible systems, and related derivatives. This move gives users a new, upstream-supported option for installing and maintaining Firefox without relying solely on distro-maintained builds.

Lord Of The Rings Sauron’s Helmet Gets An Official LEGO Set

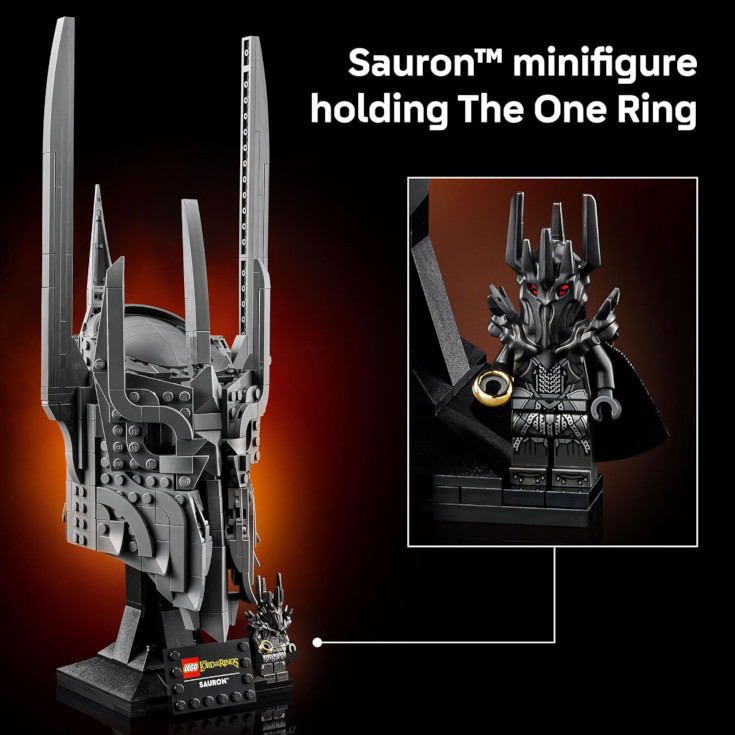
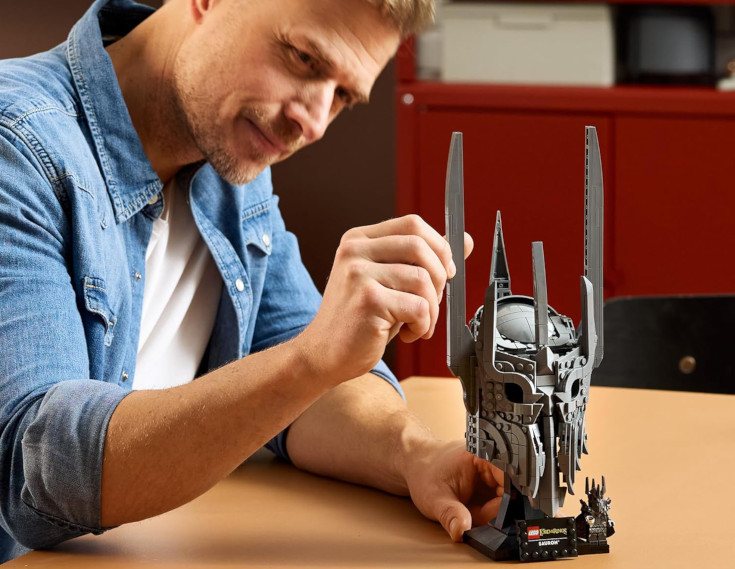
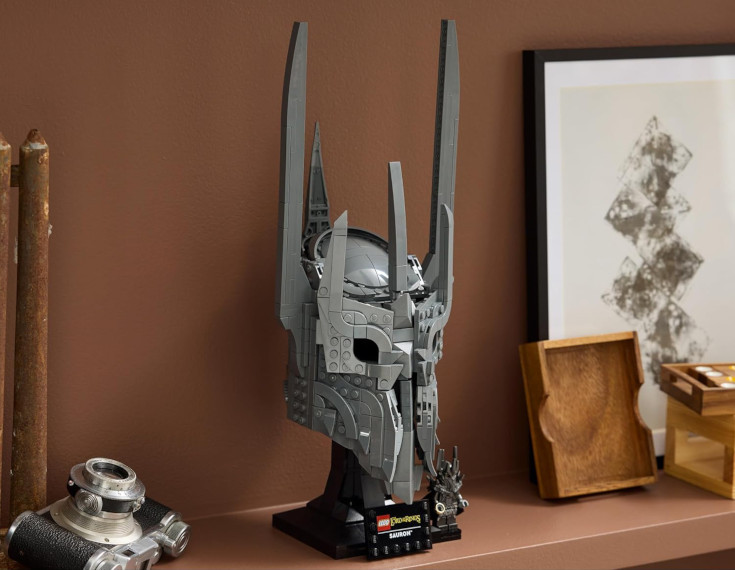
Because printing money is easy for some companies, LEGO has announced an official Lord Of The Rings Sauron’s Helmet build set. The kit will be released March 1st for $70 and include 538 pieces, including a Sauron minfig holding the One Ring. Honestly, $70 is still expensive, but after all the $200 and $300 sets they’ve been releasing lately it almost seems like a steal. It isn’t though, just to be clear. When completed (provided you didn’t eat any crucial pieces), the set makes a 13″ x 5″ replica of Sauron’s helmet. And what a helmet it is! Has anybody ever cosplayed as sloppy Sauron and made a Sauron beer helmet? Because that’s a convention-stealing cosplay idea right there. If you use it though I get half the costume contest prize money.

How often do AI chatbots lead users down a harmful path?

At this point, we’ve all heard plenty of stories about AI chatbots leading users to harmful actions, harmful beliefs, or simply incorrect information. Despite the prevalence of these stories, though, it’s hard to know just how often users are being manipulated. Are these tales of AI harms anecdotal outliers or signs of a frighteningly common problem?

Anthropic took a stab at answer ingthat question this week, releasing a paper studying the potential for what it calls “disempowering patterns” across 1.5 million anonymized real-world conversations with its Claude AI model. While the results show that these kinds of manipulative patterns are relatively rare as a percentage of all AI conversations, they still represent a potentially large problem on an absolute basis.

A rare but growing problem

In the newly published paper “Who’s in Charge? Disempowerment Patterns in Real-World LLM Usage,” researchers from Anthropic and the University of Toronto try to quantify the potential for a specific set of “user disempowering” harms by identifying three primary ways that a chatbot can negatively impact a user’s thoughts or actions:

Read full article

Comments

How YouTube Is Fighting Back Against AI Slop

Science fiction and science leaders alike have warned us that artificial intelligence may one day take over the world, but until those predictions come to pass, generative AI’s biggest impact on my life has been overloading my social media feeds with slop. It seems I can’t open TikTok, Instagram, or YouTube without running smack into bizarre and troubling AI concoctions featuring babies in danger and cats having affairs. It really is the wild west (or maybe Westworld) out there.

I think few among us really believe these videos are any good, and it’s pretty obvious they aren’t good for us, or for the world. Short-form video is already numbing enough, but this AI content is generally completely devoid of any meaning or substance. And yet, it’s everywhere. I haven’t spent too much time on YouTube Shorts recently, but in my limited experience, the feed has been chock full of AI, especially if I’m logged out of my personal account.

Still, if you’re a dedicated YouTube Shorts user (or a frequent YouTube user in general) you might have noticed something odd in recent days: There don’t seem to be quite as many AI videos on the platform right now. There are still a lot, don’t get me wrong, but it turns out YouTube has recently taken action to remove some of its AI content—the sloppiest of the slop.

YouTube’s war on AI slop

Android Police spotted the development on Wednesday, basing its findings on a November report from Kapwing, a company that develops an online video editor. Kapwing investigated AI slop across YouTube’s vast content library, noting the top 100 most-subscribed YouTube channels that publish this sort of AI content. In the two months since that report, Android Police noticed that 16 of those 100 channels are no longer with us.

That includes the most popular AI channel on YouTube, at least according to Kapwing. “CuentosFacianantes” had 5.95 million subscribers at the time of their initial report, and produced AI-generated shorts inspired by Dragon Ball. The channel had amassed roughly 1.28 billion views by the end of last year; despite launching in 2020, it had curated its library to begin Jan. 8, 2025, so those numbers were racked up pretty recently. The number two channel, “Imperio de Jesus” with 5.87 million subscribers, and the number seven channel “Super Cat League,” with 4.21 million subscribers, were also shut down.

According to Android Police, the 16 channels in question had a total of 35 million subscribers and over 4.7 billion views across their collective videos. Some of these channels are completely gone, while others simply have had their videos removed.

Why is YouTube removing AI slop?

YouTube CEO Neal Mohan published a post on Jan. 21 of this year describing the company’s vision for 2026. Towards the end of that letter, he acknowledges AI content, predicting that, “AI will be a boon to the creatives who are ready to lean in,” and comparing it to tools like Photoshop and CGI, adding “AI will remain a tool for expression, not a replacement.” However, Mohan was also critical of the technology, noting that it’s becoming more difficult to tell real videos from AI. He notes that YouTube is now removing “any harmful synthetic media that violates our Community Guidelines,” and is giving creators tools to help identify and block deepfakes.

More interestingly, the letter includes a section labeled “Managing AI slop,” which is the first time I’ve seen a company like YouTube use that expression. Mohan says that YouTube’s goal is to be a place where free expression thrives, but also a place “where people feel good spending their time.” To that point, he says, “To reduce the spread of low quality AI content, we’re actively building on our established systems that have been very successful in combatting spam and clickbait, and reducing the spread of low quality, repetitive content.”

Mohan doesn’t call out any accounts by name, nor does he acknowledge the accounts and content the company has already deleted, but it’s a clear line in the sand: YouTube is not against AI-generated content, but it will remove low-quality AI content it feels is, well, slop. That’s good news for anyone who uses YouTube (so, pretty much everyone), even if it’s far from a cure for the growing problem.

I’ve reached out to YouTube for comment on this story, and will update this piece if I hear back.