
It sounds too good to be true
The post Valve Says Its New Console Plays The ‘Majority’ Of Steam Games At 4K 60FPS With FSR appeared first on Kotaku.
It sounds too good to be true
The post Valve Says Its New Console Plays The ‘Majority’ Of Steam Games At 4K 60FPS With FSR appeared first on Kotaku.
Following December’s release of COSMIC Epoch 1 along with the Pop!_OS 24.04 release by System76, today they shared more of their feature plans for the next two major COSMIC desktop updates…
Ahead of the imminent GNOME 50 beta release, the GNOME Shell and Mutter components have declared their “50.beta” releases to ship the latest bug fixes, memory leak fixes, and some last minute improvements ahead of the stable release in March…

The console-like gaming PCs won’t be coming in early 2026 as originally planned
The post The AI-Fueled PC Gaming Shortage Just Delayed Valve’s Steam Machine appeared first on Kotaku.
Microsoft has finally delivered on its promise to integrate Sysmon — the long-standing system monitoring tool from its Sysinternals suite — directly into Windows, a move that should make life considerably easier for enterprise administrators who have struggled with deploying and managing the utility across thousands of endpoints.
The functionality landed this week in Windows Insider builds 26300.7733 (Dev channel) and 26220.7752 (Beta channel). Sysmon allows administrators to capture system events through custom configuration files, filter for specific activity, and pipe the data into standard Windows event logs for pickup by security tools and SIEM pipelines. Mark Russinovich, Microsoft technical fellow and Winternals co-founder, has previously noted the lack of official customer support for Sysmon in production environments — a gap this integration addresses. The feature ships disabled by default and requires PowerShell to enable. Microsoft notes that any existing Sysmon installation must be uninstalled before activating the built-in version.


Read more of this story at Slashdot.
Inside this week’s LWN.net Weekly Edition:
The Document Foundation released LibreOffice 26.2 today as a major update for this open-source, free, and cross-platform office suite software for GNU/Linux, macOS, and Windows systems.
Because who likes changing gears to make climbing hills easier anyways, this is a video of Sergii Gordieiev of Youtube channel The Q replacing a bicycle chain with a series of 3D printed gears, effectively making it a single speed. So is that an upgrade or a downgrade? I suppose that depends on who you ask, but if you ask me life is a lot like learning to ride a bike: you fall and get hurt a lot while your neighbors laugh and throw empty beer cans.
An unofficial port of the Rare-made N64 classic first-person shooter Perfect Dark is well underway.
Created by Alex Le Tux, the VR port will be coming as a standalone app for Meta Quest headsets, and is derived in part from the Perfect Dark decompilation project from 2022.
Alex Le Tux recently uploaded footage of the VR port to their YouTube channel, where the video description lists the build as “experimental” and not suitable for public release. That said, the video, which shows the player running through Perfect Dark’s memorable opening level “dataDyne Central: Defection,” seems to be running beautifully with head tracking and motion control aiming.
If the response on social media is any indication, the quality of this Perfect Dark port has people pretty excited, with many commenters frothing over the possibility that we’ll soon see a fully playable build, plus other VR ports of classic decompiled games.
VR ports of classic games have become an increasingly popular idea in recent years, almost exclusively driven by fans, indie devs, and open-source communities. Among the notable contributions are those from Team Beef, whose unofficial VR ports of classic PC games like id Software’s Doom, Quake II, and Lucasarts’ Jedi Knight games have been so well-received that they even grabbed the attention of id co-founder John Carmack.
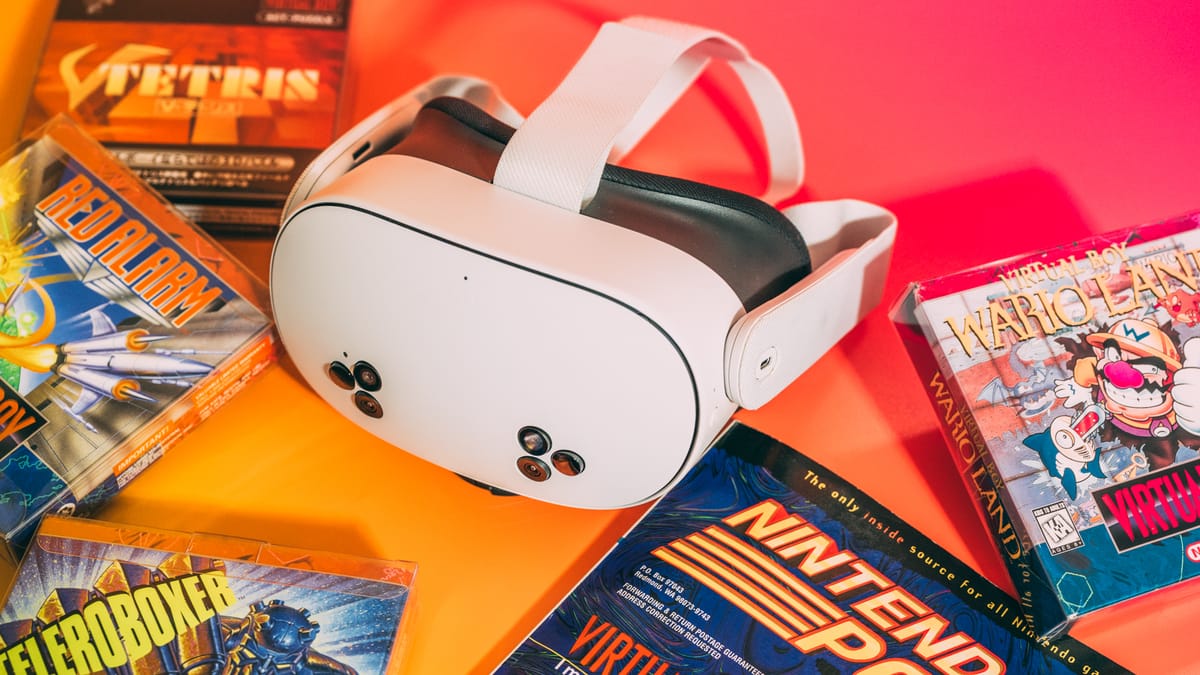
Beyond ports alone, excitement around VR emulation of classic games and consoles has also blossomed in recent years. For instance, Virtual Boy Go is an open-source emulator that allows Nintendo’s infamous foray into “VR” hardware to live on via Quest headsets. Projects like this demonstrate the ways that VR can serve not only as a preservation tool for classic games, but as a better, more immersive way to experience the classics.
 UploadVRJames Tocchio
As for Alex Le Tux’s Perfect Dark port, we’ll keep an eye on this one and be sure to update you all with any and all future developments.
Russian-state hackers wasted no time exploiting a critical Microsoft Office vulnerability that allowed them to compromise the devices inside diplomatic, maritime, and transport organizations in more than half a dozen countries, researchers said Wednesday.
The threat group, tracked under names including APT28, Fancy Bear, Sednit, Forest Blizzard, and Sofacy, pounced on the vulnerability, tracked as CVE-2026-21509, less than 48 hours after Microsoft released an urgent, unscheduled security update late last month, the researchers said. After reverse-engineering the patch, group members wrote an advanced exploit that installed one of two never-before-seen backdoor implants.
The entire campaign was designed to make the compromise undetectable to endpoint protection. Besides being novel, the exploits and payloads were encrypted and ran in memory, making their malice hard to spot. The initial infection vector came from previously compromised government accounts from multiple countries and were likely familiar to the targeted email holders. Command and control channels were hosted in legitimate cloud services that are typically allow-listed inside sensitive networks.
High
The Federal Bureau of Investigation has so far been unable to access data from a Washington Post reporter’s iPhone because it was protected by Apple’s Lockdown Mode when agents seized the device from the reporter’s home, the US government said in a court filing.
FBI agents were able to access the reporter’s work laptop by telling her to place her index finger on the MacBook Pro’s fingerprint reader, however. This occurred during the January 14 search at the Virginia home of reporter Hannah Natanson.
As previously reported, the FBI executed a search warrant at Natanson’s home as part of an investigation into a Pentagon contractor accused of illegally leaking classified data. FBI agents seized an iPhone 13 owned by the Post, one MacBook Pro owned by the Post and another MacBook Pro owned by Natanson, a 1TB portable hard drive, a voice recorder, and a Garmin watch.
We may earn a commission from links on this page.
Amazon announced Alexa+, its overhauled digital assistant with generative AI capabilities, about a year ago. Shortly thereafter, it kicked off an early access program allowing interested users to try it out free of charge. Unfortunately, that honeymoon period has come to an end: Alexa+ has now officially launched, and now you’ll need to pay to access its most useful features.
While certain features will still be free to use, the majority of the Alexa+ experience is now locked behind a paywall. True, you might already pay for that paywall—but if you don’t, it’s going to cost you quite a bit to keep the features you’ve been test driving for months. (Of course, the standard Alexa assistant still exists if you don’t care for the latest generative AI enhancement.)
The new Alexa is much like the old one, but now behaves a bit more like other generative AI assistants, including ChatGPT. In addition to simple requests and questions, Alexa+ can handle more complex queries and understand context (meaning one complex question can be followed by another, without needing to repeat yourself). For all the hullabaloo around generative AI, contextual awareness is really one of the big improvements users will notice with their digital assistants.
Amazon has a big vision for Alexa+. It still wants you to use it to control smart home devices, run timers, check the weather, and catch up on the news, but it also wants users to take advantage of “agentic” tasks, or actions that the AI can handle on your behalf. In theory, agentic AI allows you to ask the AI to order dinner to-go, make reservations at restaurants, schedule an Uber, or book a home repair. I’m still not sold on the capabilities of agentic AI assistants, and I imagine most people will continue to use Alexa+ the way they used regular old Alexa, (e.g. asking “Is it cold today?” or telling it to “set a timer for 10 minutes,” or ordering it to “Play ‘Manchild’ by Sabrina Carpenter on repeat”), but what do I know? Maybe Alexa+ really will change the way people interact with their Echo devices.
If you’re interested in Amazon’s newest AI assistant, there are three different ways to try it—one free, and two paid.
The most basic, Alexa+ chat, is totally free of charge. You can try it by heading to alexa.com or using the Alexa app for iOS or Android, where you can talk to Alexa in a chat window, ala ChatGPT. Amazon says users can get “quick answers, plan research, and explore new topics.”
But the thing is, you can’t use Alexa+ chat for any of the things you probably want to have Alexa+ do. It is solely a web-based chatbot experience, not something you can connect to your Alexa-enabled devices. If you’re interested in the full Alexa+ package, you’ll need to pay Amazon one way or another.
The good news is, you might have already paid Amazon for the privilege, even if you didn’t realize it: Currently, Amazon is offering all Prime members full access to Alexa+, including via the chatbot and through Alexa-enabled devices. Alexa+ also works with other Amazon services that come free with Prime, including Prime Video and Amazon Music. Seeing as over half the U.S. population has a Prime account, chances are good that if you’re at all interested, you already have access to Alexa+.
Maybe you’re one of the rare unicorns who doesn’t have a Prime account, but still wants to try Alexa+ on an Echo smart speaker. In that case, Amazon will offer you the full experience for a cool $19.99/month. That’s a slightly ridiculous price, seeing as a full Prime membership (with all the added benefits, from Prime Video to free shipping) will run you $14.99/month (or $139 per year). You definitely save money by subscribing to the latter, which is probably a big part of Amazon’s motivation here—Jeff Bezos will never truly rest until everyone uses Amazon to buy everything.
If you opt for either of the paid options, you can set up Alexa+ by simply telling your Alexa-enabled device, “Upgrade to Alexa+.” You can also use Alexa+ by logging into your Amazon account on alexa.com. And as noted above, you can certainly opt to keep the old Alexa assistant for the time being, whether whether you have Prime or not. While Amazon may do away with the legacy assistant in the future, it isn’t forcing anyone to switch just yet.

Blizzard says that it’s hoping for more character diversity moving forward
The post Why Blizzard Says It’s Been Making <em>Overwatch</em> Heroes Hotter appeared first on Kotaku.
A new phishing scam is targeting Apple Pay users, attempting to lock them into phony support calls or emails that could see them handing over their passwords and credit card numbers. The news was first highlighted by AppleInsider and involves warnings that look suspiciously like official Apple messaging. While AppleInsider’s report doesn’t link to any specific user complaints of this happening, it does include example screenshots, and reports matching AppleInsider’s description have popped up on both Reddit and Apple’s official support forums over the last 30 days.
The scam might come over either email or text, and usually warns the recipient about a potentially fraudulent purchase made using their Apple Pay at a physical Apple Store, while offering a phone number or email to contact to address the issue. According to AppleInsider, it might also include a case ID, timestamp, or other technical details in order to appear more legitimate. One user on Reddit, for instance, considered that the scam might be a legitimate text from Apple because it included the official sounding phrase “If this was you, no action is needed.”
However, inconsistencies remain, such as the scam often referring to Apple Accounts as Apple IDs, a now outdated term. Additionally, while emails might use official looking letterhead that makes them appear to come straight from Apple, mistakes could remain. For instance, an email could open with “Hello {Name}” instead of being addressed to the recipient’s actual name. It could come from a bogus address, but even appearing to come from a legitimate source like “appointmentandebills@icloud.com” isn’t a strong indicator that it’s real, as it’s possible for scammers to spoof email addresses. Overall, the idea seems to be to speed the recipient into action with an urgent tone, while using Apple’s logo and a professional writing style to mask any clues as to who is really sending these notices.
If you are receiving any texts or emails about your Apple Pay activity at all, chances are they probably aren’t real—Apple doesn’t reach out to its users in this way. Rather than sending texts or emails, communication instead comes directly from the Wallet app. Additionally, Apple Pay serves as a medium for payment rather than as a credit or debit account in and of itself. As such, if any fraudulent transactions are detected, notices would come from your bank or credit card provider rather than Apple itself.
Still, it is worth keeping an eye out for any red flags as well. Look for small typos or unusual domain names, which can help give a fake message away, even if a lack of these isn’t an indicator that a message is legitimate. Also, rather than calling any provided phone numbers, consider searching for them online to see whether they’ve been reported as being tied to a scam operation. At any rate, do not respond to these notices, and don’t provide any information (such as passwords, which Apple will never ask for) to them if you’ve already reached out by accident. There are better ways to verify your Apple Pay activity.
If you think a message you’ve received is illegitimate, the best thing you can do is ignore it and verify it independently. Instead of responding to the suspicious text or email directly, or calling any provided phone numbers, double check any claims made in the statement through official Apple channels. You can see your recent Apple Pay purchases in the Wallet app by tapping on one of your registered cards, and opening the Settings app and navigating to Media & Purchases > View Account > Purchase History will show you any recent App Store purchases. If you don’t see a transaction mentioned in one of these notices in your official payment history, chance are it never happened.
If you’re still in doubt you have options. Rather than reaching out to an email or phone number linked in a potential scam notice, start fresh with a new message straight to Apple’s official support. You can find the proper contact details, including an official Apple phone number for your region, on Apple’s website. The company will be able to determine whether it’s seen any suspicious activity tied to your account.
Finally, once you’re certain a message is part of a scam, you can forward it (or simply report it, if forwarding isn’t possible) to Apple to help the company shut it down. The specific email address you’ll want to use will differ based on the type of message, and you can find all your options on Apple’s support website, under “How to report suspicious emails, messages, and calls.” Once you’ve sent the message to the correct channels, delete it from your inbox to keep yourself from accidentally clicking any compromised links. As added security, also consider changing your Apple Account password, or using a password manager.

‘You are not alone in that hospital room’ replied series co-creator John Romero to the dying fan on Reddit
The post Terminally Ill Fan Spending Final Days Playing <i>Doom</i> And The Devs Want Him To Know He’s Not Alone appeared first on Kotaku.
On Wednesday, Anthropic announced that its AI chatbot, Claude, will remain free of advertisements, drawing a sharp line between itself and rival OpenAI, which began testing ads in a low-cost tier of ChatGPT last month. The announcement comes alongside a Super Bowl ad campaign that mocks AI assistants that interrupt personal conversations with product pitches.
“There are many good places for advertising. A conversation with Claude is not one of them,” Anthropic wrote in a blog post. The company argued that including ads in AI conversations would be “incompatible” with what it wants Claude to be: “a genuinely helpful assistant for work and for deep thinking.”
The stance contrasts with OpenAI’s January announcement that it would begin testing banner ads for free users and ChatGPT Go subscribers in the US. OpenAI said those ads would appear at the bottom of responses and would not influence the chatbot’s actual answers. Paid subscribers on Plus, Pro, Business, and Enterprise tiers will not see ads on ChatGPT.

Also, Black Myth: Wukong might be the console’s next big port
The post Nintendo’s Stock Price Nosedives Despite Switch 2’s Complete Dominance appeared first on Kotaku.
The virtual Richard M. Stallman (vrms) concept lives on, helping Linux users identify non-free software via license audits.
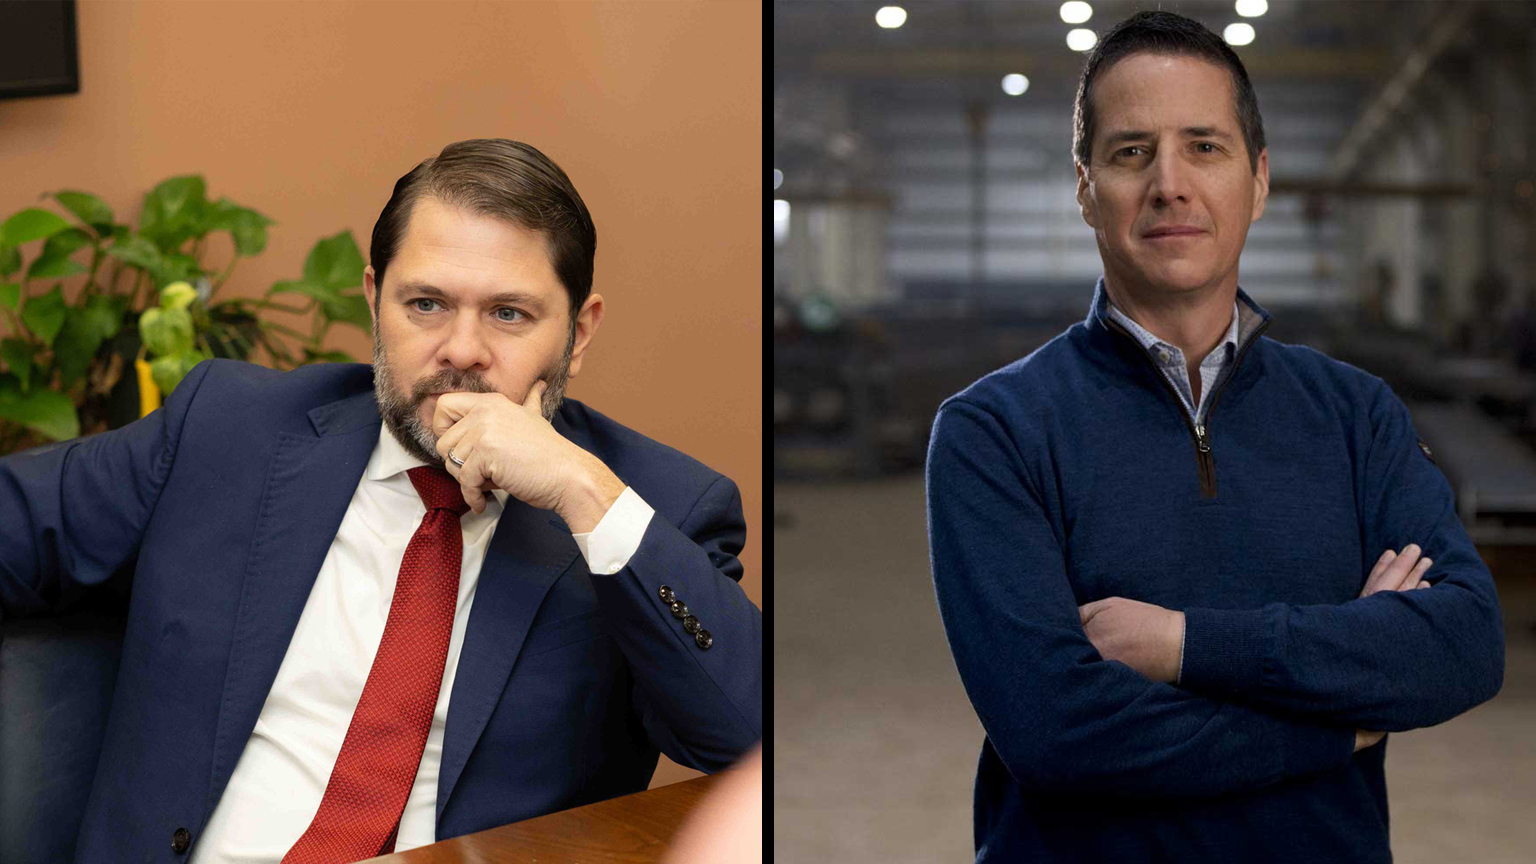
Without meaningful deterrents, Big Tech companies will do what’s profitable, regardless of the cost to consumers. But a new bipartisan bill could add a check that would make them think twice, at least in one area. On Wednesday, Senators Ruben Gallego (D-AZ) and Bernie Moreno (R-OH) introduced legislation that would require social platforms to crack down on scam ads.
The Safeguarding Consumers from Advertising Misconduct (SCAM) Act would require platforms to take reasonable steps to prevent fraudulent or deceptive ads that they profit from. If they don’t, the Federal Trade Commission (FTC) and state attorneys general could take civil legal action against them.
The backdrop to the SCAM Act is a Reuters report from last November. Meta reportedly estimated that up to 10 percent of its 2024 revenue came from scam ads. The company is said to have calculated that as much as $16 billion of its revenue that year was from scams, including “fraudulent e-commerce and investment schemes, illegal online casinos and the sale of banned medical products.”
Making matters worse, Meta reportedly refused to block small fraudsters until their ads were flagged at least eight times. Meanwhile, bigger spenders were said to have accrued at least 500 strikes without being removed. Executives reportedly wrestled with how to get the problem under control — but only without affecting the company’s bottom line. At one point, managers were told not to take any action that could cost Meta more than 0.15 percent of its total revenue. (See what I mean about needing meaningful deterrents?)
According to the FTC, Americans’ estimated total loss from fraud in 2024 (adjusted for underreporting) was nearly $19 billion. An estimated $81.5 billion of that came from seniors.
“If a company is making money from running ads on their site, it has a responsibility to make sure those ads aren’t fraudulent,” Sen. Gallego said in a statement. “This bipartisan bill will hold social media companies accountable and protect consumers’ money online.”
“It is critical that we protect American consumers from deceptive ads and shameless fraudsters who make millions taking advantage of legal loopholes,” Moreno added. “We can’t sit by while social media companies have business models that knowingly enable scams that target the American people.”
This article originally appeared on Engadget at https://www.engadget.com/big-tech/bipartisan-scam-act-would-require-online-platforms-to-crack-down-on-fraudulent-ads-210316594.html?src=rss