
This is the best portable monitor you can get.
The post Portable Gaming 15-Inch Display Is Going for Mere Pennies, Amazon Already Sold 10K Units at This Record Low appeared first on Kotaku.
This is the best portable monitor you can get.
The post Portable Gaming 15-Inch Display Is Going for Mere Pennies, Amazon Already Sold 10K Units at This Record Low appeared first on Kotaku.
fjo3 shares a report from TheWrap: There are already at least 175,000 AI-generated podcast episodes on platforms like Spotify and Apple. That’s thanks to Inception Point AI, a startup with just eight employees cranking out 3,000 episodes a week covering everything from localized weather reports and pollen trackers to a detailed account of Charlie Kirk’s assassination and its cultural impact, to a biography series on Anna Wintour. Its podcasting network Quiet Please has generated 12 million lifetime episode downloads and amassed 400,000 subscribers — so, yes, people are really listening to AI podcasts.
Inception Point CEO Jeanine Wright believes the tool is proof that automation can make podcasting scalable, profitable and accessible without human writers, editors or hosts. “The price is now so inexpensive that you can take a lot of risks,â Wright told TheWrap. âoeYou can make a lot of content and a lot of different genres that were never commercially viable before and serve huge audiences that have really never had content made for them.” At a cost of $1 an episode, Wright takes a quantity-over-quality approach. “I think very quickly we get to a place where AI is a default way that content is made, not just across audio, but across television and film and commercials and imagery, and everything. And then we will disclose when things are not made with AI instead of that they were made with AI,” Wright said. “But for now, we are perfectly happy leading the way.”


Read more of this story at Slashdot.
When the Trump administration brutally cut federal funding for biomedical research earlier this year, at least 383 clinical trials that were already in progress were abruptly cancelled, cutting off over 74,000 trial participants from their experimental treatments, monitoring, or follow-ups, according to a study published today in JAMA Internal Medicine.
The study, led by researchers at Harvard, fills a knowledge gap of how the Trump administration’s research funding cuts affected clinical trials specifically. It makes clear not just the wastefulness and inefficiency of the cuts but also the deep ethical violations, JAMA Internal Medicine editors wrote in an accompanying editor’s note.
In March, the National Institutes of Health, under the control of the Trump administration, announced that it would cancel $1.8 billion in grant funding that wasn’t aligned with the administration’s priorities. The Harvard researchers, led by health care policy expert Anupam Jena, used an NIH database and a federal accountability tracking tool to find grants supporting clinical trials that were active as of February 28 but had been terminated by August 15.
Productivity setups are a personal thing. Some people swear by to-do lists and apps, some people like scheduling and planners. For those in the latter camp, Google has made a minor but valuable addition to the Workspace suite. Going forward, you’ll be able to block off segments of time in Google Calendar for working on specific tasks. You can add descriptions and set your preferences for that task in regard to do not disturb and visibility settings. It’s a nice step up from scheduling meetings with yourself when you have to focus on a particular assignment (which several of us at Engadget have been known to do).
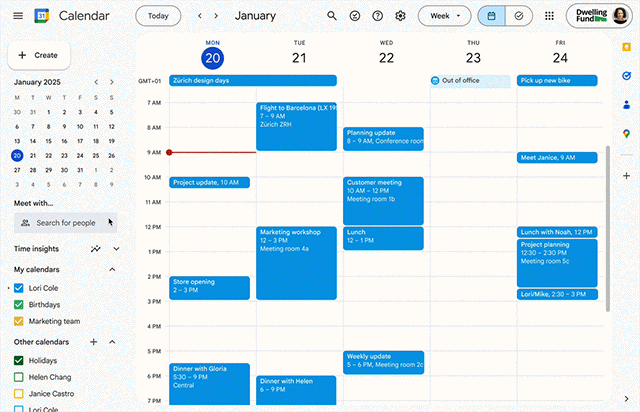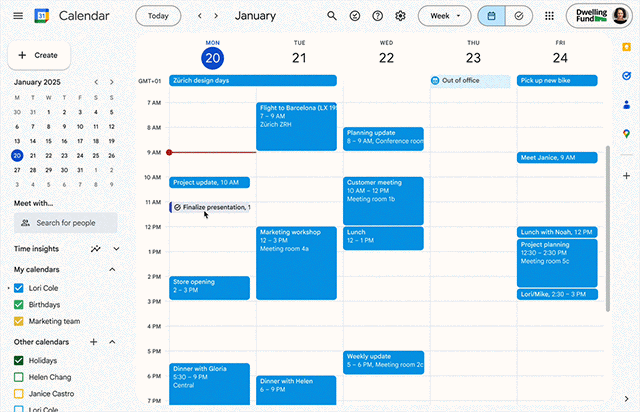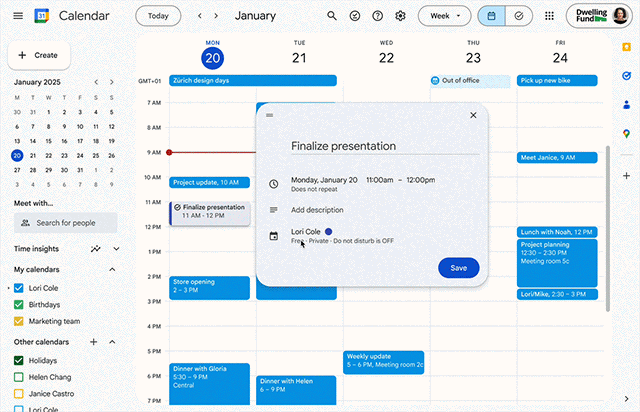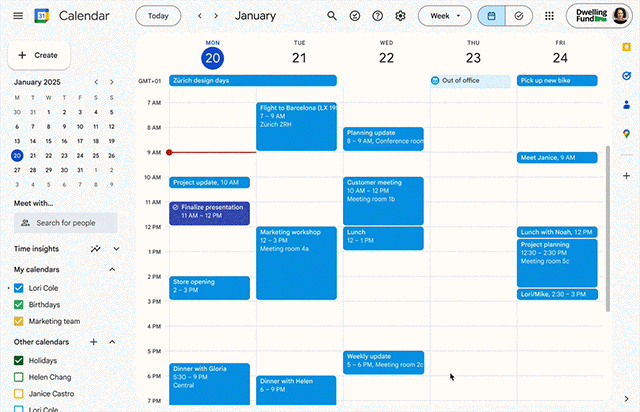
This option began appearing for Google’s Rapid Release domains earlier in November, while standard release domains will see a gradual release beginning December 1. Once it’s fully rolled out, it will be available by default, whether you’re a Google Workspaces customer or just using a personal Google account.
This article originally appeared on Engadget at https://www.engadget.com/apps/google-calendar-now-lets-you-schedule-tasks-231026000.html?src=rss

iPad Pro’s biggest rival.
The post Samsung Kicked Off Black Friday Early, Now Quietly Offloading Its Galaxy Tab S11 at a New Low appeared first on Kotaku.
Jeff Bezos is one of the world’s richest and most famous tech CEOs, but he hasn’t actually been a CEO of anything since 2021. That’s now changing as he takes on the role of co-CEO of a new AI company, according to a New York Times report citing three people familiar with the company.
Grandiosely named Project Prometheus (and not to be confused with the NASA project of the same name), the company will focus on using AI to pursue breakthroughs in research, engineering, manufacturing, and other fields that are dubbed part of “the physical economy”—in contrast to the software applications that are likely the first thing most people in the general public think of when they hear “AI.”
Bezos’ co-CEO will be Dr. Vik Bajaj, a chemist and physicist who previously led life sciences work at Google X, an Alphabet-backed research group that worked on speculative projects that could lead to more product categories. (For example, it developed technologies that would later underpin Google’s Waymo service.) Bajaj also worked at Verily, another Alphabet-backed research group focused on life sciences, and Foresite Labs, an incubator for new AI companies.

360-degree Bose sound with 17-hour battery life.
The post Bose Revolve+ Bluetooth Speaker Drops to Peanuts, Amazon Pushes Last Stock at 40% Off to Liquidate Fast appeared first on Kotaku.
FreeBSD 15.0-RC1 is available today for testing as this leading BSD operating system works toward the stable release in early December…
Five men have pleaded guilty to running laptop farms and providing other assistance to North Koreans to obtain remote IT work at US companies in violation of US law, federal prosecutors said.
The pleas come amid a rash of similar schemes orchestrated by hacking and threat groups backed by the North Korean government. The campaigns, which ramped up nearly five years ago, aim to steal millions of dollars in job revenue and cryptocurrencies to fund North Korean weapons programs. Another motive is to seed cyber attacks for espionage. In one such incident, a North Korean man who fraudulently obtained a job at US security company KnowBe4 installed malware immediately upon beginning his employment.
On Friday, the US Justice Department said that five men pleaded guilty to assisting North Koreans in obtaining jobs in a scheme orchestrated by APT38, also tracked under the name Lazarus. APT38 has targeted the US and other countries for more than a decade with a stream of attack campaigns that have grown ever bolder and more advanced. All five pleaded guilty to wire fraud, and one to aggravated identity theft, for a range of actions.
On Friday, a US District Court issued a preliminary injunction blocking the United States government from halting federal funding at UCLA or any other school in the University of California system. The ruling came in response to a suit filed by groups representing the faculty at these schools challenging the Trump administration’s attempts to force UCLA into a deal that would substantially revise instruction and policy.
The court’s decision lays out how the Trump administration’s attacks on universities follow a standard plan: use accusations of antisemitism to justify an immediate cut to funding, then use the loss of money to compel an agreement that would result in revisions to university instruction and management. The court finds that this plan was deficient on multiple grounds, violating legal procedures for cutting funding to an illegal attempt and suppressing the First Amendment rights of faculty.
The result is a reprieve for the entire University of California system, as well as a clear pathway for any universities to fight back against the Trump administration’s attacks on research and education.

That’s some Gwi-ma behavior right there
The post A School Is Banning Kids From Singing <em>KPop Demon Hunters</em> Songs appeared first on Kotaku.
Today, Valve released Proton 10 as the latest stable release of this open-source compatibility tool for Steam Play based on Wine and additional components for playing Windows games on Linux systems.
Chess is playable in Walkabout Mini Golf starting this Wednesday.
The playable activity is initially available in the VR version of the game in Upside Town and Venice, as well as in the Welcome Island.
The tabletop game joins a steadily growing list of activities inside Walkabout that can be played whether or not you engage with the core game of mini golf. In recent months the developers added slingshots, leaf blowers and bug nets to various areas, joining the existing hidden ball and “fox” hunts. Die-hard fans may have also noticed the stairs inside the shack on Welcome Island leading to an underground area styled as if it is for employees, with new areas opening up down there connecting to secret rooms all over the game.
With chess, Walkabout opens up its universe to tabletop board games. There’s no comment yet from Mighty Coconut on whether they’ve got other tabletop games queued up yet, but you can use the menu on a course like Venice to quickly teleport to the chess board where you replace your club for a hand. Just pull the trigger to grab a piece and place it somewhere else on the board. There appears to be no enforced turn order or rulesets, so you can play with custom rules if you wanted.
Developers say the game board and pieces will retain their state in a multiplayer room as long as there’s a player in it. In other words, the board will reset when the room isn’t occupied. For players who use standalone headsets with streaming PCs to play a game like Walkabout, one could hypothetically leave a private room open on their PC and just put on the headset when they hear their friend enter the virtual room already open on there. It’d be a lot of work and wasted electricity to dedicate a PC for just this purpose, but a universe sounds nice that exists just for a friendly game of chess in Venice.
Which tabletop game do you want to see Walkabout add support for next? Let us know in the comments below.

From Helldivers 2 to Astro Bot, here are the best PS5 games
The post The 23 Best Games For Sony’s PlayStation 5 appeared first on Kotaku.
An anonymous reader shares a report: When Nigel Morris tells you he’s worried about the economy, you listen. As industry observers know, Morris co-founded Capital One and pioneered lending to subprime borrowers, building an empire on understanding exactly how much financial stress the average American can handle. Now, as an early investor in Klarna and other buy-now-pay-later companies like Aplazo in Mexico, he’s watching something that makes him deeply uncomfortable.
“To see that people are using [BNPL services] to buy something as basic and fundamental as groceries,” Morris told me on stage at Web Summit in Lisbon this week, “I think is a pretty clear indication that a lot of people are struggling.” The statistics back up his unease. Buy-now-pay-later services have exploded to 91.5 million users in the United States, according to the financial services firm Empower, with 25% using the services to finance their groceries as of earlier this year, according to survey data released in late October by lending marketplace Lending Tree.
These aren’t discretionary purchases — the designer bags and latest Apple headphones that BNPL was marketed for originally. Borrowers aren’t paying it all back, either. According to Lending Tree, default rates are accelerating: 42% of BNPL users made at least one late payment in 2025, up from 39% in 2024 and 34% in 2023.


Read more of this story at Slashdot.
At the start of the year developers behind the Budgie desktop environment hoped for shipping Budgie 10.10 in Q1-2025. We are now in Q4 without a stable release but at long last a preview version is at least available. Budgie 10.10 is the point at which Budgie is going all-in on Wayland in leaving behind the X11 desktop session support…
Game publisher Paradox Interactive has split with Colossal Order, the studio behind Cities: Skylines II. Colossal Order, which also made the original Cities: Skylines back in 2015, will move on to something new after completing a few last updates. The intellectual property will remain with Paradox, which said today that work on Cities: Skylines II will be moved to Iceflake Studios. The Finland-based internal team will be responsible for all development, including future content updates and the long-awaited console version, starting in 2026.
The move comes after about two years of trying to salvage the citybuilding sequel and the reputations of all parties. While the game was initially expected to debut in October 2023 on PC and consoles, the launch was limited to PC, with higher minimum specs than previously announced and with a lot of bugs. The ongoing issues caused tension and toxicity between Colossal Order and the Cities: Skylines audience. Although the game has reached a more stable state, new content has been slow to arrive and there is still no sign of a console launch as the studio exits their project.
This article originally appeared on Engadget at https://www.engadget.com/gaming/cities-skylines-ii-dev-parts-ways-with-publisher-paradox-210229692.html?src=rss
We’ve been using passwords to protect our various accounts for a few decades now, and, to be honest, we’re not very good at it. Many of us use the same simple, easy to remember passwords for all of our accounts—convenient for logging in, but horrible for security. Not only will a bad actor (or computer) be able to guess that password easily, they’ll try it against your other accounts. Before you know it, you have multiple breaches, some of which may involve financial or private information.
There are a number of steps you can take to beef up your password security, of course. First, you can use a complex and unique password for each of your accounts, making sure to never reuse a password. A well-made password can be impossible for a human to guess, and virtually impossible for a computer to guess. But even if a company loses your password in a data breach, using two-factor authentication (2FA) can protect you further. Without a trusted device that either generates or receives a 2FA code, your password becomes essentially useless to hackers. And since you didn’t repeat passwords, they can’t try it on your other accounts. That’s what makes this combo a winning strategy.
But many, if not most, of us aren’t using this winning strategy. Many are still at risk, or putting their organizations at risk, with insecure authentication measures. As such, there’s a push for consumers to adopt a new form of authentication, something that combines the convenience of passwords, with the security of 2FA, all without you needing to remember a thing: passkeys.
Passkeys are a (relatively) new authentication method that offer a similar experience to passwords without actually involving a password of any kind. The measure relies on something called public key cryptography: When you create a new account with a passkey, or you create a passkey for your existing account, a “key pair” is generated. One of these keys is public, and is stored by the company that runs the account in question. This key is not a secret, and, theoretically, could be stolen or lost in a breach. However, the other key is a secret. This private key is stored on your device–such as a smartphone, tablet, or computer—and is what is used to actually authenticate your identity.
To create the passkey, you simply need to use your device’s built-in authentication method. That might mean a face scan, a fingerprint scan, or a PIN. Once you successfully authenticate yourself, the passkey is established. To log in in the future, you simply authenticate with one of those same three methods. If it goes through, the system then checks with the account that holds the public key to confirm your identity, and you’re in—no password required.
Your passkeys are securely stored on your devices, typically in a “vault” such as a keychain or password manager. Apple generates and stores passkeys in iCloud Keychain, for example. If you use a password manager, like Bitwarden or 1Password, you can create and store passkeys there. Any device that has access to that password manager can then also access the passkey for authentication.
However, you don’t need to log into your accounts on the device that contains the passkey. If you’re using a different device, say a friend’s computer or a tablet that doesn’t contain the passkey, you will have the option to use your trusted device to authenticate. For example, say you want to check your bank account on your PC, but your account uses a passkey stored on your iPhone. You can choose to authenticate using the passkey device, which will trigger the account’s site to present a QR code. You can scan the QR code on your iPhone, authenticate using Face ID, Touch ID, or your PIN, and you’ll log in. This is also how the feature works when signing into accounts on devices that don’t store passkeys directly, like a PlayStation 5.
The short answer? Yes. Passkeys are an extremely secure authentication method. While they’re way more secure than passwords, they’re even more secure than 2FA. 2FA is great, and certainly better than using a password alone, but it is possible for attackers to steal the authentication codes—especially when these codes are SMS-based. This can be as sophisticated as hacking into the platforms that send your codes, or as simple as a phishing scheme: Scammers can pose as representatives of the account in question, and trick you into sharing your 2FA codes with them. As such, 2FA, while secure, has an inherent phishing flaw.
Passkeys don’t have this flaw. You can’t be tricked into giving over one of your passkeys, nor can a hacker steal it from your device. The system won’t prompt you to authenticate unless you are visiting the exact domain for the platform, which means scammers can’t create dummy sites that trick you into logging in: The passkey process will simply not start. Importantly, signing in via a passkey requires the trusted device to be physically close to the device you’re logging into. As such, a hacker can’t send you an image of a QR code, trick you into scanning it, and then convince you to authenticate to log in. Unless you’re in the same room as the hacker, they’re not getting your passkey.
One of the most common concerns regarding passkeys is what happens when you lose the device the passkey is stored on. After all, if the secret key is kept only on your smartphone, what happens if it is lost, stolen, or breaks?
As it turns out, there are a few possibilities here. First, it is true there is a risk of losing the passkey for good should you lose access to the trusted device. If you choose to store your passkeys on a physical security key, like a YubiKey, losing or breaking the key will mean losing your passkey. However, depending on the account, you may have recovery options—such as answering security questions to prove your identity. This will be case-dependent, of course: If your account only has a passkey set up, and that passkey is only stored on one device, you may lose access to the account. Check if your accounts offer recovery options, or even backup authentication measures. Some accounts may still have you create a password, even if you opt into passkeys, because of this possibility.
But more importantly, you don’t need to keep your passkeys to just one device. There are secure protocols that allow you to sync your passkeys between different devices. For example, if you create a passkey on your iPhone, iCloud Keychain securely syncs that passkey to your other connected Apple devices as well, such as an iPad and Mac. That way, when you want to log into your account on any of these devices, the option to authenticate with your passkey will be available on any—you just need to use Face ID, Touch ID, or present your PIN, and you’re in.
At this time, no. This is probably passkeys’ biggest drawback. Unlike passwords, which you can export to other password managers, passkeys are stuck to the service they’re generated with. If you set up a passkey for your Google Account on your iPhone, you won’t be able to directly transfer it to, say, an Android device. If your passkey lives in Bitwarden, you can’t transfer it to Google Password Manager. As such, you should try to create passkeys on the platform you most widely use. If you’re fully in the Apple ecosystem, Apple’s iCloud Keychain will work well for you. But if you have a mix of devices from different manufacturers, you’d be better off creating passkeys on a cross-platform password manager. You can always authenticate with your iPhone, of course, but the true convenience of passkeys is quickly logging in on a device that already contains the passkey.
That doesn’t mean you need to keep this service forever, however: You can set up new passkeys for existing accounts on other services, so you can securely get rid of your old passkey devices. However, make sure to keep the old device until you have the passkey established on a new one. If something goes wrong, and you’re not able to set up a new passkey on another device, you’ll need the old device to confirm your identity—unless you have an alternative authentication option, like a password.
Passkeys aren’t perfect: In practice, they can be a bit complicated, especially when working across different devices. But at their best, they offer both convenience and security. If you aren’t particularly tech savvy, or if you’re not totally entrenched in one tech company’s ecosystem, it might be a bit too early to go all-in on passkeys. But passkeys can keep your accounts safe and secure, so long as you understand these other weaknesses.

The creator behind Nier: Automata is trying to make the games you want, but they keep getting canned
The post Please Stop Cancelling Yoko Taro’s Games appeared first on Kotaku.

If Minecraft or The Last of Us wins Best Adaptation, I will scream loud enough to break the sound barrier
The post One Of The Biggest Game Awards Snubs Wasn’t Even A Video Game appeared first on Kotaku.