Elon Musk tries to make Apple and mobile carriers regret choosing Starlink rivals

SpaceX’s $17 billion deal to buy spectrum licenses from EchoStar should help Starlink satellites deliver better service to smartphones, and it might give a few large corporations second thoughts about their current partnerships with Starlink competitors.

The spectrum, combined with a SpaceX plan to launch up to 15,000 new and improved satellites for cellular service, could cause AT&T and Verizon to question their reliance on satellite company AST SpaceMobile. Apple, which was reportedly already facing internal dissent over its deal with Globalstar, now has another reason to wonder if it made the right choice in rejecting an offer from Elon Musk.

Pending regulatory approval, SpaceX will acquire EchoStar’s AWS-4 and H-block spectrum licenses, giving Musk’s space company the rights to 50 MHz of spectrum in the 1.9 and lower 2 GHz spectrum bands. SpaceX plans to acquire EchoStar’s rights to the spectrum in the US and globally.

Read full article

Comments

Top 10 Early October Prime Day Apple Deals: AirPods, iPads & More For Less

Top 10 Early October Prime Day Apple Deals: AirPods, iPads & More For Less
We are expecting a bunch of deals to emerge this week, especially once Amazon’s Prime Big Deal Days event gets underway on Tuesday, October 7. Even though the sales event has not officially started yet, we’re still tracking bargains. To that end, we found a bunch of deals on select Apple products, such as its AirPods 4 earbuds.

For example,

Suunto sues Garmin over patent infringements as legal troubles build 

Less than a week after Strava’s lawsuit against Garmin was revealed, it has come to light that Suunto is also suing the company.

Filed in a Texas court on 22 September, Suunto’s case accuses Garmin of infringing five patents related to measuring a user’s respiratory rate, antenna design, watch casing and tracking golf shots. 

The complaint alleges that many Garmin smartwatches incorporate the patented technologies without permission, including the Marq, Fenix, Epix, Instinct, Venu and Forerunner models.

Suunto is seeking damages and potentially a permanent injunction to block sales of the Garmin devices that use the features. 

Strava’s case against Garmin 

Strava user's guide
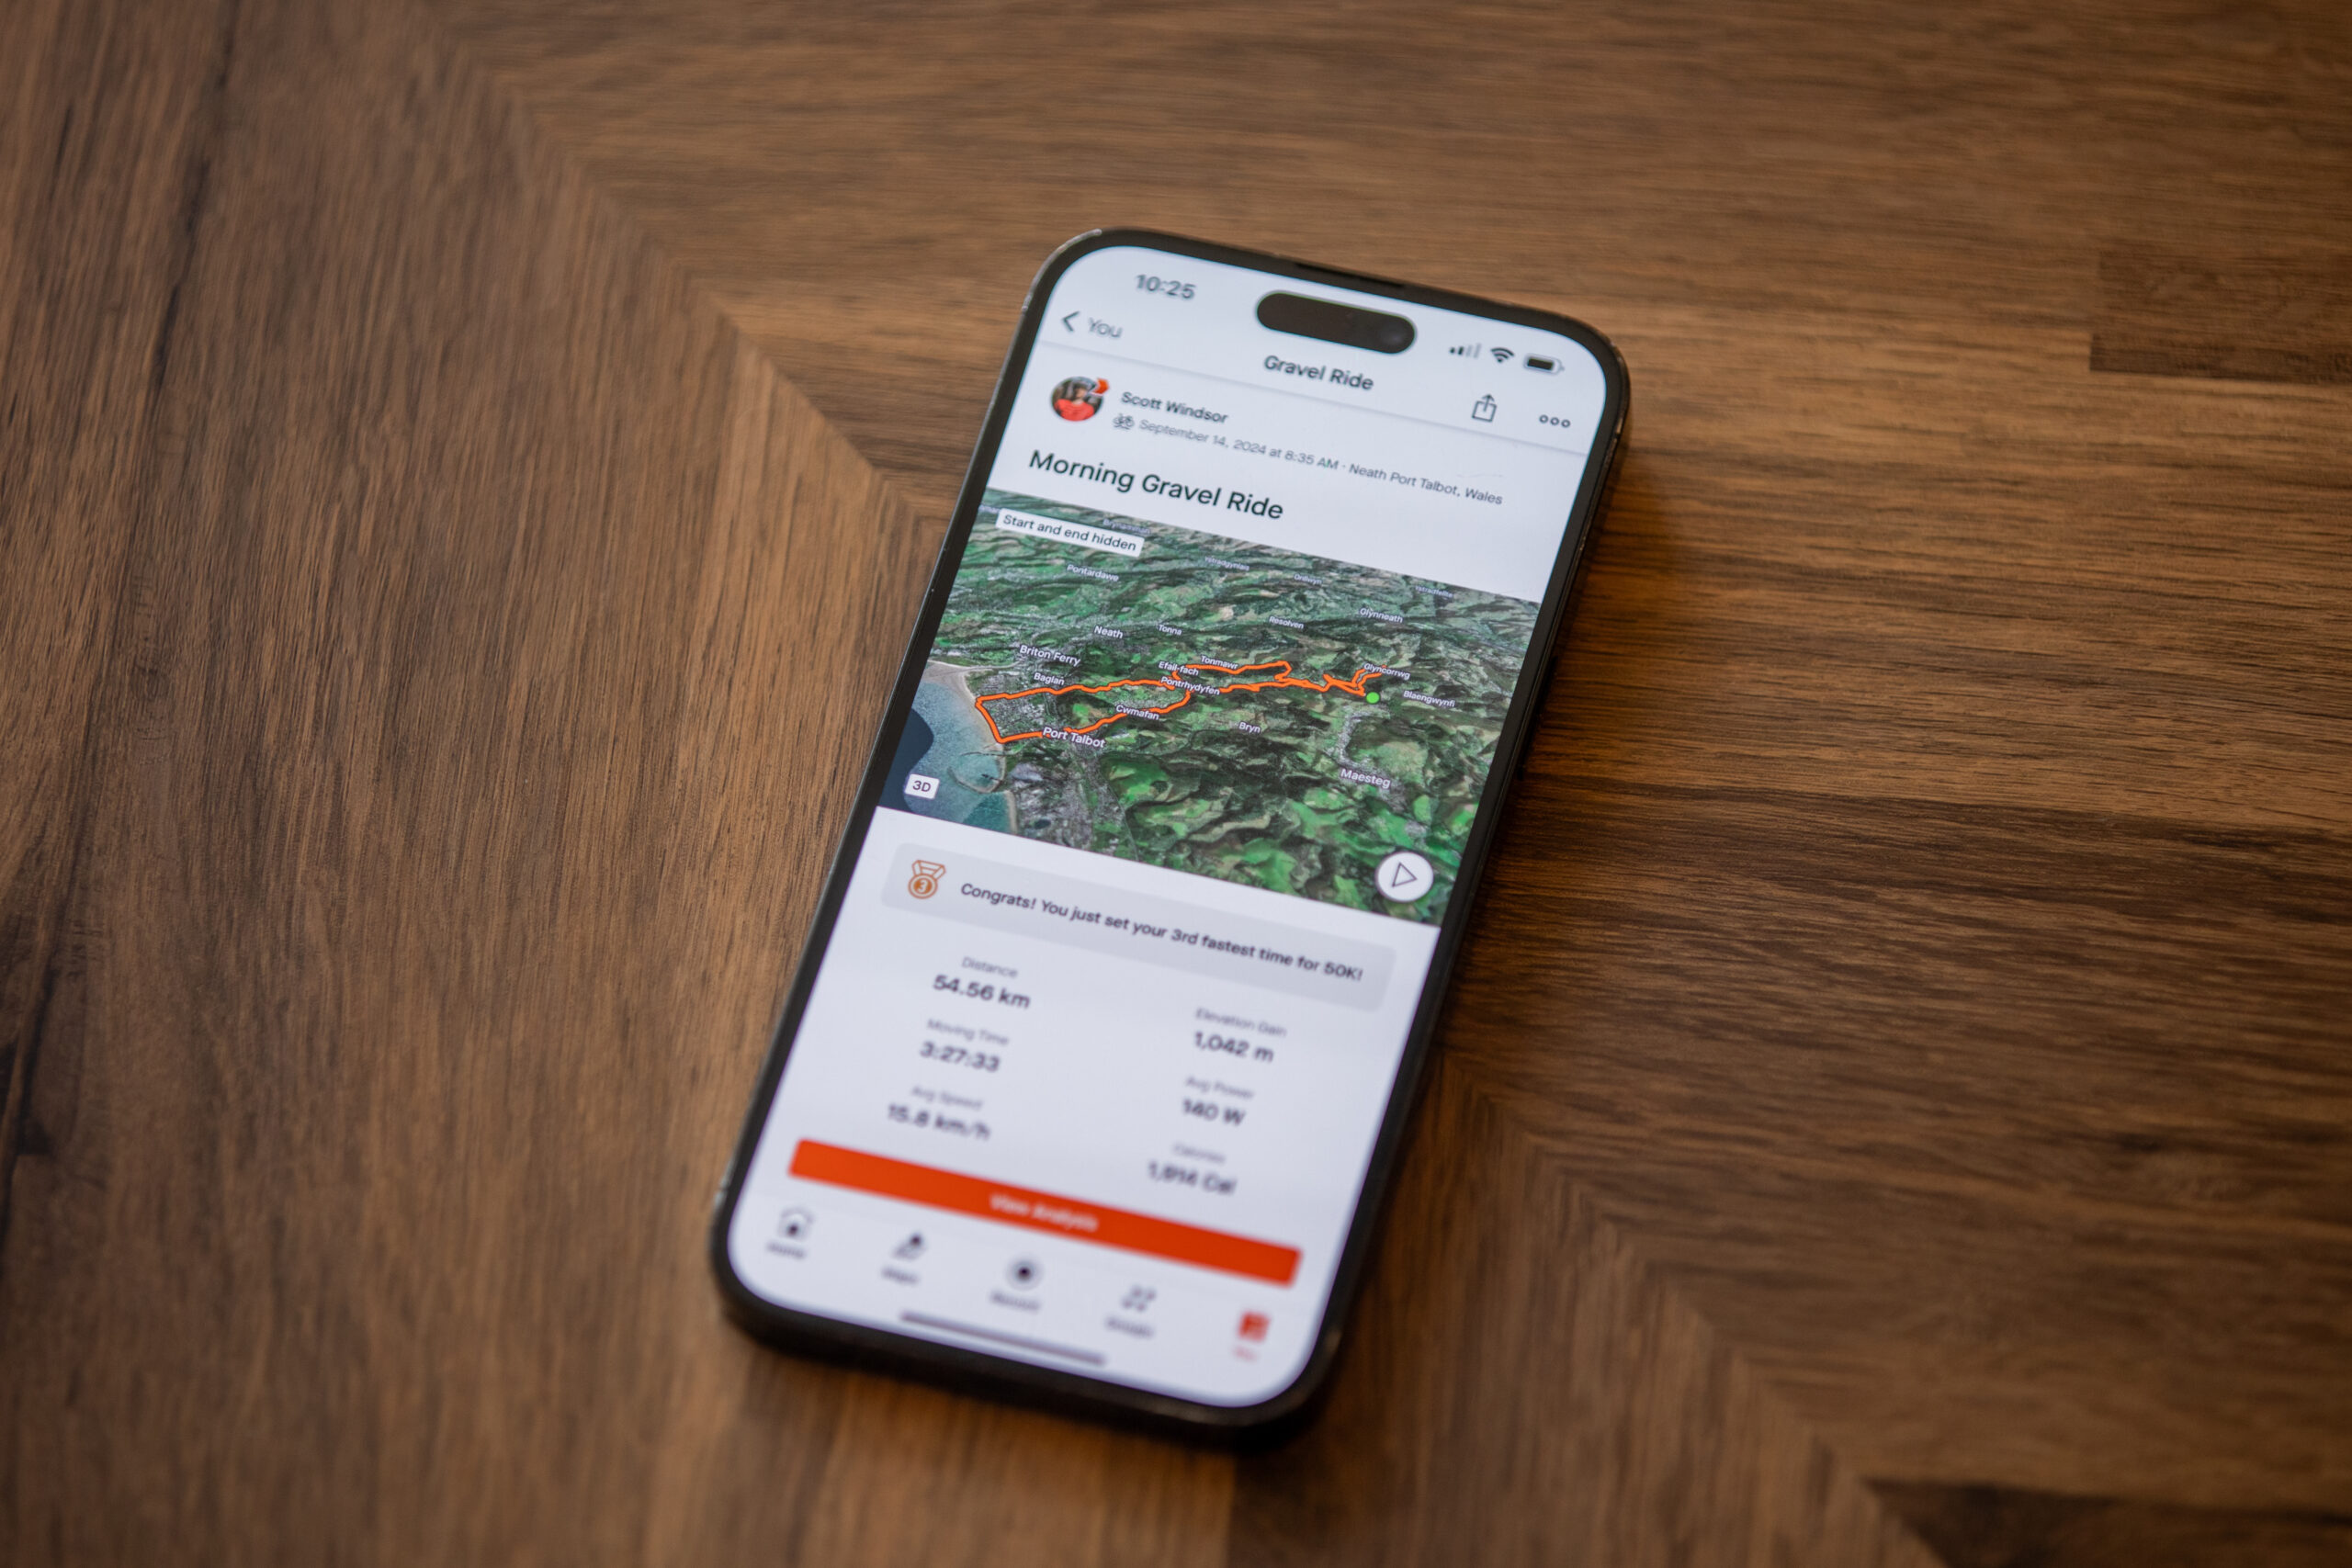
Strava’s lawsuit against Garmin also covers patent infringements. Scott Windsor / Our Media

Suunto, a Finnish smartwatch and tech company, is not alone in suing Garmin, with its filing appearing soon after Strava’s complaint against the GPS giant. 

Like Suunto, Strava is also pursuing legal action against Garmin over patent infringements. 

Filed in a Colorado court on 30 September, Strava’s case alleges that Garmin violated the terms of a 2015 agreement between the two companies by offering Garmin-branded segments and leaderboards. 

However, Strava’s chief product officer, Matt Salazar, offered a different explanation for the legal action in a Reddit post. He said the primary reason behind Strava’s litigation was a set of “new developer guidelines for all of its API partners”. 

Salazar wrote that the dispute arose from Garmin’s new API guidelines announced in July that require “the Garmin logo to be present on every single activity post, screen, graph, image, sharing card etc”. 

“We have until November 1st to comply, and if not, Garmin has threatened to cut off access to their API, stopping all Garmin activities from being uploaded to Strava,” Salazar said.

Here’s the real reason Endurance sank

In 1915, intrepid British explorer Sir Ernest Shackleton and his crew were stranded for months in the Antarctic after their ship, Endurance, was trapped by pack ice, eventually sinking into the freezing depths of the Weddell Sea. Miraculously, the entire crew survived. The prevailing popular narrative surrounding the famous voyage features two key assumptions: that Endurance was the strongest polar ship of its time, and that the ship ultimately sank after ice tore away the rudder.

However, a fresh analysis reveals that Endurance would have sunk even with an intact rudder; it was crushed by the cumulative compressive forces of the Arctic ice with no single cause for the sinking. Furthermore, the ship wasn’t designed to withstand those forces and Shackleton was likely well aware of that fact, according to a new paper published in the journal Polar Record. Yet he chose to embark on the risky voyage anyway.

Author Jukka Tuhkuri of Aalto University is a polar explorer and one of the leading researchers on ice worldwide. He was among the scientists on the Endurance22 mission that discovered the Endurance shipwreck in 2022, documented in a 2024 National Geographic documentary. The ship was in pristine condition partly because of the lack of wood-eating microbes in those waters. In fact, the Endurance22 expedition’s exploration director, Mensun Bound, told The New York Times at the time that the shipwreck was the finest example he’s ever seen; Endurance was “in a brilliant state of preservation.”

Read full article

Comments

KDE Plasma 6.5 Desktop Environment Is Now Available for Public Beta Testing

KDE Plasma 6.5 is packed with lots of goodies for everyone, including major UI improvements to the Sticky Note widget, support for displaying ink levels on your printers, rounded bottom corners for Breeze-decorated windows, and support for syncing the clipboard text between the client and server on remote sessions.

The post KDE Plasma 6.5 Desktop Environment Is Now Available for Public Beta Testing appeared first on Linux Today.

British Transport Police’s decision not to investigate bike thefts at train stations “will hit lowest income groups the hardest”

The British Transport Police’s decision not to investigate certain bike thefts at train stations “will hit the lowest income groups the hardest”, according to Sophie Gordon, campaigns manager at Cycling UK. 

Last week, the British Transport Police (BTP) said it will not investigate bike thefts at train stations where the bicycle has been left for more than two hours, and CCTV footage will not be reviewed outside of this time frame. The BTP also said the theft of any bike worth less than £200 will not be investigated and that robberies on trains should only be reported if the passenger knows which carriage they were in. 

“The decision not to investigate bike theft when cycles have been left for longer than two hours will hit the lowest income groups the hardest,” Cycling UK’s Sophie Gordon said.

“These are often working people who might not be able to afford a car and are relying on bikes and public transport to get to work. If you’re on shift or at work, you will inevitably be away longer than a couple of hours,” she added. 

Cycling UK found that cycling for commuting made up 29 per cent of all cycle journeys in 2023. 

Last year, it was revealed that 49 per cent of Brits couldn’t afford a new bike, with a quarter saying it would take them six months to save for one. The Walk Wheel Trust, formerly Sustrans, also found that almost 2 million people want to cycle but are priced out due to the initial cost of a bicycle and accessories. 

More than 14,000 bikes were stolen from outside train stations between 2021 and 2023. A freedom of information request revealed bicycle thefts from outside stations increased by 39 per cent from 2022 to 2023. 

An estimated 1.33 million cycle journeys were recorded by Transport for London in 2024, but critics have said bike thefts will discourage people from cycling in the capital.

“We know that people who have their bike stolen quite often don’t go back to cycling,” the London Cycling Campaign’s Simon Munk told the BBC. 

“Everyone understands that more cycling, more walking, fewer people in cars is a good thing for London [and] for the planet – for everyone,” he added. 

Gordon said: “Bike theft is not a petty crime but has serious social consequences and the police need to take it seriously – to have your means of getting around stolen can be devastating.

“By partnering with cycle trade, planners and other groups, the police could find ways to prevent cycle theft, seeing as that’s more effective than enforcement, but it’s not acceptable for the police to say they will be doing less to investigate theft, when they should be doing more.” 

BTP said that these crimes are unlikely ever to be solved. “The more time our officers spend reviewing CCTV footage for these offences, the less time they have available for patrolling railway stations and trains, investigating crimes which cause the most harm and providing a visible presence across the network,” a BTP spokesperson told the BBC. 

“We will continue to apply a test of proportionality when determining investigation – looking at factors such as timeframes, witnesses, the availability of CCTV, the impact on the victim or whether there is a realistic prospect of a successful outcome.

“Any offence which is not investigated will still provide us with valuable intelligence, used to direct our patrols and operations.”

You may like
Steve Jobs Remembered on 14th Anniversary of His Death

Steve Jobs died 14 years ago. But the blog Cult of Mac remembers that “Jobs himself was not sentimental.”

When he left Apple in the mid-1980s, he didn’t even clear out his office. That meant personal mementos like his first Apple stock certificate, which had hung on his office wall, got tossed in the trash. Shortly after returning to Apple in the late 1990s, he gave the company’s historical archive to Stanford University Libraries. The stash included records that Apple management kept since the mid-1980s. The reason Apple handed over this historical treasure trove? Jobs didn’t want the company to fixate on the past…

All of which goes some way to saying why it was so heartening that Steve Jobs’ death received so much attention. He wasn’t the richest technology CEO to die. But the reaction showed that his life — faults and all — meant a lot to a great number of people. Jobs helped create products people cared about, and in turn they cared about him.
The site Mac Rumors remembered Sunday that Jobs “died just one day after Apple unveiled the iPhone 4S and Siri.” Six years later, Apple CEO Tim Cook reflected on Jobs while opening Apple’s first-ever event at Steve Jobs Theater in 2017. “There is not a day that goes by that we don’t think about him.”

And Sunday Cook posted this remembrance of Steve Jobs. “Steve saw the future as a bright and boundless place, lit the path forward, and inspired us to follow.

“We miss you, my friend.”


Read more of this story at Slashdot.

What Happens When AI Directs Tourists to Places That Don’t Exist?

The director of a tour operation remembers two tourists arriving in a rural town in Peru determined to hike alone in the mountains to a sacred canyon recommended by their AI chatbot. But the canyon didn’t exists — and a high-altitude hike could be dangerous (especially where cellphone coverage is also spotty). They’re part of a BBC report on travellers arriving at their destination “only to find they’ve been fed incorrect information or steered to a place that only exists in the hard-wired imagination of a robot…”
“According to a 2024 survey, 37% of those surveyed who used AI to help plan their travels reported that it could not provide enough information, while around 33% said their AI-generated recommendations included false information.” Some examples?

– Dana Yao and her husband recently experienced this first-hand. The couple used ChatGPT to plan a romantic hike to the top of Mount Misen on the Japanese island of Itsukushima earlier this year. After exploring the town of Miyajima with no issues, they set off at 15:00 to hike to the montain’s summit in time for sunset, exactly as ChatGPT had instructed them. “That’s when the problem showed up,” said Yao, a creator who runs a blog about traveling in Japan, “[when] we were ready to descend [the mountain via] the ropeway station. ChatGPT said the last ropeway down was at 17:30, but in reality, the ropeway had already closed. So, we were stuck at the mountain top…”
– A 2024 BBC article reported that [dedicated travel AI site] Layla briefly told users that there was an Eiffel Tower in Beijing and suggested a marathon route across northern Italy to a British traveller that was entirely unfeasible…
– A recent Fast Company article recounted an incident where a couple made the trek to a scenic cable car in Malaysia that they had seen on TikTok, only to find that no such structure existed. The video they’d watched had been entirely AI generated, either to drum up engagement or for some other strange purpose.

Rayid Ghani, a distinguished professor in machine learning at Carnegie Melon University, tells them that an AI chatbot “doesn’t know the difference between travel advice, directions or recipes. It just knows words. So, it keeps spitting out words that make whatever it’s telling you sound realistic…”


Read more of this story at Slashdot.

Removing 50 Objects from Orbit Would Cut Danger From Space Junk in Half

If we could remove the 50 most concerning pieces of space debris in low-Earth orbit, there’d be a 50% reduction in the overall debris-generating potential, reports Ars Technica. That’s according to Darren McKnight, lead author of a paper presented Friday at the International Astronautical Congress in Sydney, which calculated the objects most likely to collide with other fragments and create more debris. (Russia and the Soviet Union lead with 34 objects, followed by China with 10, the U.S. with three, Europe with two, and Japan with one.) Even just the top 10 were removed, the debris-generating potential drops by 30%.

“The things left before 2000 are still the majority of the problem,” he points out, and “76% of the objects in the top 50 were deposited last century.” 88% of the objects are post-mission rocket bodies left behind to hurtle through space.

“The bad news is, since January 1, 2024, we’ve had 26 rocket bodies abandoned in low-Earth orbit that will stay in orbit for more than 25 years,” McKnight told Ars… China launched 21 of the 26 hazardous new rocket bodies over the last 21 months, each averaging more than 4 metric tons (8,800 pounds). Two more came from US launchers, one from Russia, one from India, and one from Iran. This trend is likely to continue as China steps up deployment of two megaconstellations — Guowang and Thousand Sails — with thousands of communications satellites in low-Earth orbit.

Launches of these constellations began last year. The Guowang and Thousand Sails satellites are relatively small and likely capable of maneuvering out of the way of space debris, although China has not disclosed their exact capabilities. However, most of the rockets used for Guowang and Thousand Sails launches have left their upper stages in orbit. McKnight said nine upper stages China has abandoned after launching Guowang and Thousand Sails satellites will stay in orbit for more than 25 years, violating the international guidelines.

It will take hundreds of rockets to fully populate China’s two major megaconstellations. The prospect of so much new space debris is worrisome, McKnight said. “In the next few years, if they continue the same trend, they’re going to leave well over 100 rocket bodies over the 25-year rule if they continue to deploy these constellations,” he said. “So, the trend is not good….” Since 2000, China has accumulated more dead rocket mass in long-lived orbits than the rest of the world combined, according to McKnight. “But now we’re at a point where it’s actually kind of accelerating in the last two years as these constellations are getting deployed.”

A deputy head of China’s national space agency recently said China is “currently researching” how to remove space debris from orbit, according to the article. (“One of the missions China claims is testing space debris mitigation techniques has docked with multiple spacecraft in orbit, but U.S. officials see it as a military threat. The same basic technologies needed for space debris cleanup — rendezvous and docking systems, robotic arms, and onboard automation — could be used to latch on to an adversary’s satellite.”)


Read more of this story at Slashdot.

Are Software Registries Inherently Insecure?

“Recent attacks show that hackers keep using the same tricks to sneak bad code into popular software registries,” writes long-time Slashdot reader selinux geek, suggesting that “the real problem is how these registries are built, making these attacks likely to keep happening.”

After all, npm wasn’t the only software library hit by a supply chain attack, argues the Linux Security blog. “PyPI and Docker Hub both faced their own compromises in 2025, and the overlaps are impossible to ignore.”
Phishing has always been the low-hanging fruit. In 2025, it wasn’t just effective once — it was the entry point for multiple registry breaches, all occurring close together in different ecosystems… The real problem isn’t that phishing happened. It’s that there weren’t enough safeguards to blunt the impact. One stolen password shouldn’t be all it takes to poison an entire ecosystem. Yet in 2025, that’s exactly how it played out…

Even if every maintainer spotted every lure, registries left gaps that attackers could walk through without much effort. The problem wasn’t social engineering this time. It was how little verification stood between an attacker and the “publish” button. Weak authentication and missing provenance were the quiet enablers in 2025… Sometimes the registry itself offers the path in. When the failure is at the registry level, admins don’t get an alert, a log entry, or any hint that something went wrong. That’s what makes it so dangerous. The compromise appears to be a normal update until it reaches the downstream system… It shifts the risk from human error to systemic design.

And once that weakly authenticated code gets in, it doesn’t always go away quickly, which leads straight into the persistence problem… Once an artifact is published, it spreads into mirrors, caches, and derivative builds. Removing the original upload doesn’t erase all the copies… From our perspective at LinuxSecurity, this isn’t about slow cleanup; it’s about architecture. Registries have no universally reliable kill switch once trust is broken. Even after removal, poisoned base images replicate across mirrors, caches, and derivative builds, meaning developers may keep pulling them in long after the registry itself is “clean.”

The article condlues that “To us at LinuxSecurity, the real vulnerability isn’t phishing emails or stolen tokens — it’s the way registries are built. They distribute code without embedding security guarantees. That design ensures supply chain attacks won’t be rare anomalies, but recurring events.”BR>

So in a world where “the only safe assumption is that the code you consume may already be compromised,” they argue, developers should look to controls they can enforce themselves:

Verify artifacts with signatures or provenance tools. Pin dependencies to specific, trusted versions. Generate and track SBOMs so you know exactly what’s in your stack. Scan continuously, not just at the point of install.


Read more of this story at Slashdot.

Fake AI-Generated Actress Gets Agent – and a Very Angry Reaction from (Human) Actors Union

A computer-generated actress appearing in Instagram shorts now has a talent agent, reports the Los Angeles Times.
The massive screen actors union SAG-AFTRA “weighed in with a withering response.”

SAG-AFTRA believes creativity is, and should remain, human-centered. The union is opposed to the replacement of human performers by synthetics.

To be clear, “Tilly Norwood” is not an actor, it’s a character generated by a computer program that was trained on the work of countless professional performers — without permission or compensation. It has no life experience to draw from, no emotion and, from what we’ve seen, audiences aren’t interested in watching computer-generated content untethered from the human experience. It doesn’t solve any “problem” — it creates the problem of using stolen performances to put actors out of work, jeopardizing performer livelihoods and devaluing human artistry.

Additionally, signatory producers should be aware that they may not use synthetic performers without complying with our contractual obligations, which require notice and bargaining whenever a synthetic performer is going to be used.

“They are taking our professional members’ work that has been created, sometimes over generations, without permission, without compensation and without acknowledgment, building something new,” SAG-AFTRA President Sean Astin told the Los Angeles Times in an interview:
“But the truth is, it’s not new. It manipulates something that already exists, so the conceit that it isn’t harming actors — because it is its own new thing — ignores the fundamental truth that it is taking something that doesn’t belong to them,” Astin said. “We want to allow our members to benefit from new technologies,” Astin said. “They just need to know that it’s happening. They need to give permission for it, and they need to be bargained with….”

Some actors called for a boycott of any agents who decide to represent Norwood. “Read the room, how gross,” In the Heights actor Melissa Barrera wrote on Instagram. “Our members reserve the right to not be in business with representatives who are operating in an unfair conflict of interest, who are operating in bad faith,” Astin said.

But this week the head of a new studio from startup Luma AI “said all the big companies and studios were working on AI assisted projects,” writes Deadline — and then claimed “being under NDA, she was not in a position to announce any of the details.”


Read more of this story at Slashdot.