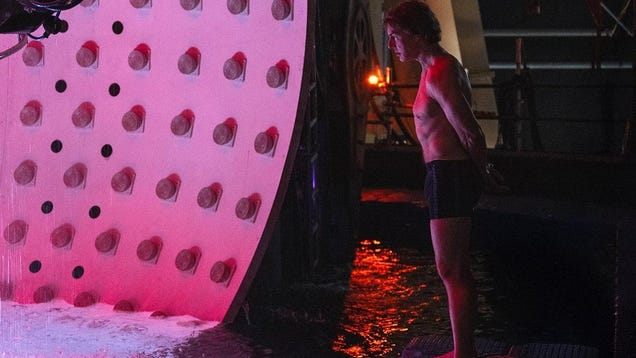
Tom Cruise Promises Underwater Sequence ‘Unlike Any Other’ In Mission: Impossible – The Final Reckoning

From speeding trains to flying motorcycles, Tom Cruise has continuously tried to one-up himself with each successive Mission: Impossible movie, sometimes breaking bones in the process. So what could he possibly do in Mission: Impossible — The Final Reckoning to raise the bar? Well, hanging off the side of an airplane…

Read more…

Raw Dating App Left User Data Unprotected, Exposing Private Details For All To See

Raw Dating App Left User Data Unprotected, Exposing Private Details For All To See
Data breaches, whether due to the nefarious activities of hackers or inadequate security measures, are a major concern due to the harm they can cause to affected users. In this latest breach, a report claims that the dating app Raw left user data unprotected, exposing private details for all to see.

Raw was launched in 2023. The app encourages

[$] Injecting speculation barriers into BPF programs

The disclosure of the Spectre
class of hardware vulnerabilities
created a lot of pain for kernel
developers (and many others). That pain was especially acutely felt in the
BPF community. While an attacker might have to painfully search the kernel
code base for exploitable code, an attacker using BPF can simply write and
load their own speculation gadgets, which is a much more efficient way of
operating. The BPF community reacted by, among other things, disallowing
the loading of programs that may include speculation gadgets. Luis
Gerhorst would like to change that situation with this patch
series
that takes a more direct approach to the problem.

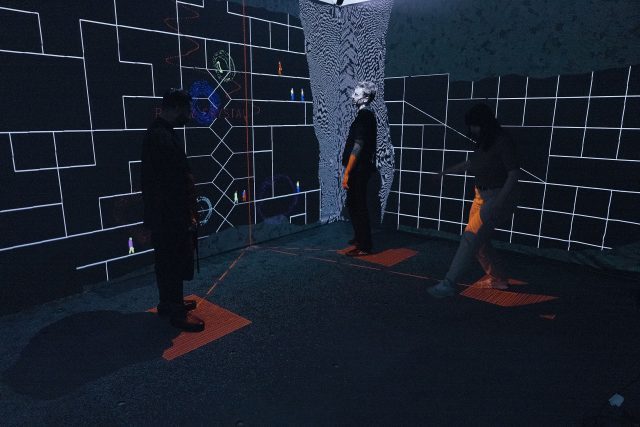
[Industry Direct] PHI Studio & Agog Are Seeking Immersive Artists for a Four Week Residency Program

Industry Direct by PHI Studio

Industry Direct is our program for sponsors who want to speak directly to the Road to VR newsletter audience. Industry Direct posts are written by sponsors with no involvement from the Road to VR editorial team and do not appear in our front-page editorial feed. Industry Direct sponsors help make Road to VR possible.

Are you an artist, designer, or creative technologist working with XR, immersive storytelling, or interactive media? Do you have a project that needs time, space, and expert guidance to fully take shape? If so, we would love to hear from you.

The PHI Immersive Residency is now accepting applications for its next cohort, on the theme of “XR for Impact”—and we’re calling on creators from North America (including Canada, the United States, Mexico, Greenland, Saint-Pierre and Miquelon, and Bermuda) who are exploring the edges of immersive art, narrative innovation, and experiential design.

A Residency for the Immersive-Minded

Hosted by PHI Studio in Montreal, Canada, and presented in partnership with Agog: The Immersive Media Institute, a grantmaking and capacity-building organization that inspires creators and changemakers to use XR for good, the residency program is designed to support creators by offering collaborative opportunities with PHI Studio experts and resources.

The residency offers artists the chance to spend four weeks developing an immersive or interactive project with the support of PHI’s internationally recognized team. The program is open to artists whose projects address and engage audiences in contemporary challenges and urgent global issues.

PHI Studio is known for producing and touring groundbreaking experiences like Space Explorers: THE INFINITE. Our in-house expertise spans creative direction, technical design, narrative development, and large-scale immersive production. This residency offers early access to that network, those skills, and the freedom to focus deeply on your work.

This is a residency for projects in their development phase to conceptualize, plan, and prototype. It’s a space to experiment, test, and evolve your vision with the guidance of a team that knows how to bring immersive work to audiences around the world.

What You’ll Get

  • 4 weeks in residence at PHI Studio in Montreal
  • Project Development Support: Tailored support and mentorship from PHI Studio during the residency, including assistance with conceptualization, creation, scenography, production, technical development, and programming support, or other PHI Studio expertise
  • A grant of $15,000 CAD to support the work carried out throughout the residency program
  • Accommodation for the duration of the residency, round-trip travel expenses and local transportation for artists residing outside of Montréal metropolitan area for the duration of the residency.
  • Access to PHI’s creative community, industry network, and technical tools

We are especially interested in projects that engage with immersive media in fresh and unexpected ways like extended reality (XR) technologies, artificial intelligence, and immersive sound or audio.

Who Should Apply?

This residency is open to artists, groups, or collectives working in immersive, XR, interactive or experiential disciplines. You don’t need to have all the answers, but you should have a strong concept, a willingness to explore, and a clear idea of how PHI Studio’s support could help push your work further.

We welcome applications from emerging and established creators alike, and we encourage artists from underrepresented communities to apply.

How to Apply

The application process is simple:

  1. Go to the residency application page
  2. Read through the residency details and eligibility
  3. Submit your application form and your project proposal

Deadline to apply: June 24, 2025, at 11:59 PM EDT

Questions? Reach out to us at phiimmersive@phi.ca. We can’t wait to see what you’re working on!

The post [Industry Direct] PHI Studio & Agog Are Seeking Immersive Artists for a Four Week Residency Program appeared first on Road to VR.

Google is reportedly getting back into film and TV with a tech-friendly production initiative

Google plans to start producing its own films and television shows via a “production initiative” called 100 Zeros, Business Insider reports. The company is working with Range Media Partners, a talent management and production company, to identify projects that appeal to younger audiences and could “promote a positive view of [Google’s] products.”

Besides the obvious opportunity for product placement, the larger goal of the initiative is to fund projects that have a positive view of technology, and to get the creative industry interested in using Google’s products. Immersive View, Google’s 3D aerial scans featured in Google Maps, could be a tool it pushes, Business Insider writes. Veo 2, Google’s AI video model, seems like a natural candidate, too. Whichever way the company goes, 100 Zeros already has a movie under its belt: The initiative reportedly helped pay for the marketing for the indie horror movie Cuckoo.

Engadget has reached out to Google to confirm the details of Business Insider‘s report and share more information about 100 Zeros. We’ll update this article if we hear back.

Google has some experience in the entertainment industry through its defunct YouTube Red Originals program. When YouTube first launched YouTube Red, the subscription service now called YouTube Premium, it did so alongside a slate of original content featuring notable YouTube talent. The program produced a number of shows and films, including popular series that found homes on other streaming services, like Cobra Kai, but never became a true competitor to Netflix. 

100 Zeros doesn’t sound like another YouTube Red, and instead, a more traditional play to make original content and sell it to other distributors — just with a potentially Google-y flavor.

This article originally appeared on Engadget at https://www.engadget.com/entertainment/tv-movies/google-is-reportedly-getting-back-into-film-and-tv-with-a-tech-friendly-production-initiative-185138762.html?src=rss

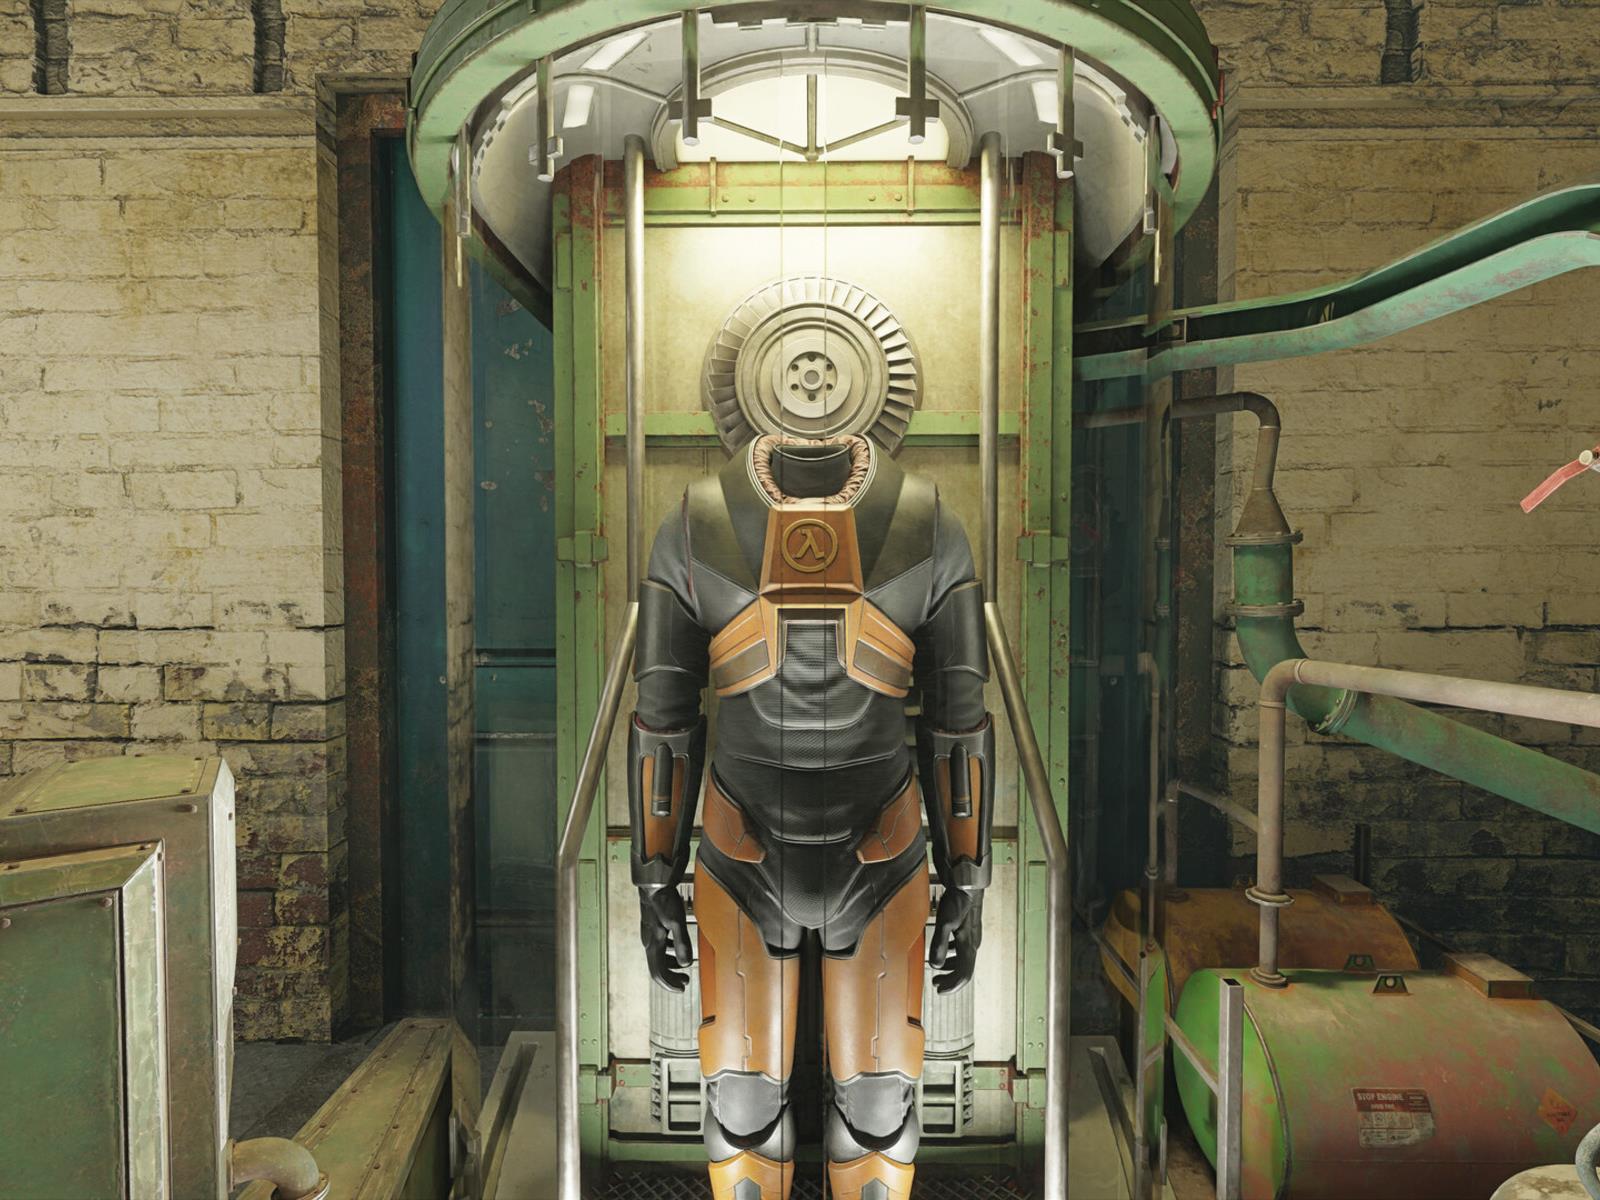
Half-Life 3 Hype Intensifies On Report Of A Fully Playable Build And Imminent Launch

Half-Life 3 Hype Intensifies On Report Of A Fully Playable Build And Imminent Launch
The dream of finally playing Half-Life 3 remains alive and well. Even though fans have gotten Black Mesa, which modernizes the original game, and have a gorgeous remasteed Half-Life 2 in the pipeline, there’s still a yearning for a new adventure featuring Gordon Freeman. If an insider is to be believed, this might come to fruition sooner rather

TeleMessage, a Signal clone the Trump administration uses, has been hacked

A hacker has exploited a vulnerability in TeleMessage to breach the service and steal data, according to reporting by 404 Media. TeleMessage is an Israeli company that provides modded versions of encrypted messaging apps like Signal and Telegram.

It was revealed last week that former US National Security Adviser Mike Waltz used TeleMessage’s modified version of Signal to archive messages. Today’s report indicated the presence of other high-ranking government officials in archived chats on the app, including Marco Rubio, Tulsi Gabbard and Vice President JD Vance.

The unnamed hacker was able to access archived chats, but it doesn’t look like they got into any of Waltz’s conversations. The hack does, however, prove that the app’s message archiving service is not end-to-end encrypted. 

The hacker also accessed contact information of government officials, login credentials for TeleMessage and data pertaining to the US Customs and Border Protection agency. Some businesses who use the service, like Coinbase and Scotiabank, were also hacked. 404 Media spoke to the anonymous hacker, who said the whole thing only “took about 15-20 minutes” and that it “wasn’t much effort at all.” TeleMessage’s parent company Smarsh has yet to comment on the matter.

All of this happened after Waltz accidentally revealed he used TeleMessage during a cabinet meeting last week. This led people to question what kind of information was being shared on the app and how it was being secured. Now we know it wasn’t secured all that well.

Of course, it’s only been a few weeks since Signalgate, in which it was revealed that top US officials were using the messaging app Signal to discuss active combat operations. Prior to the Trump administration, government officials typically avoided consumer-grade messaging apps to hash out military plans. Instead, they used Sensitive Compartmented Information Facilities (SCIFs) and in-house encrypted communication channels.

This article originally appeared on Engadget at https://www.engadget.com/big-tech/telemessage-a-signal-clone-the-trump-administration-uses-has-been-hacked-183606147.html?src=rss

Open Home Foundation Marks Second Year with Structural Changes and Home Assistant 2025.4 Update

April 2025 marked the start of the Open Home Foundation’s second year. Since its launch at the State of the Open Home 2024 event, the Foundation has grown rapidly, gaining broad community and industry support. Last month’s 2025 event highlighted key milestones from its first year and outlined plans for continued development. Over the past […]

Microsoft Cracks Down On Bulk Email With Strict New Outlook Rules

BrianFagioli writes: Microsoft has officially begun rejecting high-volume emails that don’t meet its new authentication rules.

Here’s the deal. If you send more than 5,000 messages per day to Outlook.com addresses (including hotmail.com and live.com) and you’re not properly set up with SPF, DKIM, and DMARC, your emails may never arrive.


Read more of this story at Slashdot.

The US Government’s Signal Situation Just Got Worse

If you’re looking to send personal messages securely, Signal is a great option. If you’re a government official discussing classified information? Not so much.

So is the case with Trump administration officials: Last month, we learned that highly sensitive war plans were being discussed in Signal group chats, after Jeffrey Goldberg, editor-in-chief of The Atlantic, was accidentally added to the conversation by then-U.S. National Security Advisor Mike Waltz. (Trump has since fired Waltz—and then nominated him to be U.N. ambassador.)

‘Signalgate’ continues

There are many reasons why the administration’s “Signal strategy” is problematic, but the issues didn’t end there. On Thursday, Reuters posted a photograph of Mike Waltz during a cabinet meeting at the White House. While there are plenty of important people in the photograph to pay attention to, 404 Media zeroed in on Waltz—specifically, his iPhone. The outlet spotted that Waltz had what appeared to be a thread opened with officials like Tulsi Gabbard (Director of National Intelligence), Marco Rubio (Secretary of State), and JD Vance (Vice President), with the PIN verification message that Signal will routinely send to users to keep their credentials fresh in their minds.

However, 404 Media spotted that this wasn’t Signal’s usual PIN verification pop-up: The message says “TM SGNL PIN,” which is the PIN verification screen for TeleMessage, a Signal “clone” that advertises itself as a way to archive your Signal messages. While the app claims it does not break Signal’s secure messaging system to archive messages, 404 Media reports that the service as advertised has many security vulnerabilities.

It didn’t take long for those vulnerabilities to manifest in disaster, either. On Sunday, 404 Media reported a hacker broke into TeleMessage’s networks and stole customer data. While the hacker didn’t take everything, they did obtain some DMs and group chats, in addition to data of modified versions of other chat apps, like WhatsApp, Telegram, and WeChat, all in about 15 to 20 minutes of hacking. 404 Media says the hacker did not access Waltz’ chats or the conversations of any cabinet members, but they did access government officials’ names and contact information, credentials to log into TeleMessage’s backend panel (the tool that lets TeleMessage admins manage the service), as well as information that points to which agencies might use TeleMessage.

Some of the stolen messages appeared to show a discussion about an ongoing effort to whip up votes in support of a cryptocurrency bill. One text read, “Just spoke to a D staffer on the senate side – 2 cosponsors (Alsobrooks and gillibrand) did not sign the opposition letter so they think the bill still has a good chance of passage the senate with 5 more Ds supporting it.” The hack didn’t expose classified information, but it did reveal political conversations that the senders likely never intended to be printed in the press.

Why is TeleMessage insecure?

To understand why TeleMessage is not a secure service—and why it is unbelievable that a government agency would rely on it for classified conversations—you need to understand what makes Signal secure.

Signal chats are end-to-end encrypted. That means when you talk to someone over the app, only you and the recipient can access the conversation. When you send a message, that text is encrypted in transit, and decrypted when it reaches the other user’s device. If someone were to intercept the message in transit, it would look like a scramble of code—only the devices of the people in the chat can decrypt the message and return it to a readable form.

Because of this setup, not even Signal can access your messages. No authority can compel Signal to release your messages, since the company itself doesn’t have access to the only thing that can decrypt the messages: your device. Even if someone hacked Signal’s database, they’d be out of luck.

TeleMessage, on the other hand, breaks that security chain. In order to archive those messages, TeleMessage must first intercept them as plain-text and store them. While the company says that they do so while maintaining security, the fact that this hacker was able to obtain DMs proves end-to-end encryption is broken. The stolen information was taken from data captured for “debugging purposes,” an unintended leak of decrypted data in TeleMessage’s security chain. It doesn’t matter if the service stores all messages in an encrypted archive: The company handles decrypted data in insecure ways, which leaves it open for hackers to access.

Even before the hack, 404 Media was skeptical of the service’s security, since they advertised archiving these “end-to-end encrypted” messages in Gmail, a platform that is infamously not end-to-end encrypted. (Though TeleMessage said the Gmail aspect was just for a “demo.”) The outlet also highlights how Signal does not guarantee the privacy and security of unofficial versions of their app.

Signal is great for personal use—not classified information

Signal—and other end-to-end encrypted services like it—are great for personal security. Your messages cannot be accessed by anyone without physical access to the trusted devices involved, which goes a long way toward protecting your digital privacy.

But encryption isn’t the only security concern here. There are still plenty of vulnerabilities and weak points when it comes to digital communication of any kind—end-to-end encryption included.

Hackers know that these messages can only be decrypted by the devices involved. So, a great way to break that security is to hack the devices themselves. Hackers use malware like “Pegasus” to silently stow away onto a target’s device and access sensitive data—encrypted data included.

Hackers routinely target high-profile individuals with this type of malware, so much so that Apple issues a regular warning to affected users. Waltz is no exception: In the view of Mike Casey, the former director of National Counterintelligence and Center, there’s a “zero percent chance that someone hasn’t tried to install Pegasus or some other spyware on [Mike Waltz’s] phone…he is one of the top five, probably, most targeted people in the world for espionage.”

Of course, that’s just the concern with your own personal device. You also have to worry about the other end of the conversation. If you’re chatting with someone over an encrypted chat app, and their phone is compromised, it doesn’t matter how secure you are: Your messages are vulnerable. They don’t even need to be hacked: They could leave their phone unlocked for anyone to pick up and access. And if you’re talking in group chats—like Trump administration officials have been—the security implications only multiply.

There is risk involved in all digital communication: It’s up to you to decide what risk level the data you’re transferring is worth. For most personal conversations, you’re probably just fine sticking with an encrypted service like Signal. If you’re discussing details that could put lives at risk, however, it might be best to keep it in the SCIF.
Destiny 2: Year Of The Prophecy Release Date, $275 Bundle And More Revealed In Major Leak

Destiny 2: Year Of The Prophecy Release Date, $275 Bundle And More Revealed In Major Leak
Bungie is working towards the release of Marathon, which the company hopes will be its next big blockbuster, it’s still supporting Destiny 2 with new content updates despite a shrinking team. Unfortunately for the studio, it’s big reveal event for Destiny’s The Edge of Fate expansion, along with the details of an upcoming collector’s edition,

RIP Skype (2003–2025), survived by multiple versions of Microsoft Teams

Today is the day: Microsoft has formally shuttered the Skype app and service after announcing in February that Skype was being axed in favor of Microsoft Teams, the company’s Slack competitor.

The Skype apps have all been advertising the end of the service and pointing users to Teams for weeks now. As of today, if you open the app or navigate to the Skype site, you’ll be directed to use Teams instead. The last active vestige of Skype is the Skype Dial Pad, which Skype subscribers and members with Skype Credits can still use to make calls to traditional telephone numbers (the Dial Pad is also incorporated into Microsoft Teams Free).

It’s an unceremonious end for an app that was once synonymous with video calls. Microsoft originally bought Skype for $8.5 billion in 2011; it was also owned by eBay from 2005 to 2009 and by a group of venture capital firms between 2009 and 2011. Ironically, Microsoft bought the app to replace its own first-party communication client at the time, Windows Live Messenger (which itself had grown out of the old MSN Messenger).

Read full article

Comments