Windows 10 Support ‘Ends’ Today

An anonymous reader quotes a report from Ars Technica: Today is the official end-of-support date for Microsoft’s Windows 10. That doesn’t mean these PCs will suddenly stop working, but if you don’t take action, it does mean your PC has received its last regular security patches and that Microsoft is washing its hands of technical support. This end-of-support date comes about a decade after the initial release of Windows 10, which is typical for most Windows versions. But it comes just four years after Windows 10 was replaced by Windows 11, a version with stricter system requirements that left many older-but-still-functional PCs with no officially supported upgrade path. As a result, Windows 10 still runs on roughly 40 percent of the world’s Windows PCs (or around a third of US-based PCs), according to StatCounter data.

But this end-of-support date also isn’t set in stone. Home users with Windows 10 PCs can enroll in Microsoft’s Extended Security Updates (ESU) program, which extends the support timeline by another year. […] Home users can only get a one-year stay of execution for Windows 10, but IT administrators and other institutions with fleets of Windows 10 PCs can also pay for up to three years of ESUs, which is also roughly the amount of time users can expect new Microsoft Defender antivirus updates and updates for core apps like Microsoft Edge. Obviously, Microsoft’s preferred upgrade path would be either an upgrade to Windows 11 for PCs that meet the requirements or an upgrade to a new PC that does support Windows 11. It’s also still possible, at least for now, to install and run Windows 11 on unsupported PCs. Your day-to-day experience will generally be pretty good, though installing Microsoft’s major yearly updates (like the upcoming Windows 11 25H2 update) can be a bit of a pain.


Read more of this story at Slashdot.

Salesforce Says AI Customer Service Saves $100 Million Annually

Salesforce says it’s saving about $100 million a year by using AI tools in the software company’s customer service operations. From a report: The company is working to sell AI features that can handle work such as customer service or early-stage sales. To illustrate the value of the Agentforce product to business clients, Salesforce has been vocal about its own use of the technology.

Chief Executive Officer Marc Benioff announced the statistic on Salesforce’s savings during a speech Tuesday at the annual Dreamforce conference in San Francisco. The company said more than 12,000 customers are using Agentforce. For example, Reddit was able to cut customer support resolution time by 84%, Salesforce said.


Read more of this story at Slashdot.

NATO boss mocks Russian navy, which is on the hunt for Red October “the nearest mechanic”

When one of its Kilo-class, diesel-electric submarines recently surfaced off the coast of France, Russia denied that there was a problem with the vessel. The sub was simply surfacing to comply with maritime transit rules governing the English Channel, the Kremlin said—Russia being, of course, a noted follower of international law.

But social media accounts historically linked to Russian security forces suggested a far more serious problem on the submarine Novorossiysk. According to The Maritime Executive, “Rumors began to circulate on well-informed social media channels that the Novorossiysk had suffered a fuel leak. They suggested the vessel lacked onboard capabilities and was forced to surface to empty flooded compartments. Some reports said it was a dangerous fuel leak aboard the vessel, which was commissioned in 2012.”

France 24 quoted further social media reports as saying, “The submarine has neither the spare parts nor the qualified specialists onboard to fix the malfunction,” and it “now poses an explosion hazard.”

Read full article

Comments

Feds seize $15 billion from alleged forced labor scam built on “human suffering”

Federal prosecutors have seized $15 billion from the alleged kingpin of an operation that used imprisoned laborers to trick unsuspecting people into making investments in phony funds, often after spending months faking romantic relationships with the victims.

Such “pig butchering” scams have operated for years. They typically work when members of the operation initiate conversations with people on social media and then spend months messaging them. Often, the scammers pose as attractive individuals who feign romantic interest for the victim.

Forced labor, phone farms, and human suffering

Eventually, conversations turn to phony investment funds with the end goal of convincing the victim to transfer large amounts of bitcoin. In many cases, the scammers are trafficked and held against their will in compounds surrounded by fences and barbed wire.

Read full article

Comments

Destiny 2 Is In Dire Straits, Is This The End Of Bungie’s Hit Game?

Destiny 2 Is In Dire Straits, Is This The End Of Bungie's Hit Game?
It has been a tumultuous time for Destiny 2—and even as we were writing this with the game showing its lowest player count ever, Bungie dropped a new update hoping to fix some player progression complaints and keep people invested. The writing might just be on the wall, though. Despite a major leak for Year of the Prophecy, the upcoming Renegades expansion

Trump admin pressured Facebook into removing ICE-tracking group

Attorney General Pam Bondi today said that Facebook removed an ICE-tracking group after “outreach” from the Department of Justice. “Today following outreach from @thejusticedept, Facebook removed a large group page that was being used to dox and target @ICEgov agents in Chicago,” Bondi wrote in an X post.

Bondi alleged that a “wave of violence against ICE has been driven by online apps and social media campaigns designed to put ICE officers at risk just for doing their jobs.” She added that the DOJ “will continue engaging tech companies to eliminate platforms where radicals can incite imminent violence against federal law enforcement.”

When contacted by Ars, Facebook owner Meta said the group “was removed for violating our policies against coordinated harm.” Meta didn’t describe any specific violation but directed us to a policy against “coordinating harm and promoting crime,” which includes a prohibition against “outing the undercover status of law enforcement, military, or security personnel.”

Read full article

Comments

DirecTV Will Soon Bring AI Ads To Your Screensaver

DirecTV wants to use AI to put you, your family, and your pets inside a custom TV screensaver. From a report: If that’s not uncanny enough, you’ll find items you can shop for within that AI environment, whether it’s a piece of clothing similar to the one your AI likeness is wearing or a piece of furniture that pops up alongside it.

The satellite TV giant is partnering with the AI company Glance to roll out this experience to DirecTV Gemini devices starting next year. “We are making television a lean-in experience versus lean back,” Rajat Wanchoo, the group vice president of commercial partnerships at Glance, tells The Verge. “We want to give users a chance to use the advancements that have happened in generative AI to create a ChatGPT moment for themselves, but on TV.” Glance is owned by InMobi, the same company that injected ecommerce bloatware into Motorola’s budget phones.


Read more of this story at Slashdot.

Meta removes Facebook Group for tracking ICE agents after DOJ pressure

Attorney General Pam Bondi posted on X that the Department of Justice contacted Facebook in order to have a group removed that she claimed “was being used to dox and target” US Immigration and Customs Enforcement agents operating in Chicago. We reached out to Meta for confirmation and a representative said, “This Group was removed for violating our policies against coordinated harm,” however they did not confirm the name of the group or whether the DOJ was involved in the action. 

Officers for the immigration agency have reportedly been moving through Chicago with facial coverings, no name tags and sometimes in vehicles with no license plates, although a US District Judge ruled that all ICE agents who are not undercover are required to display visible identification while operating in the Chicagoland area. 

The Department of Justice has demanded that other tech companies remove content the current administration has deemed critical of its immigration policies and practices. At the start of the month, Apple removed ICEBlock, an app for tracking the movements of immigration agents, from the App Store following similar pressure from Bondi. “Capitulating to an authoritarian regime is never the right move,” ICEBlock developer Joshua Aaron said in an interview following the action. “Our mission has always been to protect our neighbors from the terror this administration continues to reign down on the people of this nation.”

This article originally appeared on Engadget at https://www.engadget.com/meta-removes-facebook-group-for-tracking-ice-agents-after-doj-pressure-203429574.html?src=rss

Microsoft’s October ‘Patch Tuesday’ Update Fixes Over 170 Flaws

Dd you know you can customize Google to filter out garbage? Take these steps for better search results, including adding my work at Lifehacker as a preferred source.


On the second Tuesday of each month, Microsoft issues a major security update for Windows users, known as “Patch Tuesday.” Some patches are larger than others; it all depends on how many vulnerabilities researchers discovered over the past month. October’s Patch Tuesday update, however, is quite large.

As reported by Bleeping Computer, this latest Patch Tuesday update fixes over 170 security flaws with Windows. That includes 80 elevation of privilege vulnerabilities, 31 remote code execution vulnerabilities, 28 information disclosure vulnerabilities, 11 security feature bypass vulnerabilities, 11 denial of service vulnerabilities, and 10 spoofing vulnerabilities.

Bleeping Computer only includes the patches released by Microsoft itself in its totals for Patch Tuesday numbers. The total number is higher, as there are patches for Azure, Mariner, and vulnerabilities released earlier in October. All in, there are well over 200 patches here.

While all security patches are important, some are more critical than others. To that point, this Patch Tuesday includes fixes for eight vulnerabilities labeled as “Critical”—that includes five remote code execution vulnerabilities, and three elevation of privilege vulnerabilities.

Six zero-days

But even more important than that are the patches for six zero-day vulnerabilities. Zero-days are particularly dangerous, as there are vulnerabilities that are either publicly disclosed or exploited before the software developer has a chance to issue a patch. In this case, there are six zero-days, three publicly disclosed, and three exploited without this current patch, leaving Windows users vulnerable.

These are the three exploited vulnerabilities:

  • CVE-2025-24990: Windows Agere Modem Driver Elevation of Privilege Vulnerability: This flaw allowed bad actors to gain administrative privileges via a bad Agere Modem driver. Microsoft has now removed the driver.

  • CVE-2025-59230: Windows Remote Access Connection Manager Elevation of Privilege Vulnerability: This flaw allowed bad actors to gain SYSTEM privileges.

  • CVE-2025-47827: MITRE CVE-2025-47827: Secure Boot bypass in IGEL OS before 11: This flaw allowed bad actors to bypass Secure Boot, a security process that helps prevent malware from loading when a user’s computer starts up.

These are the three publicly disclosed vulnerabilities:

  • CVE-2025-0033 – AMD CVE-2025-0033: RMP Corruption During SNP Initialization: This AMD flaw could impact memory integrity. Microsoft says this fix is not finished yet, and the patches will roll out through Azure Service Health Alerts when they’re ready.

  • CVE-2025-24052 – Windows Agere Modem Driver Elevation of Privilege Vulnerability: This flaw can be used to gain administrative privileges via a Agere Modem Driver. As Bleeping Computer notes, it appears quite similar to CVE-2025-24990.

  • CVE-2025-2884 – Cert CC: CVE-2025-2884 Out-of-Bounds read vulnerability in TCG TPM2.0 reference implementation: This flaw could have allowed for information disclosure or denial of service of the target’s TPM.

In other Microsoft news, the company has officially ended support for Windows 10. Unless you enroll in Extended Security Updates, your Windows 10 PC will not receive these security patches going forward.

Lawyer Caught Using AI While Explaining to Court Why He Used AI

An anonymous reader shares a report: An attorney in a New York Supreme Court commercial case got caught using AI in his filings, and then got caught using AI again in the brief where he had to explain why he used AI, according to court documents filed earlier this month.

New York Supreme Court Judge Joel Cohen wrote in a decision granting the plaintiff’s attorneys’ request for sanctions that the defendant’s counsel, Michael Fourte’s law offices, not only submitted AI-hallucinated citations and quotations in the summary judgment brief that led to the filing of the plaintiff’s motion for sanctions, but also included “multiple new AI-hallucinated citations and quotations” in the process of opposing the motion.

“In other words,” the judge wrote, “counsel relied upon unvetted AI — in his telling, via inadequately supervised colleagues — to defend his use of unvetted AI.”

The case itself centers on a dispute between family members and a defaulted loan. The details of the case involve a fairly run-of-the-mill domestic money beef, but Fourte’s office allegedly using AI that generated fake citations, and then inserting nonexistent citations into the opposition brief, has become the bigger story.


Read more of this story at Slashdot.

This GoPro Alternative Is 21% Off Right Now

We may earn a commission from links on this page. Deal pricing and availability subject to change after time of publication.

Did you know you can customize Google to filter out garbage? Take these steps for better search results, including adding my work at Lifehacker as a preferred source.


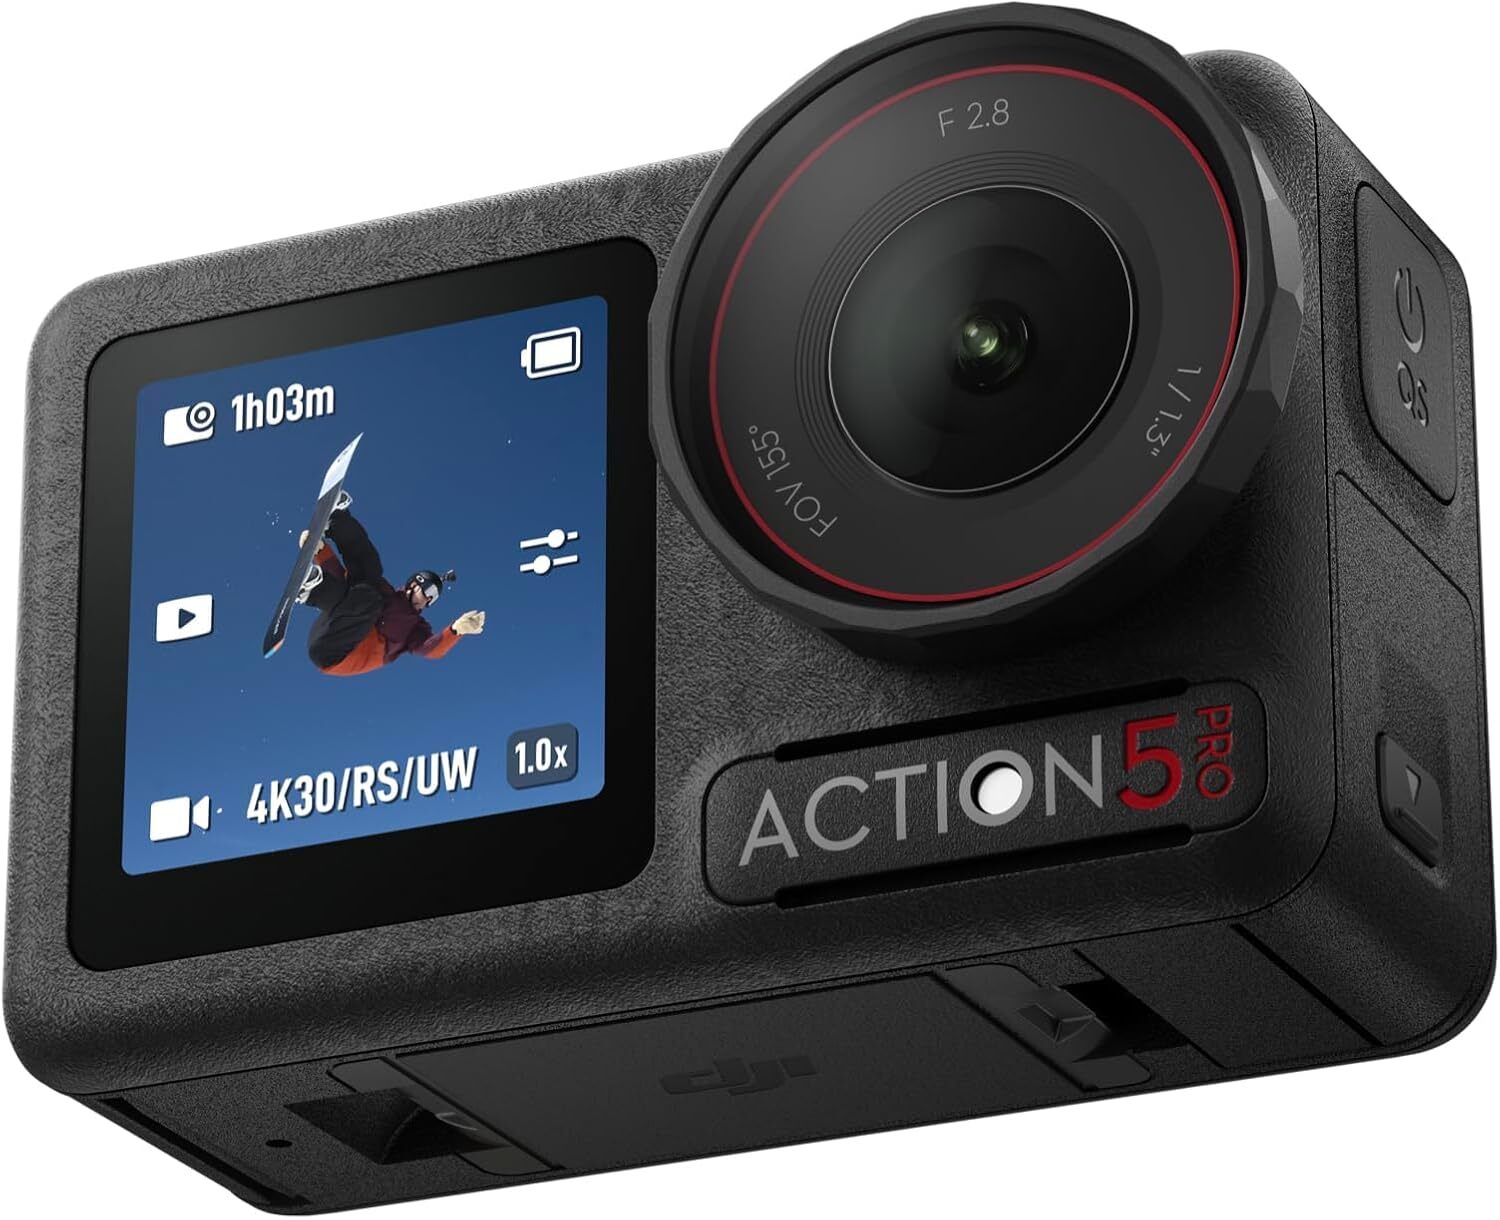
As far as action cameras go, GoPro might be a household name, but there are still some high-quality (and often more affordable) competitors that appeal to both casual adventurers and power users. One of them, the DJI Osmo Action 5 Pro (Essential Combo), is a #1 bestseller on Amazon, and is currently 21% off, marking its lowest price ever at $269.

This action cam is a tough, waterproof camera (up to 65.6 feet) that you can mount practically anywhere. It has a 10-bit 4K120 video, and at 5.2 ounces, it’s lightweight yet powerful, with dual touch displays and multiple field-of-view options, including an ultra-wide setting without distortion. It also records vertical video, with creative tools like time-lapse, slow motion, and a tracking mode that keeps subjects centered. Its digital stabilization system, RockSteady, keeps things smooth, and while it may slightly narrow the lens’s view, the extra-wide 155-degree angle still allows for immersive coverage. Compared to its predecessor, it has a new image sensor with bigger pixels, a more efficient processor, touch-sensitive OLED panels on both displays, and a bigger battery.

According to PCMag, which awarded it an “Outstanding” rating, its battery life blows other action cameras out of the water. Its 1,950mAh battery uses a 4nm architecture for its image processor. While it claims to provide up to four hours of continuous shooting, the PCMag tester found that it lasts 26 minutes at 4K60, 154 minutes at 4K30, and 182 minutes at 1080p30 without overheating, whereas the GoPro Hero13 only ran for around half an hour before overheating and provided just 80 minutes at 4K30.

While the app features and lens options may not be as strong or varied as GoPro’s, if you’re looking for an action camera with best-in-class battery life, strong digital stabilization, and the ability to record continuously without overheating, the DJI Osmo Action 5 Pro (Essential Combo) is a long-lasting powerhouse that rivals contenders like the Hero13. And at a sub-$300 price point, it’s well worth it.

Our Best Editor-Vetted Tech Deals Right Now


Ring Battery Doorbell Plus


—
$149.99

(List Price $149.99)


Ring Indoor Cam (2nd Gen, 2-pack, White)


—
$79.99

(List Price $99.98)


Amazon Fire TV Stick 4K (2nd Gen, 2023)


—
$29.99

(List Price $49.99)


Amazon Fire HD 10 (2023)


—
$69.99

(List Price $139.99)

Deals are selected by our commerce team

DirecTV screensavers will show AI-generated ads with your face in 2026

As if DirecTV doesn’t have enough trouble keeping customers, the satellite TV provider’s streaming devices will show AI-generated screensaver ads next year, according to an announcement today from partnering ads company Glance.

People who use either of DirecTV’s two Gemini streaming devices will start seeing the ads “in early 2026,” per the announcement. DirecTV’s Gemini Air is an Android TV-powered USB device that people can plug into a TV for access to live TV channels, as well as streaming apps. Gemini Air doesn’t require a DirecTV satellite connection, and DirecTV gives all of its Internet customers the device. DirecTV first started selling Gemini devices in 2023, when it launched a separate Gemini set-top box that connects through DirecTV satellite setups.

DirecTV made an agreement with Glance to show AI-generated content and ads on Gemini devices’ screensavers. Currently, Gemini devices show Google wallpapers as screensavers, which are on by default. When the new screensavers launch, Glance’s AI content will show if the TV is idle for 10 minutes, The Verge reported.

Read full article

Comments

Google reportedly offers to tweak search results to avoid EU fine

In order to avoid paying billions of dollars in fines for violating the European Union’s Digital Markets Act, Google is considering changing how search results are displayed, Reuters reports. EU regulators first took issue with Google’s Search and Play Store businesses in March 2025, claiming it favored its own services in search results over third-party options and prevented developers from informing customers of alternative ways of accessing apps.

One of regulators main issues with Google Search was that Google appeared to favor results from services like Google Flights or Google Hotels over ones from “vertical search services,” providers that specialize in displaying search results from a specific industry, like Expedia or Hotels.com. To avoid fines, Google now wants Search to give VSS businesses equal treatment in results.

“We will create the opportunity for each VSS to show its own box on Search. A VSS box will be populated with results from that VSS inventory,” Google said in a proposal viewed by Reuters. Results from Google’s own services will exist with the same formatting alongside, and the winning VSS box will be displayed in search results based on “objective and non-discriminatory criteria.” Importantly, search results from actual airlines and car rental companies won’t be excluded, they’ll also appear in a box “above or below the VSS box depending on the relevance to the user’s query.”

Engadget has asked Google to comment on Reuters‘ report and to confirm the details of its proposed changes to Google Search. We’ll update this article if we hear back.

Like Apple, Google faces significant scrutiny from the EU because of its monopolistic control over its various platforms and services. The threat of fines from the DMA has forced Apple to open up its products to third-party app stores, among a host of other changes. Clearly, Google is willing to tweak what once seemed like untouchable pillars of its business to avoid fines, too. Whether these proposed changes will be enough for the regulators remains to be seen, though.

This article originally appeared on Engadget at https://www.engadget.com/big-tech/google-reportedly-offers-to-tweak-search-results-to-avoid-eu-fine-193940005.html?src=rss

Spotify Premium Subscribers Can Finally Save Their Algorithm From Their Kids

Did you know you can customize Google to filter out garbage? Take these steps for better search results, including adding my work at Lifehacker as a preferred source.


If you have a Premium Family plan through Spotify, there’s good news: You can now set up managed accounts for your kids. Not only can you control what they listen to, their music choices won’t reflect in or affect your listening history. Congratulations: You’re getting your Wrapped back.

On Tuesday, Spotify announced it is rolling out managed accounts for Premium subscribers to seven new regions: the U.S., UK, Canada, Australia, Germany, France, and the Netherlands. Premium Family subscribers in these countries can now create managed accounts for users younger than 13 that allow those users to listen on their own, in a controlled environment.

Managed accounts are music-only, so younger listeners can’t browse Spotify’s other offerings, such as podcasts, or send or receive DMs. In addition, account managers can control a number of settings on these accounts, including whether the account can listen to explicit music, choose to block specific artists and songs, and decide to hide video—including short-form Canvas content.

While Spotify has an existing service designed for children, Spotify Kids, it’s much different, as it only contains music hand-picked for the service, and doesn’t allow subscribers to control the account. Managed accounts allow subscribers to give a full Spotify experience to their kids, while having total control over what they can listen to.

Personally, I think this is a fantastic feature. As someone who grew up in the early days of iTunes, I would have loved the ability to add whatever songs I wanted to my playlists—assuming my parents gave those songs the OK, of course. It’s also great that kids can get recommendations for new music from Spotify. If they are obsessed with the latest trending song, perhaps Spotify can recommend similar tunes, both contemporary tracks as well as classics. It could be a great way to expand kids’ music tastes.

Spotify first tested managed accounts in 10 other countries: New Zealand, Sweden, Denmark, Spain, Italy, Portugal, Brazil, Mexico, Argentina, and Columbia. It’s now available as part of its Premium Family plan, which costs $19.99 per month.

How to create a managed account

If you’re using the Spotify mobile app, head to Settings and privacy > Account > Premium Family. If you’re on your account page on Spotify’s website, choose “Manage members.” Either way, under Plan members, choose to add members to your plan. Choose “Add a listener aged under 13,” then choose “Add account.”

You’ll then follow the on-screen steps to confirm you are the parent or guardian of the listener; set a PIN to control the experience; choose the name and birthdate of the listener; and choose your settings.

Indonesia’s Film Industry Embraces AI To Make Hollywood-style Movies For Cheap

Indonesia’s film industry has started using generative AI tools to produce films at a fraction of Hollywood budgets. The country’s filmmakers are deploying ChatGPT for scriptwriting, Midjourney for image generation, and Runway for video storyboarding. VFX artist Amilio Garcia Leonard told Rest of World that AI has reduced his draft editing time by 70%.

The Indonesian Film Producer Association supports the technology. Indonesian films typically cost 10 billion rupiah ($602,500), less than 1% of major Hollywood productions. The sector employed about 40,000 people in 2020 and generated over $400 million in box office sales in 2023. Jobs for storyboarders, VFX artists, and voice actors are disappearing.


Read more of this story at Slashdot.

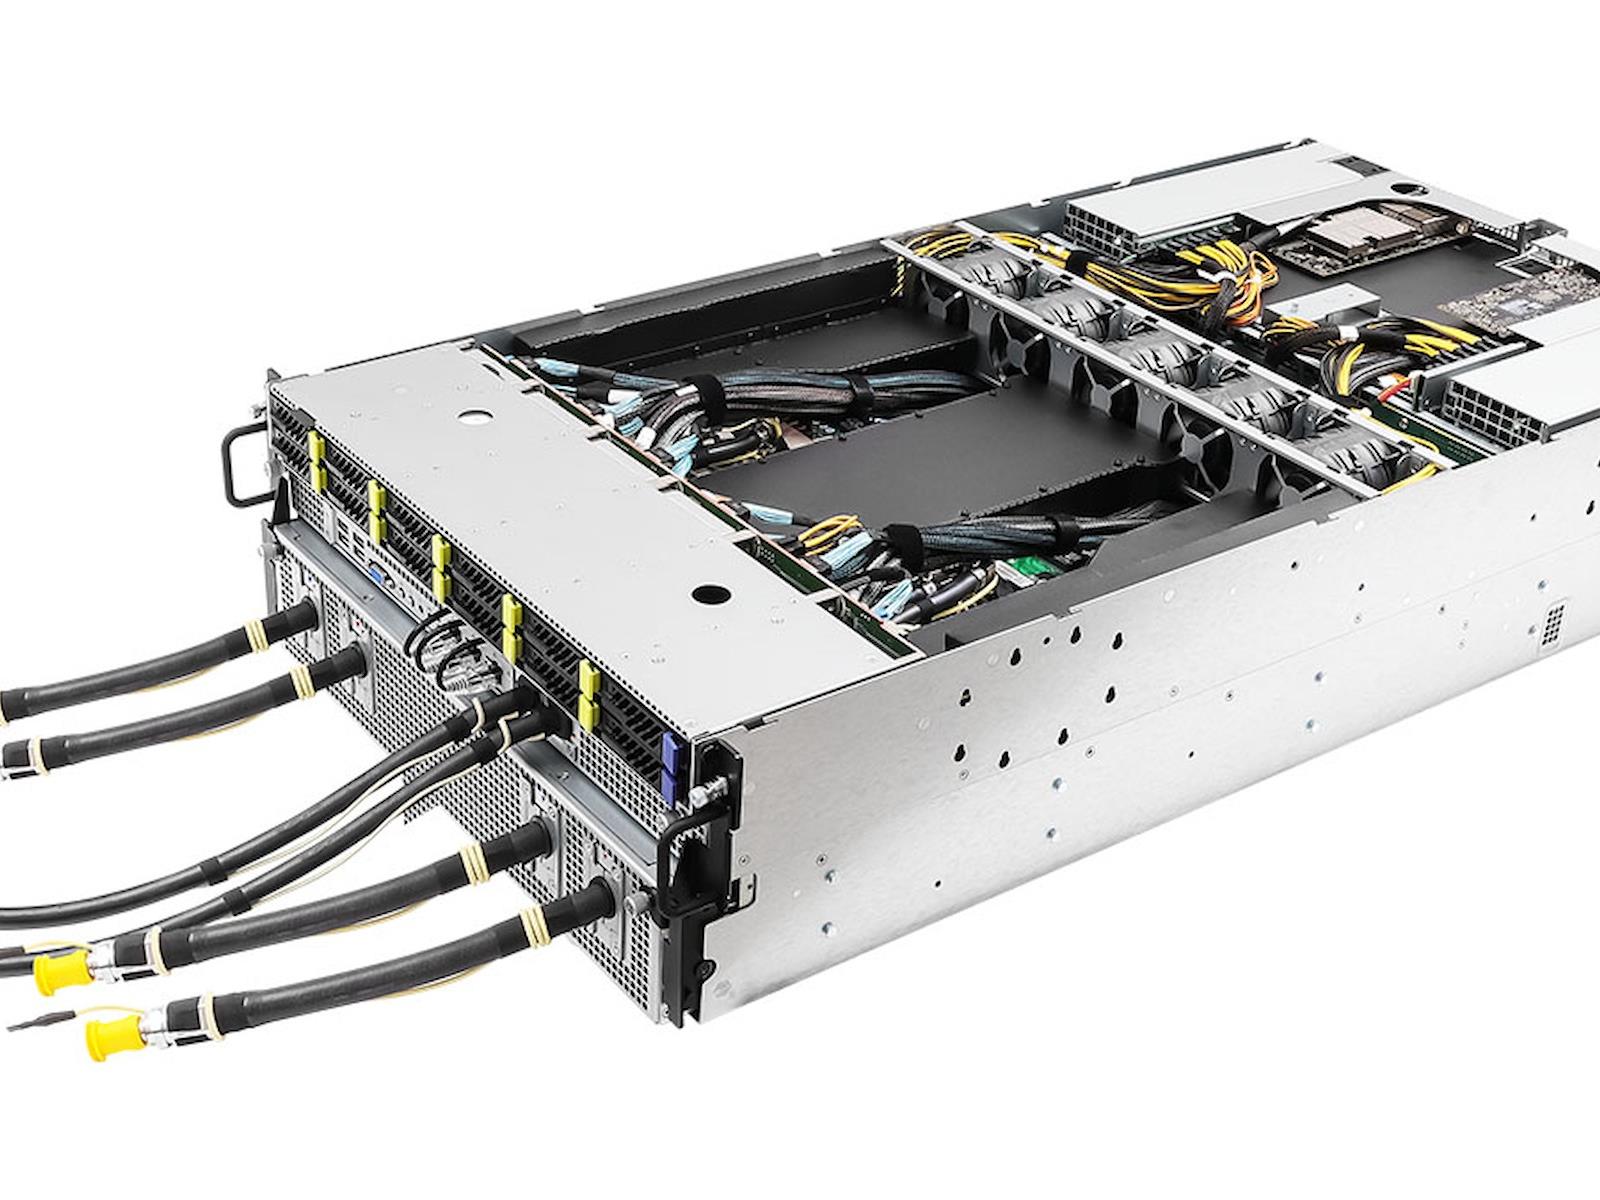
ASRock’s Liquid-Cooled NVIDIA HGX B300 Server Doesn’t Use Any Water

ASRock's Liquid-Cooled NVIDIA HGX B300 Server Doesn't Use Any Water
At the 2025 OCP Global Summit in San Jose, ASRock Rack and ZutaCore jointly unveiled what they’re calling the first NVIDIA HGX B300 system with fully integrated “waterless liquid cooling.” The new 4U16X-GNR2/ZC server pairs NVIDIA’s latest “Blackwell” AI hardware with ZutaCore’s HyperCool direct-to-chip cooling technology, aiming to keep pace

The ‘Pixnapping’ Attack Can Steal Your 2FA Codes

Did you know you can customize Google to filter out garbage? Take these steps for better search results, including adding my work at Lifehacker as a preferred source.


Researchers have demonstrated a new type of malware attack that can steal sensitive information from Android devices—including Google and Samsung phones—without the knowledge or action of the target user.

The attack is called “Pixnapping,” an apparent portmanteau of “pixel” and “snapping.” When you download and open a piece of software containing the malware, the app scans your phone for specific apps it might want to spy on. It then accesses another app on your phone—say, Google Authenticator—but rather than open it, it pulls the information that would be displayed into the Android rendering pipeline. From there, the app scans the display information for individual pixels, targeting areas known to contain sensitive information. In the case of Google Authenticator, the focus is on the pixels known to contain the 2FA codes within the app. The malware then checks to see whether a pixel is blank, or contains some type of rendered content. It uses these findings to recover the original images, like a complete 2FA code, without ever actually having seen the original images in the first place.

This process can repeat for as long as it takes to scan the stolen pixels and pull the original information from them, all without you knowing it’s happening. Researchers compare the process to taking screenshots of screen contents the malware should not have access to.

How the malware works

There are three reasons Pixnapping attacks are possible on Android, according to researchers. First, the OS allows apps to send another app’s activity to the Android rendering pipeline, which allows the malicious app to invoke sensitive activities, like refreshing 2FA codes. Second, apps can run graphical operations on pixels displayed through another app’s activity, which is how the malicious app can pull pixels from something like Google Authenticator. Third, apps can measure the pixel color-dependent side effects of those operations, which allows the malicious app to leak the pixel values.

Researchers demonstrated these Pixnapping attacks on Google and Samsung phones, including the Pixel 6, Pixel 7, Pixel 8, Pixel 9, and Galaxy S25. These phones were running Android 13, 14, 15, and 16. Researchers say they aren’t sure if other types of Android devices are affected by this attack, though the “core mechanisms” involved are usually present in all Android devices. Different Pixel devices had different rates of success in the 2FA hack (73%, 53%, 29%, and 53% for the Pixel 6, 7, 8, and 9, respectively), though researchers could not obtain 2FA codes on the Galaxy S25 within the 30 second timeline before the codes refreshed.

In addition to devices, researchers demonstrated Pixnapping attacks on sites and services like Gmail, Google Accounts, Signal, Google Authenticator, Venmo, and Google Maps. The implication is that this type of attack could steal many different types of information from your phone, including emails, encrypted messages, payment records, and location histories.

According to the findings, Google has tried to patch Pixnapping, but researchers were able to workaround this patch in demonstrated attacks. The vulnerability is currently tracked as CVE-2025-48561. Google is working on a new patch for the December Android security builtin.

How to protect yourself from Pixnapping

The good news, at this time anyway, is that researchers are not aware of Pixnapping attacks happening in the wild. However, that doesn’t mean they won’t happen, especially now that the attack has been disclosed.

The first thing to do to protect yourself is to make sure you’re running the latest security patches on your Android device. While Google is still working on a subsequent Pixnapping patch, there is a patch in existence. Make sure you install it on your phone by heading to System > Software updates.

Next, be cautious with the apps you download on your device. Always try to download apps from trusted and verified marketplaces, as it’s much more difficult for bad actors to hide malware on apps distributed through these stores. Even when you download apps on something like the Google Play Store, investigate the app thoroughly: Ensure it’s really the app you think it is, and it’s coming from the developer that makes it. If you sideload apps, be careful with what you download, and only install apps from developers you trust.
Kobo made a remote control for its ereaders

Kobo is making a remote control for its line of ereaders. The appropriately-named Kobo Remote costs $30 and will be available to purchase on November 4.

A remote control for an ereader may seem silly to some, but avid readers will likely appreciate this accessory. It’s basically a wireless page turner, so users can lay in bed and read all day without having to physically hold the device or prop a hand up to push a button every 30 seconds. Kobo is calling it “the ideal reading companion.”

It has been custom-built for Kobo products and will be available in both black and white, which matches the company’s other products. It can integrate with any Kobo ereader with Bluetooth functionality, which includes the Libra 2 and the well-reviewed Clara Colour.

“In a Canadian winter, we know that sometimes maximum reading comfort means burrowing down in the blankets, tucking yourself in and not emerging until spring,” said Rakuten Kobo CEO Michael Tamblyn. “The Kobo Remote is the perfect accessory for peak immersive reading; it’s an invitation to lounge deeper, multitask smarter and simply enjoy reading without limits, no matter whether your environment is beach or blankets.”

The remote will be available in multiple regions, including the US, Canada, Europe, Australia, Singapore, Japan and many others. The company says it’ll be sharing more details about the remote soon, but we aren’t sure what details could be left to share. It’s a remote control for an ereader. Maybe it can do one or two unexpected things.

This article originally appeared on Engadget at https://www.engadget.com/mobile/tablets/kobo-made-a-remote-control-for-its-ereaders-185010955.html?src=rss

The World is Producing More Food Crops Than Ever Before

The United Nations Food and Agriculture Organization projects record production of global cereal crops in the 2025-26 farming season. The forecast covers wheat, corn and rice, and comes as the global stocks-to-use ratio stands around 30.6% — the world is producing nearly a third more of these foundational crops than it currently uses.

The U.S. Department of Agriculture reported in August that American farmers would harvest a record corn crop at record yield per acre. The FAO Food Price Index has risen slightly this year but remains nearly 20% below its peak during the early months of the war in Ukraine. Average calories available per person worldwide have climbed from roughly 2,100 to 2,200 kilocalories daily in the early nineteen-sixties to just under 3,000 kilocalories daily by 2022. Cereal yields have roughly tripled since 1961. Yet the World Bank estimates around 2.6 billion people cannot afford a healthy diet, and current famines in Gaza and Sudan stem from political failures rather than crop failures.


Read more of this story at Slashdot.

AMD & Intel Reflect On First Year Of x86 Ecosystem Alliance And Outline What’s Next

AMD & Intel Reflect On First Year Of x86 Ecosystem Alliance And Outline What's Next
Last year, AMD and Intel formed the x86 Ecosystem Advisory Group. On the cusp of their one year anniversary, AMD has released a blog post detailing the advancements made by AMD, Intel and “key ecosystem partners” in the time since, as well as setting some future expectations. The four things AMD highlights are the standardization of FRED (Flexible