The new series from Breaking Bad creator Vince Gilligan, Pluribus, was emphatically made by humans, not AI, reports TechCrunch:
If you watched all the way to the end of the new Apple TV show “Pluribus,” you may have noticed an unusual disclaimer in the credits: “This show was made by humans.” That terse message — placed right below a note that “animal wranglers were on set to ensure animal safety” — could potentially provide a model for other filmmakers seeking to highlight that their work was made without the use of generative AI.
In fact, yesterday the former X-Files writer told Variety “I hate AI. AI is the world’s most expensive and energy-intensive plagiarism machine….”
He goes on, about how AI-generated content is “like a cow chewing its cud — an endlessly regurgitated loop of nonsense,” and how the U.S. will fail to regulate the technology because of an arms race with China. He works himself up until he’s laughing again, proclaiming: “Thank you, Silicon Valley! Yet again, you’ve fucked up the world.”
He also says “there’s a very high possibility that this is all a bunch of horseshit,” according to the article. “It’s basically a bunch of centibillionaires whose greatest life goal is to become the world’s first trillionaires. I think they’re selling a bag of vapor.”
And earlier this week he told Polygon that he hasn’t used ChatGPT “because, as of yet, no one has held a shotgun to my head and made me do it.” (Adding “I will never use it.”)
Time magazine called Thursday’s two-episode premiere “bonkers.” Though ironically, that premiere hit its own dystopian glitch. “After months of buildup and an omnipresent advertising campaign, Apple’s much-anticipated new show Pluribus made its debut…” reports Macworld. “And the service promptly suffered a major outage across the U.S. and Canada.”
As reported by Bloomberg and others, users started to report that the service had crashed at around 10:30 p.m. ET, shortly after Apple made the first two episodes of the show available to stream. There were almost 13,000 reports on Downdetector before Apple acknowledged the problem on its System Status page. Reports say the outage was brief, lasting less than an hour…
[T]here remains a Resolved Outage note on Apple TV (simply saying “Some users were affected; users experienced a problem with Apple TV” between 10:29 and 11.38 p.m.), as well as on Apple Music and Apple Arcade, which also went down at the same time. Social media reports indicated that the outage was widespread.
“The Firefox brand is getting a refresh and you get the first look,” says a new web page at Firefox.com. “Kit’s our new mascot and your new companion through an internet that’s private, open and actually yours.”
Slashdot reader BrianFagioli believes the new mascot “is meant to communicate that message in a warmer, more relatable way.”
And Firefox is already selling shirts with Kit over the pocket (as well as stickers)…
For more than a decade, the nonprofit Common Crawl “has been scraping billions of webpages to build a massive archive of the internet,” notes the Atlantic, making it freely available for research.
“In recent years, however, this archive has been put to a controversial purpose: AI companies including OpenAI, Google, Anthropic, Nvidia, Meta, and Amazon have used it to train large language models.
“In the process, my reporting has found, Common Crawl has opened a back door for AI companies to train their models with paywalled articles from major news websites. And the foundation appears to be lying to publishers about this — as well as masking the actual contents of its archives…”
Common Crawl’s website states that it scrapes the internet for “freely available content” without “going behind any ‘paywalls.'” Yet the organization has taken articles from major news websites that people normally have to pay for — allowing AI companies to train their LLMs on high-quality journalism for free. Meanwhile, Common Crawl’s executive director, Rich Skrenta, has publicly made the case that AI models should be able to access anything on the internet. “The robots are people too,” he told me, and should therefore be allowed to “read the books” for free. Multiple news publishers have requested that Common Crawl remove their articles to prevent exactly this use. Common Crawl says it complies with these requests. But my research shows that it does not.
I’ve discovered that pages downloaded by Common Crawl have appeared in the training data of thousands of AI models. As Stefan Baack, a researcher formerly at Mozilla, has written, “Generative AI in its current form would probably not be possible without Common Crawl.” In 2020, OpenAI used Common Crawl’s archives to train GPT-3. OpenAI claimed that the program could generate “news articles which human evaluators have difficulty distinguishing from articles written by humans,” and in 2022, an iteration on that model, GPT-3.5, became the basis for ChatGPT, kicking off the ongoing generative-AI boom. Many different AI companies are now using publishers’ articles to train models that summarize and paraphrase the news, and are deploying those models in ways that steal readers from writers and publishers.
Common Crawl maintains that it is doing nothing wrong. I spoke with Skrenta twice while reporting this story. During the second conversation, I asked him about the foundation archiving news articles even after publishers have asked it to stop. Skrenta told me that these publishers are making a mistake by excluding themselves from “Search 2.0” — referring to the generative-AI products now widely being used to find information online — and said that, anyway, it is the publishers that made their work available in the first place. “You shouldn’t have put your content on the internet if you didn’t want it to be on the internet,” he said. Common Crawl doesn’t log in to the websites it scrapes, but its scraper is immune to some of the paywall mechanisms used by news publishers. For example, on many news websites, you can briefly see the full text of any article before your web browser executes the paywall code that checks whether you’re a subscriber and hides the content if you’re not. Common Crawl’s scraper never executes that code, so it gets the full articles.
Thus, by my estimate, the foundation’s archives contain millions of articles from news organizations around the world, including The Economist, the Los Angeles Times, The Wall Street Journal, The New York Times, The New Yorker, Harper’s, and The Atlantic…. A search for nytimes.com in any crawl from 2013 through 2022 shows a “no captures” result, when in fact there are articles from NYTimes.com in most of these crawls.
“In the past year, Common Crawl’s CCBot has become the scraper most widely blocked by the top 1,000 websites,” the article points out…
A CRISPR-based drug given to study participants by infusion is raising hopes for a much easier way to lower cholesterol, reports CNN:
With a snip of a gene, doctors may one day permanently lower dangerously high cholesterol, possibly removing the need for medication, according to a new pilot study published Saturday in the New England Journal of Medicine.
The study was extremely small — only 15 patients with severe disease — and was meant to test the safety of a new medication delivered by CRISPR-Cas9, a biological sort of scissor which cuts a targeted gene to modify or turn it on or off. Preliminary results, however, showed nearly a 50% reduction in low-density lipoprotein, or LDL, the “bad” cholesterol which plays a major role in heart disease — the No.1 killer of adults in the United States and worldwide. The study, which will be presented Saturday at the American Heart Association Scientific Sessions in New Orleans, also found an average 55% reduction in triglycerides, a different type of fat in the blood that is also linked to an increased risk of cardiovascular disease.
“We hope this is a permanent solution, where younger people with severe disease can undergo a ‘one and done’ gene therapy and have reduced LDL and triglycerides for the rest of their lives,” said senior study author Dr. Steven Nissen, chief academic officer of the Sydell and Arnold Miller Family Heart, Vascular & Thoracic Institute at Cleveland Clinic in Ohio…. Today, cardiologists want people with existing heart disease or those born with a predisposition for hard-to-control cholesterol to lower their LDL well below 100, which is the average in the US, said Dr. Pradeep Natarajan, director of preventive cardiology at Massachusetts General Hospital and associate professor of medicine at Harvard Medical School in Boston…
People with a nonfunctioning ANGPTL3 gene — which Natarajan says applies to about 1 in 250 people in the US — have lifelong levels of low LDL cholesterol and triglycerides without any apparent negative consequences. They also have exceedingly low or no risk for cardiovascular disease. “It’s a naturally occurring mutation that’s protective against cardiovascular disease,” said Nissen, who holds the Lewis and Patricia Dickey Chair in Cardiovascular Medicine at Cleveland Clinic. “And now that CRISPR is here, we have the ability to change other people’s genes so they too can have this protection.”
“Phase 2 clinical trials will begin soon, quickly followed by Phase 3 trials, which are designed to show the effect of the drug on a larger population, Nissen said.”
And CNN quotes Nissen as saying “We hope to do all this by the end of next year. We’re moving very fast because this is a huge unmet medical need — millions of people have these disorders and many of them are not on treatment or have stopped treatment for whatever reason.”
A former Business Analyst reportedly filed a class action lawsuit claiming that for years, hundreds of remote employees at Bank of America first had to boot up complex computer systems before their paid work began, reports Human Resources Director magazine:
Tava Martin, who worked both remotely and at the company’s Jacksonville facility, says the financial institution required her and fellow hourly workers to log into multiple security systems, download spreadsheets, and connect to virtual private networks — all before the clock started ticking on their workday. The process wasn’t quick. According to the filing in the United States District Court for the Western District of North Carolina, employees needed 15 to 30 minutes each morning just to get their systems running. When technical problems occurred, it took even longer…
Workers turned on their computers, waited for Windows to load, grabbed their cell phones to request a security token for the company’s VPN, waited for that token to arrive, logged into the network, opened required web applications with separate passwords, and downloaded the Excel files they needed for the day. Only then could they start taking calls from business customers about regulatory reporting requirements…
The unpaid work didn’t stop at startup. During unpaid lunch breaks, many systems would automatically disconnect or otherwise lose connection, forcing employees to repeat portions of the login process — approximately three to five minutes of uncompensated time on most days, sometimes longer when a complete reboot was required. After shifts ended, workers had to log out of all programs and shut down their computers securely, adding another two to three minutes.
Thanks to Slashdot reader Joe_Dragon for sharing the article.
Blue Origin stands ready to help NASA achieve its goals with regard to landing humans on the Moon as soon as possible, the company’s chief executive said Saturday in an interview with Ars.
“We just want to help the US get to the Moon,” said Dave Limp, CEO of the space company founded by Jeff Bezos. “If NASA wants to go quicker, we would move heaven and Earth, pun intended, to try to get to the Moon sooner. And I think we have some good ideas.”
Limp spoke on Saturday, about 24 hours ahead of the company’s second launch of the large New Glenn rocket. Carrying the ESCAPADE spacecraft for NASA, the mission has a launch window that opens at 2:45 pm ET (19:45 UTC) at Cape Canaveral Space Force Station in Florida, and runs for a little more than two hours.
The Associated Press reports that “For the past decade, Dr. Priscilla Chan and her husband Mark Zuckerberg have focused part of their philanthropy on a lofty goal — ‘to cure, prevent or manage all disease’ — if not in their lifetime, then in their children’s.”
During that decade they also funded other initiatives (including underprivileged schools and immigration reform), according to the article. But there’s a change coming:
Now, the billionaire couple is shifting the bulk of their philanthropic resources to Biohub, the pair’s science organization, and focusing on using artificial intelligence to accelerate scientific discovery. The idea is to develop virtual, AI-based cell models to understand how they work in the human body, study inflammation and use AI to “harness the immune system” for disease detection, prevention and treatment. “I feel like the science work that we’ve done, the Biohub model in particular, has been the most impactful thing that we have done. So we want to really double down on that. Biohub is going to be the main focus of our philanthropy going forward,” Zuckerberg said Wednesday evening at an event at the Biohub Imaging Institute in Redwood City, California…. Chan and Zuckerberg have pledged 99% of their lifetime wealth — from shares of Meta Platforms, where Zuckerberg is CEO — toward these efforts…
On Thursday, Chan and Zuckerberg also announced that Biohub has hired the team at EvolutionaryScale, an AI research lab that has created large-scale AI systems for the life sciences…
Biohub’s ambition for the next years and decades is to create virtual cell systems that would not have been possible without recent advances in AI. Similar to how large language models learn from vast databases of digital books, online writings and other media, its researchers and scientists are working toward building virtual systems that serve as digital representations of human physiology on all levels, such as molecular, cellular or genome. As it is open source — free and publicly available — scientists can then conduct virtual experiments on a scale not possible in physical laboratories.
“We will continue the model we’ve pioneered of bringing together scientists and engineers in our own state-of-the-art labs to build tools that advance the field,” according to Thursday’s blog post. “We’ll then use those tools to generate new data sets for training new biological AI models to create virtual cells and immune systems and engineer our cells to detect and treat disease….
“We have also established the first large-scale GPU cluster for biological research, as well as the largest datasets around human cell types. This collection of resources does not exist anywhere else.”
Store pages on Steam are looking a lot less cramped thanks to a new update. Pages have been made wider, with support for higher resolution images and new viewing modes for trailers and screenshots. You’ll notice changes in the top carousel and in the “About the Game” section, where some new formatting options should make things look a bit more organized. The update just rolled out to the public after first being tested among beta users.
With this update, pages have been widened to 1200 pixels, which Valve says “felt like a good balance where we can show more content on screen without overwhelming the page and making it hard to navigate.” There’s now the option of a large pop-up view called theater mode in the carousel, as well as full-screen mode. In addition to games’ store pages, Valve has slightly tweaked the appearance of search results and recommendation pages to be wider, and made store hubs, Steam Charts and the News Hub look more uniform.
You may also notice some more colorful backgrounds on games’ store pages and in bundle detail pages. Where you won’t see changes yet, though, is the homepage. While Valve says it’s working on “similar adjustments” for the homepage, those aren’t rolling out with this update.
This article originally appeared on Engadget at https://www.engadget.com/gaming/pc/steam-store-pages-get-a-mini-makeover-to-better-suit-wide-screens-200142506.html?src=rss
Long-time Slashdot reader AmiMoJo shared this report from Marine Insight:
The world’s largest cargo sailboat, Neoliner Origin, completed its first transatlantic voyage on 30 October despite damage to one of its sails during the journey. The 136-metre-long vessel had to rely partly on its auxiliary motor and its remaining sail after the aft sail was damaged in a storm shortly after departure… Neoline, the company behind the project, said the damage reduced the vessel’s ability to perform fully on wind power…
The Neoliner Origin is designed to reduce greenhouse gas emissions by 80 to 90 percent compared to conventional diesel-powered cargo ships. According to the United Nations Conference on Trade and Development (UNCTAD), global shipping produces about 3 percent of worldwide greenhouse gas emissions…
The ship can carry up to 5,300 tonnes of cargo, including containers, vehicles, machinery, and specialised goods. It arrived in Baltimore carrying Renault vehicles, French liqueurs, machinery, and other products. The Neoliner Origin is scheduled to make monthly voyages between Europe and North America, maintaining a commercial cruising speed of around 11 knots.
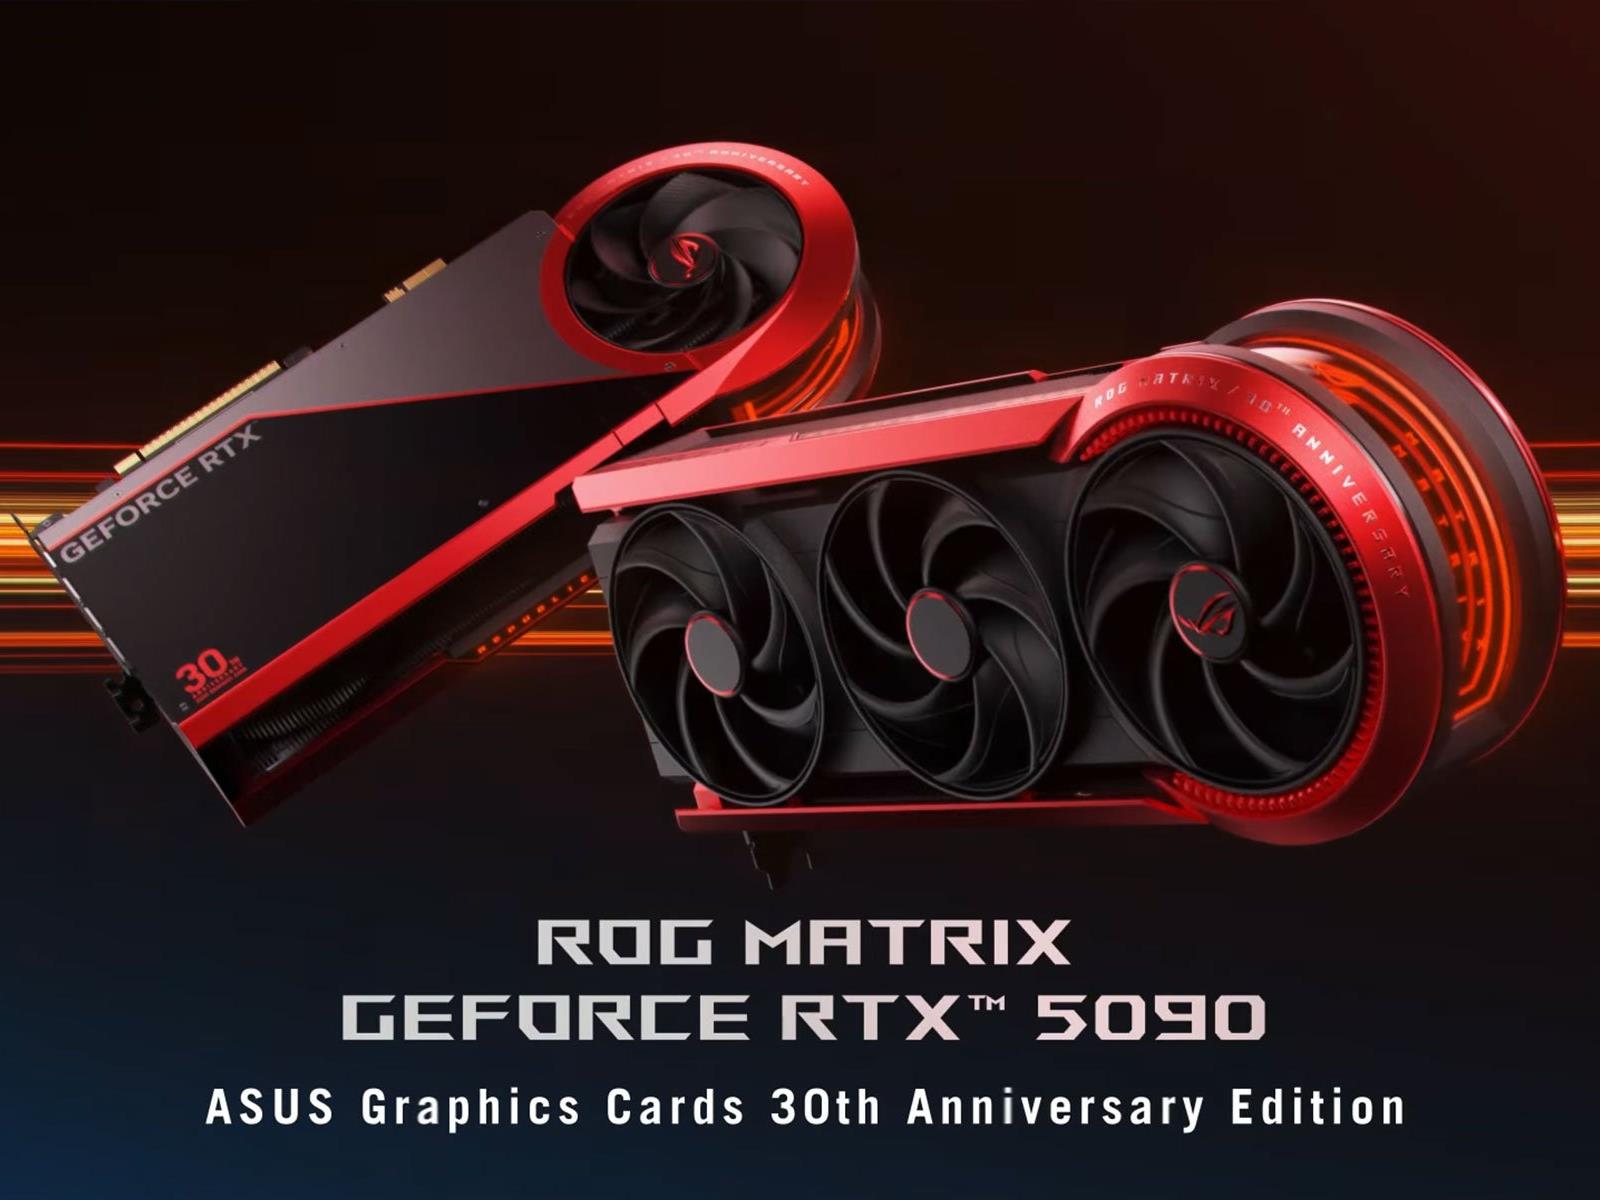
Have you seen the ASUS ROG Matrix GeForce RTX 5090 card? Yes you have; it’s right above this text. The new high-end graphics card from the halo-tier Matrix series has a striking design that we’d assume was a Radeon GPU if not for the obvious GEFORCE RTX branding on the backplate. This is a 30th Anniversary edition of the company’s graphics
Just days before Rockstar Games announced another delay of Grand Theft Auto VI, the company also fired between 30 and 40 employees—and according to claims made by a current Rockstar developer (verified by GTAForums moderators as well as The Independent Workers’ Union of Great Britain), this was an act of union busting. While some rumors suggest
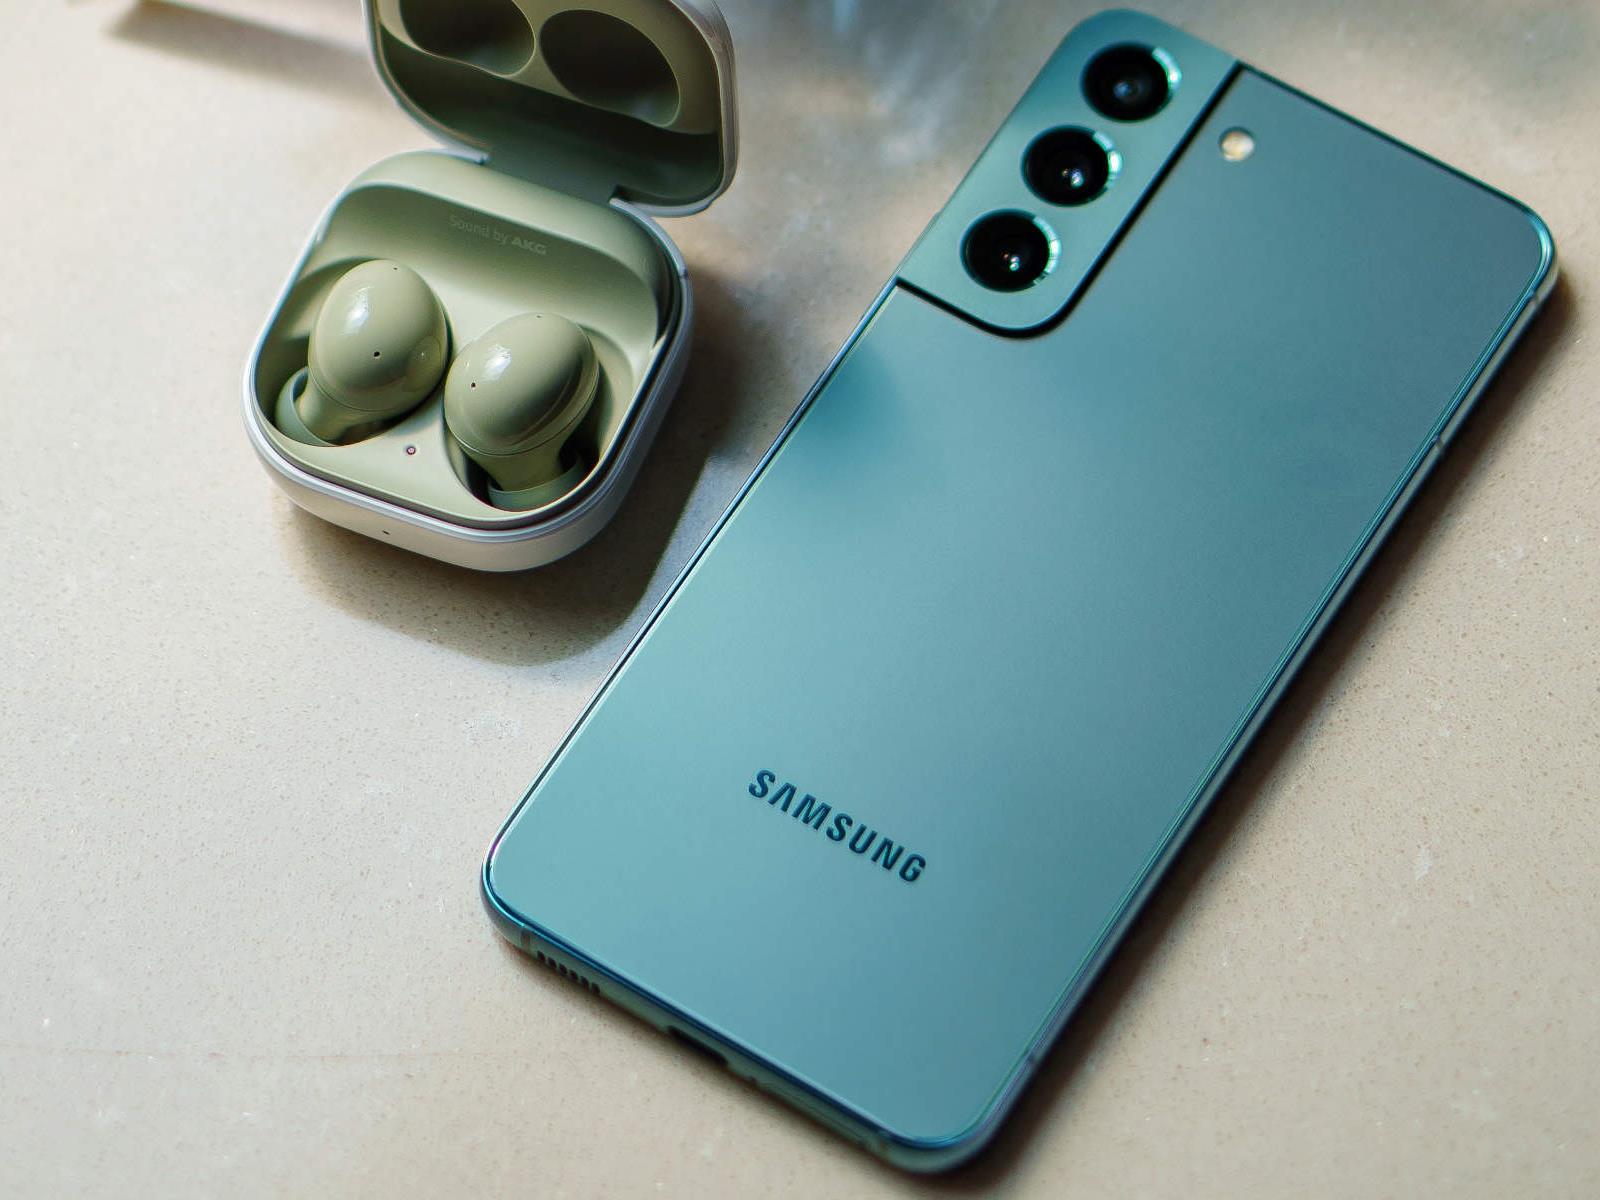
Samsung Galaxy phones have been targeted by Android spyware dubbed Landfall, and for nearly a year, the attack went unpatched, running rampant throughout the Middle East. Unit 42 has recently released an in-depth report on the spyware and how it works, showcasing how a weakness in Samsung’s image processing library allowed for Landfall to
Long-time Slashdot reader AmiMoJo shared this report from Linuxiac:
The Japanese branch of Mozilla’s Support Mozilla (SUMO) community — responsible for localizing and maintaining Japanese-language support documentation for Firefox and other Mozilla products (consisting of Japanese native speakers) — has officially disbanded after more than two decades of voluntary work…
SUMO, short for Support Mozilla, is the umbrella project for Mozilla’s user support platform, support.mozilla.org, that brings together volunteers and contributors worldwide who translate, maintain, and update documentation, tutorials, and troubleshooting guides for Firefox, Thunderbird, and other Mozilla products… According to marsf, the long-time locale leader of the Japanese SUMO team, the decision to disband was triggered by the recent introduction of an automated translation system known as Sumobot. Deployed on October 22, the bot began editing and approving Japanese Knowledge Base articles without community oversight.
The article notes marsf’s complaints in a post to the SUMO discussion forum, including the fact that the new automated system automatically approved machine-translated content with only a 72-hour window for human review. As a result, more than 300 Knowledge Base articles were overwritten on the production server, which marsf called “mass destruction of our work.”
American multinational freight company UPS “has grounded its fleet of MD-11 aircraft,” reports the Guardian, “days after a cargo plane crash that killed at least 13 people in Kentucky. The grounded MD-11s are the same type of plane involved in Tuesday’s crash in Louisville. They were originally built by McDonnell Douglas until it was taken over by Boeing.”
More details from NBC News:
UPS said the move to temporarily ground its MD-11 fleet was made “out of an abundance of caution and in the interest of safety.” MD-11s make up 9% of the company’s air fleet, it said. “We made this decision proactively at the recommendation of the aircraft manufacturer. Nothing is more important to us than the safety of our employees and the communities we serve,” UPS spokesman Jim Mayer said… FedEx said early Saturday that it was also grounding its MD-11s. The UPS rival has 28 such planes in operation, out of a fleet of around 700, FedEx said.
Video shows that the left engine of the plane caught fire during takeoff and immediately detached, National Transportation Safety Board member Todd Inman said Wednesday. The National Transportation Safety Board is the lead agency in the investigation.
Thanks to long-time Slashdot reader echo123 for suggesting the article.
“Maybe you’ve heard that artificial intelligence is a bubble poised to burst,” writes a Washington Post technology columnist. “Maybe you have heard that it isn’t. (No one really knows either way, but that won’t stop the bros from jabbering about it constantly.)”
“But I can confidently tell you that the money being thrown around for AI is so huge that numbers have lost all meaning.”
The companies pouring money in are so rich and so power-hungry (in multiple meanings of that term) that our puny human brains cannot really comprehend. So let’s try to give some meaning and context to the stratospheric numbers in AI. Is it a bubble? Eh, who knows. But it is completely bonkers. In just the past year, the four richest companies developing AI — Microsoft, Google, Amazon and Meta — have spent roughly $360 billion combined for big-ticket projects, which included building AI data centers and stuffing them with computer chips and equipment, according to my analysis of financial disclosures…. How do companies pay for the enormous sums they are lavishing on AI? Mostly, these companies make so much money that they can afford to go bananas…
Eight of the world’s top 10 most valuable companies are AI-centric or AI-ish American corporate giants — Nvidia, Apple, Microsoft, Google, Amazon, Broadcom, Meta and Tesla. That’s according to tallies from S&P Global Market Intelligence based on the total price of the companies’ stock held by investors. My analysis of the S&P data shows that the collective worth of those eight giants, $23 trillion, is more than the value of the next 96 most valuable U.S. companies put together, which includes many still very rich names such as JPMorgan, Walmart, Visa and ExxonMobil. No. 1 on that list, the AI computer chip seller Nvidia, last week become the first company in history to reach a stock market value of $5 trillion. That alone was more than the value of entire stock markets in most countries, Bloomberg News reported, other than the five biggest (in the U.S., China, Japan, Hong Kong and India)…
All the announced or under-construction data centers for powering AI would consume roughly as much electricity as 44 million households in the United States if they run full tilt, according to a recent analysis by the Barclays investment bank as reported by the Financial Times.
For context, that’s nearly one-third of the total number of residential housing units in the entire country, according to U.S. Census Bureau housing estimates for 2024.
Retailers getting are getting an even earlier start to Black Friday this year with chunky discounts and doorbuster deals on all kinds of tech. If you missed it, check out our recent article highlighting big savings on OLED TV models, including a 65-inch Samsung OLED for a low $899.99. Now we’re turning our attention to Pixel 10 phones and
There’s a fundamental question you can ask of both the internet and real life: “How do I enjoy my time here without taking unnecessary risks?” In grass-touching meatspace, you can cut out processed foods, carry pepper spray and avoid skydiving without a partner.
But the best methods for staying safe online aren’t as intuitive. The internet is a massive town square where people are constantly bellowing deeply personal facts about themselves. It’s no surprise that it’s become a breeding ground for scams, theft and other criminal activity.
Given the breadth of dangers, it may feel easier to throw up your hands and say that whatever happens will happen. I’m here to tell you, though, that cybersecurity doesn’t have to be complex, difficult or time-consuming. You don’t need to be a hacker to foil a hacker — you only have to take advantage of simple tips and free apps designed to make you safer online. Whether you commit to all 12 detailed here or only focus on one, you’ll be much more secure for it.
1. Install security updates immediately
One of the most important things you can do to ensure your digital security is to install all software updates as soon as they become available on your devices. When you see the notification, don’t wait — train yourself to download the update immediately.
Not all software updates are about security, but the ones that are form your best line of defense against technical hacks. When developers discover a flaw that can be exploited, they ship an update to fix it. By the time the flaw gets patched, chances are very high that hackers also know about it, so any time lost means you could be the next to get exploited.
As you go down this list, you’ll learn that cybersecurity threats are less technical than you think. To counter the ones that are, however, there’s nothing more important you can do than install security updates.
2. Use strong passwords
Weak, easily guessed passwords are one of the most frequent causes of data breaches and malware attacks. If a password is one of the ten or so most common, an attacker may be able to guess it with no other information. If it’s connected to you — your birthday, say, or mother’s maiden name — it may be guessable from information anyone can look up online.
Even if your password is a random string of characters, it might still be guessable if it’s too short. Hackers can use programs to guess all possible combinations and try each one on a target account. The longer a password is, the more exponentially difficult it is to guess.
SEAN GLADWELL via Getty Images
That means you need passwords that are both long and meaningless to you. You might rightly complain that these are bastards to remember, but you’re in luck: password managers can do that for you. A password manager app or browser extension can create passwords when you need them, store them securely and fill them in automatically. All you have to remember is the one master password that unlocks all the others.
3. Set up two-factor authentication
Even the strongest password might get revealed through no fault of your own, like if it’s stored without encryption and leaked in a data breach. That’s why it helps to have two-factor authentication (2FA), also known as multi-factor authentication (MFA), as a second secure layer on every account.
You probably already know 2FA as the irritating extra step that makes you go get your phone — but that’s not the only way to do it. Many apps, including Google and Apple, now let you log in through passkeys. These not only don’t require you to enter a code or password, but use asymmetric encryption, sharing credentials between your device and the service that runs the passkeys. It’s a lot quicker for you, and leaves nothing to steal.
4. Back everything up
Ransomware and its cousins are a growth industry within the cybercrime economy. These attacks corrupt your files or lock you out of them until you pay a fee to get them back. The easiest way to foil a ransomware attack, or to clear any other kind of malware off a device, is to restore the entire system from the most recent backup.
To make sure you actually have a backup, experts recommend the 3-2-1 rule: three different backups, on two different types of storage, with at least one physically distant from the main system. For example, you could have one backup on another device in your house, one in the cloud and one on a portable hard drive. Automatic backup services can save disk images for you at set intervals so you don’t have to remember to do it yourself.
5. Learn to spot social engineering
Despite all the technobabble flying around the cybersecurity world, a great many scams and hacks are accomplished through methods a 19th-century con artist would recognize. Scammers pose as experts or authority figures to gain your trust, and use frightening language to bypass your critical thinking. Ticking clocks, emotional manipulation and fake identities are all in the toolbox.
Alex Cristi via Getty Images
Take phishing, in which hackers trick you into giving up your information willingly. A typical phishing email might pose as a bank, credit bureau or other authoritative service. In red letters, it may demand your bank password or social security number to immediately fix an irregularity with your account. Other common approaches include warning you about speeding tickets you never incurred or sending receipts for subscriptions you never bought.
Social engineering attacks are constantly evolving, but they often fall back on the same strategies. The best way to foil them is to take a deep breath every time you receive a frightening email or text message, then research it in detail: look up the email address, check the visual design to make sure the sender is who they claim to be, and ask yourself if there’s any way the message could be true. I highly recommend working through this phishing quiz — it’s tough, but fair, and extremely educational.
6. Always check links before clicking
This is a companion to the previous tip. Social engineering scams don’t always try to get you to give up information yourself. They also get you to click on links that put secret malware on your device — like keyloggers that watch you type your passwords or ransomware programs that corrupt your files.
If you’re ever not sure about an email attachment or a link you’re being asked to click, copy the link (without opening it) and paste it into a URL checker like this one from NordVPN. These free tools can tell you if a link is associated with any known malware domains.
Sam Chapman for Engadget
You can also mouse over any link, then look at the bottom-left of your browser to see what URL it will take you to. If an email is from your bank, any links within it should go to your bank’s website. If it’s going anywhere else, especially to an unidentifiable string of characters, be suspicious.
7. Don’t overshare
Over the last two decades, lots of us have gotten into the habit of dumping all sorts of personal information on social media. This trend has supercharged the scam economy. It may seem harmless to broadcast the names of your kids or the dates you’ll be on vacation, but every piece of data you put into the world makes it easier for a stranger to get hooks into you.
For example, “grandparent scams” are on the rise right now. Grifters contact a target, usually a senior, pretending to be their grandchild. They’ll claim to be in a crisis and need money fast. The more information they have on their target, the more convincing their tale of woe will be. Social media is a prime place to study a potential victim.
Oversharing can also be a compounding problem. If you use weak passwords, your public information can be used to guess your credentials or answer your security questions. So, if you don’t have a password manager yet, think twice before you engage with that quiz post on Facebook that asks for the name of your childhood pet.
8. Use a VPN
I’m a big booster of virtual private networks (VPNs), but it’s important to be realistic about what they can and can’t do. Even the best VPNs aren’t total cybersecurity solutions — you can’t just set one and assume you’re safe forever. A VPN can’t protect you if you use easily guessed passwords, for example, or click on a malware link. It’s about hiding your identity, not making you invulnerable.
So what can a VPN do? In short, it replaces your IP address (a fingerprint that identifies you online) with another IP address, belonging to a server owned by the VPN. The VPN server does business with the internet on your behalf, while its conversations with your device are encrypted so it can’t be traced back to you.
Sam Chapman for Engadget
This means no third party can connect your online actions with your real-world identity. Nobody will be harvesting data on the websites you visit to sell to advertisers, nor building a file on you that an unscrupulous government might misuse. VPNs also protect you from fake public Wi-Fi networks set up by cybercriminals — even if a hacker tricks you with a man-in-the-middle attack, they can’t do much without your real IP address.
Many top VPNs, including my top pick Proton VPN, include ad blockers that can also keep cookies and tracking pixels from latching onto you. So, even if a VPN can’t do everything, you’ll be far safer and more private with one than without one. If you don’t want to pay for a new subscription right now, I’ve also compiled a list of the best free VPNs that are actually safe to use.
9. Run regular virus scans
The most important time to look for malware is when you’re downloading a file from the internet. Not only can unwanted apps hitch rides on seemingly safe files, but links can start downloads in secret, even if you don’t think they’re meant to be downloading anything. A solid antivirus program can catch malware as it arrives on your system, and if it’s uncertain, can lock suspicious files in quarantine until it knows whether they’re safe or not.
Dedicated antivirus apps are sometimes even capable of catching malware that hasn’t been seen or used yet. AV software uses machine learning to identify the common patterns of malware, filtering out new viruses that behave like old ones.
But what about malware that’s already gotten through the perimeter? An antivirus app can also check your computer at set intervals in search of unwanted apps, including those that might be masquerading as system files. Windows computers now come pre-installed with Windows Defender, which is enough to handle most of these tasks, but I recommend at least one anti-malware program on any device.
10. Use email maskers and private search engines
If you’re concerned about your information being misused or mishandled, remember that the less you put out into the world, the less danger you’re in. Keeping your private data off social media is one important step, but there are other ways your data gets disseminated — and other options for responding.
For example, you often need an email address to sign up for an online account. If you use your real email, your contact information is now floating around online, increasing the chance of someone using it to scam you (or at least adding you to mailing lists you never signed up for). To stay safe, use an email masker. These services give you a fake email address you can use to create accounts, which automatically forwards messages to your real address.
Sam Chapman for Engadget
Search engines, especially Google, are also notorious for building profiles on users by watching the terms they search for. You can dodge that by switching to a private search engine like DuckDuckGo, which doesn’t track anything you do — it’s funded by non-targeted ad sales on its search results pages, not by selling your data to brokers.
11. Use a data removal service
Speaking of data brokers: unfortunately, if you’ve been on the internet at any point in the last 10 years without taking intense precautions, your data is probably in the hands of at least one business that makes money by hoarding and selling it. These data brokers range from public-facing, people-search sites to private backend dealers.
Data brokers are poorly regulated and lax about safety. The longer one has your personal information, the more likely it is to leak. The good news is that most brokers (though not all of them) are legally required to delete your data if you ask them to.
However, there are a lot of data brokers out there, and they really want to keep your data. Each one makes opting out harder than uninstalling a Norton product — and hundreds of them may have files on you. To make the process easier, you can use a data removal service like DeleteMe or Surfshark VPN’s partner service Incogni.
12. Practice physical security
Let’s close out the list by getting a little old school. I’ve already discussed how many online scams depend on classic con artistry to work. By the same token, physical infiltration and smash-and-grab tactics still pose a threat to cybersecurity.
It doesn’t take too much imagination to see how this could work. If you leave your laptop or phone unattended in public, for example, someone might insert a flash drive that loads malware onto the system. In one illustrative case, a thief in the Minneapolis area would loiter in bars, watch people unlock their phones, then steal those phones and unlock them himself.
I’m not saying you need to be paranoid every second you’re in public. Just use the same level of caution you’d use to protect your car. Lock your phone with a biometric key so only you can open it, and make sure not to leave any device lying around if it can access your online accounts. And at work, be careful not to let anyone into a secure area if they don’t have the proper credentials.
This article originally appeared on Engadget at https://www.engadget.com/cybersecurity/12-steps-you-can-take-right-now-to-be-safer-online-130008335.html?src=rss
The next major update for Halo Infinitewill also be its last. Halo Studios, which is part of Microsoft’s Xbox Game Studios, has announced that it’s rolling out Operation: Infinite on November 18. It’s going to be the last major update for the first-person shooter, because the whole team will now be focusing on the “multiple Halo titles” under development.
Xbox previously announced that it’s releasingHalo: Campaign Evolved, a remake of the first game in the franchise, Halo: Combat Evolved, sometime in 2026. It will be available for the Xbox, PC and PS5. According to unverified reports, Halo Studios is also working on a new multiplayer live service project similar to Fortnite.
Operation: Infinite will double the earning rate for Career Rank and Spartan Points. The final free Operation Pass will have no expiration date and will unlock three new armor sets. Upgrading to the 100-tier Premium Pass will give players the chance to unlock “five more unique armor sets, six weapon models and over 30 exclusive Spartan customizations.” The last major update will also add a new asymmetrical map for select Ranked modes.
While Operation: Infinite is the game’s last major update, Halo Infinite will still have a rotating selection of daily and weekly challenges, as well as a new slate of Ranked Seasons for those who want to keep playing it.
This article originally appeared on Engadget at https://www.engadget.com/gaming/halo-infinite-will-get-its-last-major-content-update-on-november-18-130000955.html?src=rss
Nothing brings people together in uncertain times quite like food. Get to talking and laughing and reminiscing over a meal, and suddenly things don’t seem so bleak anymore, even if only temporarily. A Pizza Delivery is all about rediscovering the spark through these little moments of human connection — just strangers bonding over a slice of pizza, and regaining a bit of hope in the process. It’s wistful and heartfelt in a kind of vague, nonspecific way, with some beautiful scenery and an atmospheric soundtrack to really hammer home the vibes.
Still, while A Pizza Delivery feels close to achieving its goals, it could use more polishing to fully get there. It’s not a bad way to spend a couple of hours on a cozy evening in, but you’ll have to look past the parts where it’s a little broken.
A Pizza Delivery begins with its main character, B, delivering a pizza to an apartment in a strange building in the middle of nowhere. Then a pay phone outside rings, and B’s boss tells her there’s just one last delivery she has to make. But, there’s a spare pizza pie in her scooter’s cargo box too, to share slices with anyone else she comes across during the journey.
The place B has found herself in is not normal reality, but “a space where people go when they are stuck in life, feeling empty and unfulfilled.” Each area seems its own wholly distinct little world: an empty city, a broken down factory that sits beneath dancing auroras, a prairie where a sole cottage stands among a smattering of sunflowers. You must explore the ins and outs of each area to help get B to her final destination and piece together her story, collecting items and solving some light puzzles to unlock whatever comes next.
What this game really has going for it is the mood. There’s a kind of Wristcutters: A Love Story feeling to the whole thing that I couldn’t help but latch onto. The offbeat, crestfallen characters you encounter each have their own sad story to tell, but after a bit of conversation and a slice of pizza, they’re off to (hopefully) make a fresh start and reclaim their lives. The general sense is that B will have the same opportunity if she can push through and complete her mission.
And we did get there in the end, but there were some serious hiccups along the way. Controlling B’s scooter is a somewhat clunky experience, and if you make the mistake of dismounting while it’s still moving, B will end up stuck in a cursed, floating arabesque that won’t let up for an indeterminable amount of time. I found myself repeatedly trapped in this broken position when trying to switch from riding the scooter to walking. The alternative is to come to a full stop and wait out the subsequent animation, which involves B very slowly parking and engaging the kickstand.
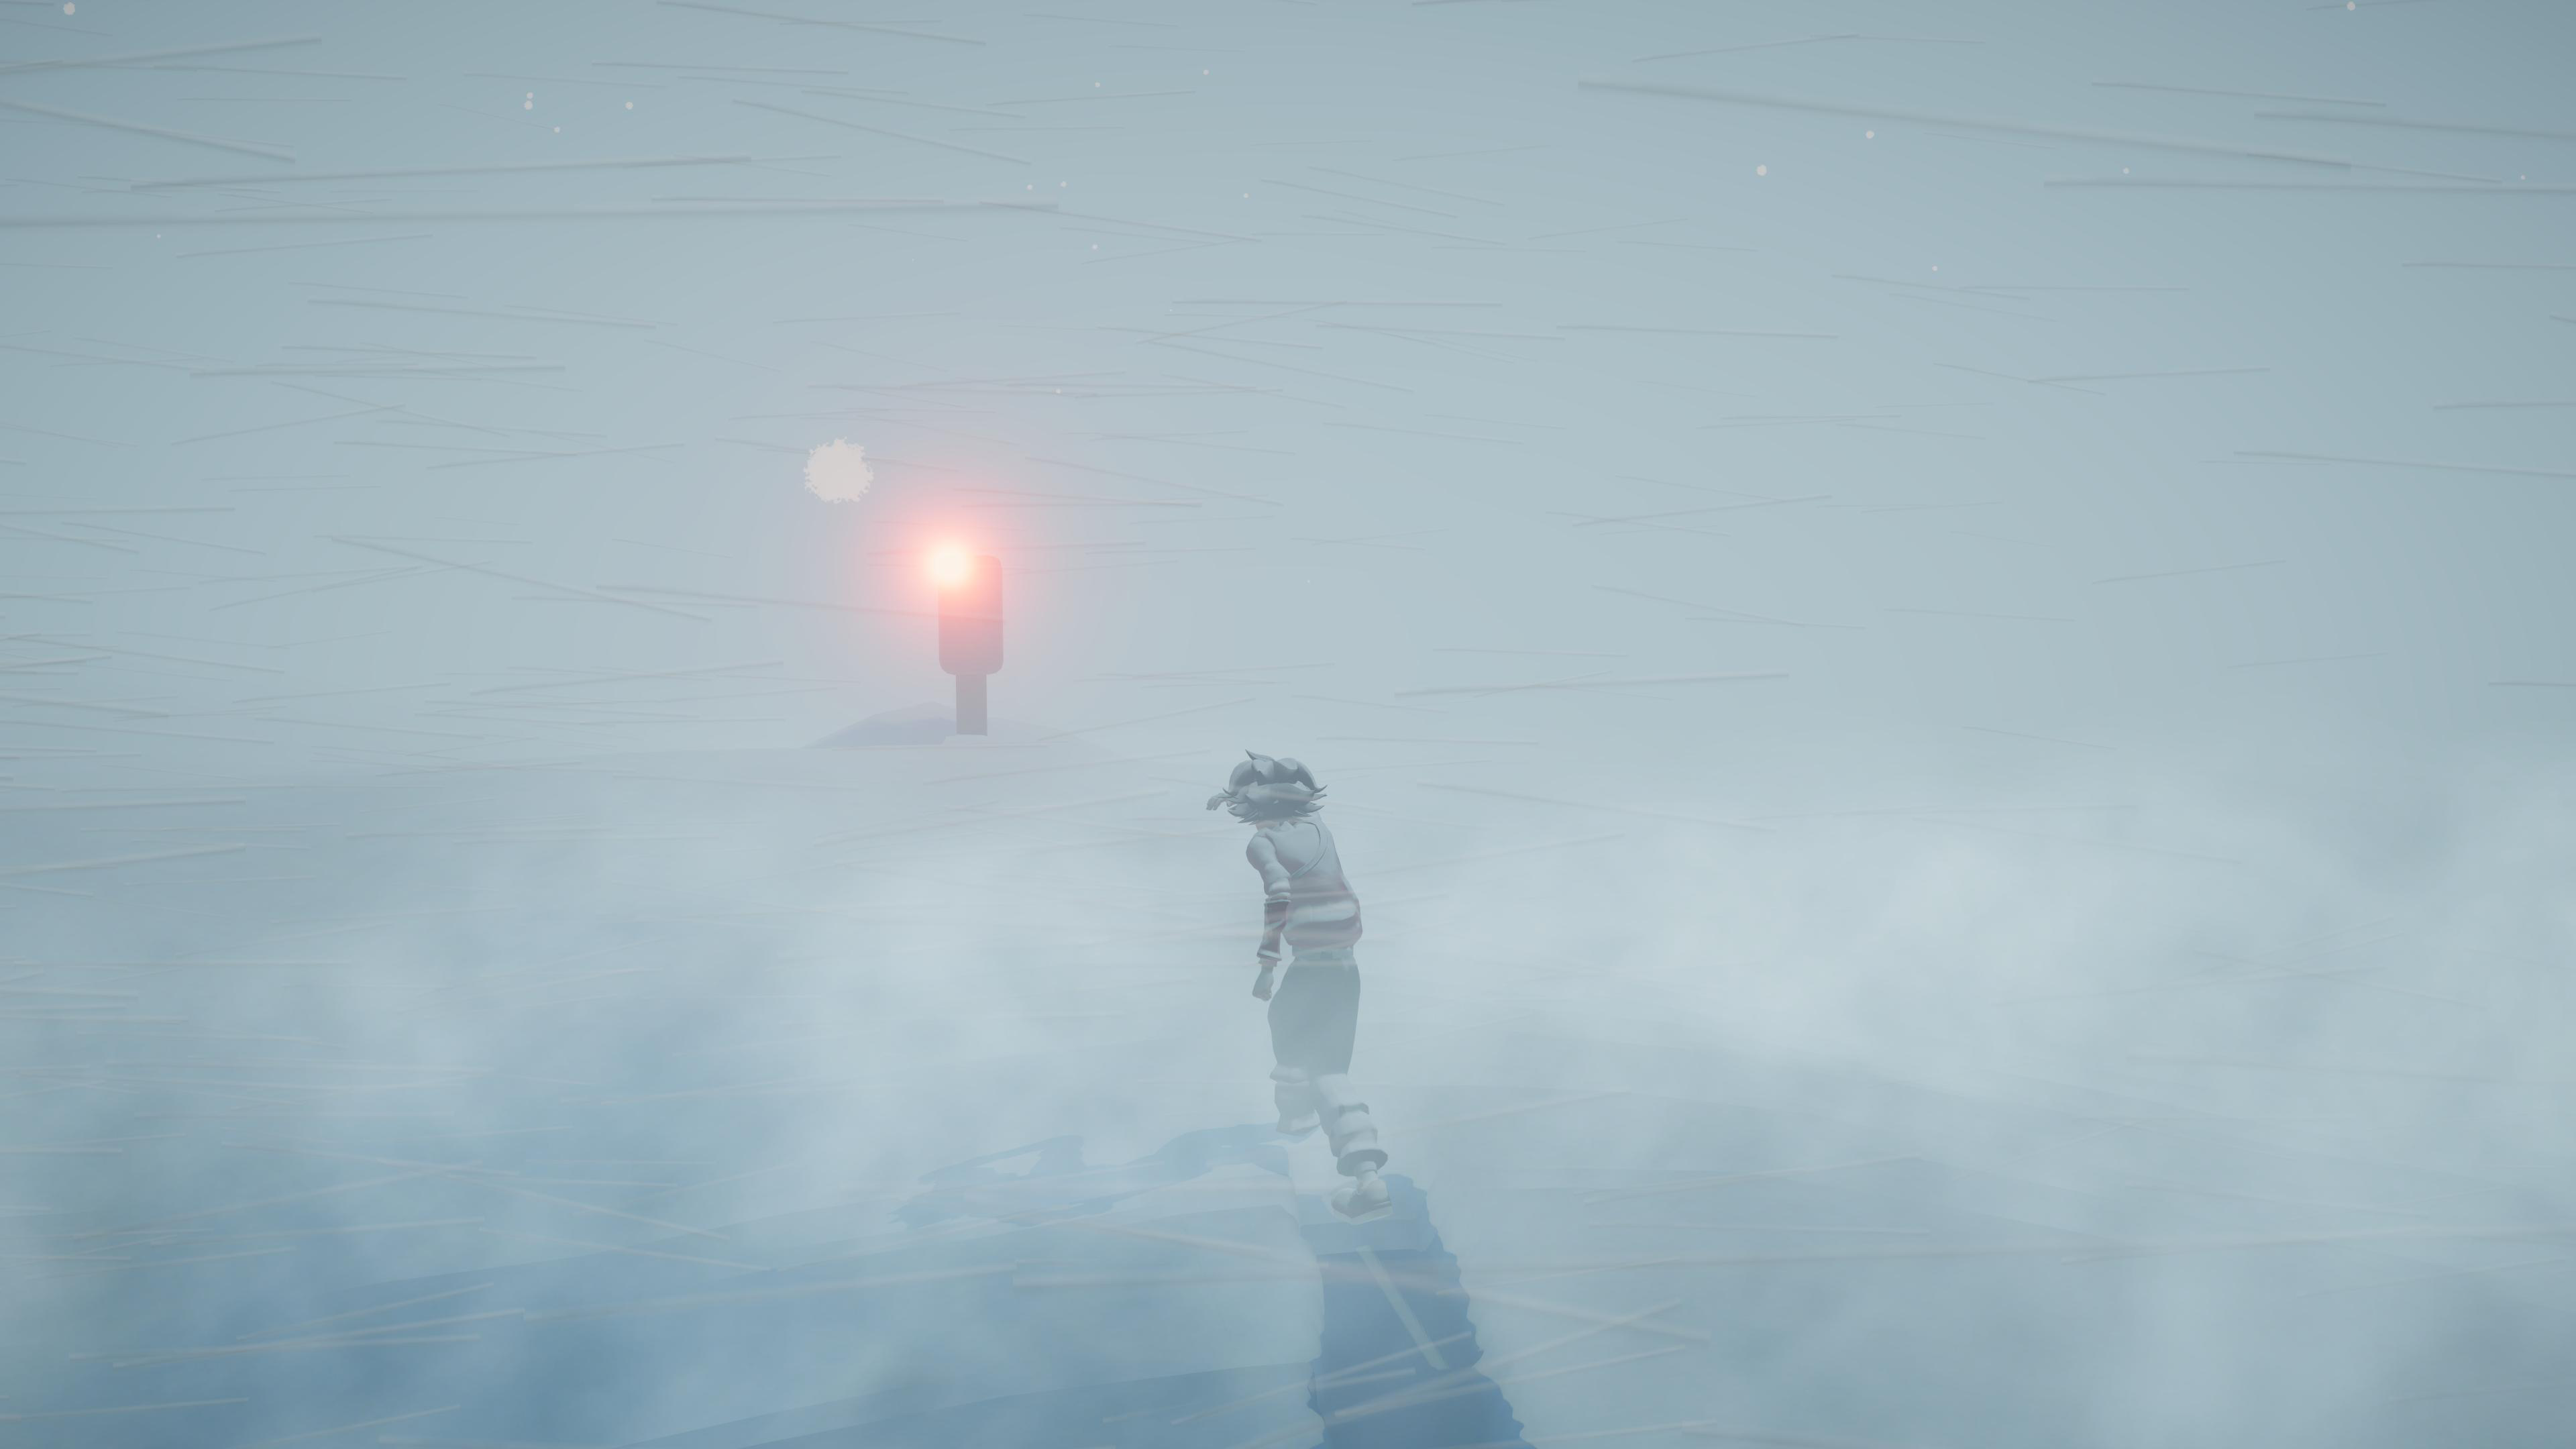
A still from A Pizza Delivery showing a blizzard scene, with the character seen trudging through low visibility toward the red light of a pay phone
Dolores Entertainment
Most of the puzzles were fairly easy to figure out, but one in which B has to trudge through a blizzard seemed to have no rhyme or reason behind it and almost made me rage-quit the game. Instead, I stepped away for a few hours and came back to it later, and only made it out after an extremely frustrating 45 minutes or so of wandering aimlessly, repeatedly going out of bounds and getting kicked back to the start of the area. Early in the game, you pick up a compass that would seem to be the solution to this puzzle, as the instructions are all direction-based. But, you can’t actually use the compass, and trying to navigate based on the way it’s oriented in your inventory doesn’t help.
B’s story didn’t entirely come together for me like I hoped either. Even after collecting all of the memory items, her background felt incomplete. I found myself wishing I knew more about her and what got her to this place once she was finally on her way to leaving it. But I don’t regret sticking it out. The ending was ultimately a touching reward and pretty darn uplifting.
A Pizza Delivery is available now for PS5, Xbox Series X/S and PC.
This article originally appeared on Engadget at https://www.engadget.com/a-pizza-delivery-is-a-dreamy-indie-adventure-that-tests-your-will-to-press-on-130000842.html?src=rss
An anonymous reader quotes a report from the New York Times: Facebook Dating, which debuted in 2019, has become a surprise hit for the company. It lets people create a dating profile free in the app, where they can swipe and match with other eligible singles. It has more than 21 million daily users, quietly making it one of the most popular online dating services. Hinge, a leading dating app in the United States, has around 15 million users. “Underlying it all is that there are real people on Facebook,” Tom Alison, the head of Facebook, said in an interview. “You can see who they are, you can see how you’re connected to them, and if you have mutual friends, we make it easy to see where you have mutual interests.”
Facebook Dating’s popularity is a sign of how Facebook has been reinventing itself. One of the early social networks, its main social feed has become less popular over time than younger apps like Instagram and TikTok. But along with Facebook Marketplace, where people look for deals on things like couches and used cars, Facebook Dating shows how an older social network can remain relevant. “When you look at Gen Z usage on Facebook, they aren’t using the social media feed,” said Mike Proulx, a research director at Forrester VP, a research firm. “What’s bringing them back to the platform is Marketplace, Messenger, Dating.”