An open source AI assistant called Moltbot (formerly “Clawdbot”) recently crossed 69,000 stars on GitHub after a month, making it one of the fastest-growing AI projects of 2026. Created by Austrian developer Peter Steinberger, the tool lets users run a personal AI assistant and control it through messaging apps they already use. While some say it feels like the AI assistant of the future, running the tool as currently designed comes with serious security risks.
Among the dozens of unofficial AI bot apps that never rise above the fray, Moltbot is perhaps most notable for its proactive communication with the user. The assistant works with WhatsApp, Telegram, Slack, Discord, Google Chat, Signal, iMessage, Microsoft Teams, and other platforms. It can reach out to users with reminders, alerts, or morning briefings based on calendar events or other triggers. The project has drawn comparisons to Jarvis, the AI assistant from the Iron Man films, for its ability to actively attempt to manage tasks across a user’s digital life.
However, we’ll tell you up front that there are plenty of drawbacks to the still-hobbyist software: While the organizing assistant code runs on a local machine, the tool effectively requires a subscription to Anthropic or OpenAI for model access (or using an API key). Users can run local AI models with the bot, but they are currently less effective at carrying out tasks than the best commercial models. Claude Opus 4.5, which is Anthropic’s flagship large language model (LLM), is a popular choice.
I’ve been using Firefox as my default browser for over two decades now, and during this time, I’ve learned a thing or two about making the most of its many features. There are some features that are turned on by default that I would recommend turning off, and some simple tweaks you can make that will greatly enhance your privacy and security. Here are all the Firefox hacks I use to make my browsing experience better, so you can try them yourself.
Make the home screen truly yours
Firefox pushes the Firefox Home screen as the default whenever you open a new tab. There’s nothing particularly wrong about that, but it does come with some unnecessary sponsored content, which you can get rid of. To do this, go to the Firefox settings, by clicking the three-lines icon in the top-right corner of an open Firefox window window and selecting Settings. Now, click the Home tab in the left pane and scroll to Firefox Home Content. Disable Support Firefox to remove sponsored content, and toss in remove Shortcuts if you prefer a cleaner look over quick links to commonly visited sites. My home screen just has Web Search enabled, which looks good with a nice wallpaper.
Use the built-in task manager
Credit: Pranay Parab
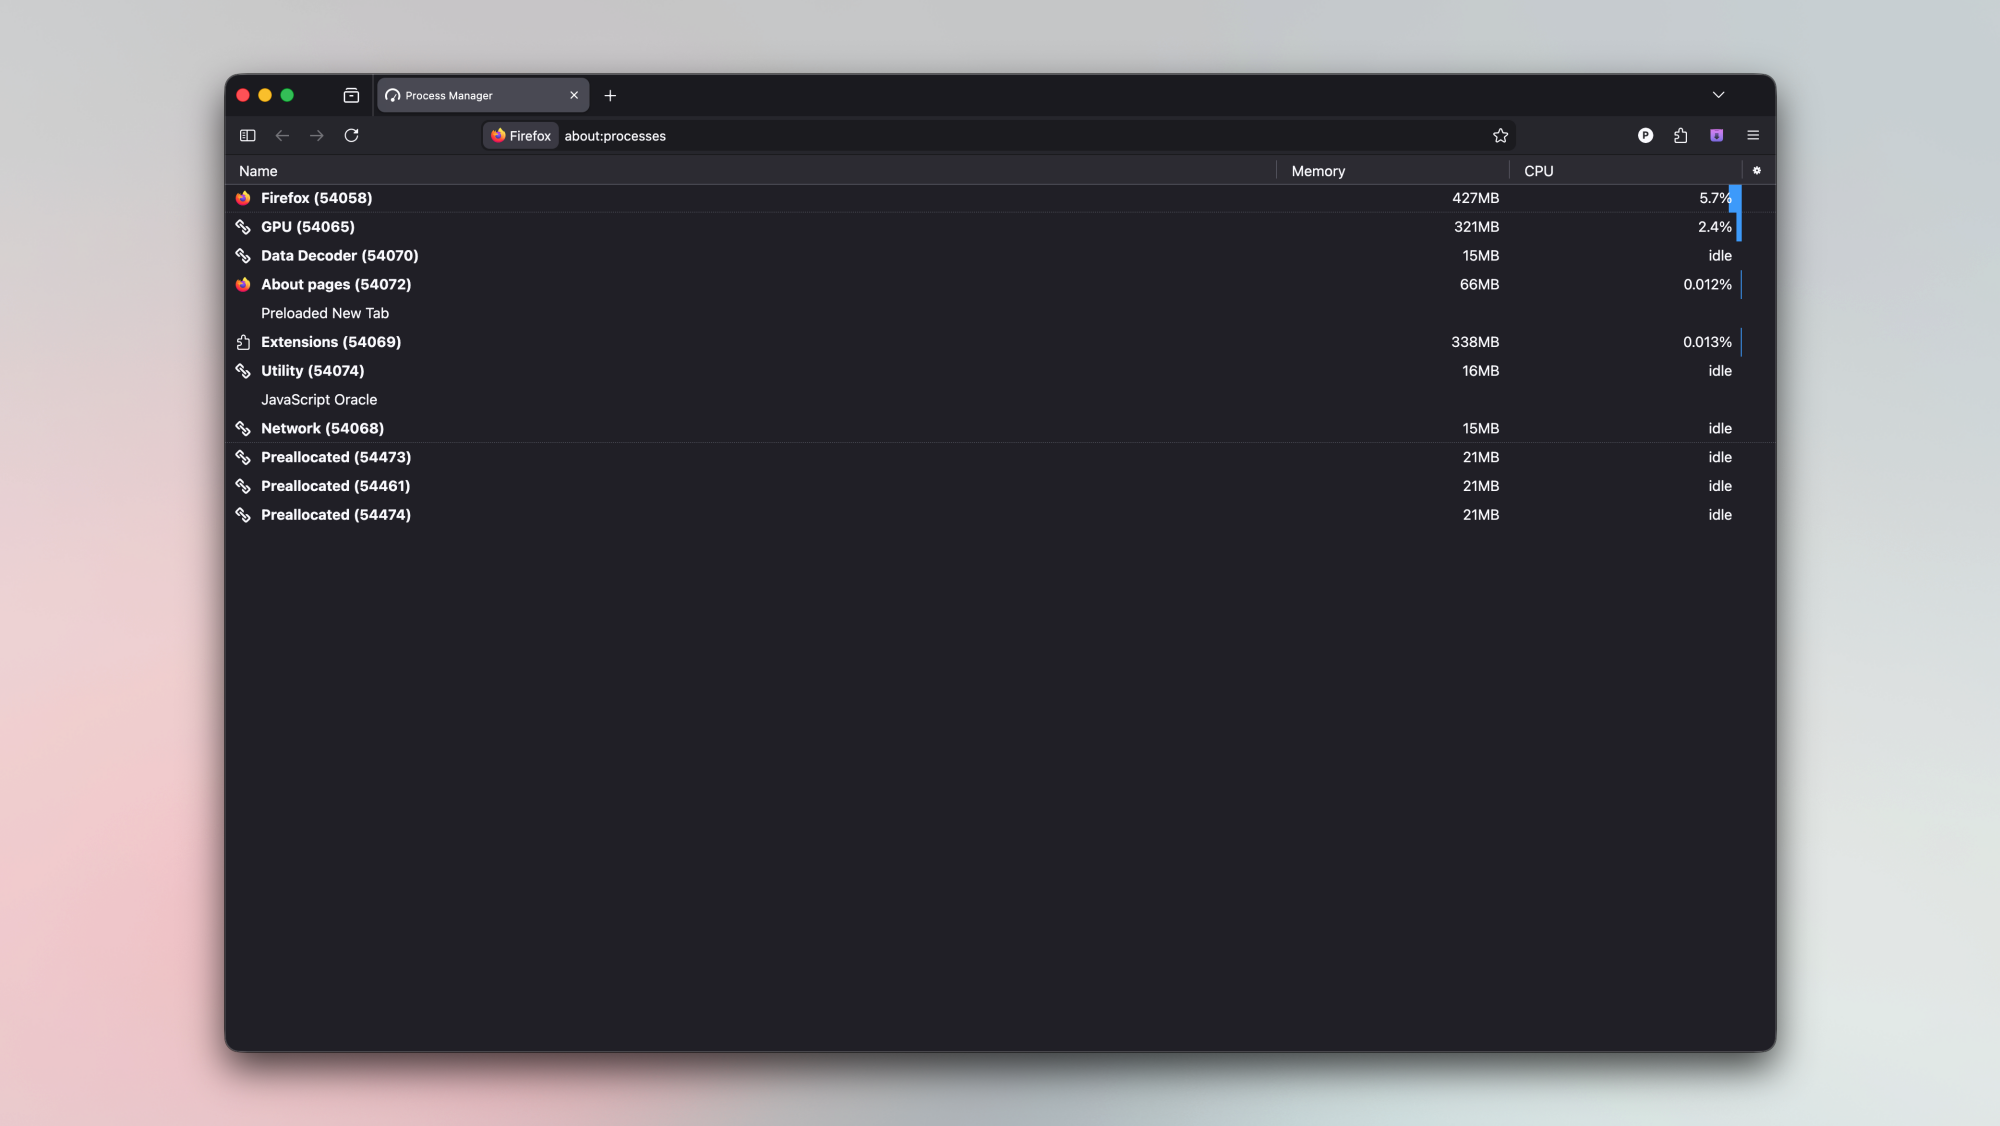
If your Firefox is being slow or unresponsive, you can use the built-in task manager to identify which tabs or extensions are causing a slowdown. This feature is also great for periodically monitoring the browser’s performance. You can access it by clicking the three-lines icon in the top-right and navigating to More tools > Task Manager. Alternatively, you can open Firefox and press Shift-Esc, or type about:processes in the address bar.
Once the task manager is open, you can use it just as you’d use the task manager on your PC or Mac. It lets you quickly close unresponsive tabs, disable all extensions in one go, and monitor RAM and CPU usage, too.
Firefox has a handy screenshot tool
You can open any webpage in Firefox and use the built-in screenshot tool to take a quick picture of the webpage you’re on. This is the fastest way to take a full-page screenshot without throwing in the rest of your screen, or to capture just a small section of a webpage. Just right-click anywhere on a webpage and select Take Screenshot. You’ll see both options (capture a selected part of the page, or the full page), and you can pick one to take a quick screenshot.
Disable unwanted AI features
Like every other app in the world, Firefox has added AI features I never asked for to the browser. One of these appears in the context menu, so you can easily remove it from there. Right-click any webpage, and in the Ask AI Chatbot section, select Remove AI Chatbot to get rid of this feature. You can also go to Firefox settings > General > Tabs and disable Use AI to suggest tabs and a name for tab groups.
Stop Firefox’s data collection (and generally protect your privacy)
Credit: Pranay Parab
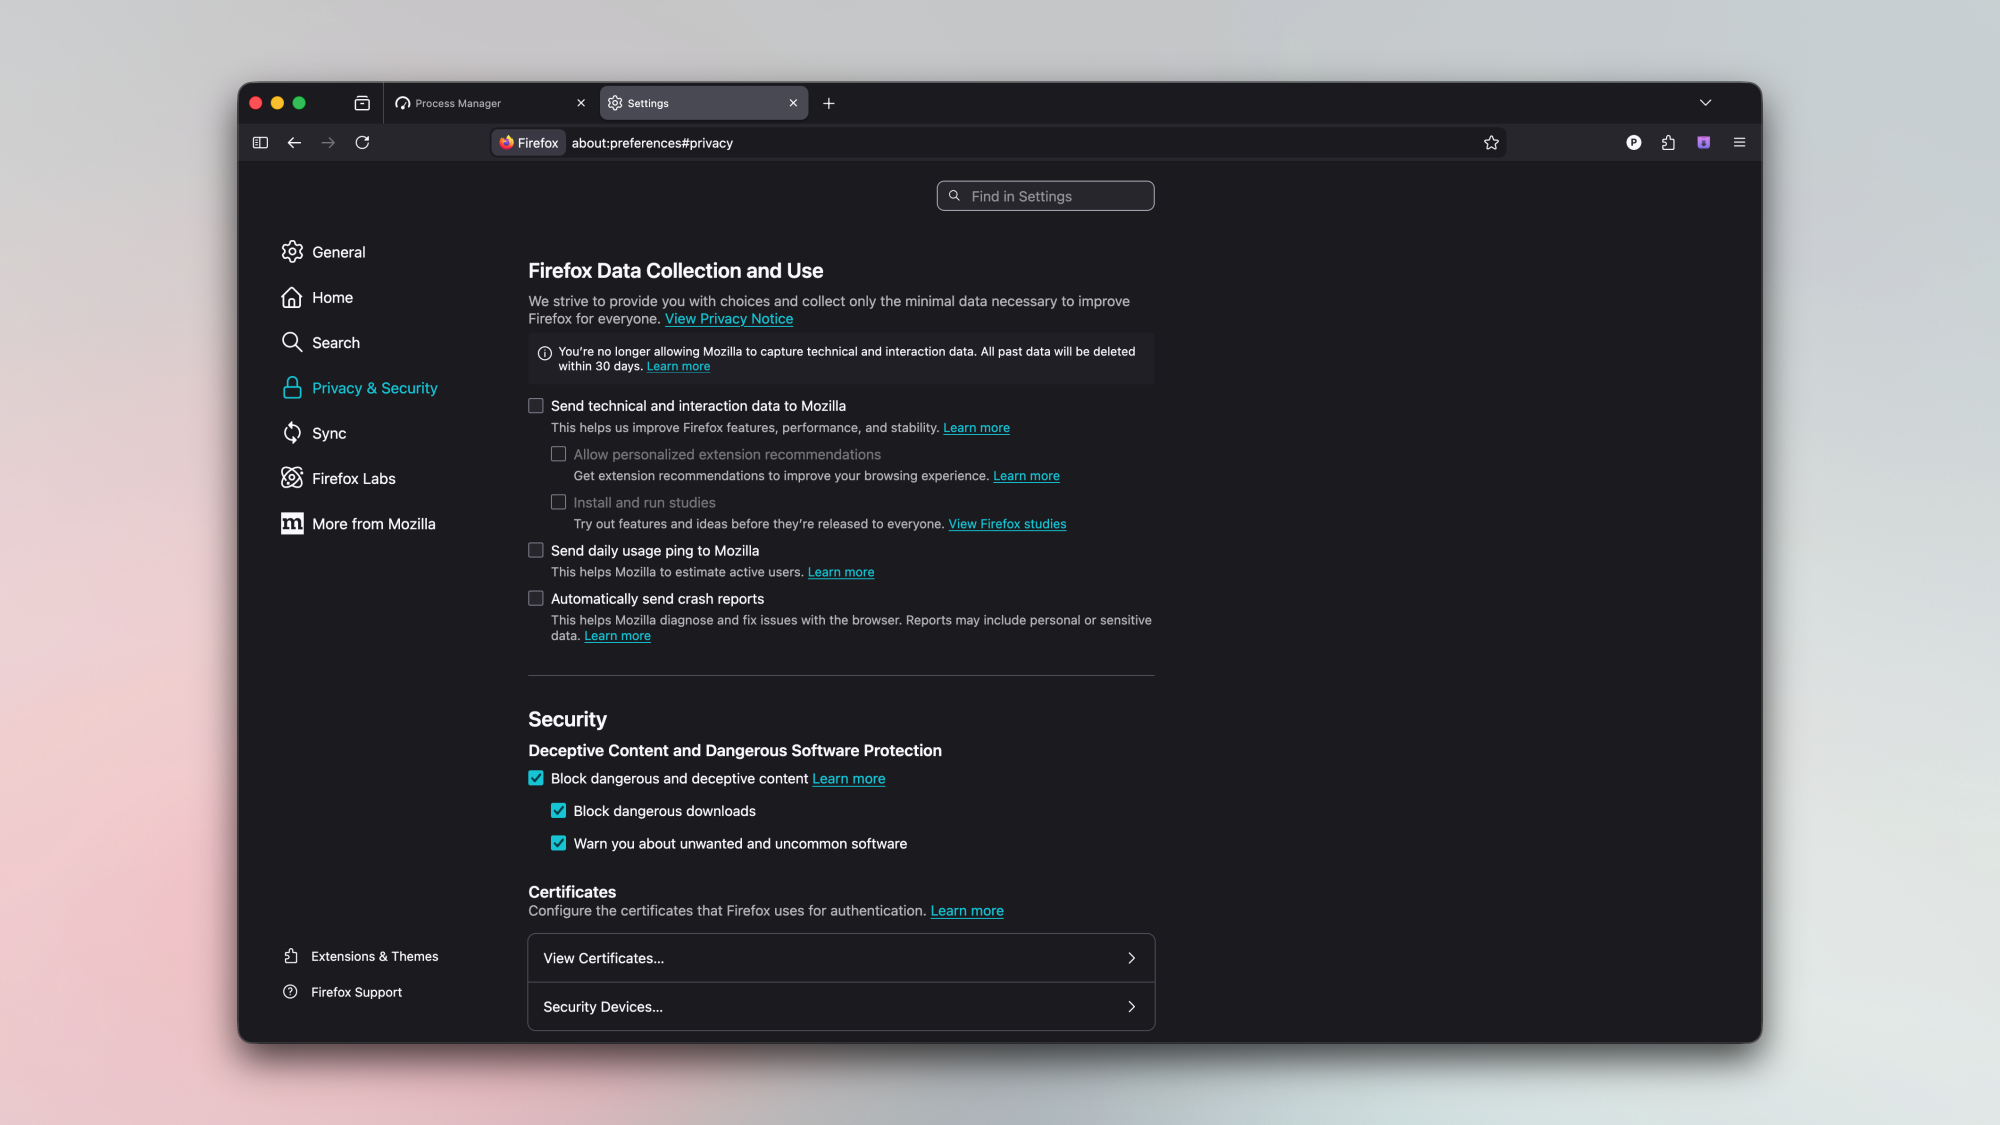
Unfortunately, Firefox collects a lot of data about your browsing habits by default, and I highly recommend disabling this to enhance your privacy. Go to Firefox settings > Privacy & Security > Firefox Data Collection, and disable every option under this section.
While you’re at it, let’s keep people who aren’t Firefox from seeing your browsing data, too. Firefox can automatically switch to a more secure HTTPS page if you accidentally open an unencrypted HTTP link (these are mostly being phased out, but you might stumble upon them every once in a while). Under Firefox settings > Privacy & Security > HTTPS-Only Mode, just toggle on Enable HTTPS-Only Mode in all windows. The browser will handle the rest.
You can also encrypt your web traffic further by enabling DNS over HTTPS, which is below the option I just mentioned. On the same page, in the section titled Enable DNS over HTTPS using:, scroll down a bit and choose Increased Protection or Max Protection (Max Protection is a bit stricter, but can break some websites, so I only recommend it for power users). The default DNS provider is Cloudflare, but you can also use NextDNS or a custom DNS if you wish. This feature makes it harder for third-parties to see which sites you’re visiting.
Whenever I visit a website these days, it feels like I’m being bombarded with permissions pop-ups asking me if they can send me notifications, use my location, and who knows what else. Firefox lets you easily disable most of these. Go to Firefox settings > Privacy & Security > Permissions. Click Location and select Block new requests to access your location. While you’re there, you can click through the available options and turn on other blocks, too. You can use these to block notification requests and autoplaying videos. Some sites may still use special tricks to bypass autoplay blocks, but it doesn’t hurt to make them work for it.
Install a few good extensions (but don’t overdo it)
Credit: Pranay Parab
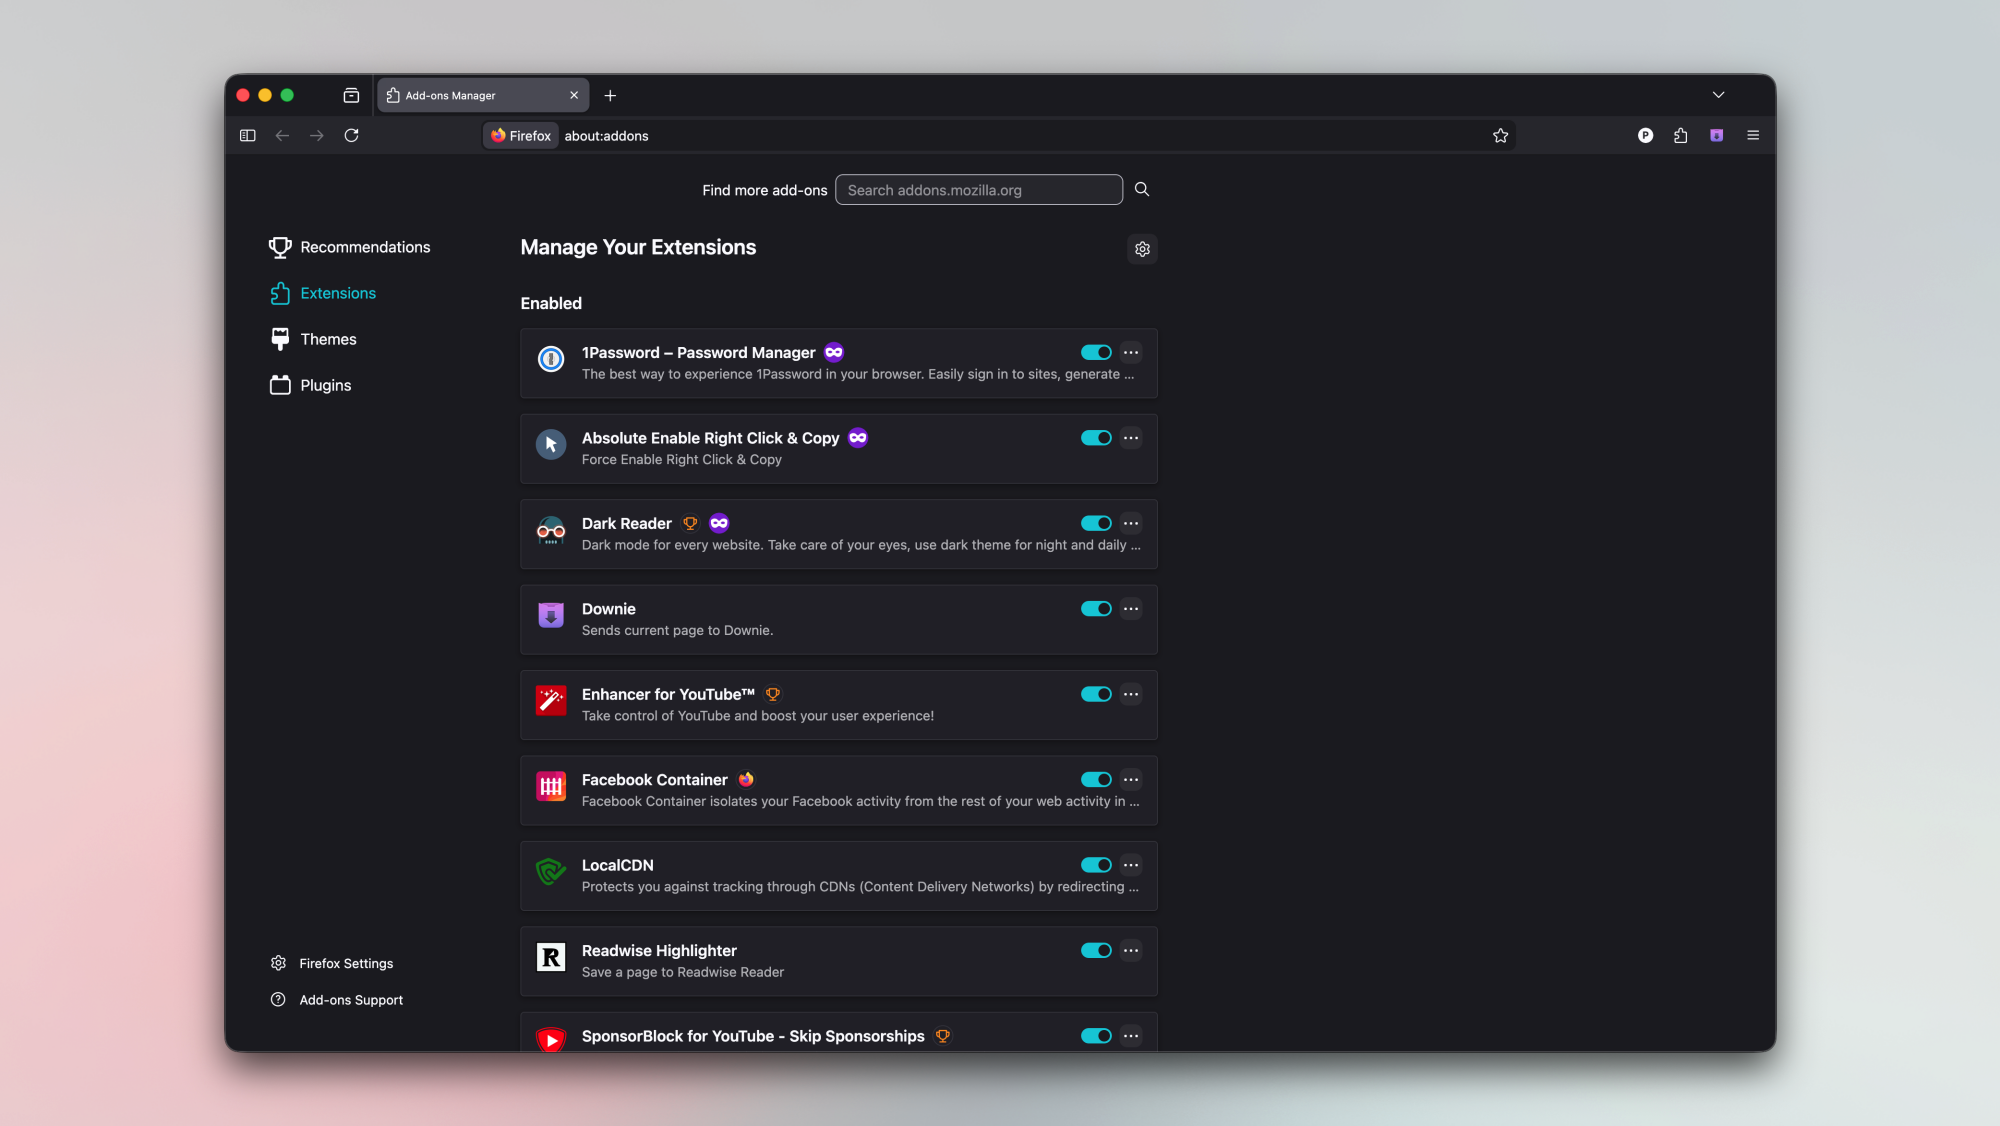
A Firefox installation just isn’t complete without a few good browser extensions. I keep seeing fun new extensions I want to install, but having too many of these can slow your browser down. So, it’s best to install a few good ones and remove any redundant extensions. To know where to start, check out my list of the best Firefox extensions.
Use a good ad blocker
There are many pros and a few cons to using an adblocker, but it’s a recommended tool these days, both to protect your privacy and to stay safe from scams. A good ad blocker will remove unwanted junk from webpages, block trackers, and speed up browsing. I’ve been using uBlock Origin for a decade now, and it’s still the one I recommend most to everyone who asks. Once the extension is installed, you should tweak a few advanced uBlock Origin settings to make the most of it.
Consider using vertical tabs
This is a bit of a controversial take, but it works for me, so here it goes: Vertical tabs are better than horizontal ones. I really like my browser window to occupy as much space as possible, and using horizontal tabs goes against that idea. Once I made the switch to vertical tabs, my browser’s window just started looking a lot cleaner. On my Mac, I still use horizontal tabs, but that’s because I keep the dock on the left side of the screen. On my Windows PC, however, vertical tabs just look so much nicer. If you want to try making the switch, go to Firefox settings > General > Browser Layout. Pick Vertical Tabs and enjoy.
Try Firefox Labs to see what the future looks like
No, this is not a time travel tip. Firefox Labs is where the browser releases experimental new features before making them public (or canning them). If you’re fine with being a guinea pig, Firefox Labs is your chance to try these experimental features without downloading the browser’s full beta release. You can enable these features by going to Firefox settings > Firefox Labs.
If you’re in the space business long enough, you learn there are numerous ways a rocket can fail. I’ve written my share of stories about misbehaving rockets and the extensive investigations that usually—but not always—reveal what went wrong.
But I never expected to write this story. Maybe this was a failure of my own imagination. I’m used to writing about engine malfunctions, staging issues, guidance glitches, or structural failures. Last April, Ars reported on the bizarre failure of Firefly Aerospace’s commercial Alpha rocket.
Japan’s H3 rocket found a new way to fail last month, apparently eluding the imaginations of its own designers and engineers.
Windscribe is a virtual private network (VPN) with intense “How do you do, fellow kids?” energy. It has servers in 69 countries and an annual plan that costs $69, an obsession with the sex number that rivals Elon Musk’s. I’m shocked that it doesn’t have a subscription costing $4.20 per month.
But there’s another side to Windscribe’s cringe: an obsession with independence and a Bernie Sanders-like anger on behalf of an exploited public. In a market where the best VPNs aim for professionalism, Windscribe aspires to be punk. Its iconoclasm may have led it to develop an app that looks like ExpressVPN in a trash compactor, but it also spurred Windscribe to offer a strong free plan and forgo financial relationships with VPN reviewers. That attitude earned it a spot on my list of the best free VPNs.
Although Windscribe’s heart is in the right place, my job is to figure out whether that translates into a good product. I used our rigorous VPN testing procedure to rate Windscribe in 11 categories. You can find my results in the table below and a final verdict at the end of the review.
Editor’s note (1/27/26): We’ve overhauled our VPN coverage to provide more detailed, actionable buying advice. Going forward, we’ll continue to update both our best VPN list and individual reviews (like this one) as circumstances change. Most recently, we added official scores to all of our VPN reviews.Check out how we test VPNs to learn more about the new standards we’re using.
Findings at a glance
Category
Notes
Installation and UI
Installation and setup are always straightforward
Apps look very similar on Windows, macOS, iOS and Android
App design is overly compact and often impenetrable, but hides a solid program
Browser extensions allow one-click bypassing of security features on the current page, much like common ad blockers
Speed
Average latency below 300 worldwide
Some slowdown in download and upload speeds, but not severe
Speeds were highly consistent everywhere except some African servers
Security
Six solid protocols — WireGuard, IKEv2, and four based on OpenVPN
Most protocols available on all platforms, except IKEv2 on Android
No leaks detected, even while switching servers
Packets are encrypted as expected
Pricing
$9 per month, $69 for one year ($5.75 per month)
Custom plans cost $1 per country plus $1 for unlimited data; must spend at least $3
Static IPs available for $2 per month or $8 per month for a residential address
Free plan gives you 10 locations and 10GB per month with a confirmed email
Bundles
Shares coupon codes for various discounts on five “partners in privacy”
Privacy policy
Retains very little information, none of it personally identifiable
Can make an account without an email address
All apps have been audited by independent overseers
Fought Greek court case in 2025 because it had no logs to turn over
Virtual location change
15 different servers in five locations unblocked Netflix
Content changed each time, suggesting the destination site was completely fooled
Server network
193 server locations in 122 cities across 71 countries
Only two virtual server locations in the entire network
Real servers in Russia and India risk abrupt shutdowns
Features
Standout extras include the customizable R.O.B.E.R.T blocker and split tunneling on Windows, Mac and Android
Network Options offers lots of automation choices, but terminology makes it needlessly confusing
Includes obfuscation to get online in restrictive regions
Firewall is a stronger version of a kill switch, preventing any access unless the VPN is connected
Customer support
Knowledgebase search bar is good at finding articles, and articles themselves are useful
Garry AI chatbot is helpful, but pushed way too hard at the expense of access to human agents
Active Reddit and Discord communities for peer-to-peer help
Background check
Founded in Canada in 2016
No significant controversies in 10 years
Canada is a Five Eyes nation, but this shouldn’t matter if Windscribe is keeping to its no logs policy
Installing, configuring and using Windscribe
The first step is always to figure out how easy or hard the VPN is to use. Windscribe and other VPNs are important tools, but you’ll never use them if the UI gets in the way. I tested Windscribe’s desktop apps on Windows and Mac, its mobile apps on iOS and Android and its Chrome and Firefox browser extensions.
To start with, let me say that installing Windscribe is a breeze no matter where you do it. The downloaders and installers handle their own business, only requiring you to grant a few permissions. The apps arrive on your system ready to use out of the box.
Windows
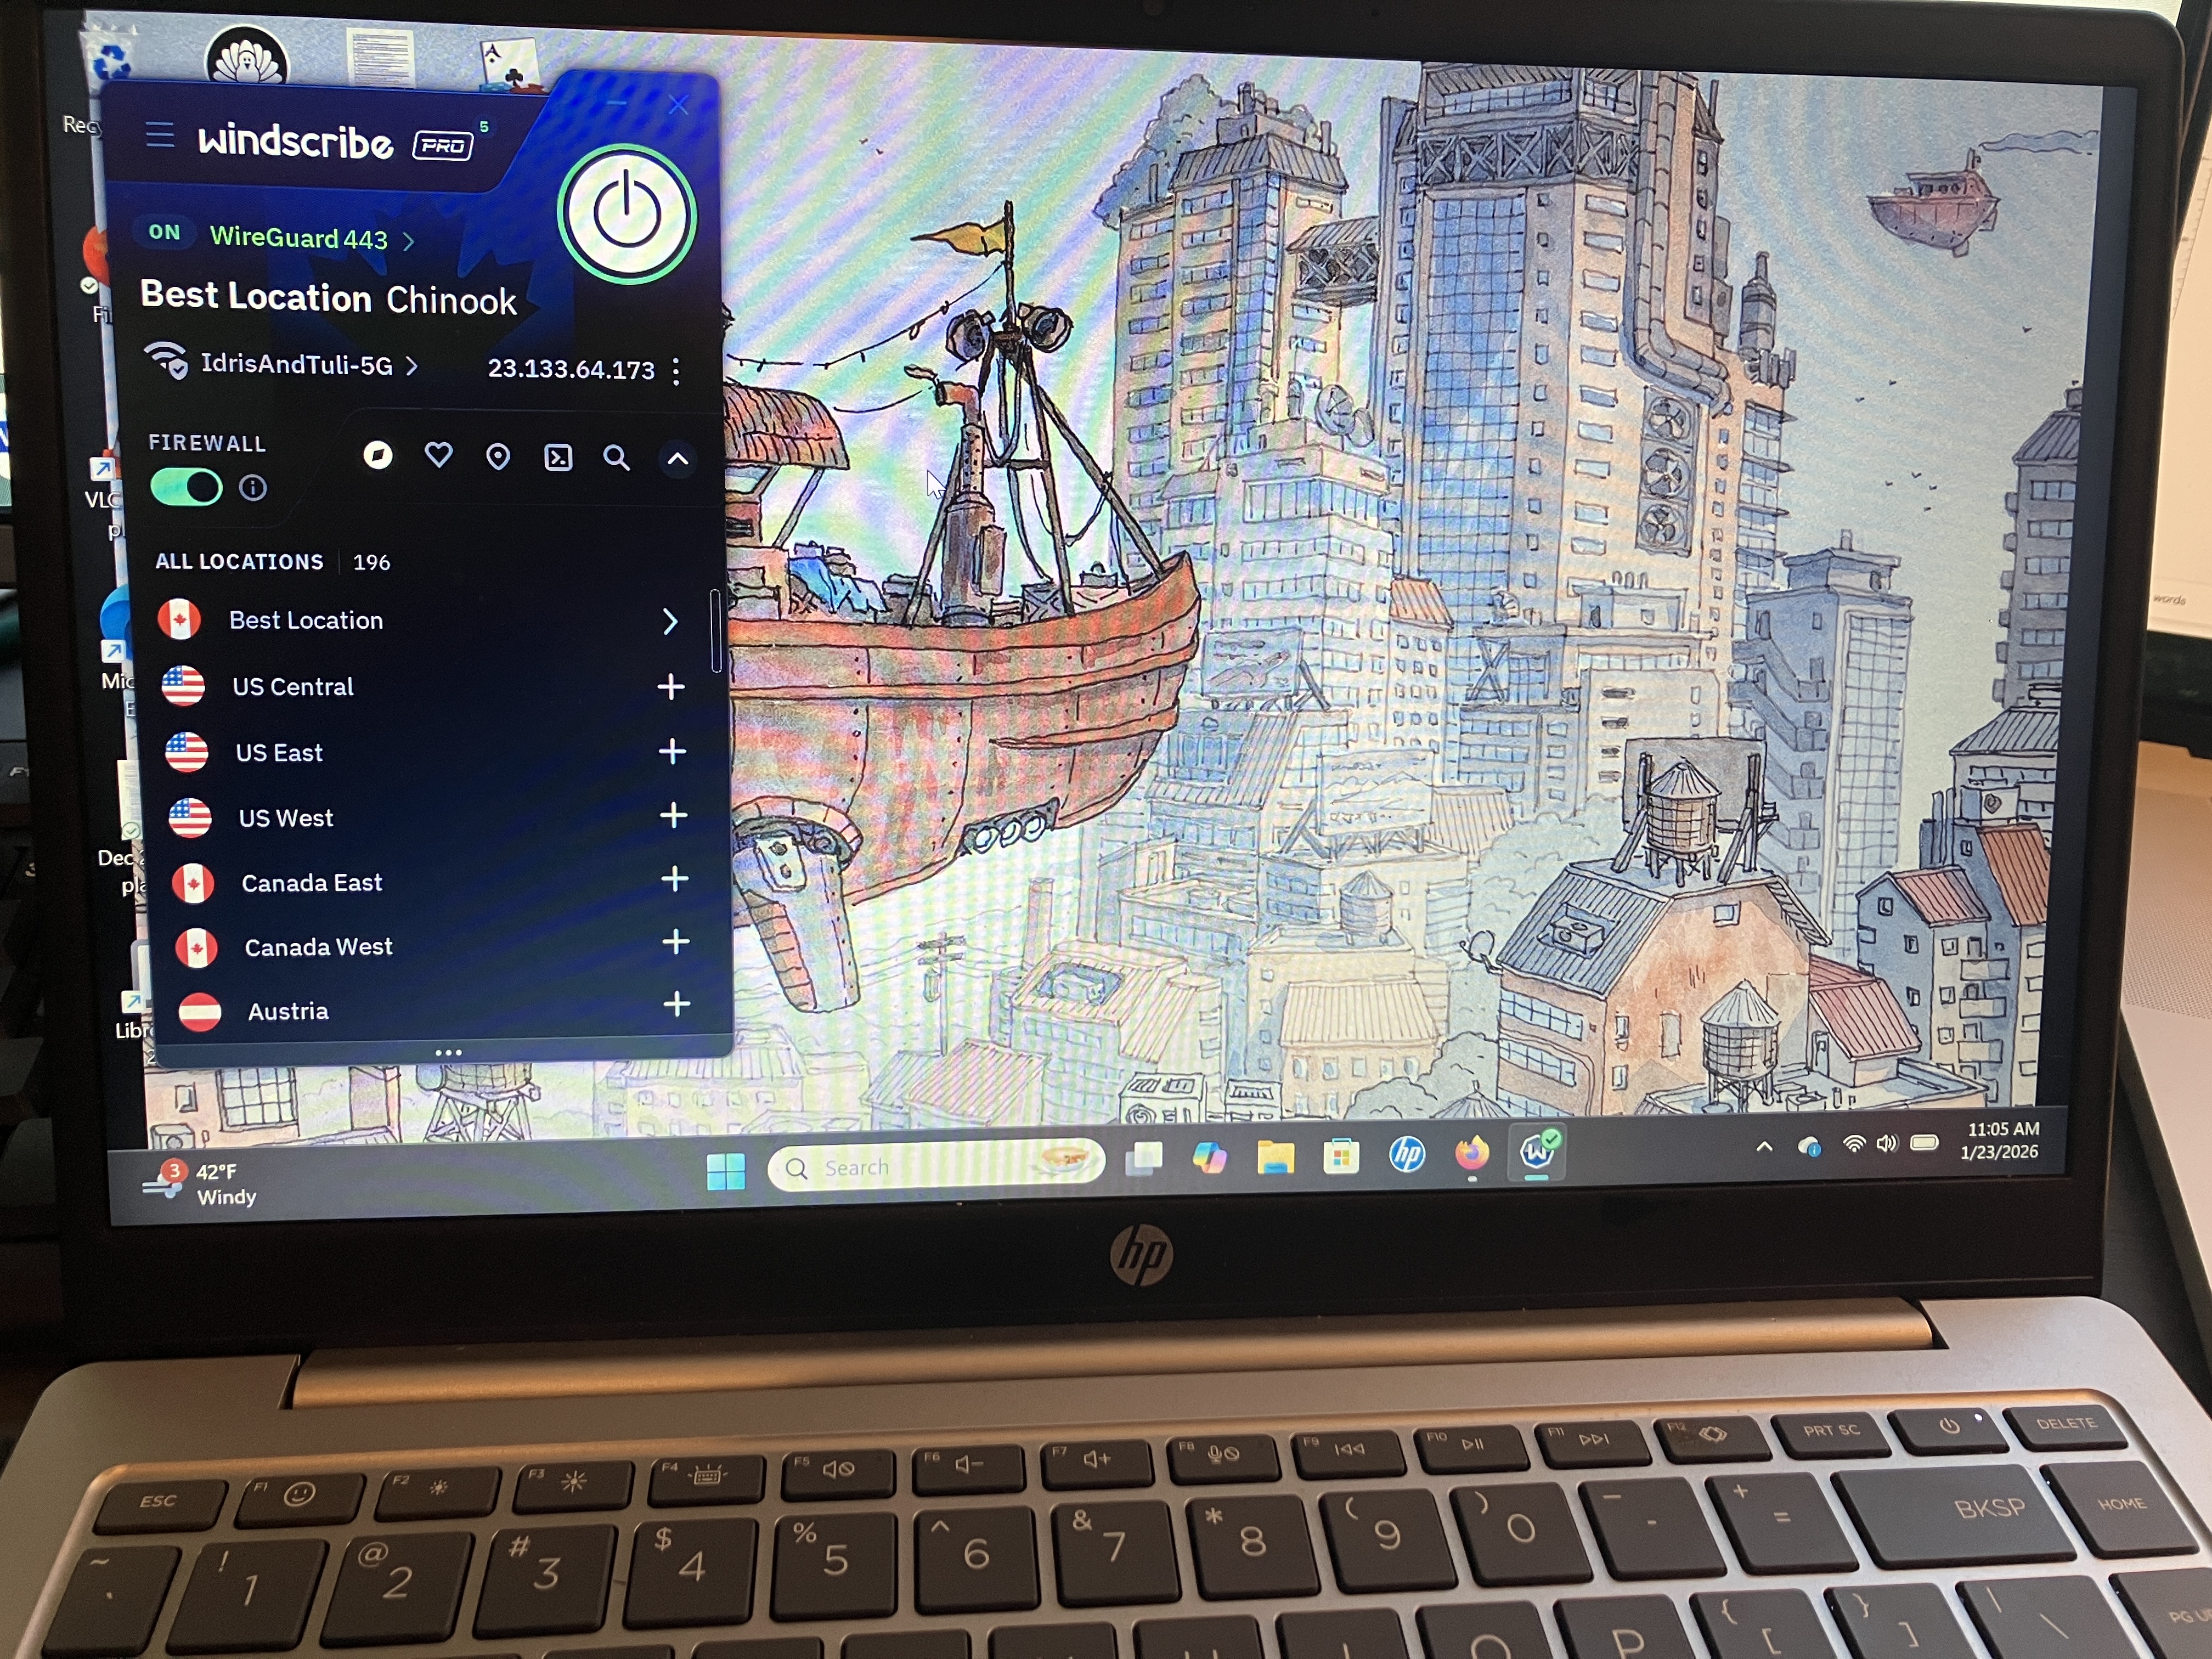
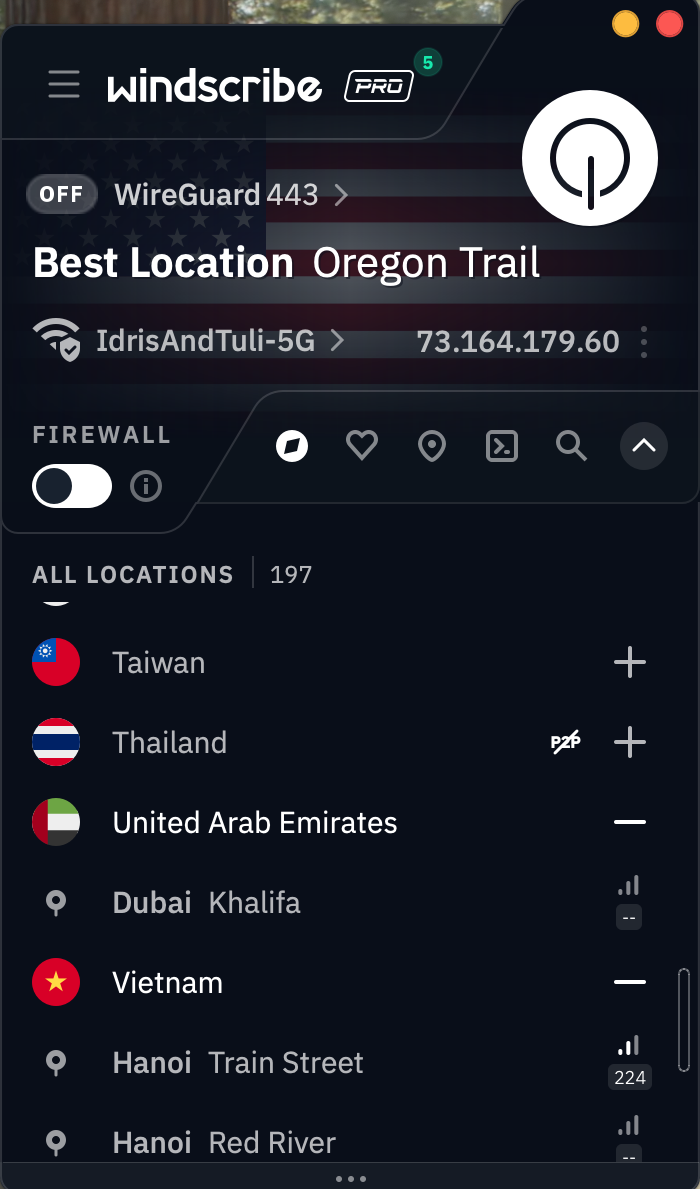
The first thing you’ll notice about Windscribe is that it’s not even slightly interested in looking like any other VPN. It crams everything into an extremely compact window, which has some advantages — mainly that it’s easy to operate it while looking at another app. On the downside, well, it looks like this.
Windscribe’s UI on a Windows laptop.
Sam Chapman for Engadget
The Windscribe team will probably just say that I’m brainwashed by the establishment, but there’s a good reason that most VPNs choose designs with a little more space. This fiddly console, most of which is taken up by information you can’t interact with, is likely to confirm all a newcomer’s worst fears about using a VPN. Private Internet Access had a similar problem of tightening its app design to the point of being incomprehensible.
The problems persist when you get to the settings page. It’s easy to make sense of a VPN without technical knowledge, but Windscribe’s preferences menu does everything it can to obscure that truth. Highly technical features are mixed in with options for casual users, and the explanatory blurbs usually cloud the issue even further.
Even the “Look & Feel” settings somehow manage to be confusing. What is the difference between the Stretch, Fill and Tile modes for aspect ratio? What the heck is a Bundled background, and what does it matter whether it’s Square, Palm, Ripple, Drip or Snow? The answers to all these can be found by playing around or looking in the knowledgebase, but a VPN really shouldn’t require that for its most basic toggles.
Once you get used to Windscribe and learn where to find the features that actually matter, it runs quite smoothly. Connections are never delayed and there are none of the random error messages that have dogged me on other VPNs. In a world of VPNs that look great but run clunkily, Windscribe has built one that looks terrible but runs great. I can’t complain about how well it works, but is it too much to ask for a provider that does both? (Oh, wait, that’s Proton VPN.)
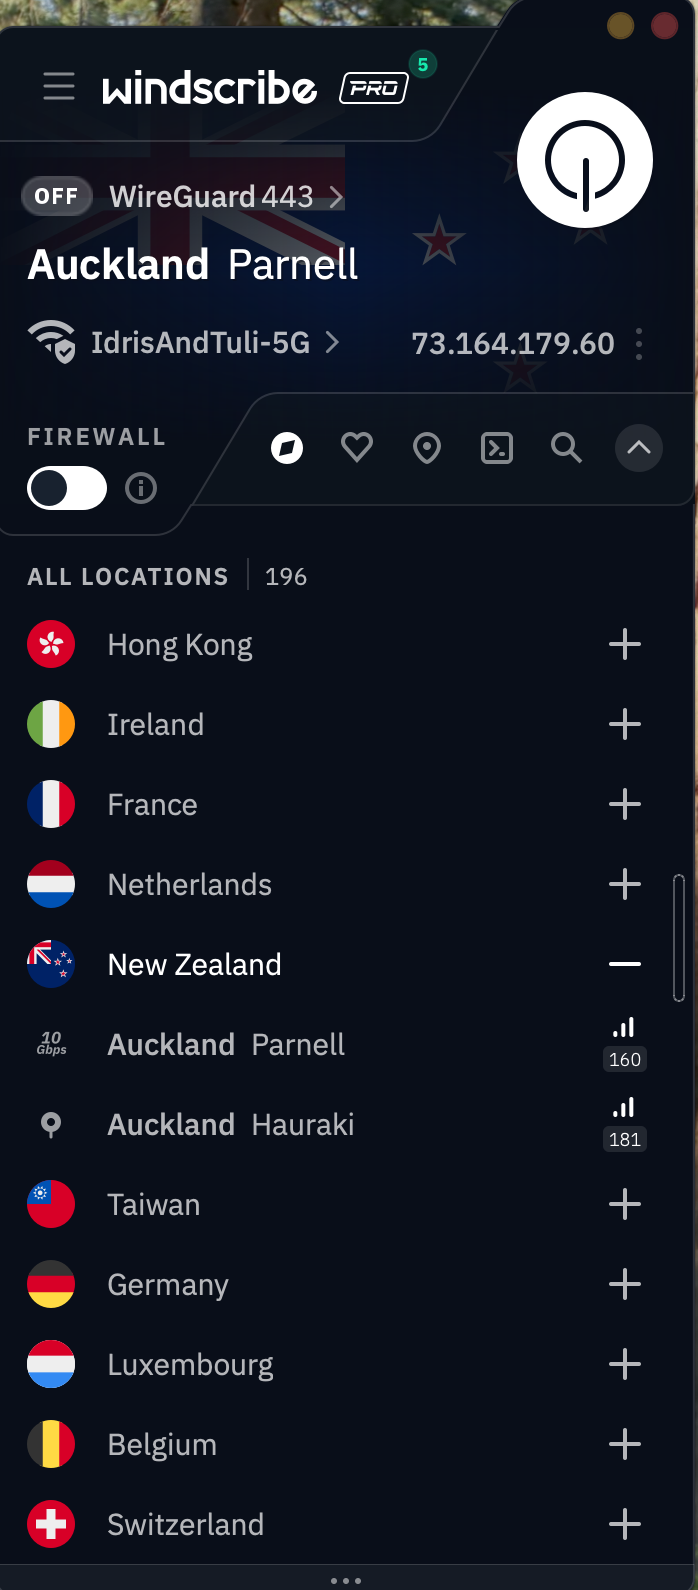
Mac
Windscribe’s macOS app is almost identical to its Windows app. That deserves praise in itself — you’ll get much the same experience no matter which type of computer you use. But it also means the Mac app shares the same problems.
Windscribe’s app for Mac desktops and laptops.
Sam Chapman for Engadget
There’s the same overly compact design cluttered with too much information. The same technobabble-filled options menu. And the same fundamental solidity underlying it all: a VPN that does the job beautifully but has no interest in being accessible. It would be a mistake to write Windscribe off because of its app design, but it’s important to know what you’ll have to work through.
Android
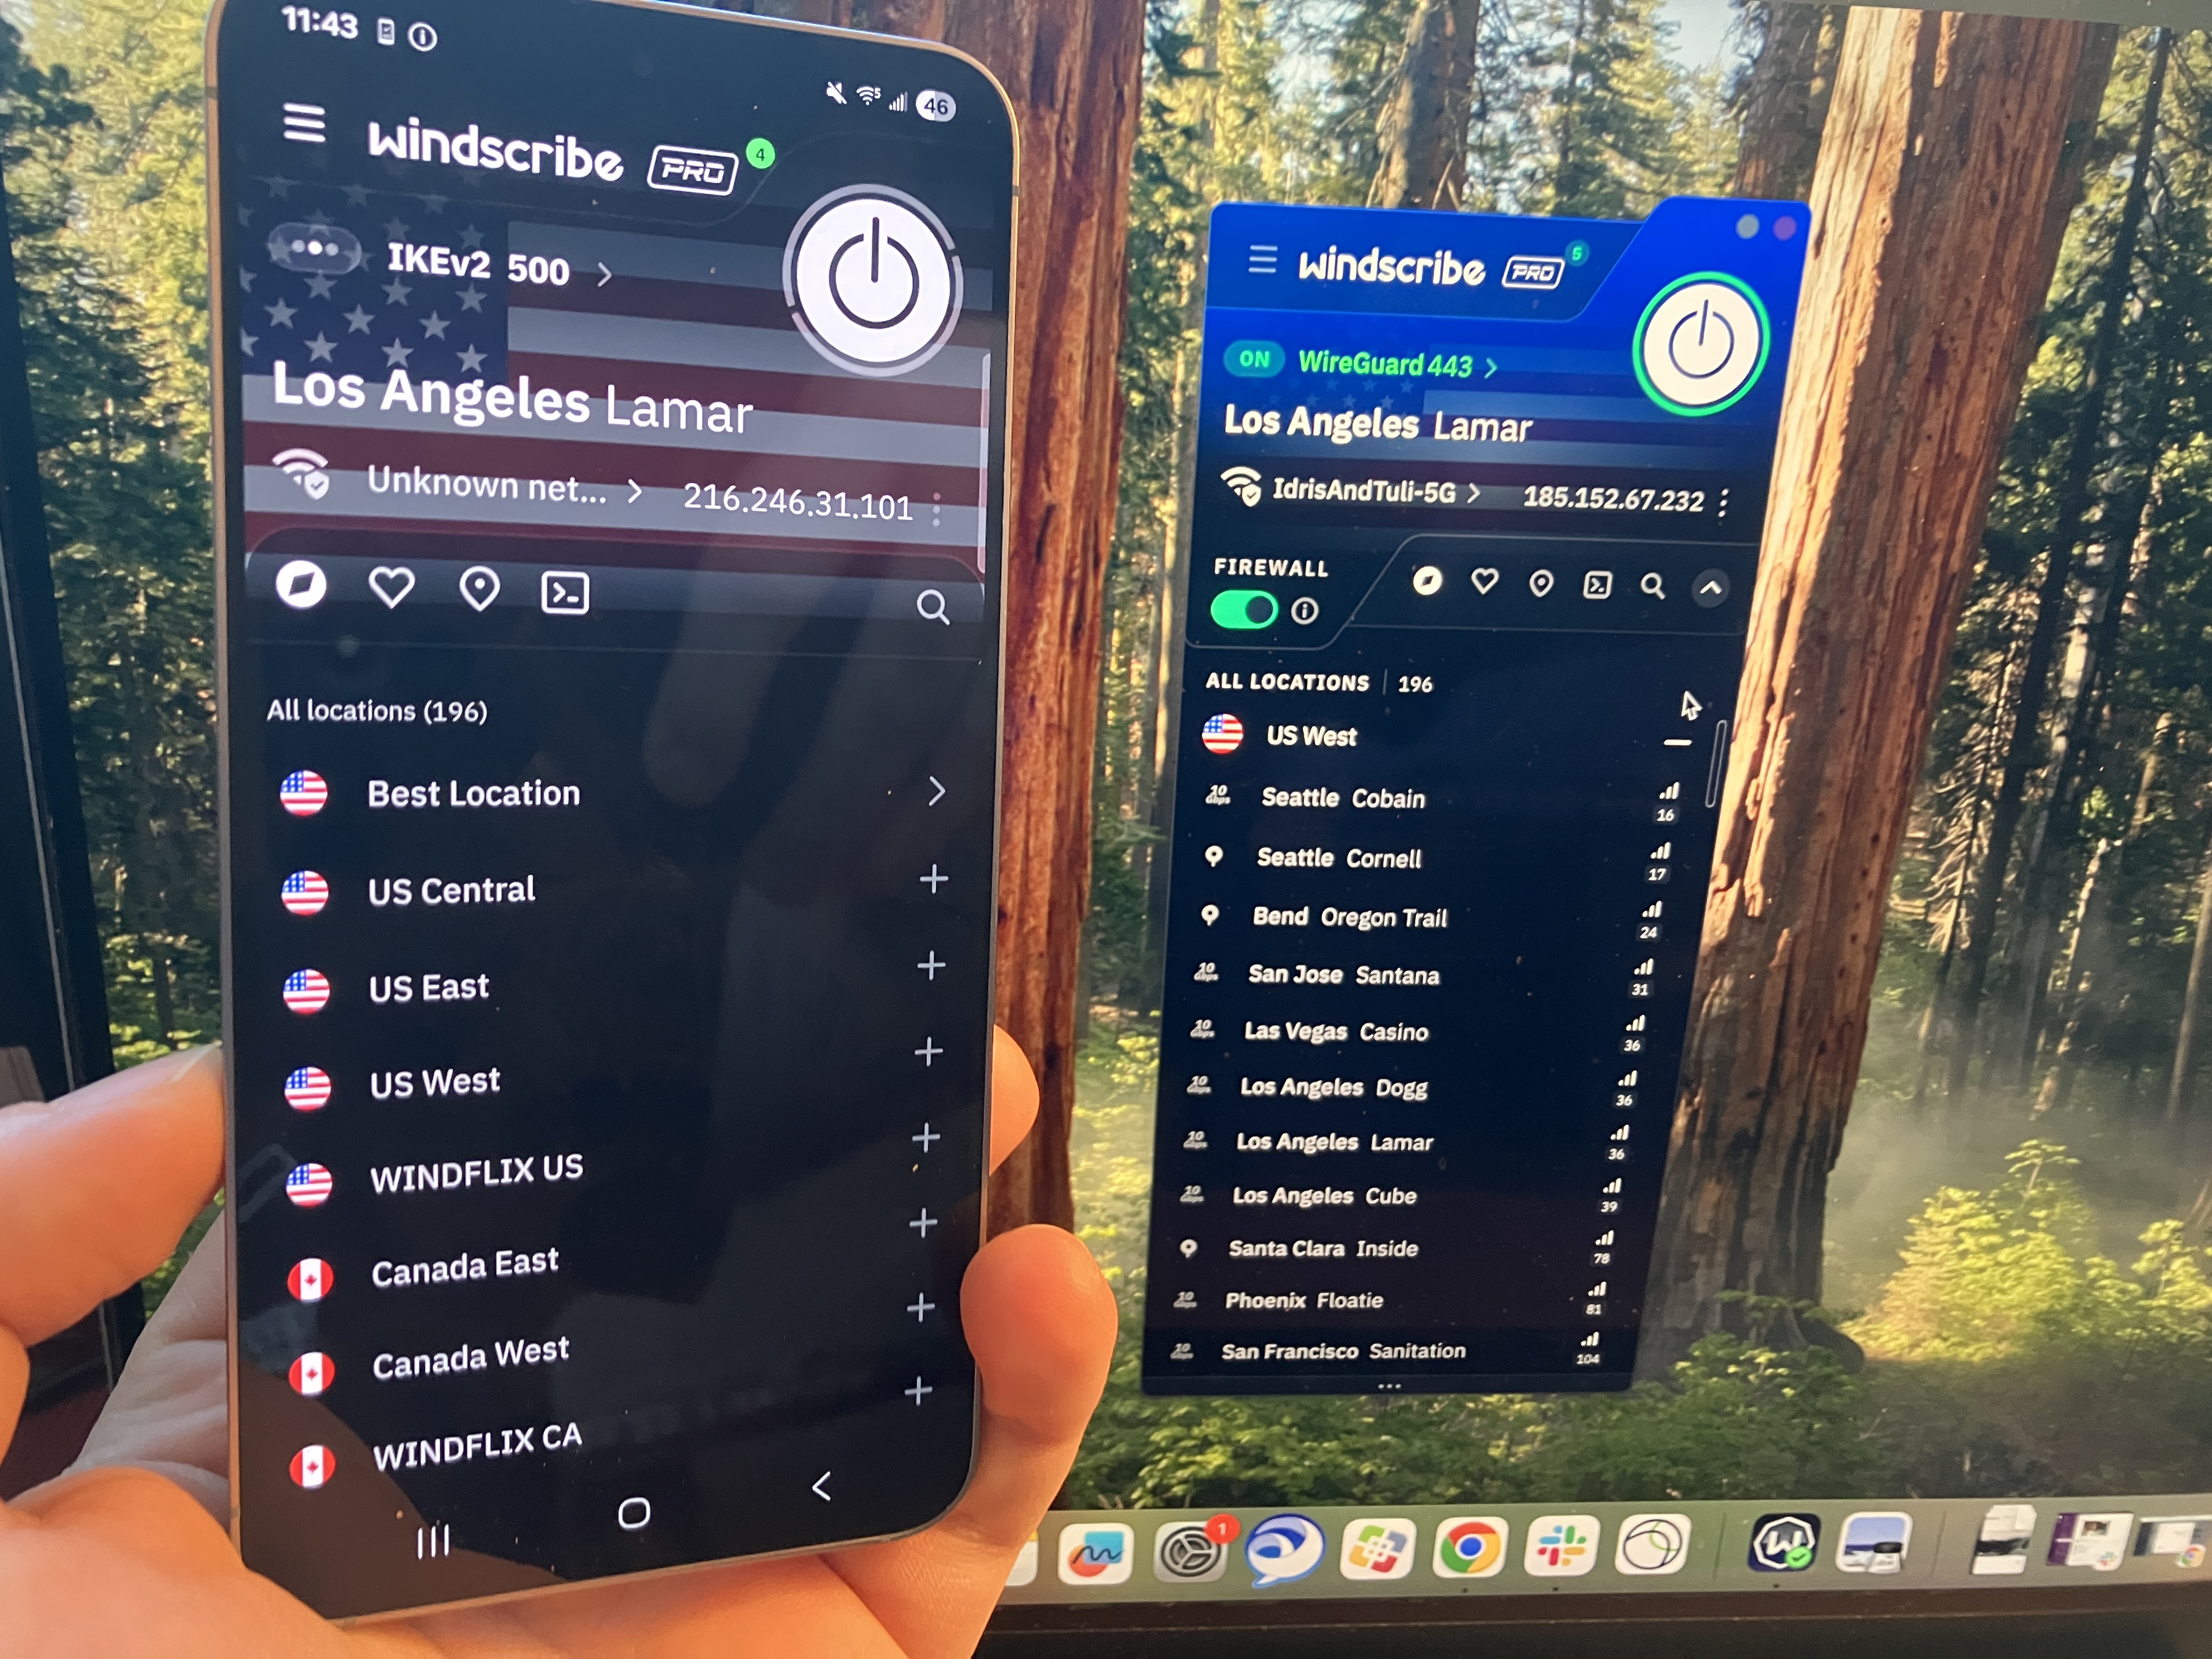
One thing I can’t fault Windscribe for is a lack of consistency. The Android app looks a lot like the Windows and Mac apps, only lightly adapted for the mobile format. On these devices, the design decisions make more sense — the UI writing is still impenetrable for casual users, but the compact pages look a lot more normal on a phone screen.
A comparison of Windscribe’s extremely similar apps on Android and Mac.
Sam Chapman for Engadget
iOS
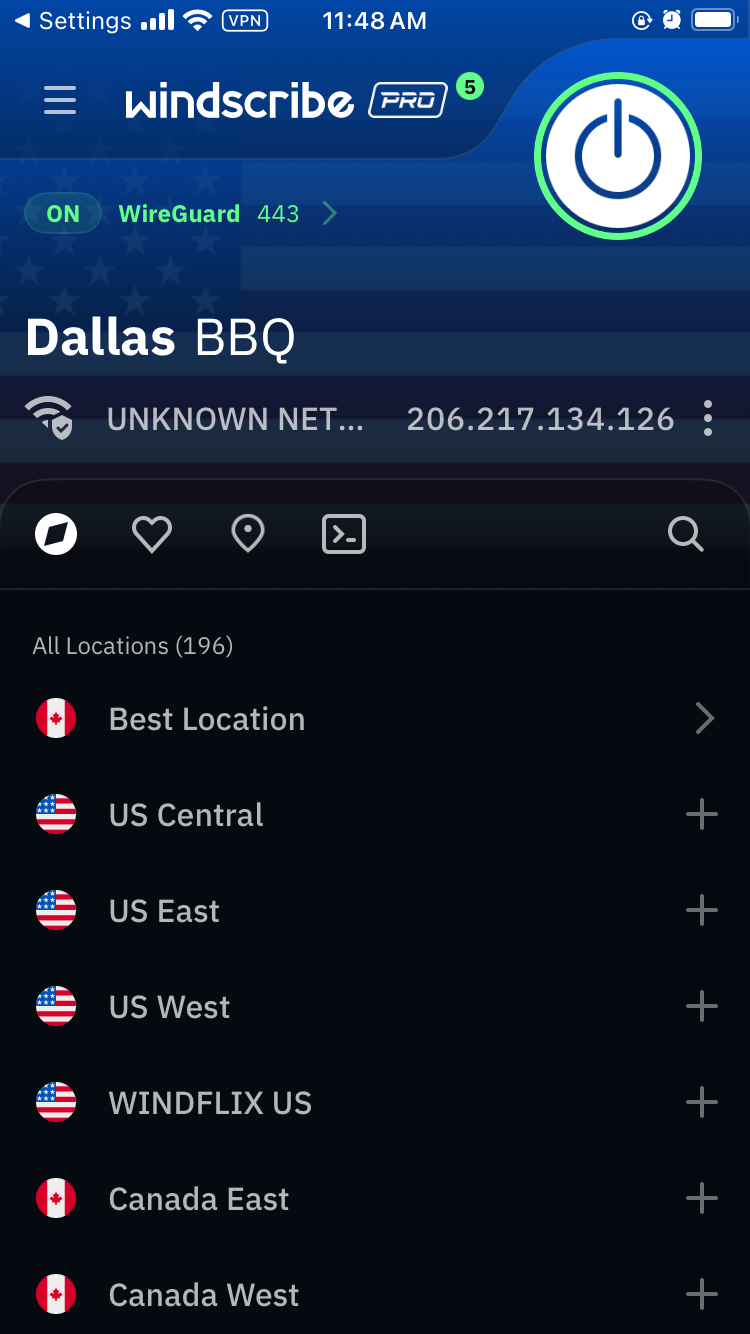
There’s not a lot to say about Windscribe on iOS that I haven’t already said about the other three main platforms. Looking over all my screenshots, it seems fairly clear that Windscribe’s problems — much like PIA’s — come from starting on mobile and trying to make that same design work on desktop. It’s still not great to look at, but I can at least see where they’re coming from.
Windscribe’s iOS app.
Sam Chapman for Engadget
Browser extensions
Windscribe’s extensions for Chrome and Firefox look a little like its desktop and mobile VPN apps, but they act a little differently. They serve the same basic purpose as the standalone apps — changing your IP address and location — but they’re also customizable ad blockers for the web page you’re currently on.
Windscribe’s Google Chrome extension.
Sam Chapman for Engadget
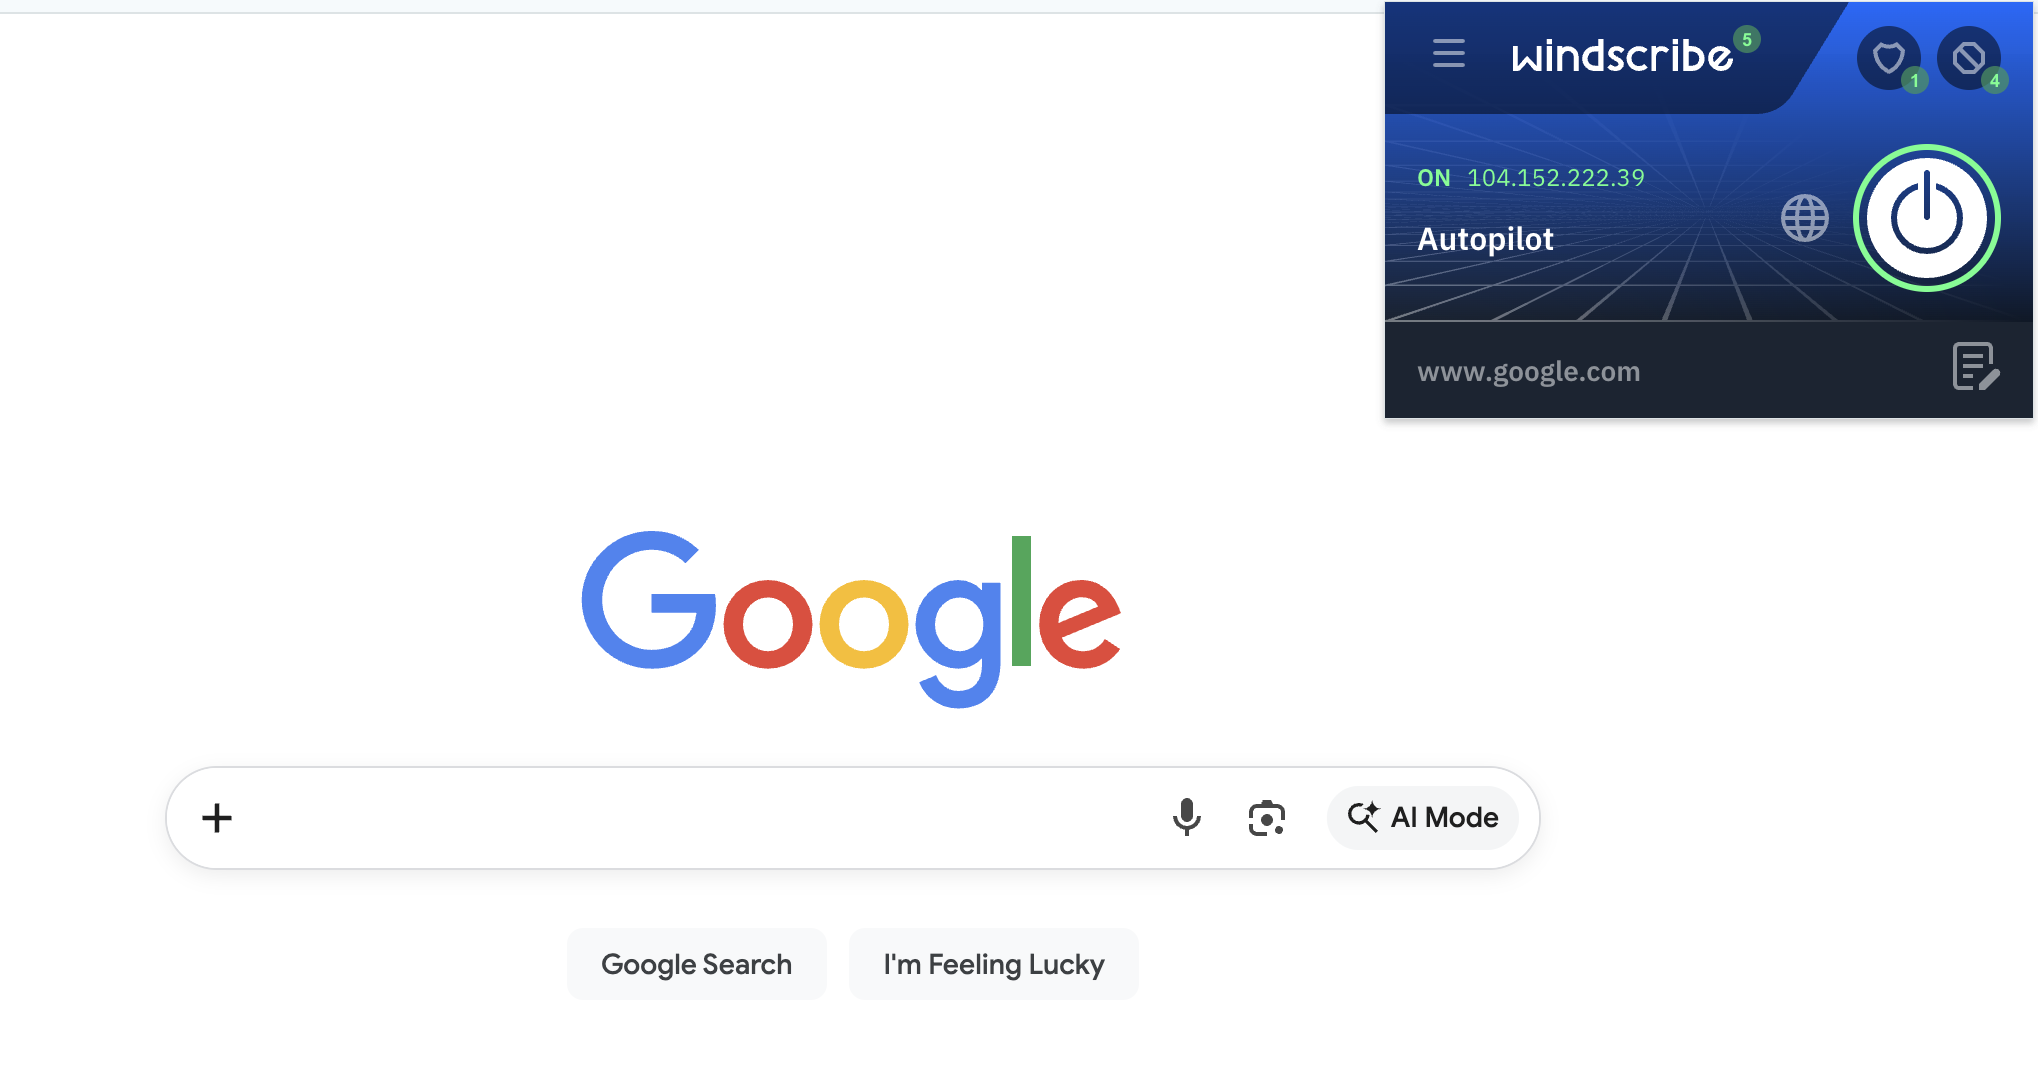
For example, in the image above, I can control what location Google perceives me to be in. But I can also control what gets blocked by choosing to let Google bypass certain features. Clicking the leftmost button makes the current website skip the VPN tunnel. The central button shuts off the ad blocker and the right-hand button shuts off the features on the Privacy section of the preferences menu. Like everything else about Windscribe, it’s unintuitive but works great once you figure it out.
Windscribe speed test
I used speedtest.net to test Windscribe’s speeds. In case you aren’t familiar with the jargon, Ping measures a server’s latency, which is how long it takes a single packet of data to reach it from your device. Download speed measures how much data can be downloaded at a time, while upload speed shows how quickly you can send data to the network. Think of ping as your car’s speed in miles per hour and download and upload speed as the amount of traffic on the road.
As usual, I used the WireGuard protocol to run these tests, since it’s almost always the fastest. Starting with my unprotected speeds at home in Portland, I moved gradually farther away until I was connecting to the other side of the world. Ideally, ping should increase linearly (not exponentially), while download and upload speeds don’t dip much at all. I’ve recorded Windscribe’s performance in the table below.
Server location
Ping (ms)
Increase factor
Download speed (Mbps)
Percentage drop
Upload speed (Mbps)
Percentage drop
Portland, USA (unprotected)
22
—
59.35
—
5.92
—
Vancouver, Canada (fastest location)
27
1.2x
55.89
5.83
5.56
6.08
Boston, USA
161
7.3x
48.49
18.30
5.66
4.39
Quito, Ecuador
283
12.9x
46.46
21.72
4.68
20.95
London, UK
287
13.0x
43.70
26.37
4.51
23.82
Nairobi, Kenya
595
27.0x
32.63
45.02
3.57
39.70
Seoul, South Korea
258
11.7x
43.27
27.09
4.48
24.32
Average
269
12.2x
45.07
24.06
4.74
19.93
Windscribe gave me some of the shortest latencies I’ve ever seen — comparable to CyberGhost, whose ping lengths I was also very impressed by. Its download and upload speeds also look a lot like CyberGhost’s, with both firmly in good-but-not-amazing territory.
However, Windscribe’s speeds were a lot more consistent. Throughout the tests, I hardly ever saw major fluctuations in the same location, on any metric. The Nairobi server seemed to be under some strain, but that’s not unusual for a VPN in Africa. Every location except for that one followed a smooth downward curve. I’m happy with that; speed is one of the areas where you want your VPN to be reliably boring, not flashy.
Practically, a speed test like this suggests that Windscribe is best for gaming, livestreaming and video chatting, and that it’s perfectly serviceable for any other task you could do online. You may not get the best speeds you’ve ever seen, but unless your internet is bad to begin with, Windscribe should not slow it down enough to be noticeable.
Windscribe security test
I can say up top that Windscribe doesn’t seem to have any dangerous security flaws, but I’ll take this section to explain why I think that. To start with, it uses only the three VPN protocols currently known to be secure: WireGuard, OpenVPN and IKEv2, plus a few other options all based on OpenVPN. With those options, you can be sure you’re getting encryption that’s currently uncrackable.
It also passed two batteries of tests I ran on its security. The first set of tests looks for DNS leaks, WebRTC leaks and other slip-ups that might reveal your real IP address. The second checks whether data packets sent through the VPN tunnel are actually getting encrypted. Check each section below for details on how Windscribe did.
VPN protocols
A VPN protocol determines how exactly a VPN makes contact between its own servers, your device and your ISP. Certain protocols can make your VPN run faster, stabilize a shaky connection or get into websites other protocols fail to unlock. If you’re having a problem with your VPN, changing the protocol is one of the first troubleshooting steps.
Windscribe makes a total of six protocols available, though it’s really just three, since four of the six are variations on OpenVPN. WireGuard works on every platform, and is currently the fastest and most stable — its drawback used to be that it was new, but with the passage of time, it’s no longer new enough to make it suspect.
IKEv2 is a connection protocol that uses the separate IPSec protocol for its security. This double team’s main strength is reconnecting to the VPN when a device switches networks; it’s also good at not draining phone batteries. Windscribe supports IKEv2 on Mac, iOS and Windows.
OpenVPN is the oldest open-source VPN protocol, refined by over a decade of repeated probing by volunteers. It’s not only relatively fast and highly secure, but comes in two flavors: TCP, which makes connections more stable, and UDP, which is usually faster and should be your first resort with OpenVPN. Windscribe supports OpenVPN on all platforms.
Windscribe rounds out the selection with two unique protocols, both focused on hiding your VPN traffic from firewalls and censors. Stealth uses the same connection ports as HTTPS, so it can’t be blocked by shutting certain ports down entirely. WStunnel obfuscates connections even further by using the extremely common WebSocket technology to establish VPN connections. Both these proprietary protocols are much slower than the other options, but can save you if you find yourself repeatedly blocked while using Windscribe.
Leak test
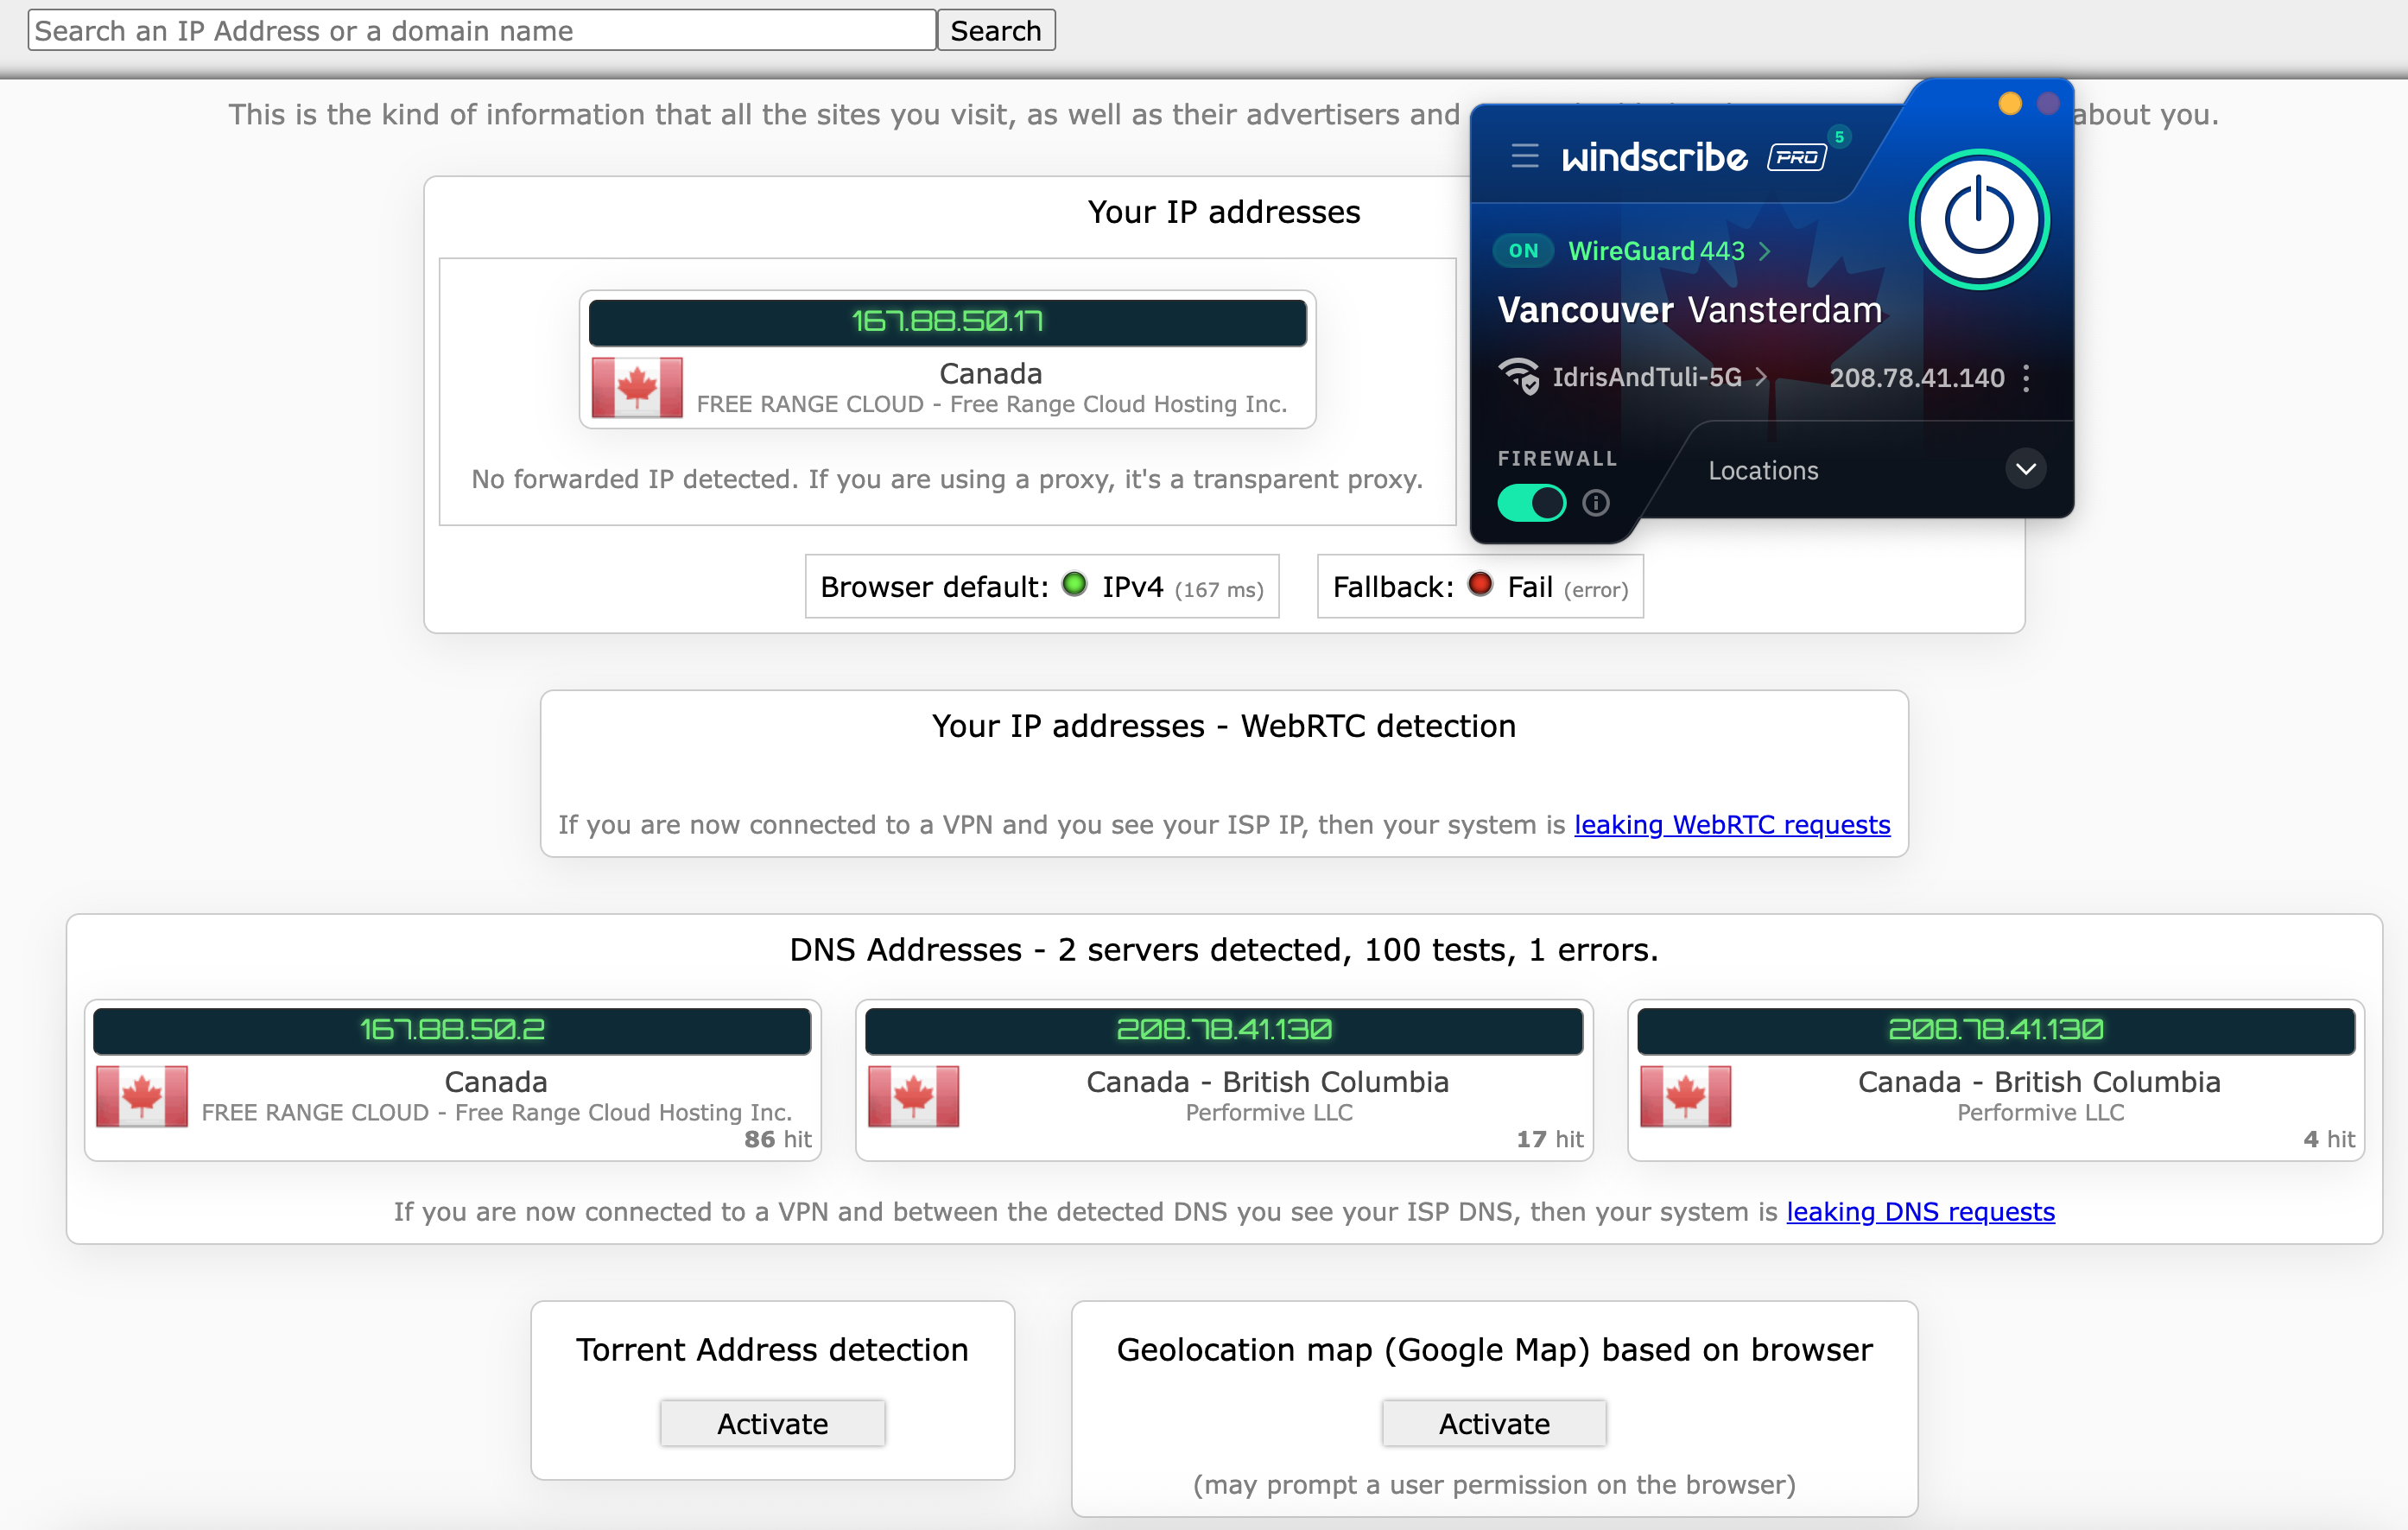
I started my leak tests by using ipleak.net to check several Windscribe servers for IP leaks of all sorts. Each time I connected and checked my location, I only saw the VPN server’s IP address, never my real one. I tried to trip Windscribe up by switching servers while remaining connected, even changing continents, but my true location never once slipped out. This puts its security solidly above CyberGhost, Norton VPN and many others.
I couldn’t find any holes in Windscribe’s armor.
Sam Chapman for Engadget
Windscribe automatically blocks IPv6 traffic while connected, so IPv6 leaks weren’t going to be a thing. I finished the test by checking five servers using browserleaks.com/webrtc, finding no issues each time.
Encryption test
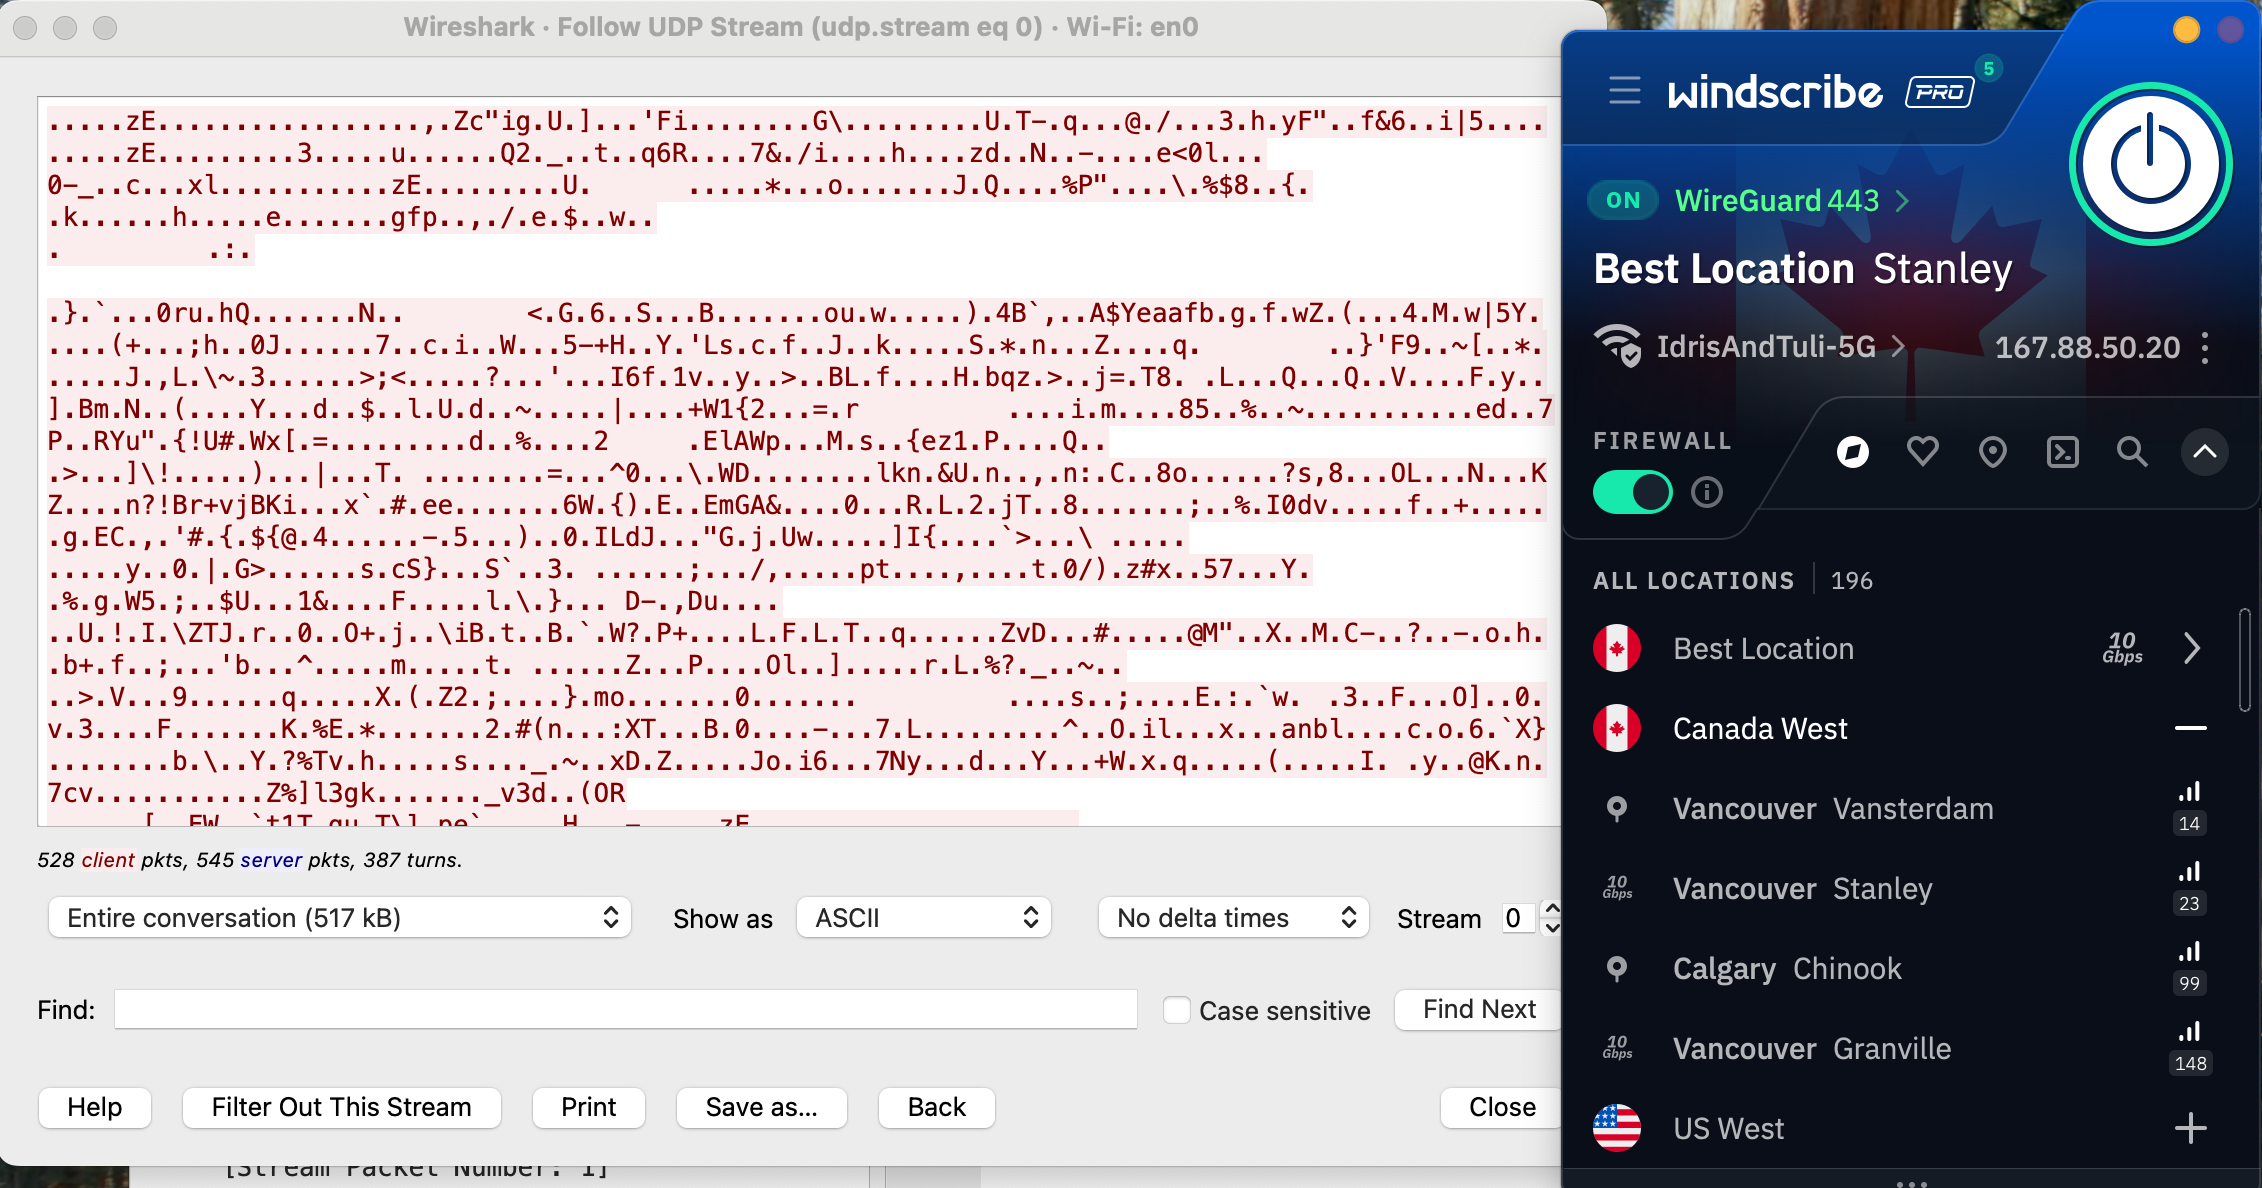
The final step is to make sure Windscribe is applying encryption properly through its VPN protocols. For this test, I used a free packet sniffer app called Wireshark to look directly at what my computer was sending out.
Windscribe’s encryption looks solid.
Sam Chapman for Engadget
It’s a bit hard to tell what’s going on, but to summarize, I’ve loaded a website without HTTPS protection and checked whether Windscribe managed to apply that protection. The lack of readable information in the data stream proves that its encryption is indeed working as expected.
How much does Windscribe cost?
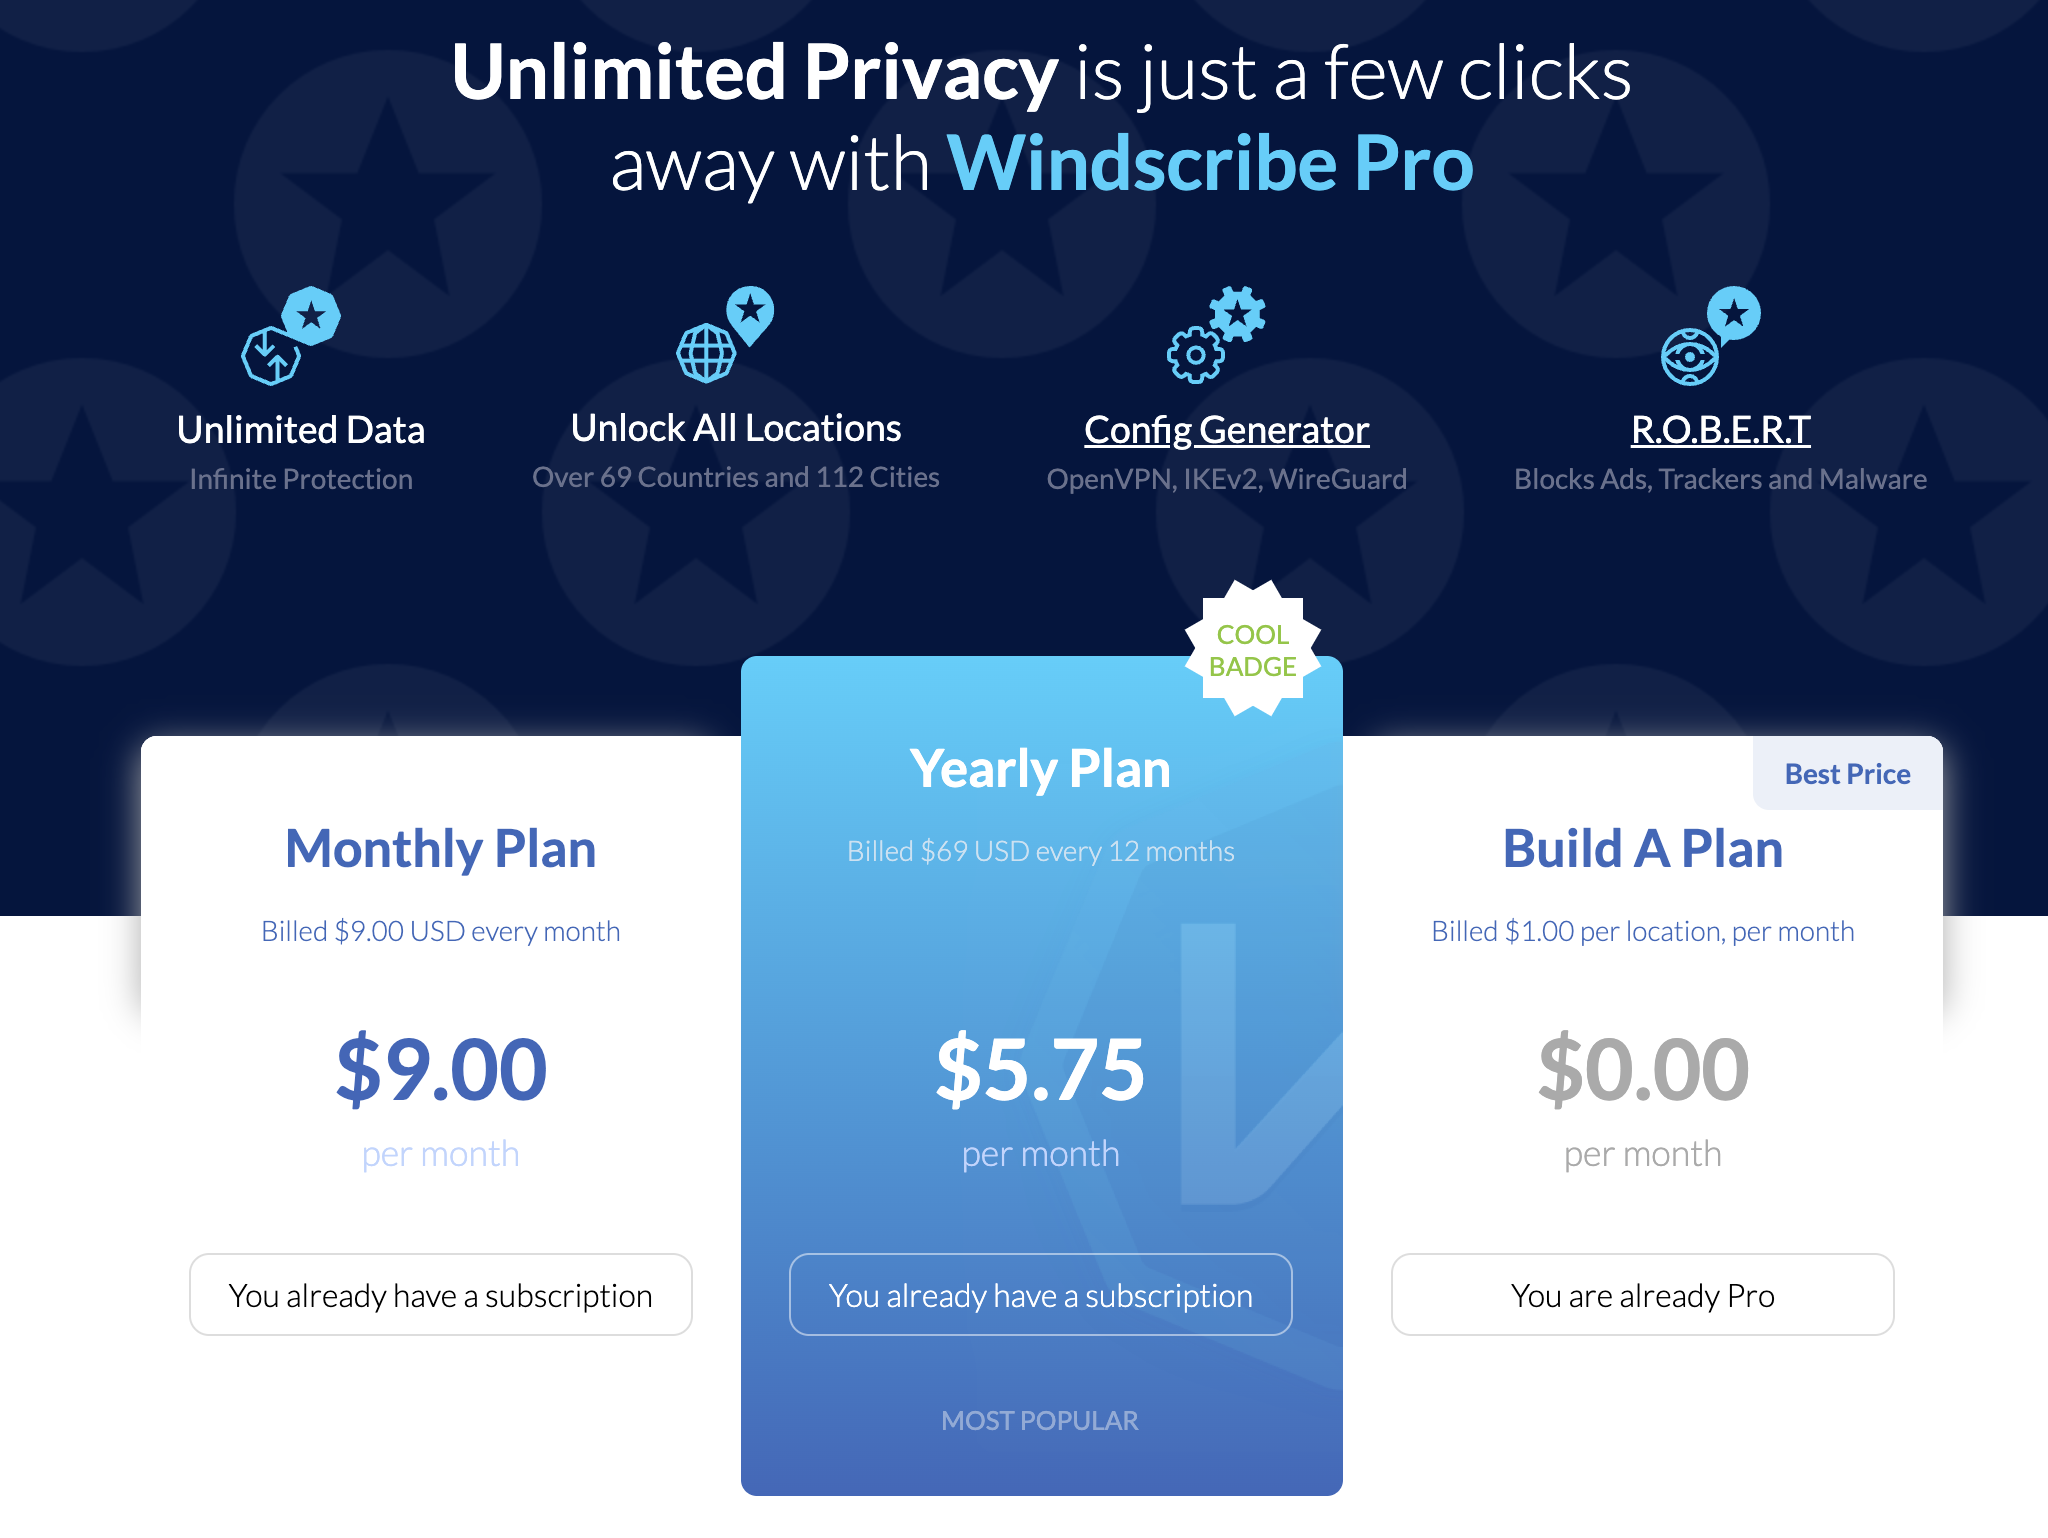
Windscribe has three subscription options (not counting its free plan, which I’ll discuss in a moment). One month of Pro service costs $9.00 — after Mullvad, the second-cheapest monthly subscription to a top-tier VPN. You can also pay $69 for a 12-month Pro subscription, working out to $5.75 per month. Both of these tiers give you the exact same set of Pro features and can be used on unlimited simultaneous devices.
The cost of Windscribe Pro at publication time.
Sam Chapman for Engadget
The third option is to build your own plan. Build-A-Plan is an interesting beast that’s unique to Windscribe. When you choose a custom plan, you must spend at least $3 per month. Gaining access to all the Pro servers in a country costs $1. For each country you add, you get an additional 10GB of data per month on top of the 10GB already included for free.
If you’d rather not budget your data at all, you can pay another $1 for unlimited data, plus 10 custom rules for the R.O.B.E.R.T. content blocker (I’ll untangle the tortured acronym soon). It’s a little convoluted, but wonderfully flexible. You can even change your Build-A-Plan in the middle of the subscription period.
Windscribe also offers shared static IPs for an extra fee. You can add a datacenter IP to any plan for $2 per month or a residential IP (usually better at getting around restrictions) for $8 per month. Team billing is also available through ScribeForce at $3 per seat per month, including a centralized management panel.
The Windscribe free plan
Windscribe isn’t the overall best free VPN — hide.me wins that honor with its more flexible data limit — but it’s close. Free users get access to servers in 10 countries: the US, Canada, the UK, the Netherlands, Norway, France, Germany, Switzerland, Romania and Hong Kong. If you plot that on a map, you’ll see that the Windscribe free plan is most useful in North America and Europe.
Free users start with a data allotment of 2GB per month. The monthly limit rises to 10GB if you sign up with a confirmed email address and 15GB if you post about Windscribe on Twitter/X. That’s enough for casual browsing, but streaming in standard definition takes about 1GB per hour, so you won’t be doing much binge-watching.
On the upside, a free plan gives you access to all Windscribe’s features except for dynamic port forwarding. You can set three R.O.B.E.R.T. rules and use your free account on an infinite number of devices (subject to the usual restrictions about exploiting that for commercial purposes — as Windscribe itself states, no one person has 30 devices that need a VPN).
Windscribe side apps and bundles
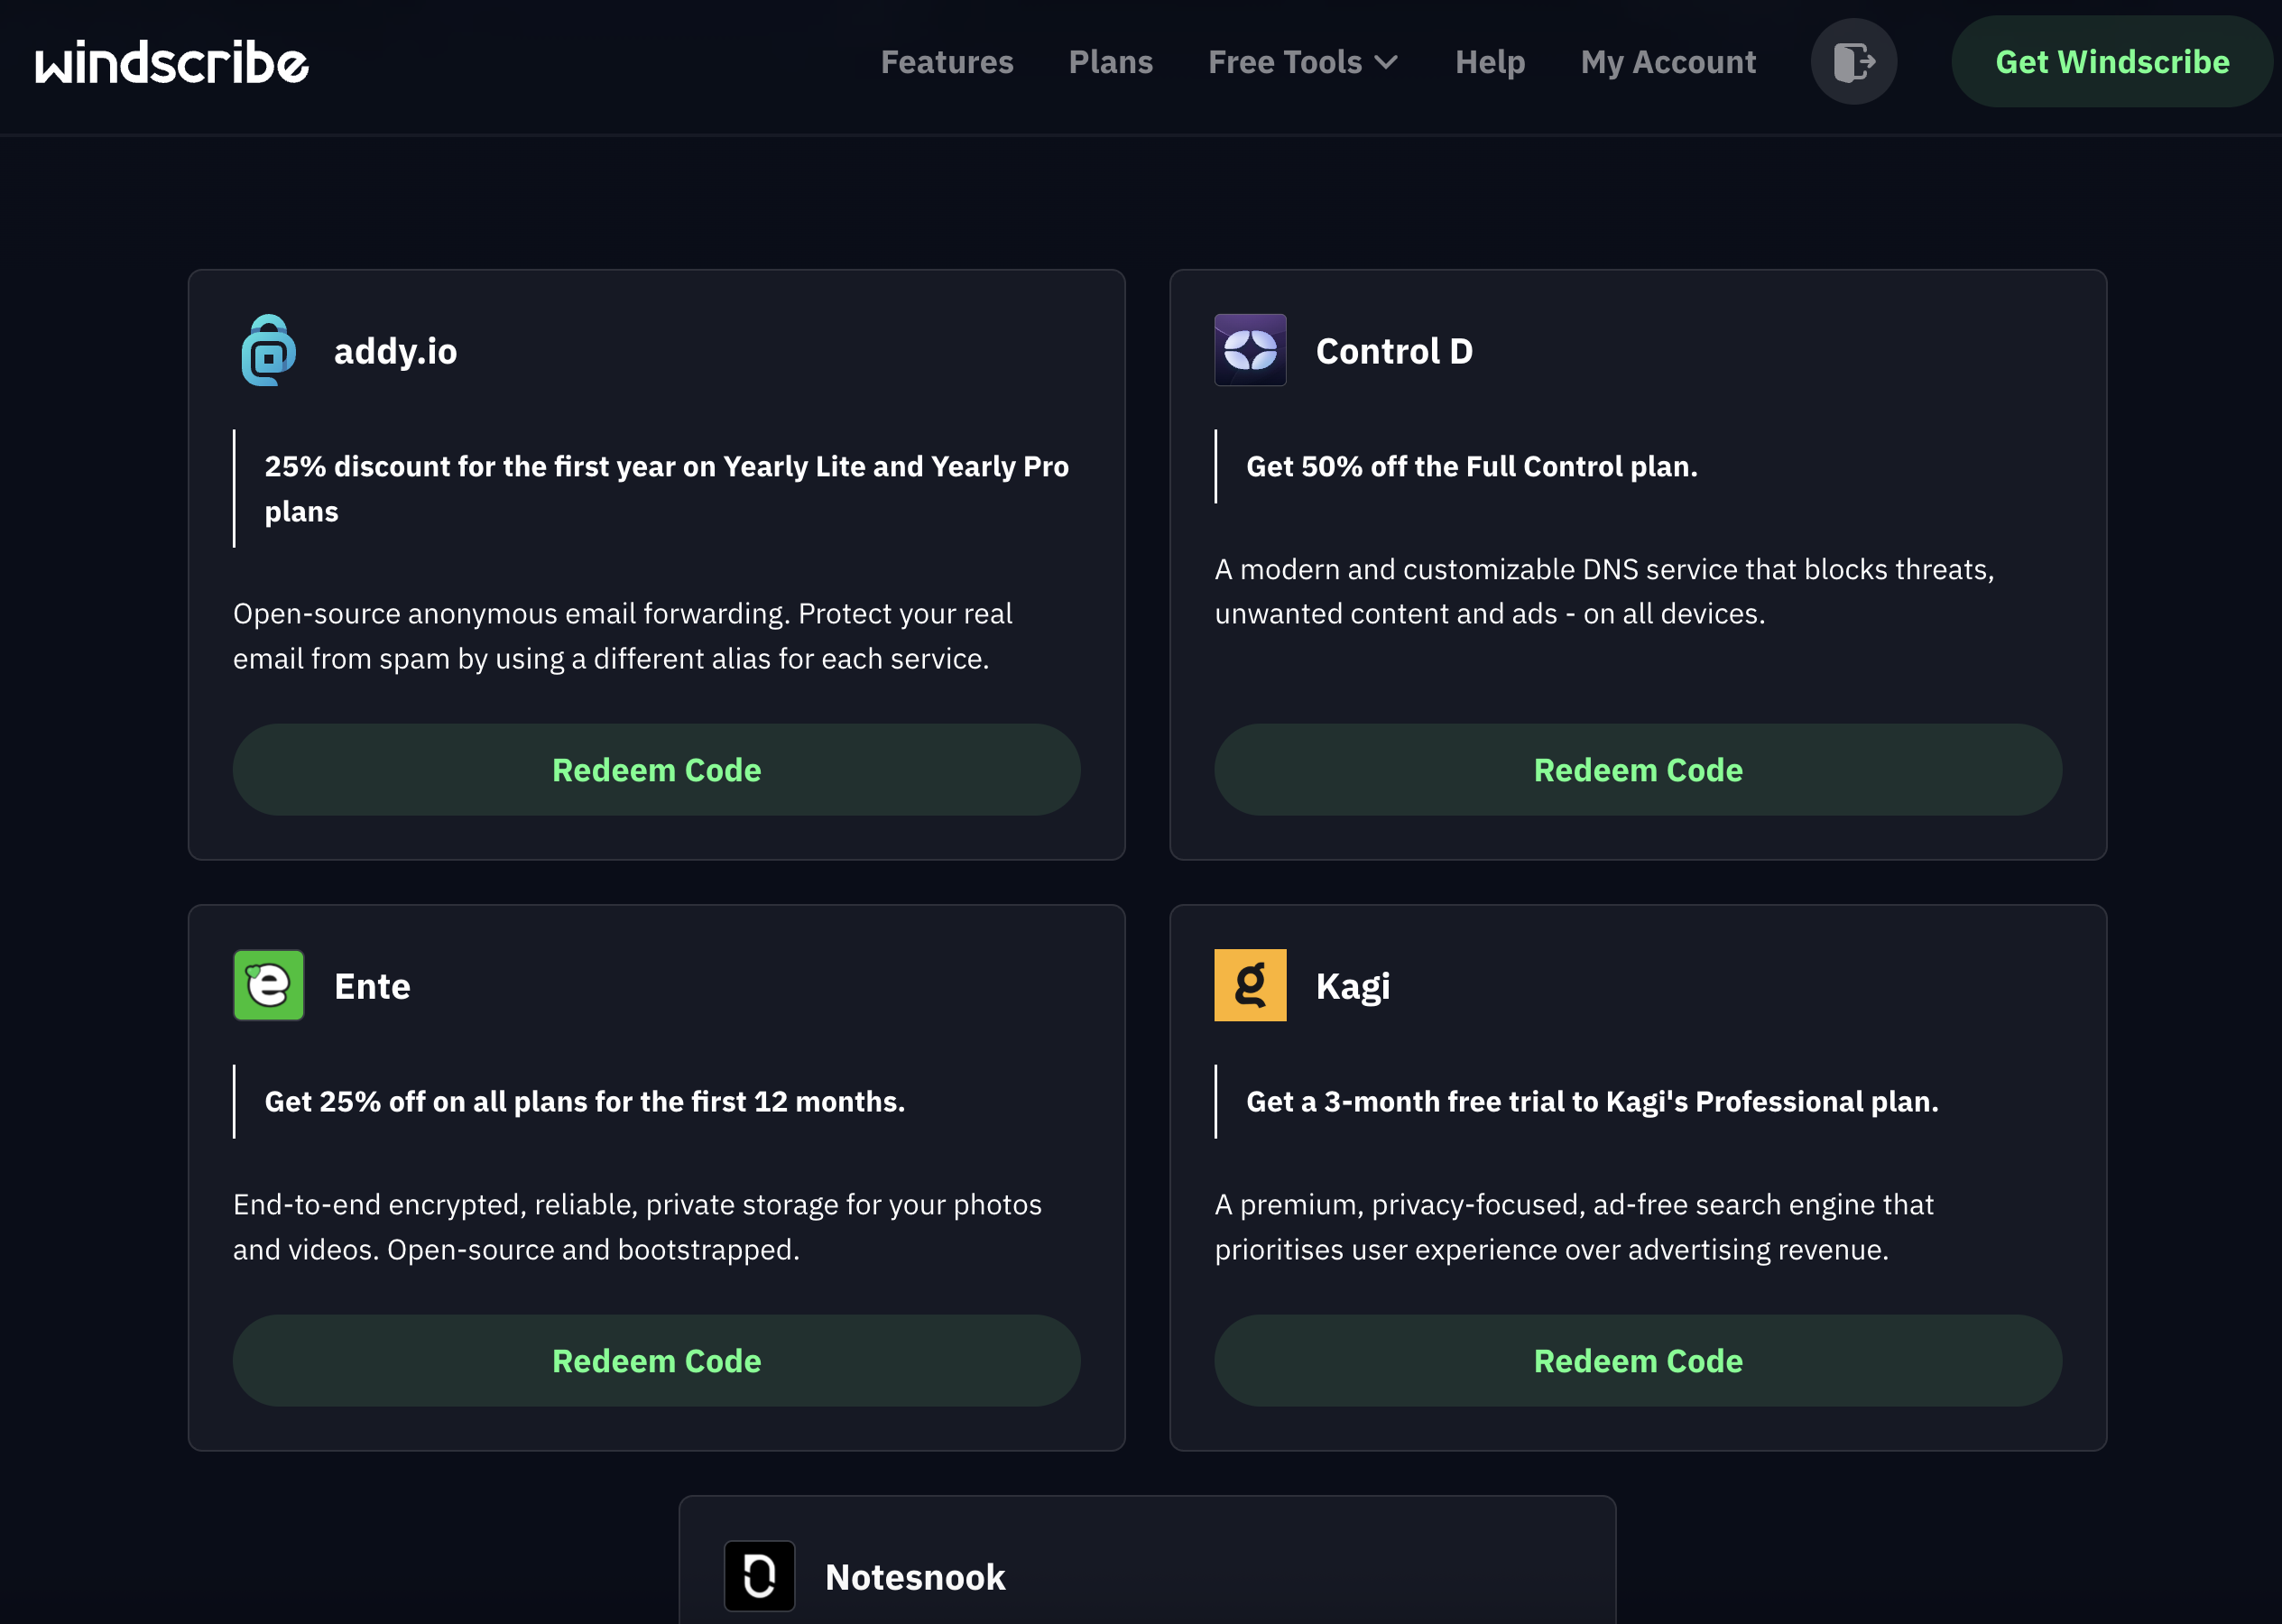
Windscribe doesn’t have any add-ons of its own except for static IP addresses. However, it does offer discount codes for a group of “partners in privacy” that share its business ethics. The coupon codes are available here and don’t require a Windscribe subscription to use.
The five members of Windscribe’s gang.
Sam Chapman for Engadget
There are currently five allies in the gang. Control D offers DNS filtering for organizations to block unwanted websites; the Windscribe coupon gives you 50 percent off. You can get 25 percent off a one-year subscription to addy.io, an open-source email anonymizer, and Ente, an encrypted storage space for photos and videos.
Rounding out the team are Kagi,a private search engine which you can use for three months free with the Windscribe coupon, and Notesnook, an encrypted notes app. Windscribe’s coupon gives you a 10% discount on Notesnook’s yearly plans in perpetuity.
Close-reading Windscribe’s privacy policy
Windscribe’s marketing positions it as serious about user independence, so I came into this section hoping for a privacy policy that backs those words up. An early green flag is that the policy is short, succinct and obviously written to be read by the users themselves. It’s also fantastic that you can sign up without an email address (though you will need one to get the full data allotment on the free plan).
Windscribe gathers information on its website using Piwik, an open-source analytics tool that it manages itself; no third parties are involved. The Windscribe app itself collects no information except for the amount of data used in a month, the time of your last connection and the number of devices you have online at once. When actively connected, it also gives you an anonymized username necessary for the OpenVPN and IKEv2 protocols.
My only quibble is that Windscribe is oddly reluctant to identify which third-party payment processors it uses. The information does exist elsewhere — an article in the knowledgebase states that payments are handled by “trusted third party processors such as PayPal and Stripe,” and another page says that CoinPayments handles cryptocurrency transactions. It’s a small thing, but the rest of the policy is so airtight that it stands out.
Independent privacy audits
Windscribe’s apps are fully open-source (you can find them on Github here). In addition to this general exposure, it’s also undergone three intensive audits from security firms. Leviathan Security looked into its desktop apps in 2021 and its mobile apps in 2022. The auditors made a total of five high-severity recommendations, all of which Windscribe claims to have addressed.
More recently, Windscribe had its entire codebase audited by PacketLabs. The auditors’ June 2024 report found that some of Windscribe’s code was storing more user information than it strictly needed to. Windscribe also claims to have handled this risk. More importantly, PacketLabs found no intentional subversions of Windscribe’s no-logs policy, so its privacy statements can likely be trusted.
Further corroboration of the latter came from a 2025 court case in which Windscribe founder and CEO Yegor Sak was indicted in Greece and charged with a crime committed by a Windscribe user through an IP address in Finland. This case is obviously absurd — like charging the head of GM with a single instance of vehicular manslaughter committed by someone driving a Buick — but Sak was obliged to appear in court anyway.
As Sak writes in the linked post, he could have turned over the logs and shown who actually committed the crime, but he couldn’t since Windscribe doesn’t keep that information. Had there been an alternative to waging an expensive and inconvenient legal campaign in another country, Sak would surely have taken it. The fact that he didn’t is strong proof of Windscribe’s no-logging policy.
Can Windscribe change your virtual location?
Changing your IP address with a VPN can do more than just anonymize your internet activity. A service like Windscribe can give you an IP address associated with a certain country or region, letting you use the internet like you were there. This has applications ranging from the serious (break out of a nationwide firewall to document human rights issues) to the fun (get new titles on streaming platforms without paying for a new subscription).
Netflix is a great tool for testing whether a VPN can change your virtual location. Like most streamers, it tries to block all VPN access to protect the copyrights it holds. Consequently, if a VPN can crack Netflix, it must be serious about keeping its server network fresh to foil any potential blockers.
A successful location change on Netflix using Windscribe.
Sam Chapman for Engadget
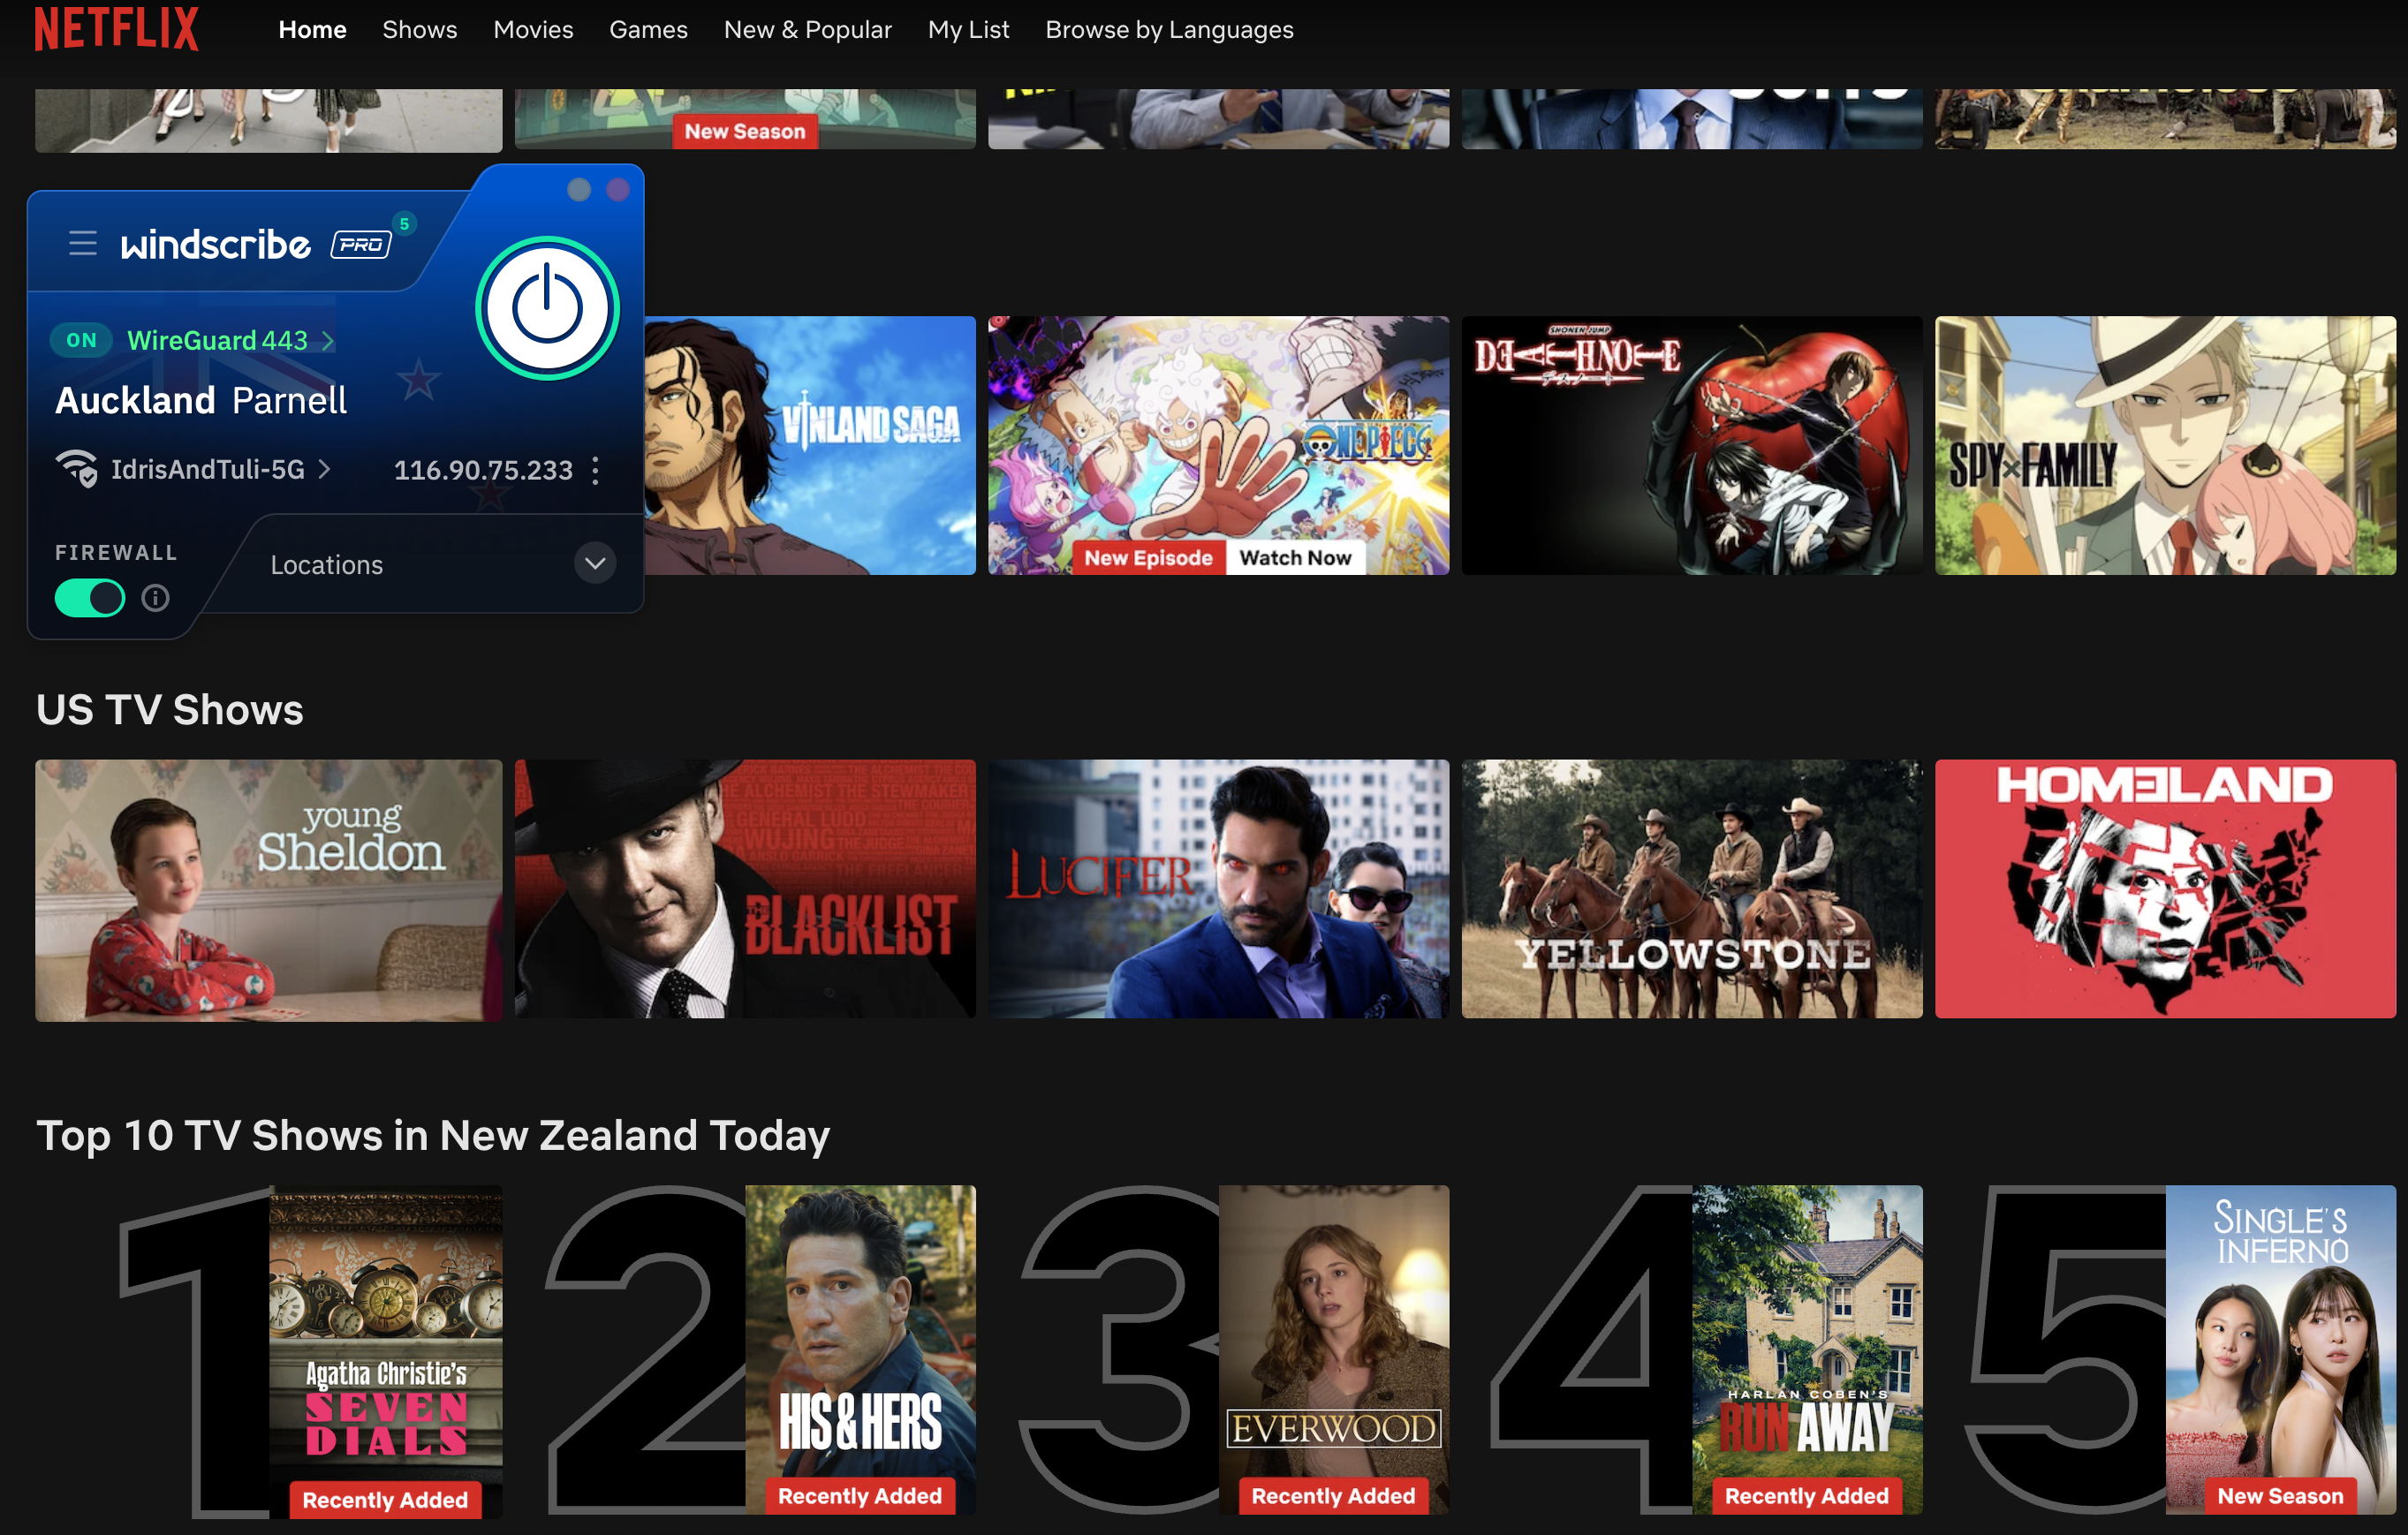
For this test, I tried to access Netflix three times each through five different Windscribe server locations, refreshing the connection to use different servers each time. I looked for successful Netflix access, plus different content to prove my location had actually changed.
Server location
Unblocked Netflix?
Changed content?
Vancouver, Canada
3/3
3/3
Queretaro, Mexico
3/3
3/3
Tokyo, Japan
3/3
3/3
London, UK
3/3
3/3
Auckland, NZ
3/3
3/3
Windscribe got a perfect score. Netflix loaded easily every time, and the content was always localized to the country I chose. With this performance combined with its fairly consistent speeds over long distances, Windscribe makes a nearly perfect streaming VPN. The only downside is that the data limits on the free plan mean you’ll probably have to pay for serious streaming time.
Investigating Windscribe’s server network
Windscribe has 193 server locations in 71 countries, which it insists on listing as “69+” (again, hilarious). Although 193 sounds like a lot, many of them are duplicate locations in the same city. This isn’t necessarily a problem, but for accuracy’s sake, the total number of cities with Windscribe servers is 122.
Region
Countries with servers
Cities with servers
Total server locations
Virtual server locations
North America
6
40
61
0
South America
7
7
9
0
Europe
38
47
75
0
Africa
3
3
5
0
Middle East
2
2
2
0
Asia
12
16
28
1
Oceania
2
6
12
0
Antarctica
1
1
1
1
Total
71
122
193
2 (1 percent)
The bigger story here is Windscribe’s spurning of virtual servers. A virtual server location is physically located in a different region than the one it outwardly displays. For example, a server with an Indian IP address might really be in Singapore. Throughout the entire Windscribe network, only two servers are virtual: one in India and one in Antarctica.
This is both good and bad. On the positive side, the near-total lack of virtual servers means you can be sure of how any server will perform. If it says it’s in Buenos Aires, it’ll run like it’s in Buenos Aires — you won’t be surprised with lagging speeds because it’s really in Miami. This also makes it clear that Windscribe isn’t interested in pumping up its network size for marketing purposes.
Windscribe’s server selection list on the Mac app.
Sam Chapman for Engadget
On the other hand, virtual locations aren’t an inherently bad thing. Windscribe acts as though advertising hype is the only reason any VPN would employ them, but there are real use cases. Virtual servers can be used to place locations inside countries where real servers would risk confiscation by the government, like Russia, India and China. Windscribe chooses instead to place real servers in Russia and India, both of which have data retention laws that directly conflict with its own privacy policy.
Does this mean that using Windscribe’s Russian servers will earn you a midnight visit from the FSB? Probably not. Assuming Windscribe is following its no-logs policy (which appears to be the case), there won’t be any user data on those servers if the government seizes them. But it does mean they’re effectively running illegal data centers which could be raided and shut down at any time. Be aware of this if you depend on Windscribe’s locations in Russia or India.
Extra features of Windscribe
As covered in the UI section, Windscribe has a lot going on in its apps. The Connection tab alone has 13 different features, including two submenus with several options of their own. With this many options, and so many of them highly situational, I won’t be able to cover every nook and cranny without this review getting seriously bloated. I’ve instead chosen some of the most important and illustrative features to give you a clear sense of the whole picture.
Network Options
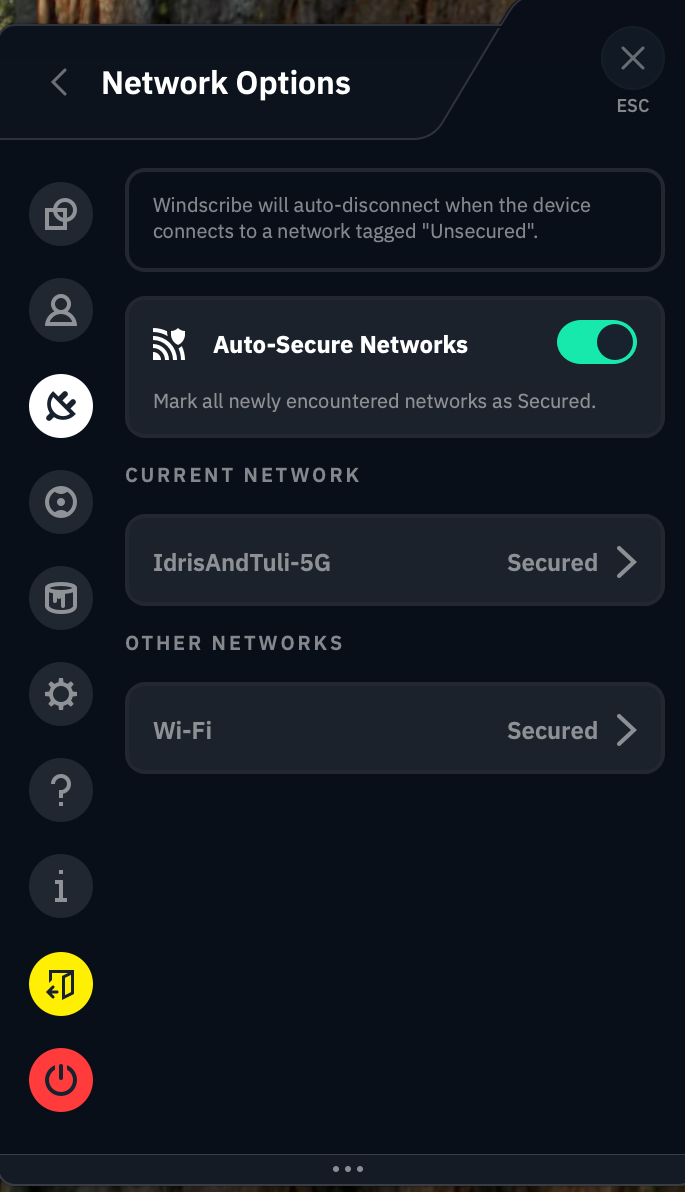
You’ll find this feature at the top of the Connection tab. When you click Network Options, you should see the name of your current Wi-Fi network and all the others your Windscribe account has discovered. This feature lets you control how the VPN reacts to each network it encounters, not unlike CyberGhost’s Smart Rules.
Just switching around a few terms would make this a lot less confusing.
Sam Chapman for Engadget
The app does a remarkably poor job of explaining how this works, so I’ll break it down for you here. When the Auto-Secure Networks switch is turned on, Windscribe will automatically mark each new network as Secured — a word which here means “Windscribe turns on when it encounters the network.”
So far, so good. But if you turn Auto-Secure Networks off, things get weird. Without it, Windscribe tags every network you encounter as Unsecured. Whenever you connect to an Unsecured network, Windscribe immediately disconnects itself. This means it secures all Secured networks and does not secure any Unsecured networks.
It feels backwards until you realize that Windscribe is referring entirely to itself here. “Secured” doesn’t mean that the Wi-Fi network is password-protected or otherwise considered safe, and “Unsecured” doesn’t mean that it’s open to the public without a password. All that matters is whether or not you want Windscribe to activate or deactivate on that network. It’s a useful feature that even lets you choose a VPN protocol for each network, but it would help to bring it more in line with mainstream terminology.
R.O.B.E.R.T.
This mouthful of a feature name allegedly stands for Remote Omnidirectional Badware Eliminating Robotic Tool. This is perhaps the apex of the VPN industry’s unfortunate habit of saddling perfectly good features with word-salad names (yes, I’m aware it’s supposed to be funny).
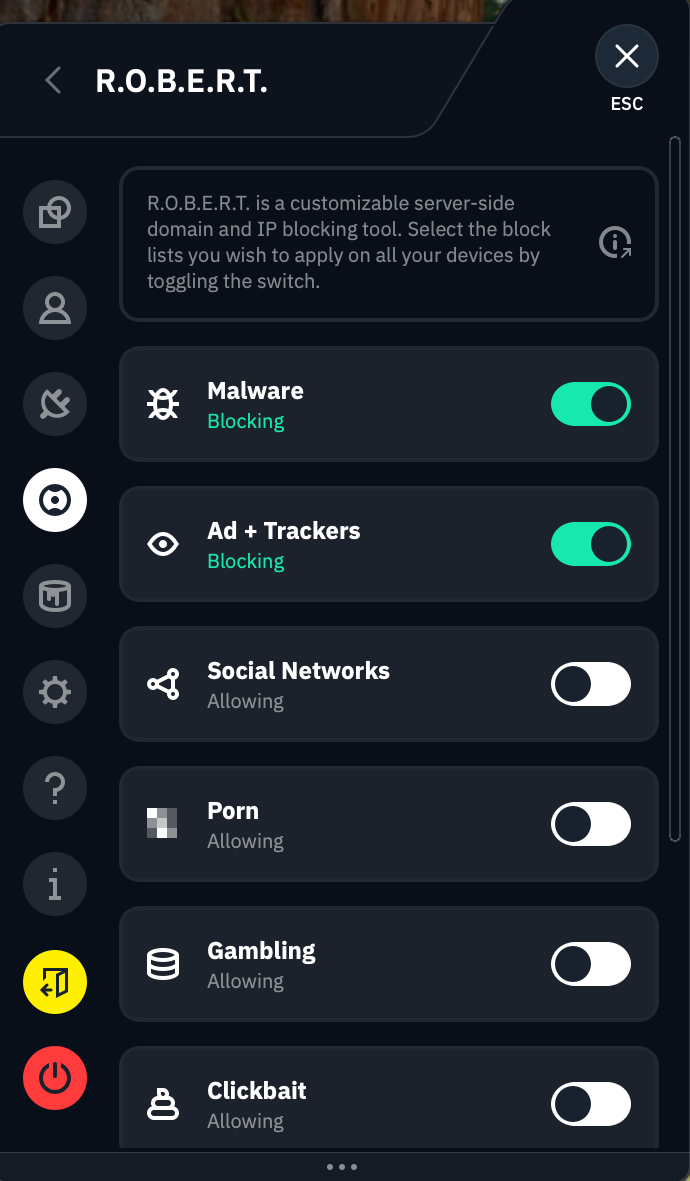
R.O.B.E.R.T. is perhaps the most customizable content blocker on any VPN right now. To start with, it includes eight lists of sites it blocks at the DNS level: Malware, Ad + Trackers, Social Networks, Porn, Gambling, Clickbait, Other VPNs and Crypto. These vary in usefulness, and you can’t determine the contents of each list, but it’s nice to have such a range of choices.
It eliminates all the badware, remotely AND omnidirectionally!
Sam Chapman for Engadget
Where R.O.B.E.R.T really shines, though, is in its browser-based customization dashboard. Each Free user can make three custom rules, and Pro upgrades that to 10. Each custom rule can be used to block a specific website or network or allowlist it from one of the other general blocklists. You can also set it to spoof a domain, though there’s no practical reason to do this (Windscribe’s idea of a “useful” application is making your friends think your post made the front page of Reddit).
Split tunneling
Split tunneling sends some of your internet requests through the VPN tunnel while others go unencrypted as normal. This can be useful if you get worse-than-usual speeds and want to minimize the amount of traffic going through the VPN, or for certain websites that refuse to work with any VPN server.
You can split tunnel on Windscribe’s apps for Windows, Mac and Android. Windows and Android users can split by app or website, while Mac users can only split by website. Windscribe lets you choose whether your split tunnel will be inclusive (only apps and IPs on the list will go through the VPN) or exclusive (the apps and IPs on the list will not go through the VPN). Note that R.O.B.E.R.T. rules apply to the entire system, even excluded apps and domains.
Firewall and Always On VPN
Instead of a kill switch, which it derides as an incomplete solution, Windscribe includes a Firewall feature on desktop and an Always On VPN feature on mobile. The Firewall can be considered a strong kill switch that prevents any internet traffic from going outside the VPN tunnel — something doesn’t have to go wrong for the blocks to activate. Always On VPN on iOS and Android is functionally the same.
A more proactive defense has its advantages, but it would be nice if Windscribe included the weak kill switch option. Kill switches and firewalls can be overactive, and sometimes, you don’t want the strongest level of security.
Circumvent Censorship
This feature is designed to let you access Windscribe on networks that don’t want you to use a VPN, from school and work systems to entire censorious countries like China. Windscribe isn’t forthcoming about how it works, but it’s probably a deep-packet obfuscation that makes VPN traffic look like regular traffic. I didn’t have time to pop over to China and test Circumvent Censorship, but I’m glad it exists.
Windscribe customer support options
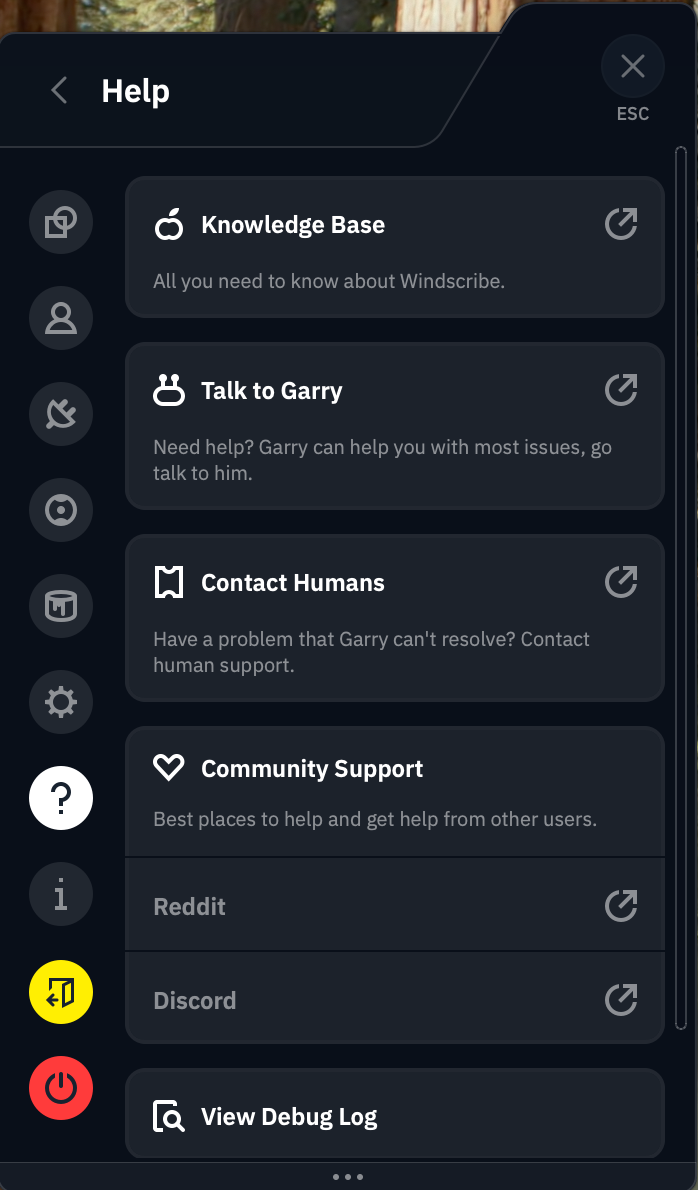
Clicking the question mark tab on the Windscribe app shows you the full list of support options. You can peruse the knowledgebase, ask their chatbot Garry, talk directly to a human or check out their user communities on Reddit and Discord.
Most of these lead back to Garry.
Sam Chapman for Engadget
I started with the written FAQs. At the top of the knowledgebase, there’s a row of buttons you can click to see only articles relating to a particular operating system. This is a good idea in theory, but it’s not implemented very well — there’s no visible tagging system, so we can’t see how it’s deciding which articles to filter.
The search bar is much more likely to get you where you need to go. It works instantaneously and always turns up relevant articles, though it’s weirdly insistent on showing exactly 10 results. I have few complaints about articles themselves, which are written in a way any user should find useful (give or take yet more attempted humor).
I tested the chatbot, Garry, by asking it about the mysterious Advanced Parameters tab of the Windscribe app. It explained each feature on that tab (none of which should be touched except by users with technical knowledge) in a spiel that was clearly pre-written but nonetheless useful. Garry was launched in 2018, when IBM Watson was the biggest thing in AI, and recently revamped into “Garry 2.0” — whether this is based on OpenAI or another platform is anyone’s guess at the moment.
Live support
Windscribe appears to handle all of its own support, without outsourcing to Zendesk or a similar third party. If you decide not to go through Garry, Windscribe does have the option of connecting directly to a human. However, the Contact Humans option on the app sends you directly back to Garry. It’s eventually possible to get Garry to connect you to a real person, but that doesn’t excuse Windscribe building an outright lie into its app.
The Contact Support button on the knowledgebase, which I expected to lead to a ticket submission, also sends you straight to Garry. Windscribe really, really wants you to use Garry, in case that wasn’t clear. You might have a better time going straight to the Windscribe Discord server or the r/Windscribe subreddit, both of which are linked to in the app.
Windscribe background check
Windscribe eschews a lot of the things we’ve come to expect from a VPN provider. It doesn’t pay for ads anywhere. It has no affiliate relationships with news sites. The only thing resembling a Windscribe ad campaign is the free-plan data reward for Xeeting about it. It doesn’t even have any venture capital investors — it’s completely self-funded and self-hosted.
As a jaded and cynical reviewer who was already annoyed by Windscribe’s memelord attitude, I was prepared to sniff out any hypocrisy in its background, which makes it all the more impressive that I didn’t find any. Since its founding in Canada in 2016, Windscribe has never once been involved in any public doings that contradict its statements of ethics. It’s even given free unlimited VPN access to every journalist working in Ukraine.
The only thing I could find resembling a controversy was an incident in July 2021 when Ukrainian police confiscated two servers that weren’t fully encrypted. Although this would only have posed a risk to users running a customized connection profile under very specific conditions, it was still a lapse. Windscribe responded appropriately in my view, ending the legacy OpenVPN implementation that caused the problem.
Canadian headquarters
Windscribe is based in Canada, which is one of the Five Eyes nations (along with the U.S., the U.K., Australia and New Zealand). This sounds scary, but it’s not actually an issue, as Yegor Sak himself points out in a blog post I reference frequently.
Five Eyes is not an organization, but an agreement between five allied countries to share necessary intelligence with each other. This can absolutely be misused. If the U.S. government wants to spy on someone without running into the 4th Amendment, it can ask the Brits to spy on that person instead and tell them what they find, knowing the Constitution can’t determine what other countries do to our citizens.
As bad as that is for our civil liberties, it doesn’t actually change anything where VPNs are concerned. If a VPN isn’t logging user data, there shouldn’t be anything for any of the Five Eyes (or Nine Eyes or Fourteen Eyes) nations to find. And if it is keeping logs, you shouldn’t be using it no matter where its headquarters are.
Final verdict
You might wonder, at this point, why my distaste for Windscribe’s tryhard sense of humor has featured so prominently in this review. One reason is that I had to read a lot of it this week, and you must suffer as I have suffered. But it also makes Windscribe look very good by implication. Having no patience for the discount-4chan act that pervades Windscribe’s brand, I was primed to dislike the VPN itself — and I simply couldn’t.
This is not to say I had no problems at all with Windscribe. Its physical servers in Russia are difficult to trust. Its help options lean way too heavily on Garry the chatbot. Its app design and UI writing are significant faults. The free plan doesn’t give you enough data for streaming.
Having said all that, though, Windscribe does everything else right. It changes virtual locations and unblocks Netflix without breaking a sweat. Its servers keep latencies low, and download speeds remain solid across the world. The apps may look bad, but they never break down. Some features, like R.O.B.E.R.T. and Auto-Secure, are both useful to everybody and deeply customizable for power users.
Windscribe may be best for privacy nerds who know how all its doohickeys work, but it’s a VPN I recommend for everybody. In a world of predatory software, it’s a relief to use an app that’s unabashedly on the customer’s side.
This article originally appeared on Engadget at https://www.engadget.com/cybersecurity/vpn/windscribe-review-despite-the-annoyances-it-has-the-right-idea-120000837.html?src=rss
Amazon has confirmed that it’s letting go of 16,000 workers and employees across its organization. In an announcement by company SVP Beth Galetti, she explained that Amazon was going through organizational changes to reduce layers and remove bureaucracy. Affected employees in the US will be given 90 days to look for another internal role and will receive severance pay if they do not find any. Galetti also said that Amazon doesn’t have plans to announce “broad reductions every few months” but admitted that the company could “make adjustments as appropriate.”
News about the layoffs was leaked in an email mistakenly sent out early to workers, along with a calendar invitation for a meeting dubbed internally as “Project Dawn.” In the email seen by Bloomberg and the BBC, Amazon Web Services Senior Vice President Colleen Aubrey told workers that their “impacted colleagues” from the US, Canada and Costa Rica had already been notified. “Changes like this are hard on everyone. These decisions are difficult and made thoughtfully as we position our organization and AWS for future success,” Aubrey reportedly wrote in the email.
Amazon eliminated 14,000 roles back in October 2025 across its games, logistics, payment and cloud computing divisions, with the availability of AI technologies being one of the main reasons for the layoffs. “This generation of AI is the most transformative technology we’ve seen since the Internet, and it’s enabling companies to innovate much faster than ever before,” Amazon said in its announcement back then. This new round of layoffs is just a continuation of the previous one, as Amazon was reportedly looking to let 30,000 people go from the start.
The announcement comes shortly after Amazon revealed that it was shutting down its remaining Amazon Go and Amazon Fresh physical stores and will focus on grocery deliveries instead. To note, Amazon’s year-over-year net sales grew by 13 percent in the third quarter of 2025 alone. Its net income increased to $21.2 billion compared to the $15.3 billion it posted in the third quarter of 2024.
This article originally appeared on Engadget at https://www.engadget.com/big-tech/amazons-latest-round-of-layoffs-will-affect-16000-workers-120000702.html?src=rss
Amazon announced on Wednesday that it is eliminating approximately 16,000 roles across the company as part of organizational changes that began in October 2025 and are only now being finalized by certain teams. Senior Vice President Beth Galetti shared the news in a memo to employees, framing the reductions as an effort to reduce layers, increase ownership, and remove bureaucracy. The memo follows another memo that the company accidentally sent to employees.
An anonymous reader quotes a report from Universe Today: There’s a bright side to every situation. In 2032, the Moon itself might have a particularly bright side if it is blasted by a 60-meter-wide asteroid. The chances of such an event are still relatively small (only around 4%), but non-negligible. And scientists are starting to prepare both for the bad (massive risks to satellites and huge meteors raining down on a large portion of the planet) and the good (a once in a lifetime chance to study the geology, seismology, and chemical makeup of our nearest neighbor). A new paper from Yifan He of Tsinghua University and co-authors, released in pre-print form on arXiv, looks at the bright side of all of the potential interesting science we can do if a collision does, indeed, happen. If Asteroid 2024 YR4 were to hit the Moon, researchers would be able to watch a large lunar impact unfold in real time and collect data on extreme collisions that usually exist only in computer models. Telescopes could follow how a newly formed crater and its pool of molten rock cool and solidify, while the resulting moonquake would offer a clearer picture of its internal structure via the seismic waves it sends through the Moon.
Furthermore, researchers could compare the fresh crater to older ones to improve our understanding of the Moon’s long history of impacts. Debris blasted off the surface could even deliver small lunar samples to Earth.
Altogether, it would be a once-in-a-generation chance to learn more about how the Moon/rocky worlds respond to powerful impacts.
alternative_right shares a report from Phys.org: New findings from NASA’s Perseverance rover have revealed evidence of wave-formed beaches and rocks altered by subsurface water in a Martian crater that once held a vast lake — considerably expanding the timeline for potential habitability at this ancient site. In an international study led by Imperial College London, researchers uncovered that the so-called ‘Margin unit’ in Mars’s Jezero crater preserves evidence of extensive underground interactions between rock and water, as well as the first definitive traces of an ancient shoreline.
These are compelling indicators that habitable, surface water conditions persisted in the crater (home to a large lake around 3.5 billion years ago) further back in time than previously thought. “Shorelines are habitable environments on Earth, and the carbonate minerals that form here can naturally seal in and preserve information about the ancient environment,” said lead author Alex Jones, a Ph.D. researcher in the Department of Earth Science and Engineering (ESE) at Imperial. The findings have been published in the Journal of Geophysical Research: Planets.
Amazon appears to have prematurely acknowledged layoffs inside AWS after an internal email referencing “organizational changes” and “impacted colleagues” was mistakenly sent to cloud employees. CNBC reports: “Changes like this are hard on everyone,” Colleen Aubrey, senior vice president of applied AI solutions at Amazon Web Services, wrote in an email viewed by CNBC. “These decisions are difficult and are made thoughtfully as we position our organization and AWS for future success.” The note also references a post from Amazon’s HR boss Beth Galetti and said the company notified “impacted colleagues in our organization.” The subject of the email mentions “Project Dawn,” and the email says it was “canceled,” possibly indicating it was recalled by the sender after the fact. It’s unclear what Project Dawn refers to.
The job cuts come after Amazon announced in October that it would lay off 14,000 corporate employees. At the time, the company indicated the cuts would continue in 2026 as it found “additional places we can remove layers.” Amazon CEO Andy Jassy said the layoffs were meant to reduce management layers and bureaucracy inside the company. He also predicted last June that efficiency gains from AI would shrink Amazon’s corporate staff in the coming years.
An anonymous reader quotes a report from Science.org: Some 10,109 doctoral-trained experts in science and related fields left their jobs last year as President Donald Trump dramatically shrank the overall federal workforce. That exodus was only 3% of the 335,192 federal workers who exited last year but represents 14% of the total number of Ph.D.s in science, technology, engineering, and math (STEM) or health fields employed at the end of 2024 as then-President Joe Biden prepared to leave office. The numbers come from employment data posted earlier this month by the White House Office of Personnel Management (OPM). At 14 research agencies Science examined in detail, departures outnumbered new hires last year by a ratio of 11 to one, resulting in a net loss of 4224 STEM Ph.D.s. The graphs that follow show the impact is particularly striking at such scientist-rich agencies as the National Science Foundation (NSF). But across the government, these departing Ph.D.s took with them a wealth of subject matter expertise and knowledge about how the agencies operate.
[…] Science’s analysis found that reductions in force, or RIFs, accounted for relatively few departures in 2025. Only at the Centers for Disease Control and Prevention, where 16% of the 519 STEM Ph.D.s who left last year got pink RIF slips, did the percentage exceed 6%, and some agencies reported no STEM Ph.D. RIFs in 2025. At most agencies, the most common reasons for departures were retirements and quitting. Although OPM classifies many of these as voluntary, outside forces including the fear of being fired, the lure of buyout offers, or a profound disagreement with Trump policies, likely influenced many decisions to leave. Many Ph.D.s departed because their position was terminated.
Apple quietly released its first update to iOS 12 since 2023 to keep iMessage, FaceTime, and device activation working on older hardware through January 2027. The update applies to legacy devices like the iPhone 5S, iPhone 6/6 Plus, and 2013-era iPads. Macworld reports: The update appears to be related to a specific issue. According to Apple’s “About iOS 12 Updates” page, iOS 12.5.78 “extends the certificate required by features such as iMessage, FaceTime, and device activation to continue working after January 2027.” Meanwhile, the iOS 16 update says it “provides important bug fixes and is recommended for all users.”
When iOS 13 arrived, it dropped compatibility for the iPhone 5S, iPhone 6, and iPhone 6 Plus, as well as the 2013 iPad Air and iPad Mini 3, so users of those phones should specifically take note. To update to the latest version, head over to the Settings app, then General and Software Update, and follow the instructions. Further reading: Apple Launches AirTag 2 With Improved Range, Louder Speaker
Scientists have released DinoTracker, a free AI-powered app that identifies dinosaur footprints by analyzing shape patterns rather than relying on potentially flawed historical labels. “When we find a dinosaur footprint, we try to do the Cinderella thing and find the foot that matches the slipper,” said Prof Steve Brusatte, a co-author of the work. “But it’s not so simple, because the shape of a dinosaur footprint depends not only on the shape of the dinosaur’s foot but also the type of sand or mud it was walking through, and the motion of its foot.” The Guardian reports: […] Brusatte, [Dr Gregor Hartmann, the first author of the new research from Helmholtz-Zentrum in Germany] and colleagues fed their AI system with 2,000 unlabelled footprint silhouettes. The system then determined how similar or different the imprints were from each other by analysing a range of features it identified as meaningful. The researchers discovered these eight features reflected variations in the imprints’ shapes, such as the spread of the toes, amount of ground contact and heel position. The team have turned the system into a free app called DinoTracker that allows users to upload the silhouette of a footprint, explore the seven other footprints most similar to it and manipulate the footprint to see how varying the eight features can affect which other footprints are deemed most similar. Hartmann said that at present experts had to double check if factors such as the material the footprints were made in, and their age, matched the scientific hypothesis, but the system clustered prints with those expected from classifications made by human experts about 90% of the time. The findings have been published in the journal PNAS.
A data breach at SoundCloud exposed information tied to 29.8 million user accounts, according to Have I Been Pwned. While SoundCloud says no passwords or financial data were accessed, attackers mapped email addresses to public profile data and later attempted extortion. BleepingComputer reports: The company confirmed the breach on December 15, following widespread reports from users who were unable to access SoundCloud and saw 403 “Forbidden” errors when connecting via VPN. SoundCloud told BleepingComputer at the time that it had activated its incident response procedures after detecting unauthorized activity involving an ancillary service dashboard. “We understand that a purported threat actor group accessed certain limited data that we hold,” SoundCloud said. “We have completed an investigation into the data that was impacted, and no sensitive data (such as financial or password data) has been accessed. The data involved consisted only of email addresses and information already visible on public SoundCloud profiles.”
While SoundCloud didn’t provide further details regarding the incident, BleepingComputer learned that the breach affected 20% of all SoundCloud users, roughly 28 million accounts based on publicly reported user figures (SoundCloud later published a security notice confirming the information provided by BleepingComputer’s sources). After the breach, BleepingComputer also learned that the ShinyHunters extortion gang was responsible for the attack, with sources saying that the threat group was also attempting to extort SoundCloud. This was confirmed by SoundCloud in a January 15 update, which said the threat actors had “made demands and deployed email flooding tactics to harass users, employees, and partners.”
Nearly half of the databases that public health officials at the Centers for Disease Control and Prevention were updating on a monthly basis have been frozen without notice or explanation, according to a study published in the Annals of Internal Medicine.
The study—led by Janet Freilich, a law expert at Boston University, and Jeremy Jacobs, a medical professor at Vanderbilt University—examined the status of all CDC databases, finding a total of 82 that had, as of early 2025, been receiving updates at least monthly. But, of those 82, only 44 were still being regularly updated as of October 2025, with 38 (46 percent) having their updates paused without public notice or explanation.
Examining the databases’ content, it appeared that vaccination data was most affected by the stealth data freezes. Of the 38 outdated databases, 33 (87 percent) included data related to vaccination. In contrast, none of the 44 still-updated databases relate to vaccination. Other frozen databases included data on infectious disease burden, such as data on hospitalizations from respiratory syncytial virus (RSV).
However, experts say that TikTok users’ censorship fears are justified, whether the bugs are to blame or not.
Ioana Literat, an associate professor of technology, media, and learning at Teachers College, Columbia University, has studied TikTok’s politics since the app first shot to popularity in the US in 2018. She told Ars that “users’ fears are absolutely justified” and explained why the “bugs” explanation is “insufficient.”
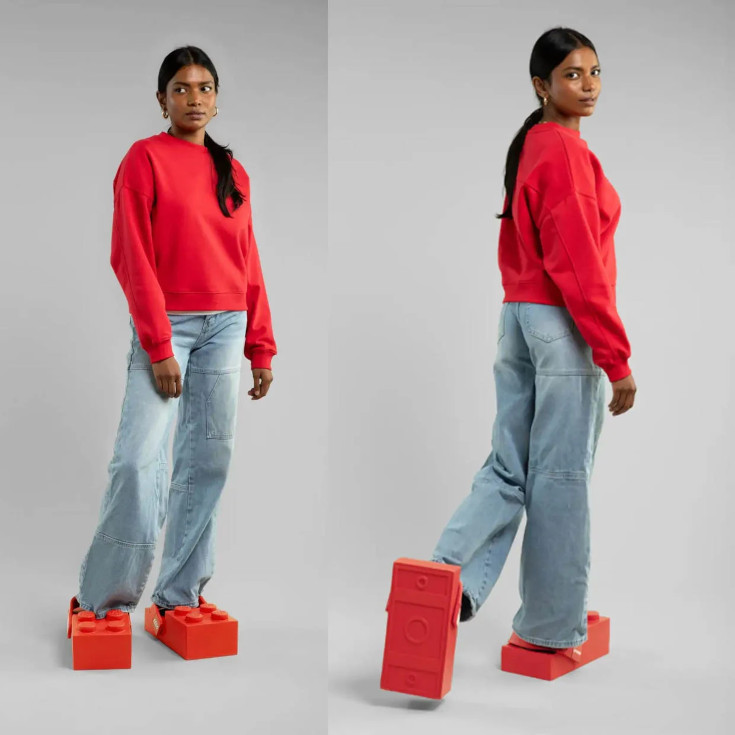
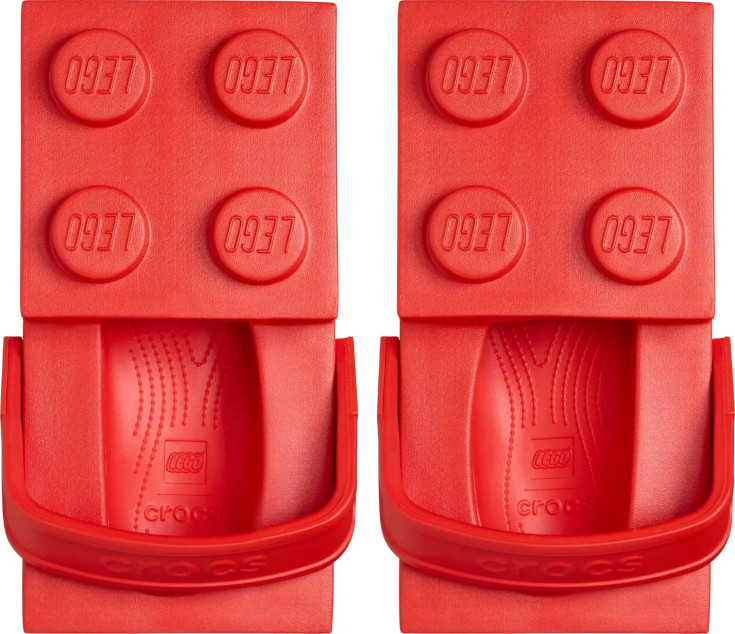
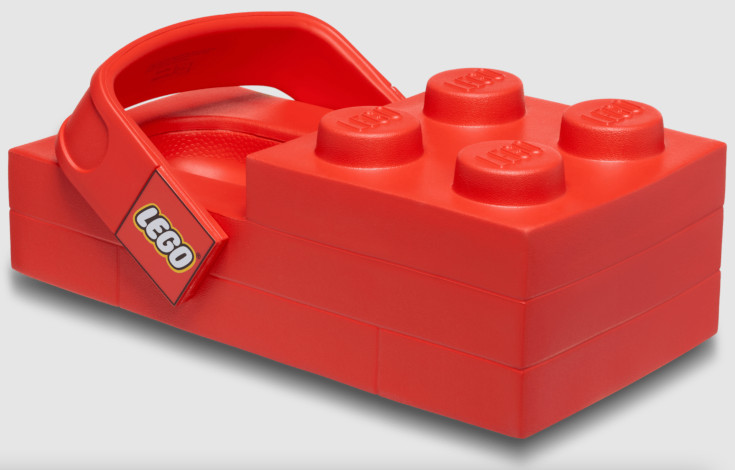
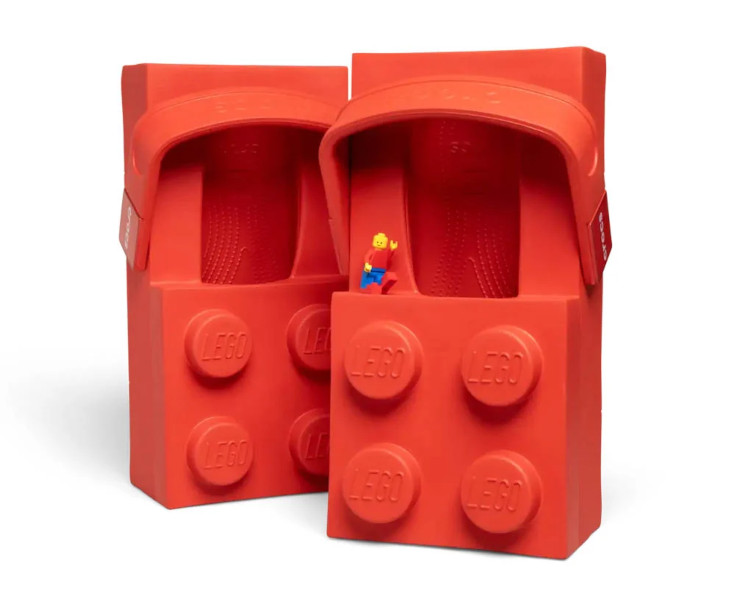
Because it was only a matter of time before some LEGO exec made a joke during a meeting about stepping on LEGO bricks and a lightbulb went off in their head and they got on the horn to Crocs to make it happen, these are the LEGO x Crocs Brick Clogs. They’re Crocs that look like the lovechild of studded LEGO plates and clown shoes (what I wouldn’t have given to be a fly on the window of that clown car!). Available in red only in men’s sizes 5 – 13 (women’s 7 – 15), they’ll cost $150 when they’re released February 16th. Great, just in time for not Valentine’s Day. Now I’ll have to remember to get something else. Or, more likely, forget to get something else. The doghouse: I live in it. “Do you even have a girlfriend?” Not that I’ve seen since two Valentine’s Days ago.
Amazon has agreed to pay $309 million and provide additional remedies in a class-action settlement over claims that customers were wrongly denied refunds after returning items. Plaintiffs say (PDF) the deal delivers over $1 billion in total value, including more than $600 million in refunds and operational changes. Reuters reports: Amazon denied any wrongdoing in agreeing to the settlement. “Following an internal review in 2025, we identified a small subset of returns where we issued a refund without the payment completing, or where we could not verify that the correct item had been sent back to us, so no refund had been issued,” an Amazon spokesperson said, adding that the company had taken steps to resolve the issue.
The lawsuit, filed in 2023, said Amazon caused “substantial unjustified monetary losses” for consumers who in some instances properly returned an item but were still charged for it. In a court filing, Amazon said customers accepted the terms of the company’s return policies, including the possibility they would be recharged for failing to return the product within a specified time frame. The proposed settlement class covers U.S. purchasers of goods on Amazon from September 2017 who allegedly did not receive timely or correct refunds, or who were later charged despite returning items. Class members are expected to recover the full amount of any incorrectly denied refund or retrocharge, plus interest, the plaintiffs told the court.
An anonymous reader quotes a report from Ars Technica: This week, the first high-profile lawsuit — considered a “bellwether” case that could set meaningful precedent in the hundreds of other complaints — goes to trial. That lawsuit documents the case of a 19-year-old, K.G.M, who hopes the jury will agree that Meta and YouTube caused psychological harm by designing features like infinite scroll and autoplay to push her down a path that she alleged triggered depression, anxiety, self-harm, and suicidality. TikTok and Snapchat were also targeted by the lawsuit, but both have settled. The Snapchat settlement came last week, while TikTok settled on Tuesday just hours before the trial started, Bloomberg reported. For now, YouTube and Meta remain in the fight. K.G.M. allegedly started watching YouTube when she was 6 years old and joined Instagram by age 11. She’s fighting to claim untold damages — including potentially punitive damages — to help her family recoup losses from her pain and suffering and to punish social media companies and deter them from promoting harmful features to kids. She also wants the court to require prominent safety warnings on platforms to help parents be aware of the risks. […]
To win, K.G.M.’s lawyers will need to “parcel out” how much harm is attributed to each platform, due to design features, not the content that was targeted to K.G.M., Clay Calvert, a technology policy expert and senior fellow at a think tank called the American Enterprise Institute, wrote. Internet law expert Eric Goldman told The Washington Post that detailing those harms will likely be K.G.M.’s biggest struggle, since social media addiction has yet to be legally recognized, and tracing who caused what harms may not be straightforward. However, Matthew Bergman, founder of the Social Media Victims Law Center and one of K.G.M.’s lawyers, told the Post that K.G.M. is prepared to put up this fight. “She is going to be able to explain in a very real sense what social media did to her over the course of her life and how in so many ways it robbed her of her childhood and her adolescence,” Bergman said.
The research is unclear on whether social media is harmful for kids or whether social media addiction exists, Tamar Mendelson, a professor at Johns Hopkins Bloomberg School of Public Health, told the Post. And so far, research only shows a correlation between Internet use and mental health, Mendelson noted, which could doom K.G.M.’s case and others.’ However, social media companies’ internal research might concern a jury, Bergman told the Post. On Monday, the Tech Oversight Project, a nonprofit working to rein in Big Tech, published a report analyzing recently unsealed documents in K.G.M.’s case that supposedly provide “smoking-gun evidence” that platforms “purposefully designed their social media products to addict children and teens with no regard for known harms to their wellbeing” — while putting increased engagement from young users at the center of their business models. Most of the unsealed documents came from Meta. An internal email shows Mark Zuckerberg decided Meta’s top strategic priority was getting teens “locked in” to Meta’s family of apps. Another damning document discusses allowing “tweens” to use a private mode inspired by fake Instagram accounts (“finstas”). The same document includes an admission that internal data showed Facebook use correlated with lower well-being.
Internal communications showed Meta seemingly bragging that “teens can’t switch off from Instagram even if they want to” and an employee declaring, “oh my gosh yall IG is a drug,” likening all social media platforms to “pushers.”
We may earn a commission from links on this page. Deal pricing and availability subject to change after time of publication.
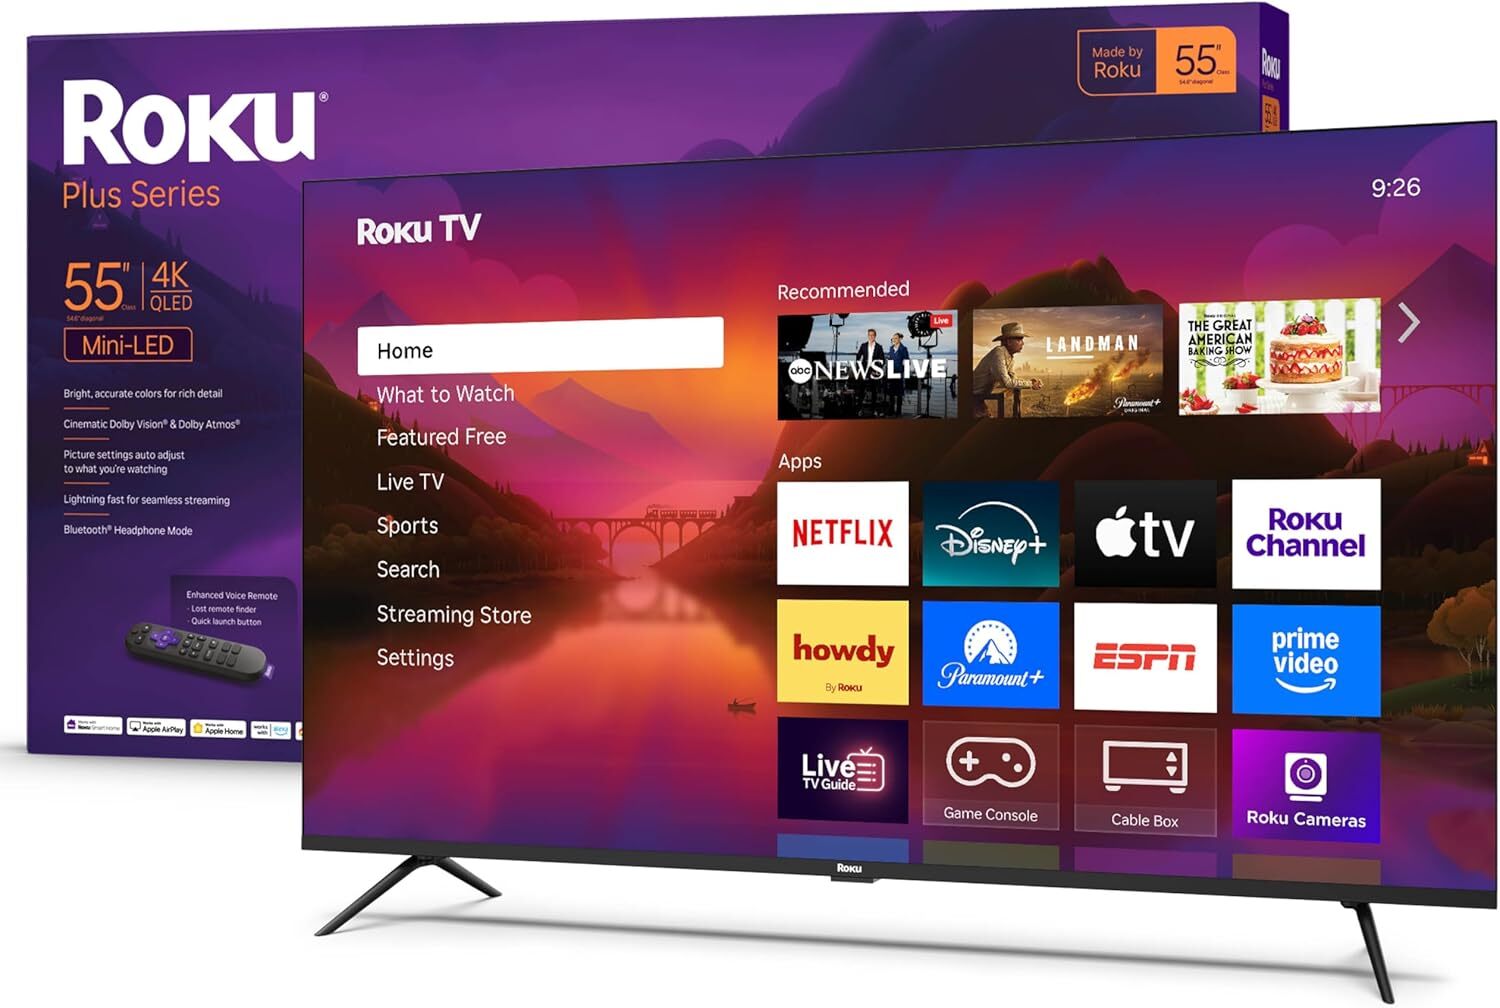
As far as smart TVs go, the Roku interface is one of the easiest to use, and with a variety of different lines, it’s also easy to find one that fits your budget. The Plus Series is the brand’s first attempt at making its own television, and it’s a reliable mid-range smart TV that gives users a plug-and-play experience (no Roku stick or box required), solid picture quality, and fast streaming for the price. Right now, the 55″ 2025 Roku Smart TV Plus Series is 30% off at a record-low $348, down from $499.99.
This model is an upgrade over the Select Series and features a 4K QLED panel with a wide color gamut and a mini-LED backlight. It also supports HDR-10, including Dolby Vision. Colors are vibrant and detailed compared to similarly priced budget TVs, though according to this PCMag review, greens can occasionally look oversaturated. It reaches a peak brightness of approximately 412 nits.
Like all Roku TVs, it has Roku OS built in, giving users access to a wide range of apps and services, and local dimming helps deepen blacks and improve contrast compared to lower-end Roku models. While it isn’t marketed as a gaming TV (it’s only 60Hz and also lacks VRR, which means no AMD FreeSync or Nvidia G-Sync), it still offers a low input lag of 3.1 milliseconds in Game Mode, making it responsive enough for everyday streaming and casual gaming.
As one of Roku’s first in-house TVs, the 2025 Plus Series has strong value as a budget TV with a panel that’s brighter and delivers deeper blacks than many Amazon Fire TVs in the same price range. While it doesn’t have the faster refresh rate and more advanced features of the pricier Roku Pro Series or premium OLED TVs, it still delivers most of the core Roku TV experience and respectable visuals, making the 55″ 2025 Roku Smart TV Plus Series hit a sweet spot between budget TVs and more expensive models for those who don’t need cutting-edge gaming features.
On Monday, I was introduced to “Clawdbot,” the latest AI craze taking over tech social media channels. Clawdbot is designed to be an agentic personal assistant. In layman’s terms, that means the bot can perform tasks on your behalf: You give it full access to your computer, and it can organize your inbox, code for you, or clear your calendar (allegedly, anyway). You can also talk to it from a chat app of your choice, like WhatsApp or iMessage, rather than it’s own interface. Some people are even buying Mac minis exclusively to run Clawdbot from.
If you’re wondering where that name came from, it takes after another AI company’s product. Creator Peter Steinberger says he was inspired by the monster that appears when users reload Claude Code—Claude being one of the big AI products in the space right now, developed by the company Anthropic. Steinberger decided to go the lobster route with his logo, and named his own lobster mascot “Clawd.” From this, Clawdbot was born. The problem: Anthropic also calls Claude Code mascot “Clawd.” Whoops.
By Tuesday, Clawdbot was no more (in name, anyway). It turns out companies like Anthropic don’t appreciate it when you start your own business and use the name of their mascot as your own—especially when you’re working in the same ridiculously lucrative field. Maybe if Clawdbot had never taken off, Anthropic wouldn’t have noticed, but the bot became an internet sensation, which no doubt landed it on Anthropic’s radar. As such, Clawdbot has officially changed its name to “Moltbot,” suggesting a lobster molting from its shell. Clawd is now affectionally known as “Molty.” The company made the announcement on its official X page, noting that Anthropic had asked it to change the name over “trademark stuff.” (Steinberger struck a different tone on his personal X account, however, writing: “I was forced to rename the account by Anthropic. Wasn’t my decision.”)
Aside from the name change, the bot appears to be the same as it was on Monday. That is to say, it’s still open source, still available to run locally on your own device, and still comes with the same inherent security risks I outlined yesterday. I still wouldn’t recommend you install a program like Moltbot on your personal device, since, name change or not, you’d still be giving it incredible access to your hardware and its data with little knowledge of the safeguards in place to protect it. All it could take is one malicious prompt injection for Moltbot to molt your security.