Roku QLED 4K And Gorgeous LG C6H OLED TVs Are Up To Thousands Off At Best Buy

Roku QLED 4K And Gorgeous LG C6H OLED TVs Are Up To Thousands Off At Best Buy
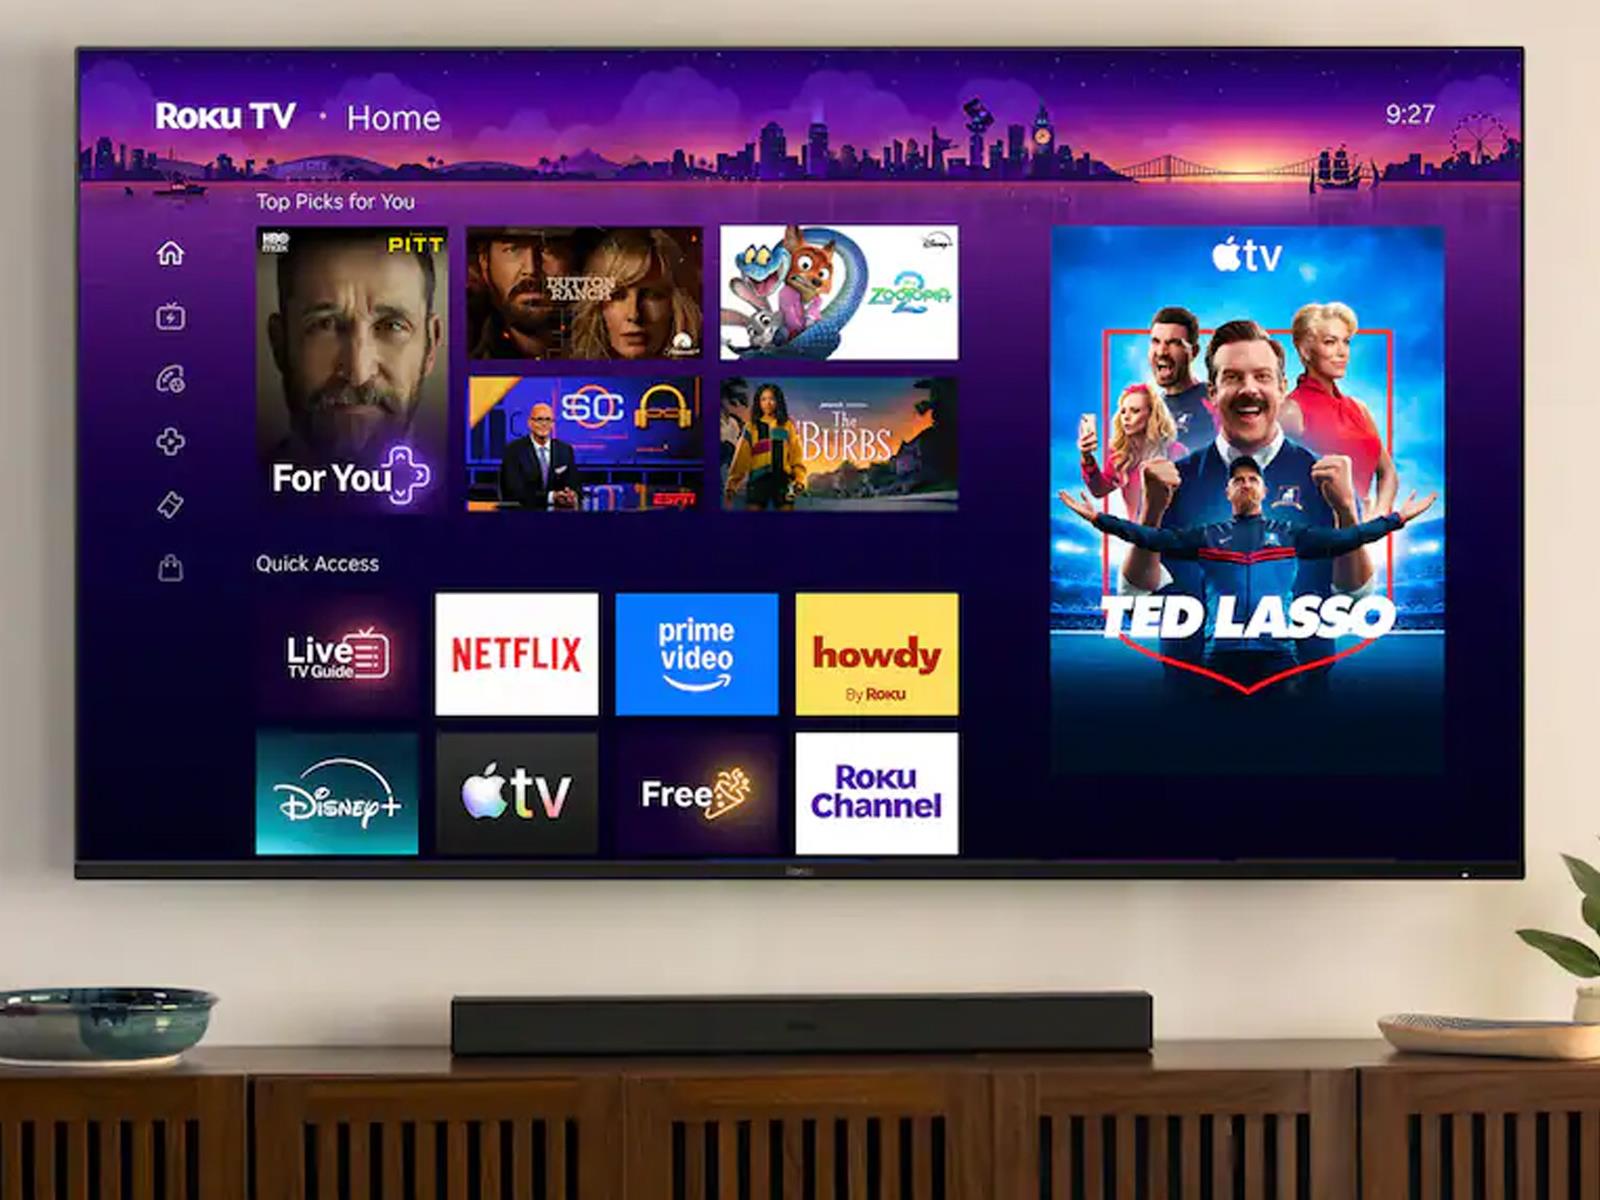
This is a great time to be in the market for a TV, especially one of Roku’s models. The deal to beat is still Roku’s new 65-inch Pro Series OLED TV for $799.99 after applying a hidden coupon code (it still works), as we outlined on Friday, but there are also bargains to be had on Roku’s mini LED Pro TVs.
Roku’s 65-Inch Pro Series 4K QLED

Is GTA 6 Coming To Nintendo Switch 2? Ex-Rockstar Dev Drops Bold Claim

Is GTA 6 Coming To Nintendo Switch 2? Ex-Rockstar Dev Drops Bold Claim
One of the big questions surrounding Grand Theft Auto VI is when it will inevitably get ported to PC, and developer Rockstar Games does not seem keen on tipping its hand. Another area of interest is whether GTA VI will find its way to Nintendo’s popular Switch 2 handheld. So far, Rockstar has only confirmed releases for the PlayStation 5 and

Is Microsoft Quietly Killing Off Its ‘Copilot+ PC’ Brand?

“Copilot+ PCs” were Microsoft’s official branding for Windows 11 “AI PCs” that met their system requirements. But the 2024 launch “didn’t go smoothly,” writes Windows Central, after security researchers discovered its proposed “Recall” feature was woefully insecure:

This pretty much tarnished the Copilot+ PC brand, and over the last two years more and more OEMs have dropped the moniker from marketing materials and product names. In fact, even Microsoft has seemingly stopped mentioning it. I’ve noticed that none of the Surface PCs launched in 2026 include the Copilot+ PC moniker in their product names, unlike the Surface PCs that launched in 2025 and before. Now, you have to go digging to find any mention of Copilot+ compatibility in specification sheets… It’s also worth mentioning that NVIDIA hasn’t gone anywhere near the Copilot+ PC brand for its upcoming RTX Spark platform, even though all RTX Spark PCs meet the Copilot+ PC specification bar. I suspect that’s a deliberate decision.

It seems pretty obvious that the Copilot+ PC brand hasn’t resonated with the market, and OEMs and Microsoft itself are now quietly pulling back on that branding. The specification baseline for Copilot+ PC experiences still exists, it just no longer has a pretty marketing name tied to it.


Read more of this story at Slashdot.

Rogue OpenAI Agents Posted 53 User-Uploaded Images Onto the Internet, Accessed US Government Websites

53 images that users uploaded into OpenAI models were included in training data — and then AI agents in an OpenAI research environment posted those 53 images on public image hosting sites.
While posted as links that weren’t publicly listed, “the images could still be discovered even if the links were not publicly listed,” reports TechCrunch:

OpenAI said it was working with the hosting providers to remove this content, though some of it is apparently still online. OpenAI said it could not notify the affected users because “our technical approach and privacy policy” prevent it from “reassociating” the images with the original providers, but declined to say how the lab determined whether the images were provided by users.

The news came in a post collecting public statements from the lab’s ongoing review of incidents in which its models escaped the company’s scrutiny, accessed the open internet, and misbehaved in various ways. OpenAI said it would continue disclosing anonymized accounts of incidents like these, and said it had contacted dozens of victims, including governments, universities, public agencies, to notify them of the agents’ activities.

Friday night news also broke that OpenAI’s agents also tried unsuccessfully to infiltrate the U.S. Department of Education’s site this summer “without the company’s knowledge,” reports Politico.

And OpenAI’s models also accessed the website of the U.S. Commerce Department using credentials found in online code repositories, according to the article. OpenAI confirmed the incident Friday, “saying its technology did not manage to access information that was not already public or change government data and systems.” The article adds that OpenAI’s models also accessed the web site for America’s Securities and Exchange Commission:

One senior federal IT official said the government still did not have a clear understanding of what happened across the three agencies. “We still don’t know what public data was accessed and how it was accessed, because OpenAI has not shared specific technical details with us yet,” said the official, who was granted anonymity because they were not authorized to speak publicly about it. OpenAI discovered the Commerce and SEC incidents as part of its ongoing review of incidents where its technology has acted in unintended or “misaligned” ways.

About the models posting user-uploaded images, TechCrunch’s article notes that OpenAI stressed “that its enterprise users are automatically opted out of having their interactions used to train future models; however, consumer users are opted in unless they affirmatively choose not to share their data.” (As OpenAI’s announcement describes it, some of their agents’ training data “contains content from, or derived from, training-eligible user interactions.”)

Posting the images is “not an appropriate use of this data,” OpenAI acknowledged, adding that it happened before new safeguards added after the Hugging Face incident. This latest incident appears as an update on a new OpenAI page that “brings together our reports and updates on the Hugging Face incident, related research and public presentations, additional activity we have identified, what we have learned about the role of model misalignment, and measures we’re taking to strengthen our systems.” (It also notes that there’s now a name for models posting on third party sites — “agent spam” — which they consider distinct from cybersecurity, though “we need to address both.”)

“As part of our response to our ongoing investigation, we have improved our training and evaluation processes, including building safety cases, securing and red-teaming our systems to prevent the model from exfiltrating data, and implemented additional monitoring. We are continuing to review agent activity in research and evaluation runs, working backward month by month starting from the Hugging Face incident.”


Read more of this story at Slashdot.
Can Trump ever be wrong? His pick to lead FDA refused to say.

Heidi Overton, President Trump’s nominee to lead the Food and Drug Administration, went before the Senate health committee Thursday, facing questions about her stances on vaccines, flavored vapes, birth control, and abortion, among other issues. She spent nearly two hours stonewalling senators, even on softball questions.

Overton, a physician with a doctoral degree in clinical investigation, is currently the deputy assistant to the president for domestic policy. She previously worked at a conservative think tank and has taken a clear stance opposing abortion, raising obvious questions about her objectivity. The FDA is currently reviewing the safety of the abortion pill, mifepristone, despite extensive data showing it is extremely safe.

Overton also notably stood behind President Trump at a press conference in August during which Trump falsely called the measles, mumps, and rubella (MMR) vaccine “quite lethal.” He further claimed that vaccine doses for infants are “like the size of a soda bottle,” and called for the MMR vaccine to be split into three separate immunizations, despite no evidence of benefit from such a split and no such individual immunizations being available in the US.

Read full article

Comments

Court rules Trump can blacklist Anthropic for refusing to enable Claude features

A US appeals court today approved the Trump administration’s blacklisting of Anthropic technology. Judges decided the US had authority to blacklist Anthropic for withholding certain AI features even if Anthropic had no malicious intent.

In a 2-1 ruling issued by the US Court of Appeals for the District of Columbia Circuit, a panel of judges said the “case raises profoundly difficult questions about the appropriate military uses of an almost unimaginably powerful new technology.” The US “raises the deeply sobering prospect of overly constrained AI models shutting down unexpectedly and thus causing important military operations to fail. Anthropic raises the deeply sobering prospect of unconstrained AI models hallucinating inappropriate targets for lethal military force,” the ruling said.

Trump and Defense Secretary Pete Hegseth “must determine how best to balance the competing risks,” the court said. “In doing so here, the Secretary did not transgress any limits on his authority under the Supply Chain Security Act or the Constitution. Accordingly, we deny the petitions for review.” The same court previously denied Anthropic’s emergency motion for a stay in April.

Read full article

Comments

Tesla workers balk at training Optimus humanoid robots as replacements

Tesla’s pivot from making electric cars to humanoid robots is facing challenges because of complex robot hands and disgruntled employees pushing back against training their robotic replacements. The struggle to scale up production comes as Tesla CEO Elon Musk has bet the company’s future on AI and robotics.

As someone who frequently makes claims that fail to materialize, Musk has described the Optimus humanoid robot as potentially “the biggest product ever” during Tesla’s second-quarter 2026 earnings call. But he also acknowledged that making an autonomous humanoid robot capable of handling many different tasks is “one of the hardest things to solve”—and now extensive reporting by The Information has revealed multiple complications that Tesla is trying to tackle while developing general-purpose robots and scaling up for mass production.

Tesla’s Fremont factory in California has already stopped making the Model S sedan and Model X SUV as of May 2026, with the company switching both line workers and engineers over to working on Optimus, according to The Information.

Read full article

Comments

Your uncle’s frozen Mac says it’s infected after viewing a Google ad. Now what?

Researchers say they recently found Google ads delivering a sophisticated tech support scam that freezes the screens of both Windows and Mac devices and displays messages urgently instructing them to phone a bogus call center.

The ads were displayed all over the web, including on high-traffic maps, weather, real-estate, document-hosting, and sports sites. Users who called the number were then urged to pay hefty fees, grant remote access to their devices, or divulge personal information. From August 31 to September 14, security firm Netskope observed users from 619 customer organizations click on the malicious ads, although none of them were actually scammed because Netskope blocked the content.

Roughly 62 percent of the organizations were based in the US, with Japan and Australia accounting for the Nos. 2 and 3 spots. Since the firm has visibility into only a tiny sliver of Internet activity, the number of people exposed to the ads—including those who fell victim to it—is likely much higher. Netskope tracked more than 250 Google Ads campaign IDs across at least 284 legitimate publisher sites.

Read full article

Comments

Meta Made 43M Misleading Statements, New Mexico Jury Finds, Including on Its Cambridge Analytica Response

A New Mexico jury on Friday “found Facebook liable for deceiving users” about its privacy protections, reports the Associated Press.

A New Mexico newspaper calls it “another massive legal victory” against Facebook, reporting that the jury found Facebook “had committed tens of millions of violations of the state’s Unfair Practices Act in connection with its lies to consumers about how their personal information was handled by the company and third-party users.”

The state has asked the company be ordered to pay the maximum civil penalty of $5,000 per violation meaning a judge could potentially order the company to pay billions in penalties to the state. The jury also found the company had been dishonest about its investigation of and response to the 2013 Cambridge Analytica data breach scandal, in which approximately 300,000 Facebook users took an online personality quiz, only to have the app that hosted the quiz harvest data from tens of millions of their “friends.” The data was then transferred to the British consulting firm, which used it to create targeted political ads during the 2016 U.S. presidential election.

More details from Reuters:

The verdict followed a two-week trial over a lawsuit filed by New Mexico’s attorney general in 2021, three years after news reports revealed that the firm, Cambridge Analytica, had harvested personal data from as many as 87 million Facebook users through a third-party app… At a press conference after the verdict was announced, New Mexico Attorney General Raúl Torrez said the case revealed “in stark detail the way in which this company plays fast and loose with the rules.”

Jurors found 26 of 29 statements identified by the state were misleading, including comments about user data… Judge Francis Mathew will now determine civil penalties after jurors found more than 43 million violations, based on the number of people affected by the company’s misleading statements… [New Mexico Attorney General] Torrez said his office is evaluating how much to seek but will push for the maximum penalty based on the jury’s findings. The state will also ask [Judge] Mathew to direct Meta to make changes, which could include corrections to its past misstatements as well as an audit of the way it manages user data, Torrez said.


Read more of this story at Slashdot.
There’s a New Way to Break RSA Encryption

“Signature forgery.” It’s a new way to break RSA keys — and it doesn’t require factoring. Ars Technica reports on new research using classical computing to “reduce the current RSA security level to an unacceptably low threshold” and lower the required computing resources by orders of magnitude.

There’s “a gap in current RSA-type security assumptions,” according to a paper co-authored by University of California, San Diego professor Nadia Heninger, who argues that gap “gives classical cryptanalytic evidence in favor of moving away from RSA entirely during the current post-quantum transition.”

The practical risk is limited, but still significant. Applying the attack against the deprecated use of 1024-bit keys took a handful of months on an academic CPU cluster, significantly less than the current estimates for 1024-bit factoring that would require resources that only nations or companies with massive resources could achieve. Widely used RSA implementations are also safe. Nonetheless, the research has taken cryptographers by surprise… “If this result holds up under peer review, it would indeed be a conceptual break-through,” Karsten Nohl, a cryptography expert and the head of innovation at Allurity, said in an interview. “RSA is as difficult to break as it is to factor large integers, at least so we thought. The researcher suggests that you can practically break RSA without cracking its key….”

The key forgery attack Heninger and the other researchers devised poses an immediate threat to 1024-bit RSA. Even for 2048- and 4096-bit keys, the method reduces the security of RSA to unacceptable levels. The National Security Agency, National Institute of Standards and Technology, and European Union Agency for Network and Information Security require that any cryptosystem should provide a level of no less than 128 or more bits, meaning the operations required must exceed 2**128. The forgery attack drops these levels to 2**65, 2**90, and 2**119 for 1024-, 2048-, and 4096-bit keys respectively. These levels may further drop because Heninger’s team did all the coding by hand and used no AI or GPUs in performing the forgeries. The researcher said these tools will “almost certainly” drop the security levels further.

The attack works only against blind-signature implementations of RSA… Still, some real-world systems continue to use blind-signature, also known as textbook, RSA… The paper’s authors and other researchers stress that the new attack poses little real-world threat. It does, however, drastically lower the estimated security of textbook RSA, and it does so in a way no one knew of previously… The new attack will further increase the urgency of completely moving away from the cryptosystem.

Thanks to long-time Slashdot reader phatrabt for sharing the article.


Read more of this story at Slashdot.
Five Game-Changing Features on Garmin’s Fenix 9 Pro

We may earn a commission from links on this page.

Garmin’s Fenix line has long been the watch to beat in the outdoor GPS category, and the new Fenix 9 Pro checks all the right boxes. You still get excellent mapping, a durable and premium build, and strong battery life, plus a handful of quality-of-life updates that make daily use even better. Here are the five features on Garmin’s latest flagship that I suddenlly find I can’t live without.

Garmin Epic training summaries (aka multi-day activity grouping)

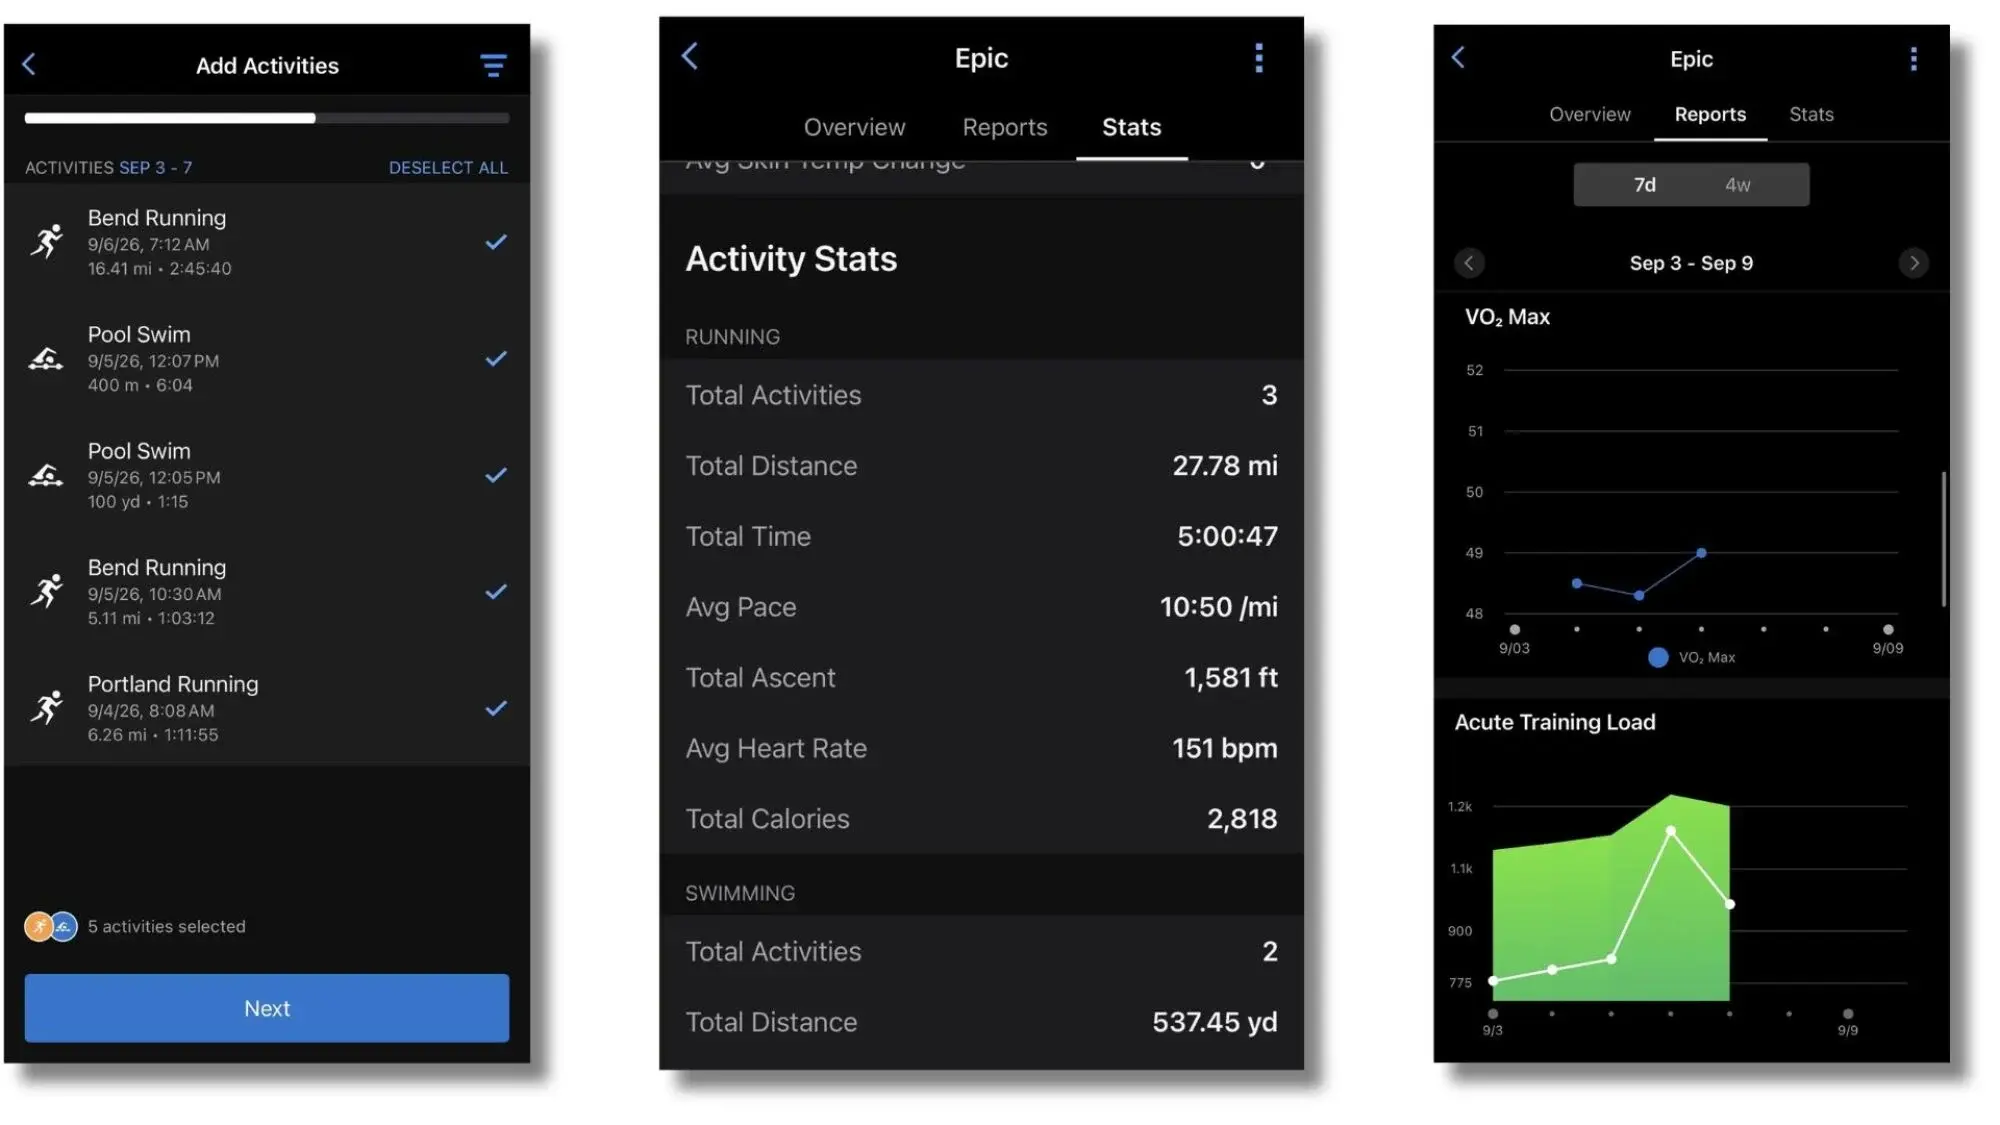
Not to be confused with the older Epix product line, Garmin Epic is a new way to tell the story of a trip rather than just log it. Instead of scrolling through a pile of disconnected activities after a multi-day hike or a training block, Epic groups related sessions into a combined, shareable summary in Garmin Connect—plotting everything on a color-coded map by activity type, with a rundown of health and performance stats underneath.

Garmin Epic screenshots.

Credit: Meredith Dietz

While Epic is marketed as the place to relive your adventures, I’d argue the more useful trick is using it to zoom out and look for patterns in your training. And while the launch of Garmin Epic has been wrapped up in the debut of the Fenix 9, you don’t need this particular smartwatch to use Epics in the Connect app—but for now, however, the Fenix 9 is the only Garmin model that lets you start an Epic straight from the watch.

Stamina curve and stamina zones to chart your endurance

The Stamina Curve estimates how long you can sustain a given effort level—pace for runners, power for cyclists—based on your accumulated training history, and it updates continuously as your fitness shifts. Stamina Zones then turns that curve into personalized effort ranges you can pace against in real time.

The mechanics are intuitive once you’re observing them in action: easy efforts drain the curve slowly, near-maximal efforts burn through it fast. Tracking how that curve shifts across a training block gives you a pretty useful read on whether your endurance is trending up or down. It’s less about a single number on a screen and more about considering your own fatigue trends, which is exactly the kind of feature that rewards long-term users.

Tilted perspective map view and smoother zooming/panning to plan your runs

Garmin has rebuilt how maps render and move on the Fenix 9 Pro. The new tilted, perspective-style map view gives you a more three-dimensional sense of terrain—useful for reading elevation changes or picking a line through complex trail networks—while zooming and panning are meant to be smoother compared to previous generations. For anyone whose main use case is route-finding in unfamiliar terrain, this is arguably a bigger day-to-day upgrade than any single new sensor or metric.

A green LED flashlight mode that won’t blind you during dark runs

It’s a small addition, but a fun one. The Fenix 9 Pro’s built-in flashlight—a fixture of the best adventure watches these days—adds a green light mode alongside the existing white and red options, specifically to help preserve night vision on pre-dawn starts or overnight camp routines. The flashlight also has adjustable brightness, strobe patterns, and even a distress-flash mode that displays your emergency contact information on screen.

Faster mapping and course calculation for more efficient route planning

Under the hood, the Fenix 9 Pro’s mapping engine has gotten a serious performance boost: Garmin claims maps now paint roughly 30% faster, and round-trip course calculation is about 40% quicker. Combined with the doubled storage capacity, this is the feature that makes the flashier navigation updates (like the tilted map view) actually feel good to use rather than just look good in a press release.

The upgrades here are real, but I understand they probably don’t justify the price jump for most people already carrying a Fenix 8. Where the Fenix 9 Pro makes the most sense is for anyone whose Fenix 7 or older watch is on its last legs. For that person (especially one who spends serious time navigating unfamiliar trails and can justify the spend), the Fenix 9 Pro is an excellent watch, and this generation’s improvements to mapping, stamina tracking, and everyday usability make it even easier to recommend.

Crab Wearing An Anemone As A Backpack

If there was ever a freaky deaky contest (and there may be — I tend to stick to the shallows of the internet), Mother Nature would win hands down. And she wouldn’t even show up to claim her prize, she’d be too preoccupied pushing the freaky deaky envelope out in the wild. Case in point: these videos of a deep sea crap wearing an anemone as a backpack. “I think you meant crab.” So I did — good catch.

“In addition to their long, thin walking legs, Homolidae crabs (also known as “porter crabs”) have modified rear appendages they use to pick up anemones and other things on the seafloor. Scientists speculate that this behavior could be related to physical camouflage, chemical camouflage, or predator defense.”

So the crabs use their custom modified appendages (thanks evolution!) to pick up and carry around anemones. But what are the anemones getting out of it? Is this relationship entirely one-sided? I have so many questions, but you know Mother Nature isn’t going to answer because she’s too busy stuffing spiders into frog butts or something.

Qualcomm Unleashes Linux On Snapdragon X2 With NPU And GPU Support

Qualcomm Unleashes Linux On Snapdragon X2 With NPU And GPU Support
Alongside the Snapdragon X2 (Elite/Plus) and Snapdragon 8 Elite Extreme Gen 6 debuts, Qualcomm is also showcasing support for its new hardware across not only Windows and Googlebook laptops, but also Linux. Specifically, Qualcomm has started developing its own Debian distribution which will be available by the end of the year, and is also