The WiCi One is available for preorders starting at $1,999.

The WiCi One is available for preorders starting at $1,999.
The WiCi One is available for preorders starting at $1,999.

The Sift will first be released with Minecraft Dungeons 2 later this month before arriving in the base game.

The Sift will first be released with Minecraft Dungeons 2 later this month before arriving in the base game.

An old netbook can automate the devices that otherwise aren’t interested in talking to one another.

Start with the vents before you reach for a screwdriver.

Apple is reportedly looking to appeal the jury verdict.

Tesla CEO Elon Musk has insisted investors think of his electric automaker as a robotics and autonomous vehicle company now. He’s targeted a $20 trillion valuation—nearly four times the value of market leader Nvidia—on that premise. But his Tesla team was in Sparks, Nevada, on Thursday to focus on, well, an electric vehicle: the long-awaited Tesla Semi.
The Semi concept first rolled onto a Tesla event stage in late 2017. Nearly a decade later, Tesla officially launched high-volume production at a livestreamed but invite-only event at the company’s factory. It targeted a niche audience: the cost-conscious people who manage large trucking fleets. A handful of them, all men, trooped across the stage to be thanked for their orders to a pulsing techno beat.
“It’s going to be, really, a driver’s truck. It’s like a sports car in truck form.” Musk said in a pre-taped video played during the evening event. (Musk, for years the ringmaster at Tesla’s circus-like events, skipped his second vehicle debut in a row; he was attending a White House China State Dinner featuring President Xi Jinping.)
TikTok has settled Alabama’s social media addiction lawsuit before it was supposed to go to trial.

macOS Golden Gate refines the Mac software experience, but not everyone can upgrade.

“Finding vulnerabilities faster also puts pressure on Linux distributions to fix and deliver patches faster,” writes Slashdot reader BrianFagioli
AI has transformed bug discovery from “a manual, time-intensive process into a highly automated engine,” notes Canonical’s blog, leading to a “recent explosion in the volume of CVEs”.
Additionally, the upstream kernel community became its own CVE Numbering Authority (CNA) and assigned CVE (Common Vulnerabilities and Exposures) identifiers to thousands of bugs, arguing that at the kernel level, almost any type of bug that can affect a running system, could potentially be classified as a vulnerability. As a result, the volume of CVEs has skyrocketed exponentially, creating a massive backlog of alerts and forcing defenders to drastically increase the speed of their fixes to close the window of risk.
To address the growing volume of CVEs and the demand for faster security fixes, we are transitioning to a unified, 2-week release cycle…
While a patch is being prepared, Canonical aims to provide safe workarounds where applicable, so users aren’t left exposed in the meantime. Where no safe workaround exists, Canonical will say so clearly and point users toward general hardening steps instead. The goal is to get environments into a defensible, safer state within 24 to 48 hours of public disclosure — well before a patch ships. This doesn’t replace the patch; it buys the time needed to fix the vulnerability properly, without sacrificing security.
“Linux did not suddenly become wildly insecure overnight,” notes the blog Nerds.xyz. “We are getting much better at finding and cataloging problems that may have previously gone unnoticed.”
There is something almost ironic about all of this. AI is routinely pitched as a tool that will make software development faster, but it is also making vulnerability discovery faster. That means maintainers now have to accelerate the other side of the equation too.
For Ubuntu users, that should ultimately be good news. More bugs being discovered is preferable to vulnerabilities sitting unnoticed in the Linux kernel.


Read more of this story at Slashdot.
Which sport smartwatch should you get?

NVIDIA’s $16,000 RTX PRO 6000 can beat the RTX 5090, but gamers aren’t who it’s built for.

Swapping out your turntable’s stylus is an easy upgrade.
Relax, that voice you’re hearing from your Roku is pretty easy to turn off.
If you switched from iPhone to Android, you don’t necessarily need to change watches. There’s an app that lets Apple Watch work with Android.
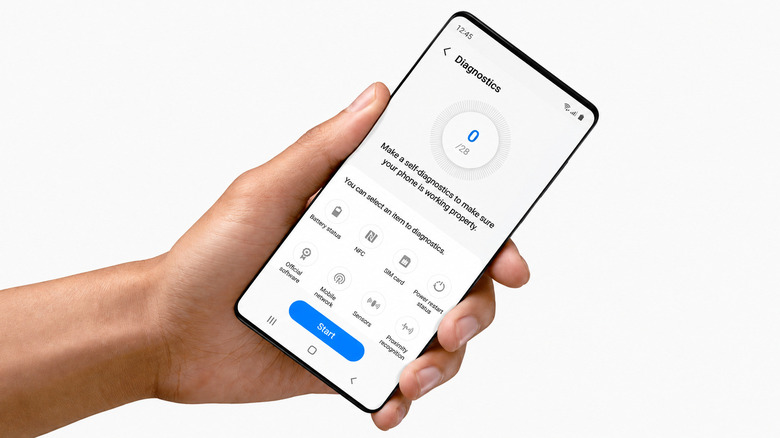
If your Samsung phone is acting strangely, you can test just about any element of the phone’s hardware using this test.
Your PS5 or Xbox Series console can use either setup, but you should consider what’s best for your space first.
The Always-On Display feature of your iPhone should be straightforward, but it can turn off in several situations. You can control some of those.