The ongoing saga of The Walt Disney Company versus Ron Desantis and his hapless oversight board continues.
Source: Gizmodo – Ron DeSantis and His Board Want To Toss Out Disney’s Counterclaims

The ongoing saga of The Walt Disney Company versus Ron Desantis and his hapless oversight board continues.
Source: Gizmodo – Ron DeSantis and His Board Want To Toss Out Disney’s Counterclaims

Enlarge (credit: Getty Images)
From the warm-and-fuzzy files comes this feel-good Friday post, chronicling this week’s takedown of two hated ransomware groups. One vanished on Tuesday, allegedly after being hacked by a group claiming allegiance to Ukraine. The other was taken out a day later thanks to an international police dragnet.
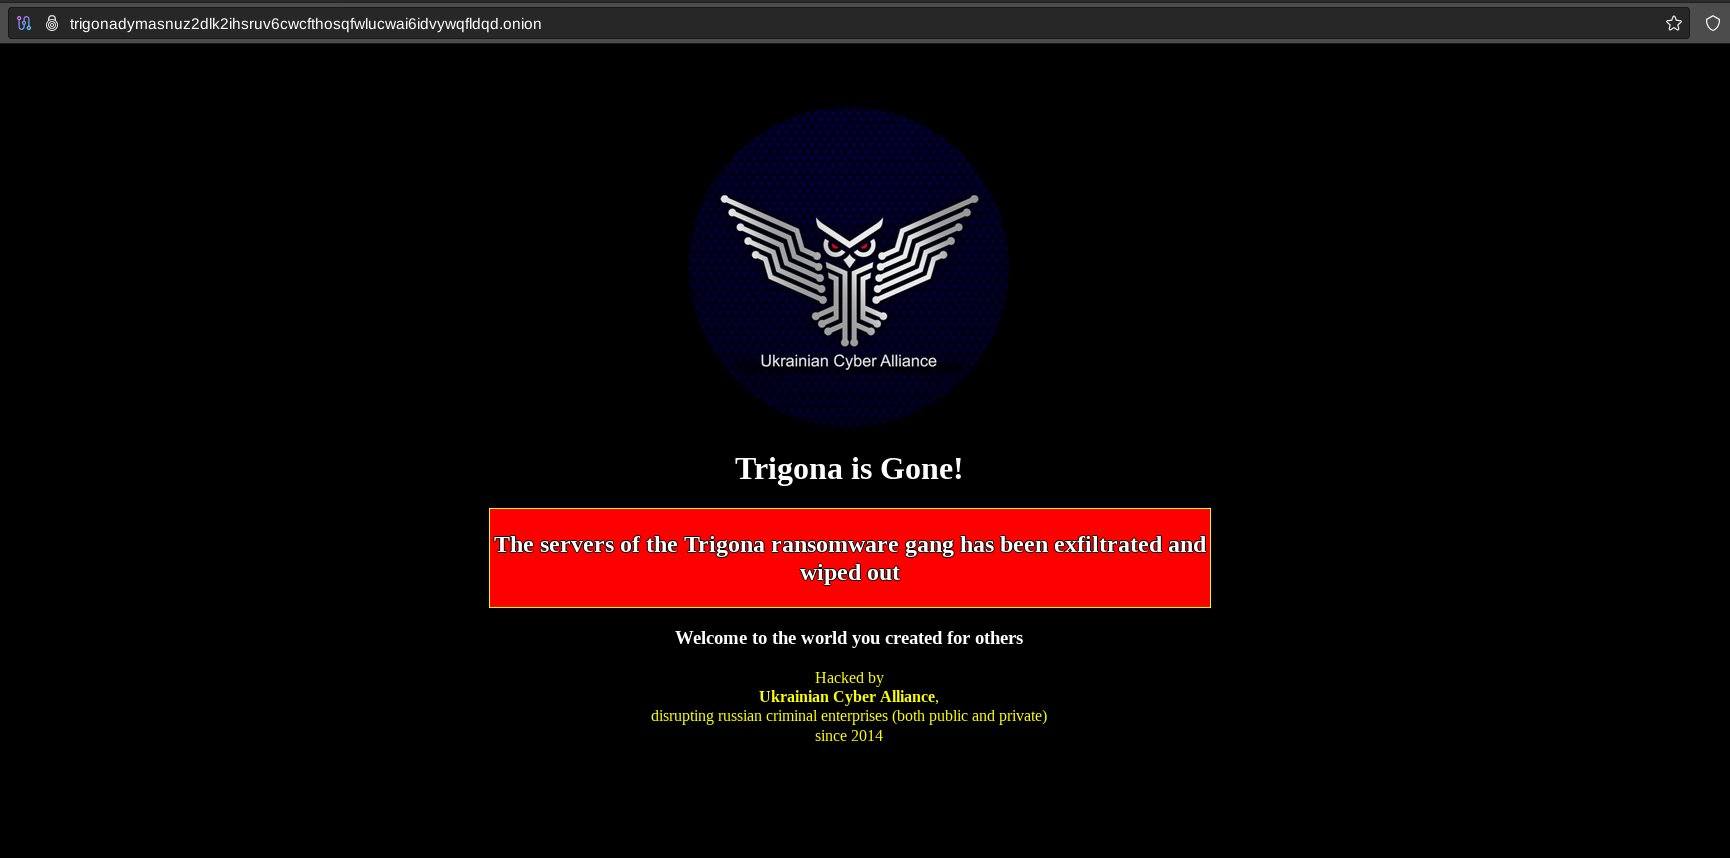
The first group, calling itself Trigona, saw the content on its dark web victim naming-and-shaming site pulled down and replaced with a banner proclaiming: “Trigona is gone! The servers of Trigona ransomware gang has been infiltrated and wiped out.” An outfit calling itself Ukrainian Cyber Alliance took credit and included the tagline: “disrupting Russian criminal enterprises (both public and private) since 2014.”
A social media post from a user claiming to be a Ukrainian Cyber Alliance press secretary said his group targeted ransomware groups partly because they consider themselves out of reach of Western law enforcement.
Read 11 remaining paragraphs | Comments
Source: Ars Technica – Feel-good story of the week: 2 ransomware gangs meet their demise

Enlarge (credit: Getty Images)
Identity and authentication management provider Okta said hackers managed to view private customer information after gaining access to credentials to its customer support management system.
“The threat actor was able to view files uploaded by certain Okta customers as part of recent support cases,” Okta Chief Security Officer David Bradbury said Friday. He suggested those files comprised HTTP archive, or HAR, files, which company support personnel use to replicate customer browser activity during troubleshooting sessions.
“HAR files can also contain sensitive data, including cookies and session tokens, that malicious actors can use to impersonate valid users,” Bradbury wrote. “Okta has worked with impacted customers to investigate, and has taken measures to protect our customers, including the revocation of embedded session tokens. In general, Okta recommends sanitizing all credentials and cookies/session tokens within a HAR file before sharing it.”
Read 7 remaining paragraphs | Comments
Source: Ars Technica – Okta says hackers breached its support system and viewed customer files
As expected, the Supreme Court will weigh in on a controversial case attempting to limit contact between federal officials and social media companies. The case could have sweeping implications for how social media companies make policy and content moderation decisions.
The case stems from a lawsuit, brought by the attorneys general of Missouri and Louisiana, that alleges Biden Administration officials, the CDC and FBI overreached in their dealings Meta, Google and Twitter as the companies responded to pandemic and election-related misinformation. A lower court previously issued an injunction that severely limited government officials’ ability to communicate with social media companies, though some restrictions were later relaxed.
Now, with the Supreme Court agreeing to hear the government’s appeal in the case, the entire lower court order remains on hold. As The New York Times notes, three justices, Samuel Alito, Clarence Thomas and Neil Gorsuch, dissented, calling the decision to allow the lower court order to remain paused “highly disturbing.”
It’s not the only case involving free speech and social media on the Supreme Court docket this term. The court will also take on two landmark cases that could reshape how social media platforms enforce content moderation rules. Those cases involve two state laws, in Texas and Florida, that would prevent social media companies from removing certain types of posts.
This article originally appeared on Engadget at https://www.engadget.com/the-supreme-court-will-hear-case-on-governments-contacts-with-social-media-companies-224551081.html?src=rss
Source: Engadget – The Supreme Court will hear case on government’s contacts with social media companies
An anonymous reader shares a Tom’s Hardware report: Unfortunately, a default setting in Windows 11 Pro, having its software BitLocker encryption enabled, robs as much as 45 percent of the speed from your SSD as it forces your processor to encrypt and decrypt everything. According to our tests, random writes and reads — which affect the overall performance of your PC — get hurt the most, but even large sequential transfers are affected.
While many SSDs come with hardware-based encryption, which does all the processing directly on the drive, Windows 11 Pro force-enables the software version of BitLocker during installation, without providing a clear way to opt out. (You can circumvent this with tools like Rufus, if you want, though that’s obviously not an official solution as it allows users to bypass the Microsoft’s intent.) If you bought a prebuilt PC with Windows 11 Pro, there’s a good chance software BitLocker is enabled on it right now. Windows 11 Home doesn’t support BitLocker so you won’t have encryption enabled there.
To find out just how much software BitLocker impacts performance, we ran a series of tests with three scenarios: unencrypted (no BitLocker), software BitLocker (the Windows 11 Pro default), and with hardware BitLocker (OPAL) enabled. While the software encryption increased latency and decreased transfer rates, hardware encryption and no encryption at all were basically tied. If you have software BitLocker enabled, you may want to change your settings.


Read more of this story at Slashdot.
Source: Slashdot – Windows 11 Pro’s On-By-Default Encryption Slows SSDs Up To 45%

The year is 1994. I head to the theater, buy a ticket for Wes Craven’s New Nightmare, and I’m not ready for what happens next. The year is 2023. I flip over to Max, press play on Wes Craven’s New Nightmare, and I’m still not ready for what happens next.
Source: Gizmodo – Wes Craven’s New Nightmare Feels More at Home Now Than 30 Years Ago

Enlarge / Jon Stewart on his Apple TV show. (credit: Apple)
Jon Stewart and his weekly talk show The Problem with Jon Stewart are out at Apple, according to reports from The New York Times and Variety. Apple canceled the show just weeks before its third season began taping. Its cancellation sheds some light on the conflict of priorities Apple faces as it leans more into content rather than just selling tools, platforms, and gadgets.
The New York Times article cites “several people with knowledge of the situation,” saying that staffers working on the show were told at the end of the day Thursday that it would not move forward.
The reason for the shift? Stewart and Apple executives “had disagreements over some of the topics and guests,” the sources said. Specifically, they claimed Stewart told staffers that Apple execs took issue with planned programming related to both China and artificial intelligence, and noted that with the 2024 US election coming up, there might have been additional opportunities for disagreement then.
Read 6 remaining paragraphs | Comments
Source: Ars Technica – The Problem with Jon Stewart cancellation highlights a problem for Apple’s content
Twitch will now allow its users to stream concurrently on other live video sites. The announcement was made at TwitchCon in Las Vegas, just as it dropped new simulcasting guidelines. The company emphasized that simulcasting is permitted as long as the “Twitch user experience is not compromised” on other platforms.
Back in August, Twitch relaxed its rules on cross-streaming, allowing channels to have their live content appear on social media apps like TikTok and Instagram. In terms of what new competitor services are kosher now, Twitch’s language is broad — citing that “any service” is on the table. The lone exception appears to be channels which have signed exclusivity contracts with Twitch.
We’ve announced that you can simulcast on ANY live streaming service!
Check out our new guidelines and FAQ here: https://t.co/bTVF3hkpV9 #TwitchConVegas— Twitch Support (@TwitchSupport) October 20, 2023
The new approach to simulcasting might seem to hurt the company’s bottom line. A live streaming platform wants more entertainers, so, why allow users to take their content elsewhere? The move might be a response to several big-name streamers jumping ship and signing deals with competitors in the space — YouTube specifically. It’s pure speculation, but perhaps handing creators additional revenue streams with no strings attached might be enough to keep major players on board, and medium-sized streamers happier with their income.
Twitch has been trying to update policies across the board to keep both its users and investors happy. The company just attempted to address off-platform doxxing, and it has even dabbled with machine learning programs that can moderate chats. It also introduced new features borrowed from other social media companies, like stories and feeds.
This article originally appeared on Engadget at https://www.engadget.com/twitch-will-allow-simulcasting-to-competitor-streaming-platforms-222133289.html?src=rss
Source: Engadget – Twitch will allow simulcasting to competitor streaming platforms

Enlarge / Palestine’s flag. (credit: Wong Yu Liang | Moment)
Meta has apologized after a 404 Media report investigating a viral TikTok video confirmed that Instagram’s “see translation” feature was erroneously adding the word “terrorist” into some Palestinian users’ bios.
Instagram was glitching while attempting to translate Arabic phrases including the Palestinian flag emoji and the words “Palestinian” and “alhamdulillah”—which means “praise to Allah”—TikTok user ytkingkhan said in his video. Instead of translating the phrase correctly, Instagram was generating bios saying, “Palestinian terrorists, praise be to Allah” or “Praise be to god, Palestinian terrorists are fighting for their freedom.”
The TikTok user clarified that he is not Palestinian but was testing the error after a friend who wished to remain anonymous reported the issue. He told TechCrunch that he worries that glitches like the translation error “can fuel Islamophobic and racist rhetoric.” It’s unclear how many users were affected by the error. In statements, Meta has only claimed that the problem was “brief.”
Read 22 remaining paragraphs | Comments
Source: Ars Technica – Instagram sorry for translation error that put “terrorist” in Palestinian bios
Toyota and BMW are two of the latest automakers to announce they’re adopting Tesla’s North American Charging System (NACS) plug for their North American EVs, giving drivers access to Tesla’s Supercharger network. Ars Technica reports: BMW’s announcement applies to all its car brands, which means that in addition to EVs like the BMW i5 or i7, it’s also swapping over to NACS for the upcoming Mini EVs as well as the Rolls-Royce Spectre. BMW will start adding native NACS ports to its EVs in 2025, and that same year its customers will gain access to the Tesla Supercharger network. BMW’s release doesn’t explicitly mention a CCS1-NACS adapter being made available, but it does say that BMW (and Mini and Rolls-Royce) EVs with CCS1 ports will be able to use Superchargers from early 2025.
Similarly, the Toyota news applies to its brand as well as Lexus. Toyota says that it will start incorporating NACS ports into “certain Toyota and Lexus BEVs starting in 2025.” And customers with Toyota or Lexus EVs that have a CCS1 port will be offered an adapter allowing them to use NACS chargers, also in 2025. And — you guessed it — 2025 is when Toyota and Lexus EVs gain access to the Supercharger network. While virtually all the brands that sell EVs in the North American market have announced the switch, there are still a couple holdouts. Stellantis has yet to make the switch, “meaning Alfa Romeo, Chrysler, Dodge, Fiat, Jeep, Maserati, and Ram are all sticking with CCS1 for now,” reports Ars.
“Volkswagen Group has also yet to take the plunge, which means that Audi and Porsche are also staying with CCS1 for now, as well as the soon-to-be-reborn Scout brand.” That said, they’re expected to announce a switch to the NACS plug any day now.


Read more of this story at Slashdot.
Source: Slashdot – BMW, Mini, Rolls-Royce, Toyota, and Lexus Are Switching To Tesla’s EV Charging Standard

Discord revealed Teen Safety Assist, a new safety initiative to promote a safer environment for younger users to hang out in. The initiative includes default enabled safety features for teenagers on the app, such as proactive filters and alerts.
Source: Gizmodo – Discord Launches Teen Safety Assist To Create Safer Places to Hang

Calling up an IT department for help can be a frustrating experience—the only thing more frustrating is getting scammed out of money. Microsoft, Amazon, and Indian law enforcement identified a potential fraud ring with a ton of tech confiscated during searches in the country.
Source: Gizmodo – Microsoft, Amazon Help India Law Enforcement Bust Call Center Fraudsters
An anonymous reader quotes a report from Krebs on Security: Okta, a company that provides identity tools like multi-factor authentication and single sign-on to thousands of businesses, has suffered a security breach involving a compromise of its customer support unit, KrebsOnSecurity has learned. Okta says the incident affected a “very small number” of customers, however it appears the hackers responsible had access to Okta’s support platform for at least two weeks before the company fully contained the intrusion. In an advisory sent to an undisclosed number of customers on Oct. 19, Okta said it “has identified adversarial activity that leveraged access to a stolen credential to access Okta’s support case management system. The threat actor was able to view files uploaded by certain Okta customers as part of recent support cases.”
Okta explained that when it is troubleshooting issues with customers it will often ask for a recording of a Web browser session (a.k.a. an HTTP Archive or HAR file). These are sensitive files because in this case they include the customer’s cookies and session tokens, which intruders can then use to impersonate valid users. “Okta has worked with impacted customers to investigate, and has taken measures to protect our customers, including the revocation of embedded session tokens,” their notice continued. “In general, Okta recommends sanitizing all credentials and cookies/session tokens within a HAR file before sharing it.”
Okta has published a blog post about this incident that includes some “indicators of compromise” that customers can use to see if they were affected. But the company stressed that “all customers who were impacted by this have been notified. If you’re an Okta customer and you have not been contacted with another message or method, there is no impact to your Okta environment or your support tickets.” The security firm BeyondTrust is among the Okta customers who was involved in the breach. “BeyondTrust Chief Technology Officer Marc Maiffret said that [Okta’s] alert came more than two weeks after his company alerted Okta to a potential problem,” reports Krebs. They have also published a blog post detailing their findings.


Read more of this story at Slashdot.
Source: Slashdot – Hackers Stole Access Tokens From Okta’s Support Unit

Enlarge / LG C3 OLED TV mounted in a living room. (credit: Best Buy/LG)
Like it or not, holiday shopping season isn’t that far off, and we’re already seeing deals rev up for tech products. Today’s Dealmaster serves up a bounty of options, from Samsung OLED TVs to Lenovo laptops and some killer Dolby Atmos soundbars. Take a gander below to find some bargains on the web right now.
Ars Technica may earn compensation for sales from links on this post through affiliate programs.
Read on Ars Technica | Comments
Source: Ars Technica – Dealmaster: OLED TVs, Apple gear, a robot vacuum, and more

Ever since the release of the original Uncharted: Drake’s Fortune in 2007, PlayStation’s first-party lineup has gradually evolved into flashy cinematic affairs. Like tentpole blockbusters or the HBO original series of old, you’re meant to feel the effort that went into these productions, and many of them often have a…
Source: Gizmodo – Marvel’s Spider-Man 2 Hits All the Right Cinematic Notes

Like more than half of adult Americans, I need a little noise to go to sleep. Some use a white noise machine or their TV, but my preference is podcasts playing on my phone. At least that was my preferred method until iOS 17 came along and messed things up.
Source: Gizmodo – This iOS 17 Bug Is Killing My Sleep
Can you heat up a pan to 30,000 degrees Fahrenheit? That’s the burning question at the center of this proposed class action lawsuit, which claims the advertising for SharkNinja’s nonstick cookware violates the laws of physics and thermodynamics. From a report: While SharkNinja is the company best known for its Shark robovacs and Ninja kitchen gadget, this lawsuit takes issue with the Ninja NeverStick Premium Cookware collection, a line of pots and pans it advertises as having superior nonsticking and nonflaking qualities thanks to its manufacturing process.
Instead of making its pans at a measly 900-degree temperature that other brands use, SharkNinja says it heats up the cookware to a maximum of 30,000 degrees Fahrenheit. That process, according to SharkNinja, fuses “plasma ceramic particles” to the surface of the pan, “creating a super-hard, textured surface that interlocks with our exclusive coating for a superior bond.” But Patricia Brown, the person who filed this lawsuit, isn’t buying it. As cited in Brown’s lawsuit, NASA recently said the “surface of the Sun is a blisteringly hot 10,340 degrees Fahrenheit,” meaning SharkNinja’s manufacturing process reaches about three times that temperature.


Read more of this story at Slashdot.
Source: Slashdot – Frying Pan Company Sued for Claiming Temperatures That Rival the Sun

Enlarge / A Falcon 9 rocket climbs into orbit from Cape Canaveral, Florida, with 22 Starlink satellites Tuesday night in this long-exposure photo. (credit: SpaceX)
Earlier this week, SpaceX launched for the 75th time this year, continuing a flight cadence that should see the company come close to 100 missions by the end of December.
SpaceX plans to kick its launch rate into a higher gear in 2024. This will be largely driven by launches of upgraded Starlink satellites with the ability to connect directly with consumer cell phones, a service SpaceX calls “Starlink Direct to Cell,” a company official told Ars this week.
The goal next year is 12 launches per month, for a total of 144 Falcon rocket flights. Like this year, most of those missions will be primarily devoted to launching Starlink broadband satellites. So far in 2023, more than 60 percent of SpaceX’s launches have delivered the company’s own Starlink satellites into orbit.
Read 16 remaining paragraphs | Comments
Source: Ars Technica – Next year, SpaceX aims to average one launch every 2.5 days
Redis, the go-to in-memory database used as a cache and system broker, is looking to include disk as part of a tiered storage architecture to reduce costs and broaden the system’s appeal. From a report: Speaking to The Register, CEO Rowan Trollope said he hoped the move would help customers lower costs and simplify their architecture. Redis counts Twitter X, Snapchat, and Craigslist among its customers, and it’s popular among developers of modern internet-scale applications owing to its ability to create a cache to prevent the main database from overloading. Trollope said the sub-millisecond distributed system gives devs the performance they need, but admitted other systems built for internet scale, such as MongoDB, might offer price advantages. To address this, the company has already created a tiered approach to memory by offering flash support behind its in-memory system.
“We have a half-step between disk and memory. For some specific use cases, in gaming for example, a company might use us for leaderboards and other in-game stats, which they need in real time,” he said. However, after an initial flush of the game launch, a large chunk of users would finish the game and their accounts would go dormant until the release of a new episode or some new content, when they might return. Trollope said using flash allowed users to dynamically tier memory. “We can take the lesser-used data that hasn’t been touched in a while and shuttle it off to flash where it can sit for a while. When the user comes back eventually, it’s very easy for us to seamlessly move it from flash back into memory. And that allows the company to save costs,” he said.


Read more of this story at Slashdot.
Source: Slashdot – In-memory Database Redis Wants To Dabble in Disk