Automatic bike transmission concept is wild and spiky—and could be a big shift

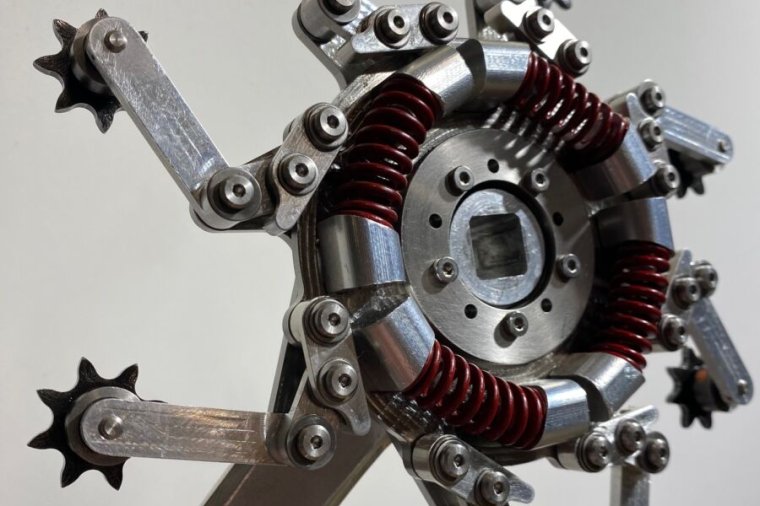
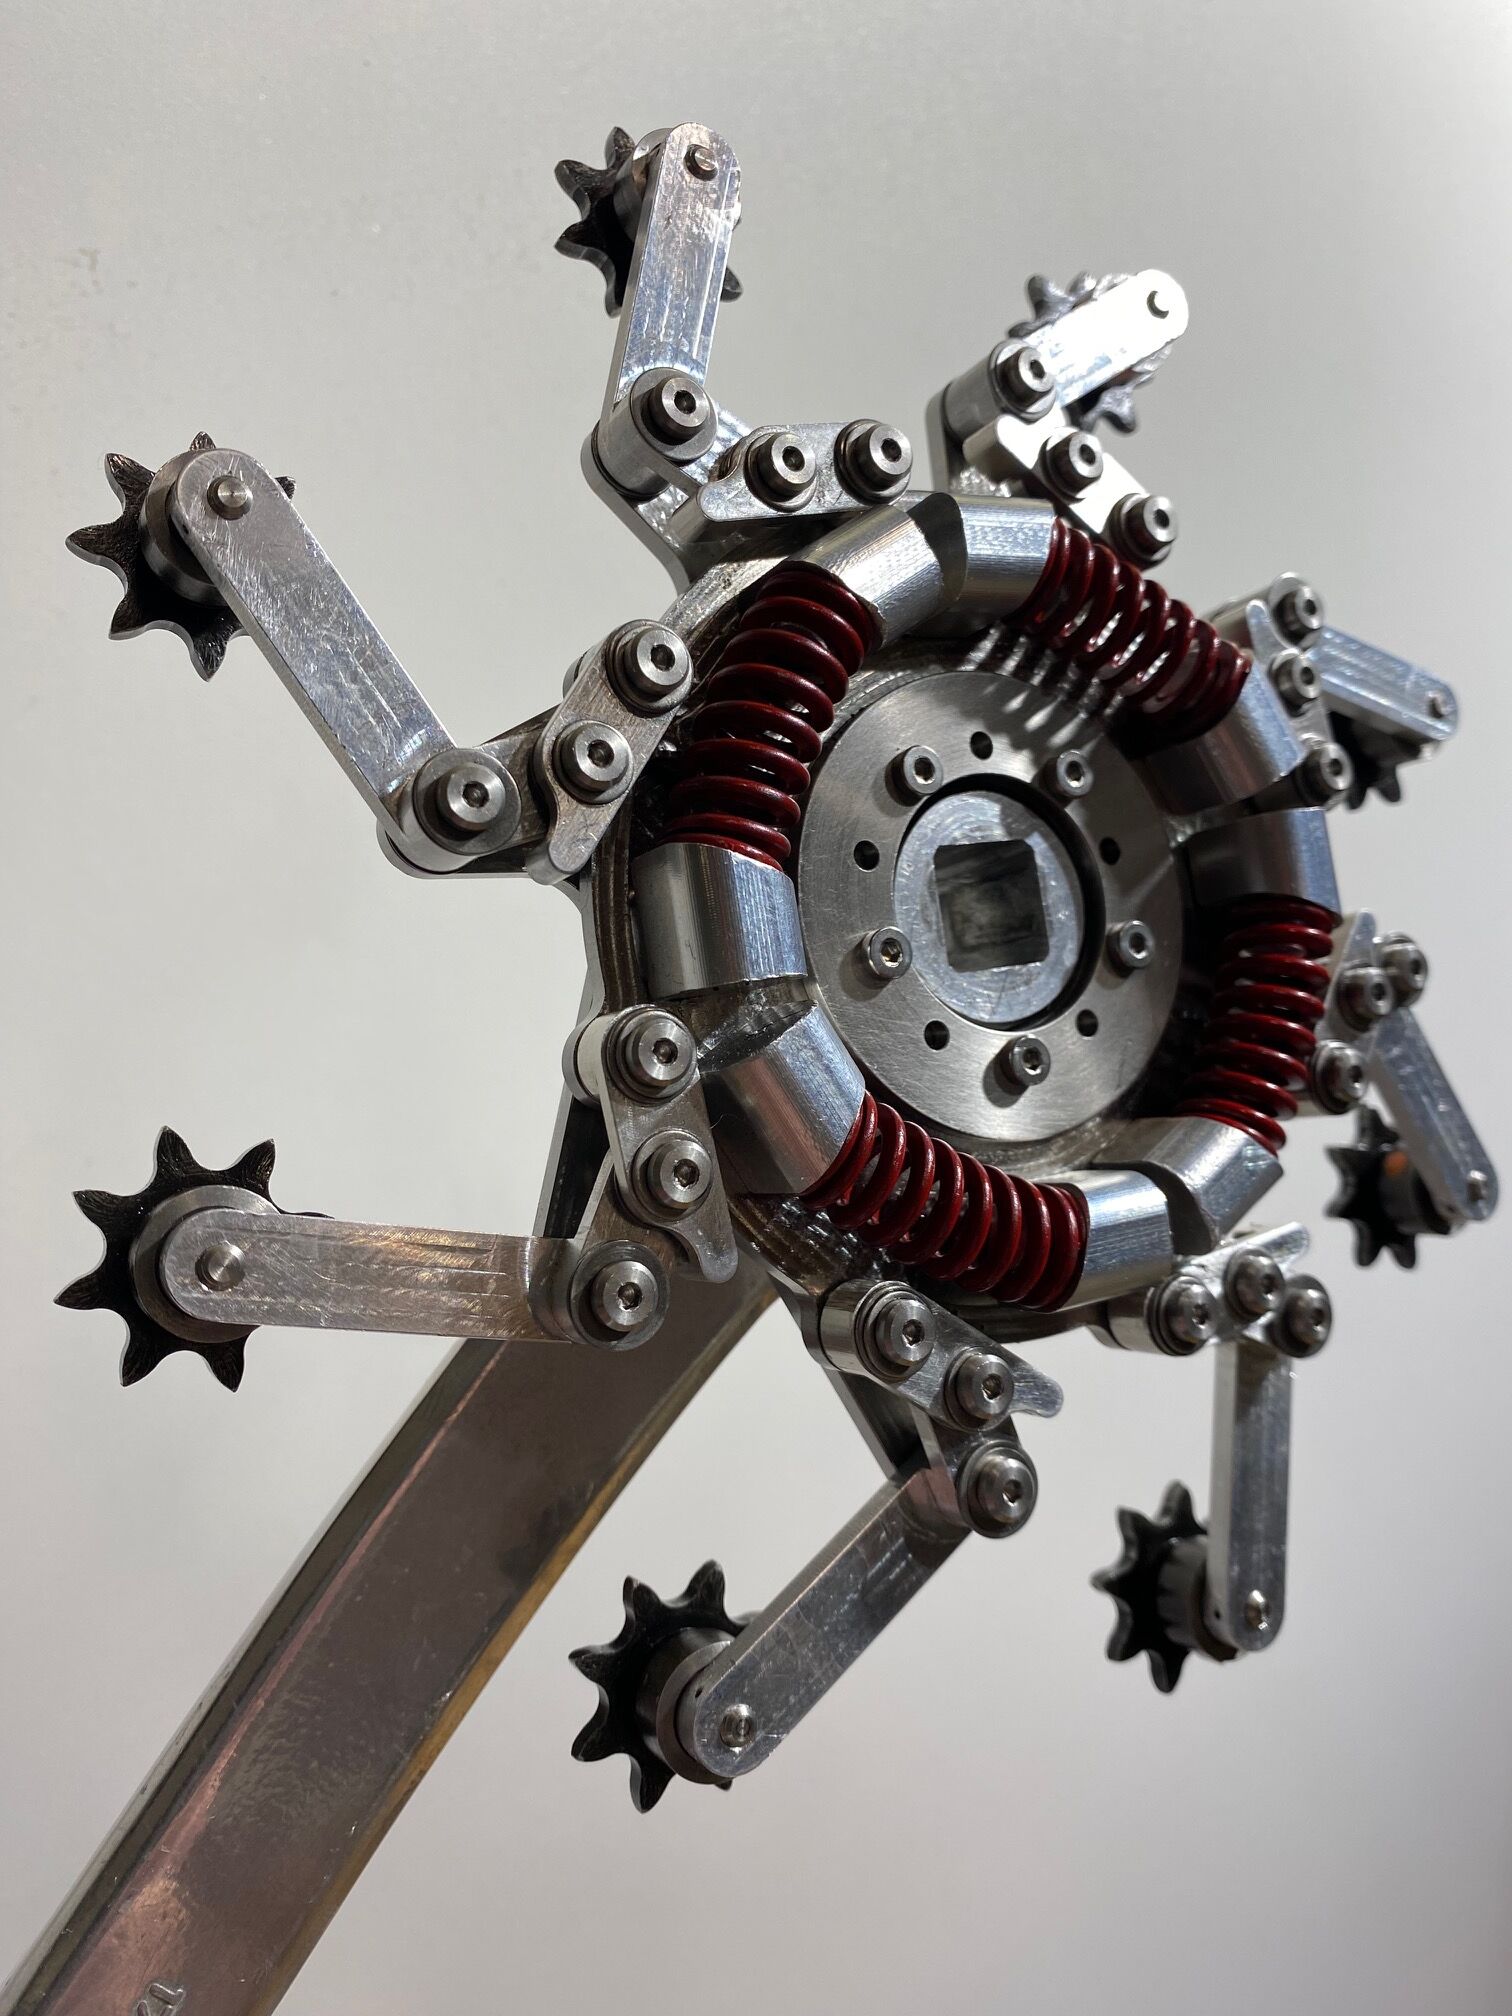
Haven Mercer's prototype front assembly for an automatic bike transmission

Enlarge / Haven Mercer’s prototype front assembly for an automatic bike transmission. (credit: Haven Mercer)

Depending on how you look at it, either a lot or not very much has changed about the way bikes shift gears since the mid-19th century.

A lot has been refined along the transmission path, in which your feet push cranks, those cranks turn a big gear, and a chain connects that big gear to a smaller gear on the rear wheel. Shifting has picked up lots of improvements, be they electronic or wireless, as have derailleurs and internal gearboxes. Materials and tolerances have only improved over the decades.

But in almost all cases, you’re still manually adjusting something to move the chain and change gears, depending on the resistance you’re feeling on the bike. Even the most outlandish recent ideas still involve indexed movement between different-sized gears.

Read 14 remaining paragraphs | Comments


Source: Ars Technica – Automatic bike transmission concept is wild and spiky—and could be a big shift

Hulu's Only Murders in the Building Is Making the Leap to ABC

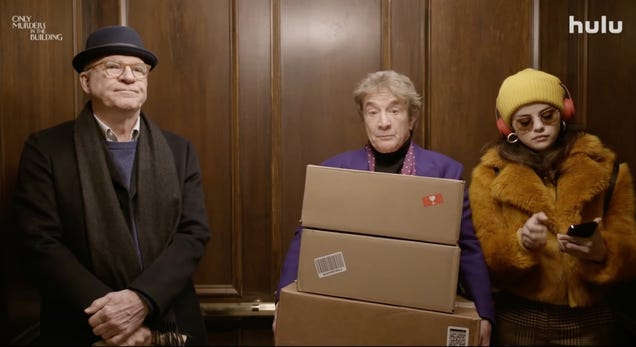
The mystery of “Who killed Tim Kono?” is coming to ABC. Emmy-nominated Hulu Original comedy series Only Murders in the Building is the latest title to shift from streaming to broadcast, with the first three episodes of season one arriving in early 2024.

Read more…


Source: Gizmodo – Hulu’s Only Murders in the Building Is Making the Leap to ABC

ownCloud Vulnerability With Maximum 10 Severity Score Comes Under 'Mass' Exploitation

An anonymous reader quotes a report from Ars Technica: Security researchers are tracking what they say is the “mass exploitation” of a security vulnerability that makes it possible to take full control of servers running ownCloud, a widely used open source file-sharing server app. The vulnerability, which carries the maximum severity rating of 10, makes it possible to obtain passwords and cryptographic keys allowing administrative control of a vulnerable server by sending a simple Web request to a static URL, ownCloud officials warned last week. Within four days of the November 21 disclosure, researchers at security firm Greynoise said, they began observing “mass exploitation” in their honeypot servers, which masqueraded as vulnerable ownCloud servers to track attempts to exploit the vulnerability. The number of IP addresses sending the web requests has slowly risen since then. At the time this post went live on Ars, it had reached 13.

CVE-2023-49103 resides in versions 0.2.0 and 0.3.0 of graphapi, an app that runs in some ownCloud deployments, depending on the way they’re configured. A third-party code library used by the app provides a URL that, when accessed, reveals configuration details from the PHP-based environment. In last week’s disclosure, ownCloud officials said that in containerized configurations — such as those using the Docker virtualization tool — the URL can reveal data used to log in to the vulnerable server. The officials went on to warn that simply disabling the app in such cases wasn’t sufficient to lock down a vulnerable server. […]

To fix the ownCloud vulnerability under exploitation, ownCloud advised users to: “Delete the file owncloud/apps/graphapi/vendor/microsoft/microsoft-graph/tests/GetPhpInfo.php. Additionally, we disabled the phpinfo function in our docker-containers. We will apply various hardenings in future core releases to mitigate similar vulnerabilities.

We also advise to change the following secrets:
– ownCloud admin password
– Mail server credentials
– Database credentials
– Object-Store/S3 access-key”

Read more of this story at Slashdot.


Source: Slashdot – ownCloud Vulnerability With Maximum 10 Severity Score Comes Under ‘Mass’ Exploitation

Doctor Who Christmas Special First Look Gives Us a New Doctor, New Companion, and New Little Freak

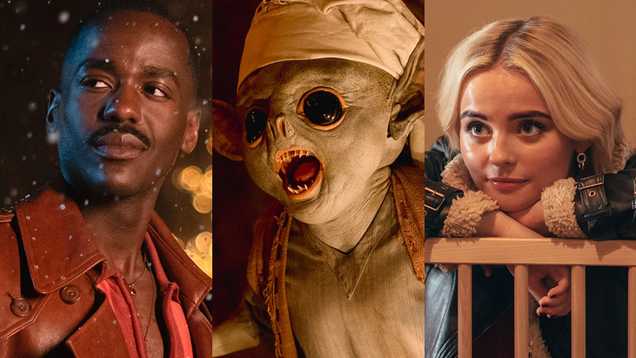
If you thought Miriam Margolyes’ the Meep was the apex of Doctor Who’s creepy little guys, then either good or bad news: things are going to get so much creepier littler and guy-er this Christmas.

Read more…


Source: Gizmodo – Doctor Who Christmas Special First Look Gives Us a New Doctor, New Companion, and New Little Freak

Apple patches two security vulnerabilities on iPhone, iPad and Mac

Apple pushed updates to iOS, iPadOS and macOS software today to patch two zero-day security vulnerabilities. The company suggested the bugs had been actively deployed in the wild. “Apple is aware of a report that this issue may have been exploited against versions of iOS before iOS 16.7.1,” the company wrote about both flaws in its security reports. Software updates plugging the holes are now available for the iPhone, iPad and Mac.

Researcher Clément Lecigne of Google’s Threat Analysis Group (TAG) is credited with discovering and reporting both exploits. As Bleeping Computer notes, the team at Google TAG often finds and exposes zero-day bugs against high-risk individuals, like politicians, journalists and dissidents. Apple didn’t reveal specifics about the nature of any attacks using the flaws.

The two security flaws affected WebKit, Apple’s open-source browser framework powering Safari. In Apple’s description of the first bug, it said, “Processing web content may disclose sensitive information.” In the second, it wrote, “Processing web content may lead to arbitrary code execution.”

The security patches cover the “iPhone XS and later, iPad Pro 12.9-inch 2nd generation and later, iPad Pro 10.5-inch, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 6th generation and later, and iPad mini 5th generation and later.”

The odds your devices were affected by either of these are extremely minimal, so there’s no need to panic — but, to be safe, it would be wise to update your Apple gear now. You can update your iPhone or iPad immediately by heading to Settings > General > Software Update and tapping the prompt to initiate it. On Mac, go to System Settings > General > Software Update and do the same. Apple’s fixes arrived today in iOS 17.1.2, iPadOS 17.1.2 and macOS Sonoma 14.1.2. 

This article originally appeared on Engadget at https://www.engadget.com/apple-patches-two-security-vulnerabilities-on-iphone-ipad-and-mac-215854473.html?src=rss

Source: Engadget – Apple patches two security vulnerabilities on iPhone, iPad and Mac

Elon’s Edsel? The Tesla Cybertruck went on sale today

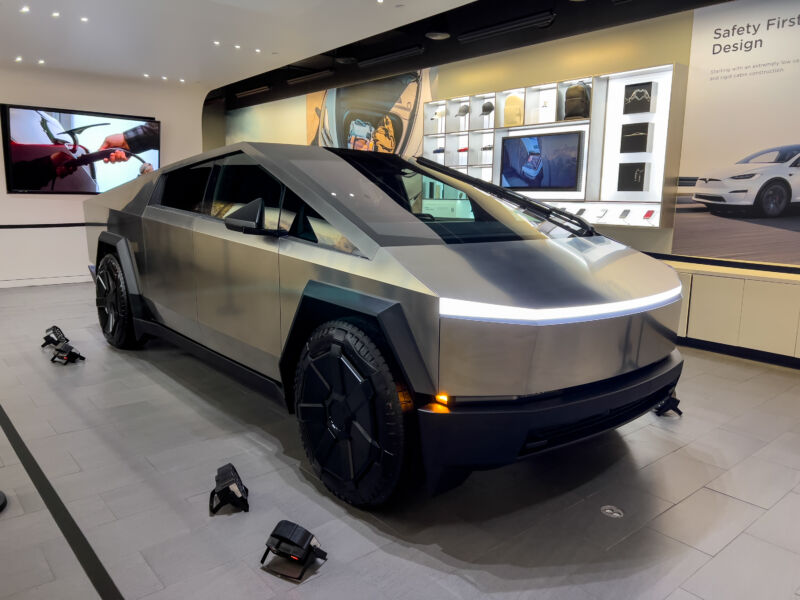
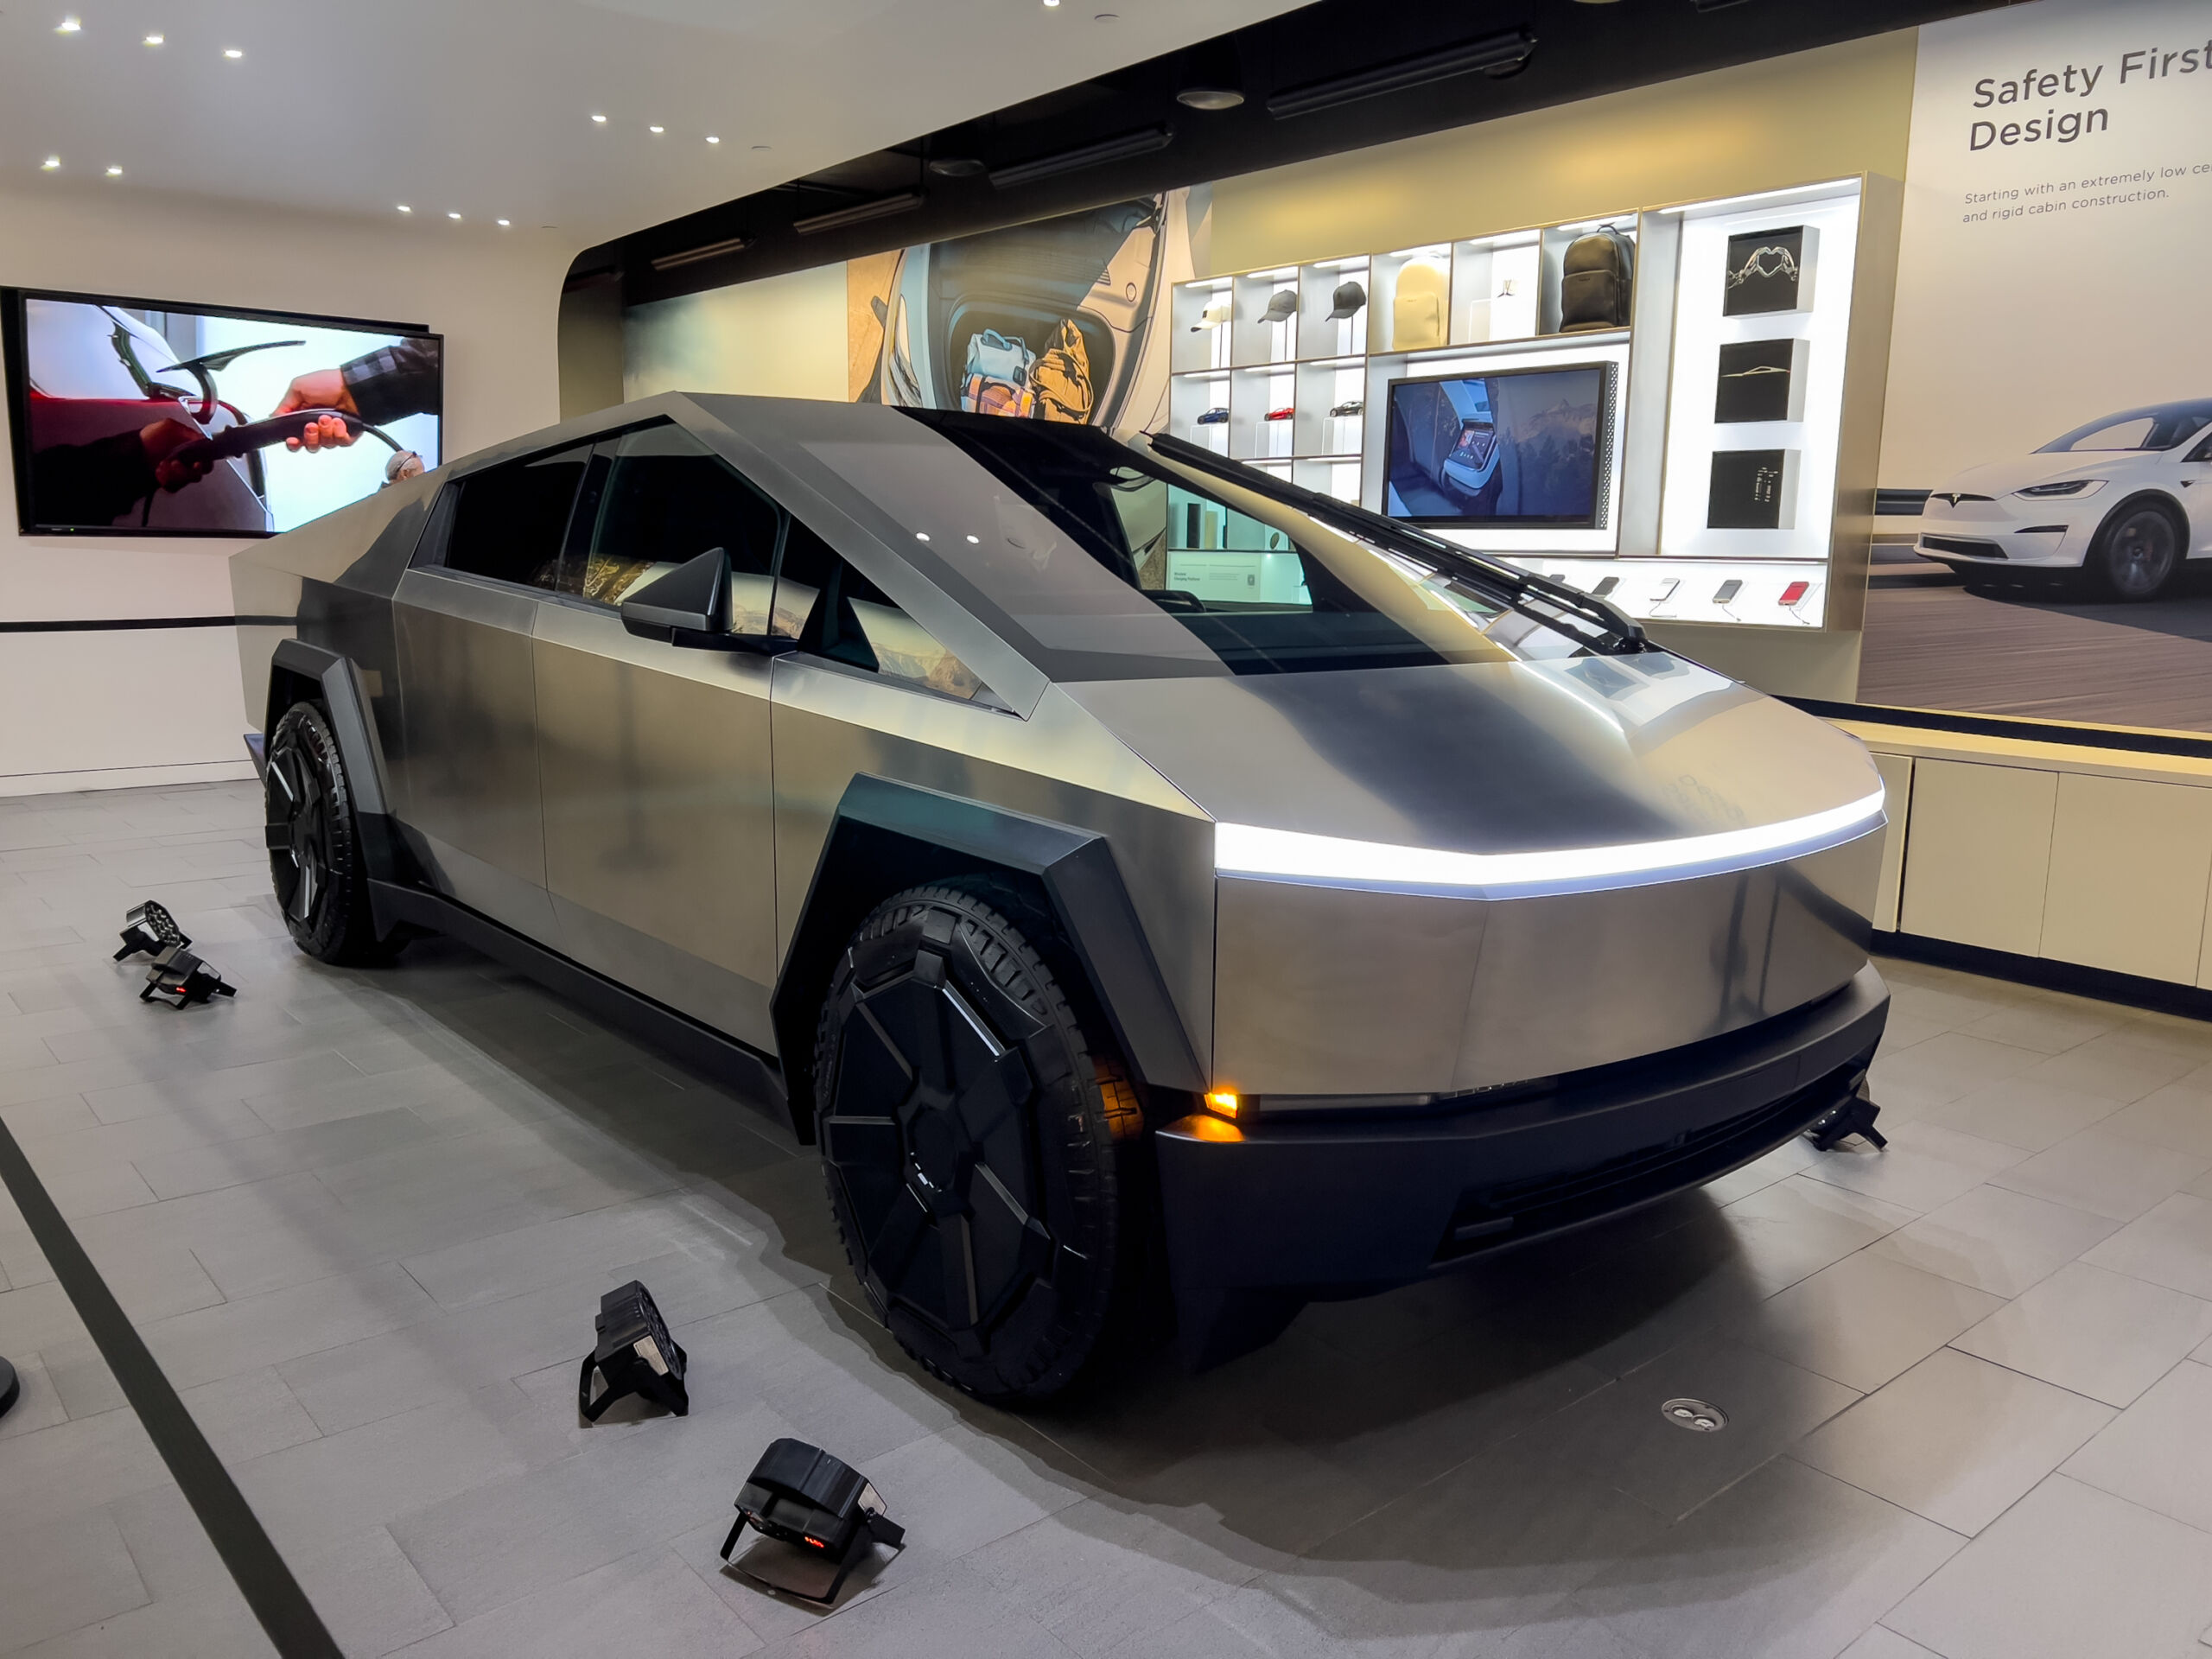
A Tesla Cybertruck in a Tesla store

Enlarge / It will probably be a while before you see these on the road, but some Tesla stores now have display Cybertrucks. (credit: Jonathan Gitlin)

On Thursday afternoon, Tesla delivered the first 10 production Cybertrucks to customers at an event livestreamed on X, Tesla CEO Elon Musk’s social media network. A demo video featured shots of the Cybertruck negotiating barren wildernesses, including one that was meant to look like Mars. Musk, who has mostly made headlines in recent weeks for endorsing virulent antisemtitic theories on his social media platform, took to the stage almost half an hour late, initially delivering his presentation from the back of a truck with his face hidden in shadow.

Musk claimed the Cybertruck is better than any other truck but also more of a sports car than any other sports car, made of a “special Tesla designed steel alloy” that he claimed will never rust and which cannot be stamped but which can also be produced in volume.

Mindful of the window-breaking debacle during the truck’s debut in 2019, Tesla designer Franz von Holzhausen came on stage to throw baseballs at its windows. Unlike last time (when presenters used metal balls), the allegedly bulletproof glass did not shatter. Musk made a point of the fact that in a crash with another vehicle, the Cybertruck—which weighs 6,603–6,843 lbs (2,995–3,104 kg)—will destroy the other vehicle.

Read 8 remaining paragraphs | Comments


Source: Ars Technica – Elon’s Edsel? The Tesla Cybertruck went on sale today

Meta Sues FTC, Says it Has No Constitutional Right to Stop Facebook From Profiting Off of Kids' Data

Meta is working all the angles it can to ensure it will still be able to profit from children’s Facebook data. After a recent loss in court, the company has now sued the Federal Trade Commission, arguing the agency doesn’t have the constitutional authority to change a 2020 $5 billion settlement over the company’s…

Read more…


Source: Gizmodo – Meta Sues FTC, Says it Has No Constitutional Right to Stop Facebook From Profiting Off of Kids’ Data

Reddit updates look after rough 6 months and ahead of reported IPO

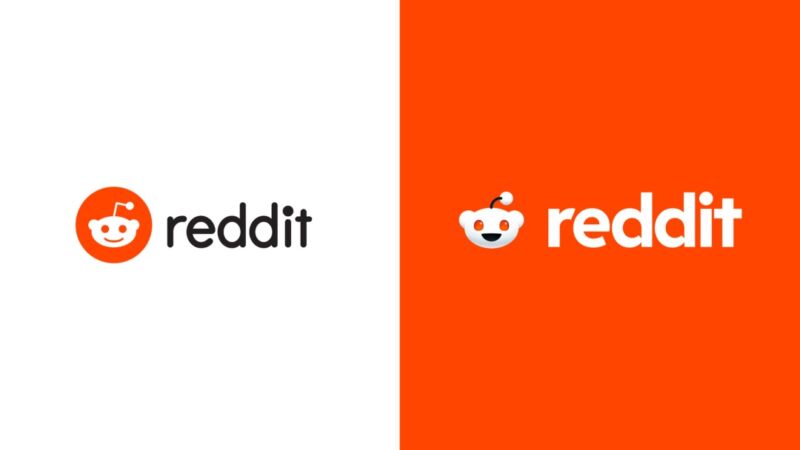
Old Reddit logo vs new Reddit logo

Enlarge / Left: Reddit’s old logo. Right: Reddit’s new logo. (credit: Reddit)

Writing a long comment providing detail about Reddit’s refreshed logo, mascot, and typeface this week, a Reddit employee seemingly rethought the post and opted to conclude it with choice words. The post’s last line currently reads:

“Edit: Obligatory ‘Fuck Spez’ for karma.”

The Reddit employee, going by Acidtwist on Reddit and known as Tavish, says they’re Reddit’s head of brand creative (Reddit says it doesn’t disclose the real identities of its workers on Reddit).

Read 19 remaining paragraphs | Comments


Source: Ars Technica – Reddit updates look after rough 6 months and ahead of reported IPO

HP Printer Software Turns Up Uninvited on Windows Systems

Windows users are reporting that Hewlett Packard’s HP Smart application is appearing on their systems, despite them not having any of the company’s hardware attached. From a report: While Microsoft has remained tight-lipped on what is happening, folks on various social media platforms noted the app’s appearance, which seems to afflict both Windows 10 and Windows 11. The Windows Update mechanism is used to deploy third-party applications and drivers as well as Microsoft’s updates, and we’d bet someone somewhere has accidentally checked the wrong box.

Up to now, the response from affected users has been one of confusion. One noted on Reddit: “I thought that was just me. I didn’t install it, it just appeared on new apps in start menu out of nowhere.” Another said: “I just checked and I had it installed too. Checking the event log for the Microsoft Store shows that it installed earlier today, but I definitely did [not] request or initiate it because I do not have any devices from HP.” And, of course, there was the inevitable: “Would it be that hard for Microsoft to just provide an operating system without needless bloat?” To be clear, not all users are affected.

Read more of this story at Slashdot.


Source: Slashdot – HP Printer Software Turns Up Uninvited on Windows Systems

Tesla's long-awaited Cybertruck will start at $60,990 before rebates

After years of production delays, Tesla CEO Elon Musk took to a dimly-lit stage on Thursday to hand-deliver the first batch of Cybertruck EVs to their new owners. The company has also, finally announced pricing for the luxury electric truck. Prospective buyers can expect to pay anywhere from $60,990 to $100,000 MSRP (and potentially $11,000 less after rebates and tax credits). The company has launched an online configurator tool for those interested in placing an order of their own.   

Tesla also officially revealed the vehicle’s performance specs and model options at the event. The Cybertruck’s entry-level version is the $60,990 single-motor rear-wheel drive ($49,890 after “incentives” and an “est. 3-year gas savings,” per the configurator). It will offer an estimated 250 miles of range and a pokey 6.5 second zero-to-60. Who knew steel sheeting would be so heavy?. It won’t be released until the 2025 model year. 

The mid-level model is the $79,990 all-wheel drive version and sports e-motors on each axle. It weighs just over 6,600 pounds — 1,900 less than the Rivian R1S and nearly 2,500 less than the Hummer EV. It will offer 340 miles of range, a more respectable 4.1-second zero-to-60 and 600 HP with 7435 lb-ft of torque. Its 11,000-pound towing capacity is a touch more than the Ford Lighting XLT’s 10,000-pound maximum.

For $99,990, you can buy the top of the line Cyberbeast — yes, you will have to refer to it as that in public. The Cyberbeast comes equipped with a trio of e-motors that will provide AWD handling, a 320 mile range, 2.6-second sero-to-60, a 130 MPH top speed, 845 horses and 10,296 lb-ft of torque. Despite those impressive specs, the Cyberbeast is stuck with the same 11,000 pound tow limit as the base model. 

Both the Cyberbeast and the AWD iteration will be able to carry 121 cubic feet of cargo and accommodate five adult passengers. The Cybertruck line is compatible with Tesla’s supercharger network and can accept up to 250W maximum, enough to add 128 miles of range for every 15 minutes of charge time. The AWD and Cyberbeast are both currently available to order on Tesla’s website, though prospective buyers will need to put down a fully-refundable $250 deposit upon ordering. 

Developing

This article originally appeared on Engadget at https://www.engadget.com/teslas-long-awaited-cybertruck-will-start-at-60990-before-rebates-211751127.html?src=rss

Source: Engadget – Tesla’s long-awaited Cybertruck will start at ,990 before rebates

Here It Is, Your First Look at the Final Cybertruck

Tesla delivered its first Cybertrucks on Thursday afternoon in Austin, Texas, four years after the dystopian electric vehicles were unveiled. Musk kicked off the delivery event by driving a Cybertruck up next to a crowd of people, standing on top of the car, and giving a speech in the dark. The top-end Cybertruck…

Read more…


Source: Gizmodo – Here It Is, Your First Look at the Final Cybertruck

Amazon’s New AI Image Generator Creates an ‘Invisible Watermark’ on Every Deepfake

How hard is it to check whether an image is an AI deepfake or not? Well, Amazon claims it has some sort of answer with its own watermarking system for Amazon Titan Image Generator, the new AI art creator it announced today. Of course, it’s not that easy. Each business that makes use of the model will have to outline…

Read more…


Source: Gizmodo – Amazon’s New AI Image Generator Creates an ‘Invisible Watermark’ on Every Deepfake

Local Governments Overwhelmed By Tennis-Pickleball Turf Wars, Documents Show

An anonymous reader shares a report: In late September, an arsonist set fire to a storage shed at Memorial Park used by the Santa Monica Pickleball Club, torching thousands of dollars worth of nets, rackets, balls, and other pickleball equipment. “Unknown suspect(s) caused a fire that damaged city property (Tennis Court Gate),” a police report I obtained using a public records request says. The report adds that there is body camera footage of the incident and police-shot photos, but the city refused to release them to me because there is an ongoing investigation. The arsonist is still at large.

We still don’t know the motive behind the arson, but the news caught my attention because it happened while I was in the midst of trying to understand what I’ve been calling the pickleball wars. For the last few months I’ve been trying to understand what’s been happening behind-the-scenes in cities large and small by filing public records requests aimed at learning how common beefs about pickleball are, and what’s causing them.

If you don’t already know about “the fastest growing sport,” Pickleball is kind of like tennis, but played on a court a quarter of the size using a plastic ball similar to a wiffle ball and a hard racket. The smaller court, hard ball, and hard racket means that pickleball is louder than tennis, a fact that is brought up very often by homeowners and homeowner associations who claim, somewhat dubiously, that the noise from pickleball drives down their home values. My hypothesis going into researching this article was that people who live in cities are mad at the noise created during the act of playing pickleball and they have probably complained to the government about it. What I found was surprisingly more complex: Thousands of pages of documents I’ve reviewed show that pickleball’s surging popularity is overwhelming under-resourced parks departments in city governments all over the country.

Read more of this story at Slashdot.


Source: Slashdot – Local Governments Overwhelmed By Tennis-Pickleball Turf Wars, Documents Show

Marvel Just Made Nightcrawler Part of a Big, Queer Family

Kurt Wagner’s relationship with Mystique and Destiny has long been a messy, divisive one–but as the current era of X-Men comics is more explicit about their queer family, this week it righted the wrongs of the past to bring Kurt and his upbringing into a bold new light.

Read more…


Source: Gizmodo – Marvel Just Made Nightcrawler Part of a Big, Queer Family

TikTok's new profile tools are just for musicians

TikTok has introduced the Artist Account, which offers up-and-coming musicians new ways to curate their profiles in ways that boost discoverability. The new suite of tools are not just meant for rising stars: established pop icons can also add an artist tag to their profiles, giving their music its own tab next to their videos, likes and reposted content.

To be eligible for an artist tag, TikTok says you will need at least four sounds or songs uploaded to the app. Artists can also pin one of their tunes so it appears first in the music tab. If a musician drops new content, the app will tag songs as ‘new’ for up to 14 days before and up to 30 days after it goes live. Any new tracks will automatically be added to a profile’s music tab.

TikTok says over 70,000 artists are already using the new tools. The app has proven to be a breeding ground for content to go viral for new artists and established music makers alike thanks to the lightning speed of dance and lifestyle video trends. TikTok’s impact on the music industry has been so massive that even streamers like Spotify have looked into experimenting with video-first music discovery feeds.

This article originally appeared on Engadget at https://www.engadget.com/tiktoks-new-profile-tools-are-just-for-musicians-201723244.html?src=rss

Source: Engadget – TikTok’s new profile tools are just for musicians

Steam’s streaming software now lets you wirelessly play PC VR games on Quest headsets

One of the key selling points of Meta Quest VR headsets is that they can play PC VR titles, but you have to be physically connected via a link cable to the PC. There are some third-party workarounds that allow for wireless game streaming, like Virtual Desktop, but now Steam has unveiled an official solution.

Steam Link is a tool available for Meta Quest 2, 3 and Pro that wirelessly streams PC VR games from your Steam library directly to the headset, so you can continue to avoid cables like the plague. The free app already exists, but has been used to stream Steam games onto phones, tablets and TVs. This is the first time it’s available for VR titles.

There’s one major caveat. Just like Virtual Desktop, you still need a capable PC that can run high-end VR games. You just won’t need the link cable. It’s possible this service can work via cloud computing platforms, but the results are likely to be janky at best. Steam outlines recommended PC specs, suggesting the NVIDIA GTX970 GPU or better, 16GB of RAM and Windows 10 or newer.

Beyond the PC, you also need a 5GHz WiFi router with both the headset and the computer connected to the same network. You can download the Steam Link app directly from the Quest store to get started. This may not be the biggest deal in the world to folks who already use Virtual Desktop, but anything that gets more people into Half Life: Alyx is a good thing.

This article originally appeared on Engadget at https://www.engadget.com/steams-streaming-software-now-lets-you-wirelessly-play-pc-vr-games-on-quest-headsets-200502768.html?src=rss

Source: Engadget – Steam’s streaming software now lets you wirelessly play PC VR games on Quest headsets

Brain Study Suggests Traumatic Memories Are Processed as Present Experience

Traumatic memories had their own neural mechanism, brain scans showed, which may help explain their vivid and intrusive nature. From a report: At the root of post-traumatic stress disorder, or PTSD, is a memory that cannot be controlled. It may intrude on everyday activity, thrusting a person into the middle of a horrifying event, or surface as night terrors or flashbacks. Decades of treatment of military veterans and sexual assault survivors have left little doubt that traumatic memories function differently from other memories. A group of researchers at Yale University and the Icahn School of Medicine at Mount Sinai set out to find empirical evidence of those differences.

The team conducted brain scans of 28 people with PTSD while they listened to recorded narrations of their own memories. Some of the recorded memories were neutral, some were simply “sad,” and some were traumatic. The brain scans found clear differences, the researchers reported in a paper published on Thursday in the journal Nature Neuroscience. The people listening to the sad memories, which often involved the death of a family member, showed consistently high engagement of the hippocampus, part of the brain that organizes and contextualizes memories. When the same people listened to their traumatic memories — of sexual assaults, fires, school shootings and terrorist attacks — the hippocampus was not involved.

[…] Indeed, the authors conclude in the paper, “traumatic memories are not experienced as memories as such,” but as “fragments of prior events, subjugating the present moment.” The traumatic memories appeared to engage a different area of the brain — the posterior cingulate cortex, or P.C.C., which is usually involved in internally directed thought, like introspection or daydreaming. The more severe the person’s PTSD symptoms were, the more activity appeared in the P.C.C. What is striking about this finding is that the P.C.C. is not known as a memory region, but one that is engaged with “processing of internal experience,” Dr. Schiller said.

Read more of this story at Slashdot.


Source: Slashdot – Brain Study Suggests Traumatic Memories Are Processed as Present Experience