Comcast Discloses Data Breach of Close To 36 Million Xfinity Customers [UPDATE]

In a notice on Monday, Xfinity notified customers of a “data security incident” that resulted in the theft of customer information, including usernames, passwords, contact information, and more. The Verge reports: Xfinity traces the breach to a security vulnerability disclosed by cloud computing company Citrix, which began alerting customers of a flaw in software Xfinity and other companies use on October 10th. While Xfinity says it patched the security hole, it later uncovered suspicious activity on its internal systems “that was concluded to be a result of this vulnerability.”

The hack resulted in the theft of customer usernames and hashed passwords, according to Xfinity’s notice. Meanwhile, “some customers” may have had their names, contact information, last four digits of their social security numbers, dates of birth, and / or secret questions and answers exposed. Xfinity has notified federal law enforcement about the incident and says “data analysis is continuing.”

We still don’t know how many users were affected by the breach. Xfinity will automatically ask customers to change their passwords the next time they log in to their accounts, and it’s also encouraging users to turn on two-factor authentication. You can find the full notice, including contact information for the company’s incident response team, on Xfinity’s website (PDF). UPDATE 12/19/23: According to TechCrunch, almost 36 million Xfinity customers had their sensitive information accessed by hackers via a vulnerability known as “CitrixBleed.” The vulnerability is “found in Citrix networking devices often used by big corporations and has been under mass-exploitation by hackers since late August,” the report says. “Citrix made patches available in early October, but many organizations did not patch in time. Hackers have used the CitrixBleed vulnerability to hack into big-name victims, including aerospace giant Boeing, the Industrial and Commercial Bank of China and international law firm Allen & Overy.”

“In a filing with Maine’s attorney general, Comcast confirmed that almost 35.8 million customers are affected by the breach. Comcast’s latest earnings report shows the company has more than 32 million broadband customers, suggesting this breach has impacted most, if not all Xfinity customers.”

Read more of this story at Slashdot.


Source: Slashdot – Comcast Discloses Data Breach of Close To 36 Million Xfinity Customers [UPDATE]
NLRB finds that eBay and subsidiary TCGPlayer engaged in union-busting practices

The National Labor Relations Board (NLRB) has found that eBay has violated the rights of unionized workers at TCGPlayer, a trading card marketplace owned by the company. This comes in response to charges filed by the Communications Workers of America back in March of this year. eBay has allegedly refused to recognize TCGPlayer’s worker union and it delayed participating in any bargaining practices and it has also refused to divulge any information with the group that the union is legally entitled to.

As part of its examination of the issue, the NLRB said that because eBay and TCGPlayer broke the law, the company must face legal consequences for its union-busting practices. The union, which officially formed in March following numerous anti-union actions from eBay and TCGPlayer, was denied representation during disciplinary investigations. The NLRB also found that eBay was changing working conditions and benefits without engaging in bargaining with the group. On top of that, eBay is said to have even enforced rules that would punish any workers’ elections to unionize.

While the NLRB lays out evidence of eBay’s union-busting practices, it did not officially issue a decision on the matter. The agency is still waiting on the company’s response to the issue. “Now that the board has come to a decision on eBay’s illegal practices, we hope the company will see the light, obey labor law and engage in good faith bargaining practices so that workers can secure a strong union contract,” Dennis Trainor, Communications Workers of America District 1 Vice-President, said in a statement. eBay could not be reached for comment.

This article originally appeared on Engadget at https://www.engadget.com/nlrb-finds-that-ebay-and-subsidiary-tcgplayer-engaged-in-union-busting-practices-205337429.html?src=rss

Source: Engadget – NLRB finds that eBay and subsidiary TCGPlayer engaged in union-busting practices

Beeper’s esoteric fix for iMessage access suggests why it’s pushing politically

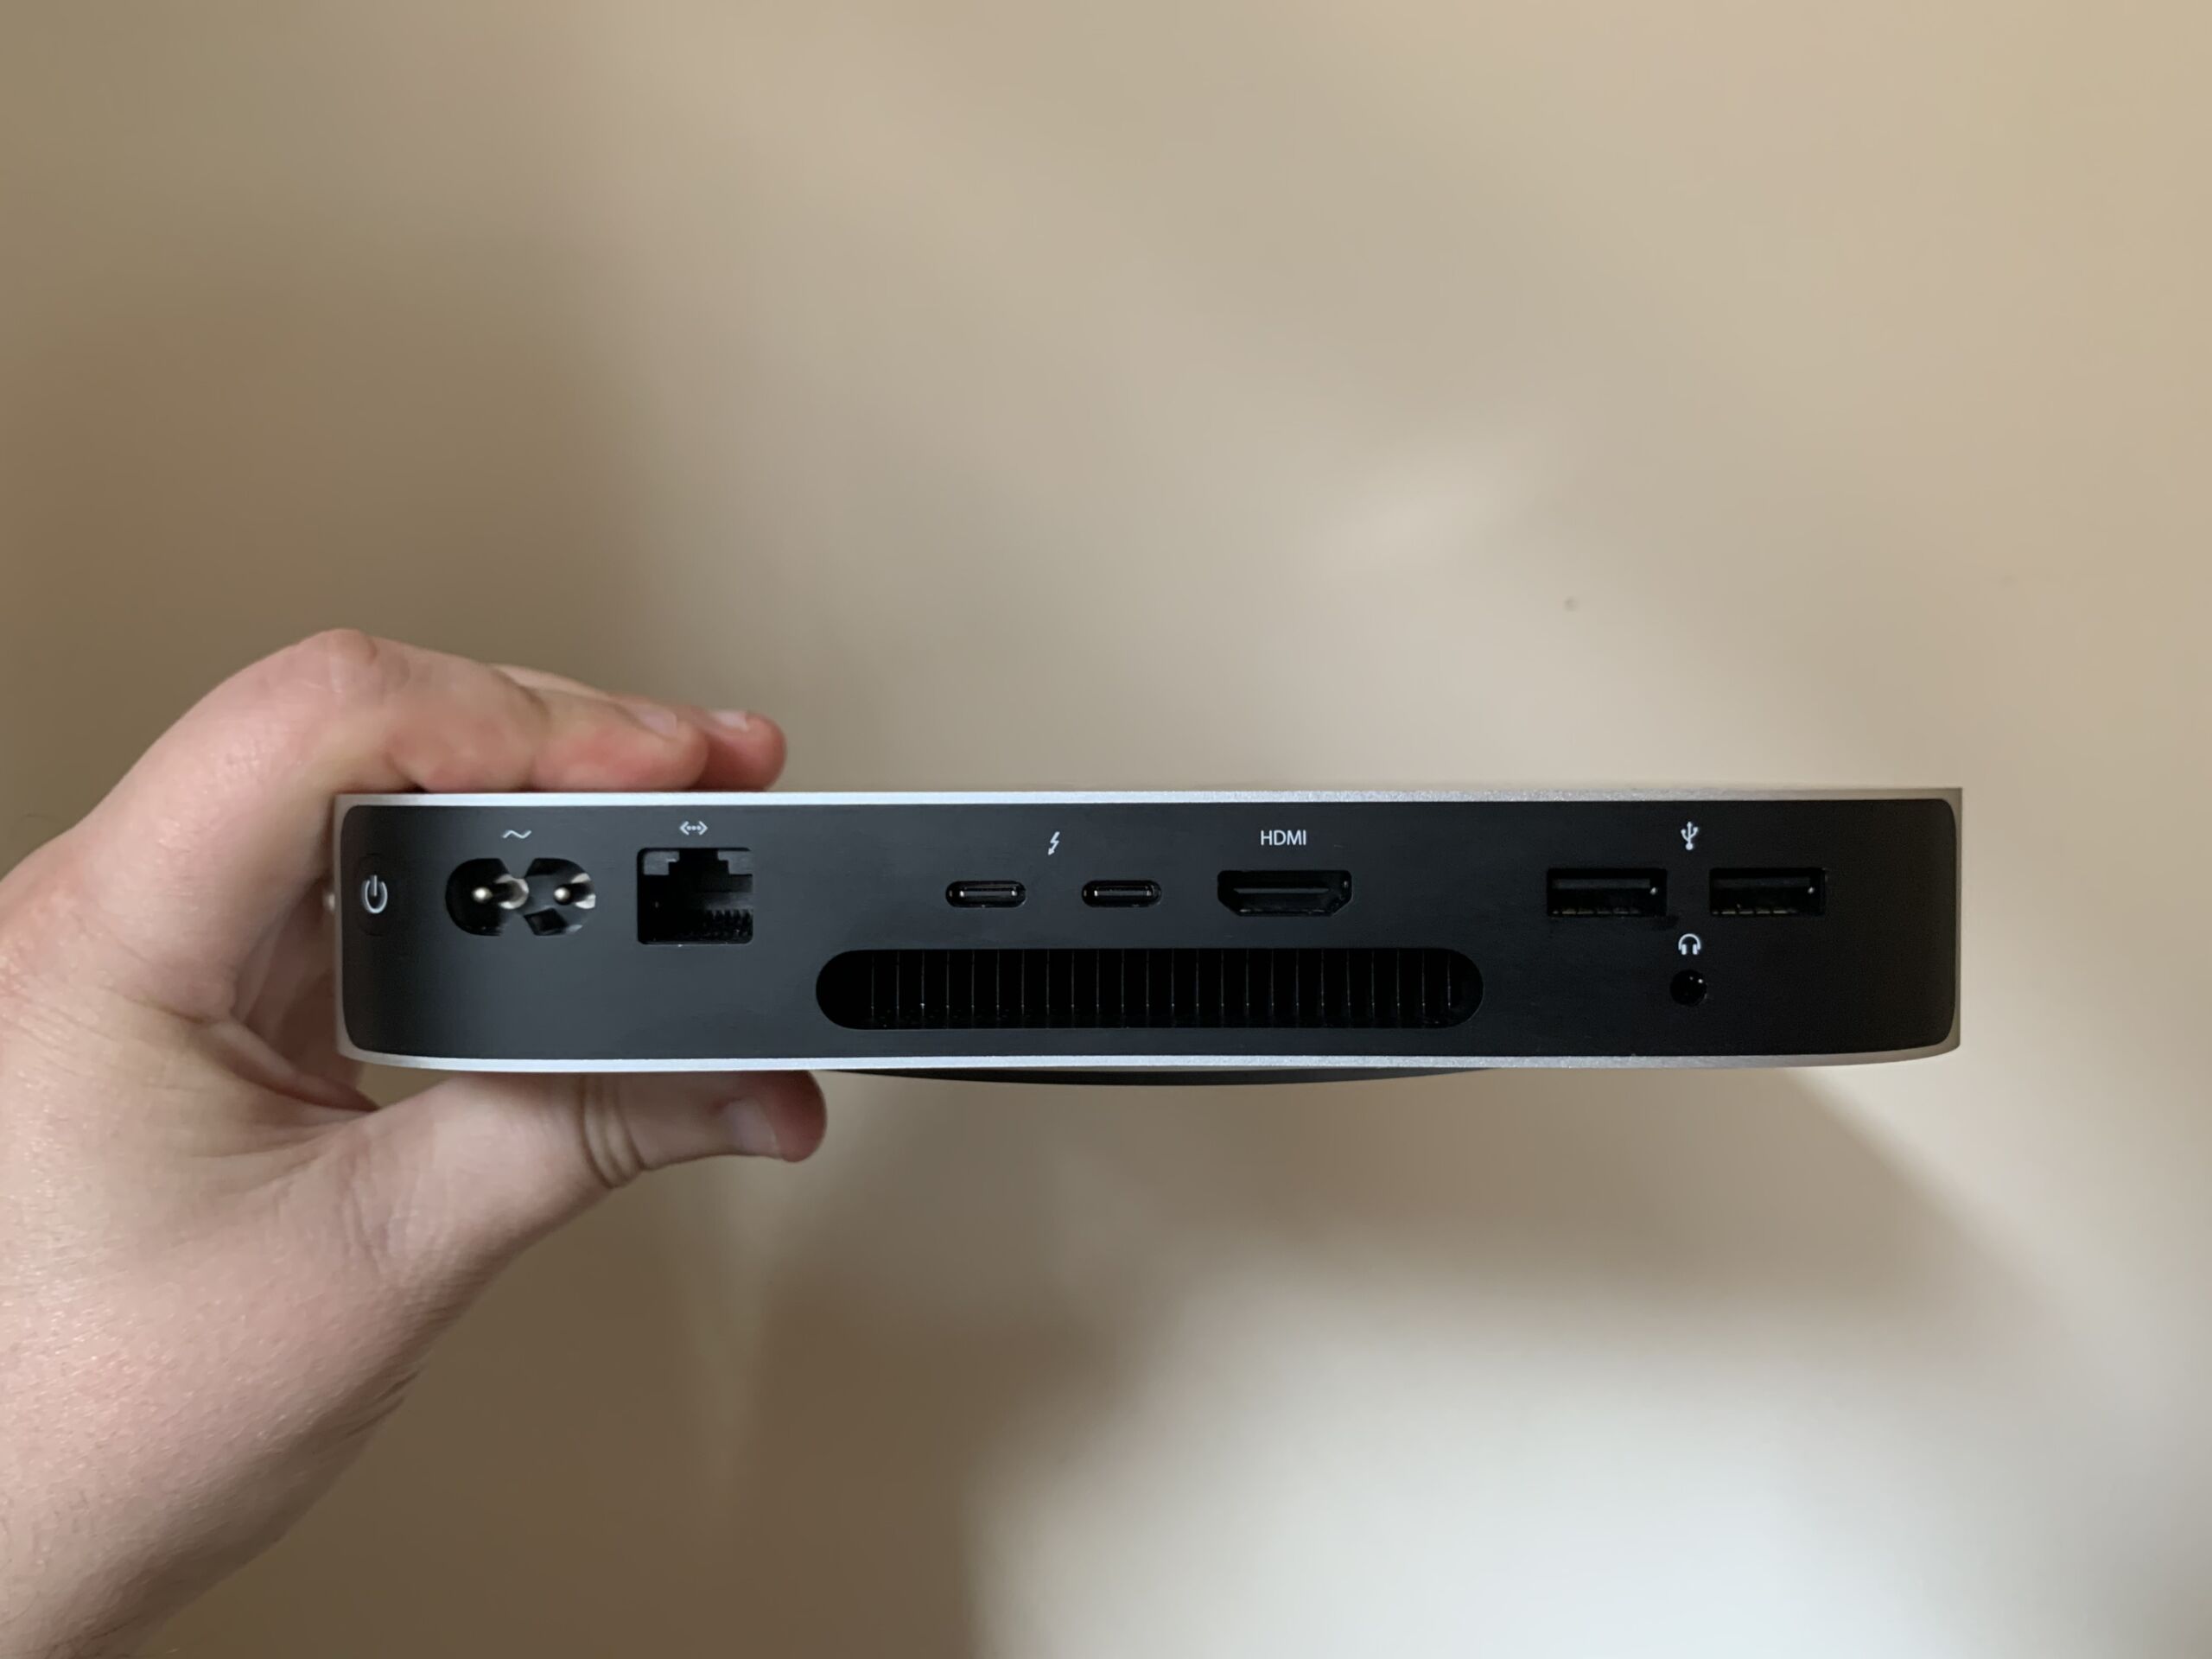
An M1 Mac Mini, held in hand.

Enlarge / If you have one of these, or another Mac handy, you should soon be able to access Beeper on Android and desktop platforms. You’ll just need to grab its “registration data” every so often. (credit: Samuel Axon)

Beeper’s Android app, which initially promised iMessage support with just a phone number, lost that connection once Apple started openly pushing back on it less than a week after it launched. Beeper has kept revising its approach, and its newest method—involving regular access to a physical Mac—suggests why the company has added a political component to its efforts.

Beeper started pushing back after its initial blockage, both through continued development and through media and political messaging. After a second, if smaller, Apple crackdown, co-founder Eric Migicovsky welcomed CBS Mornings into his garage, where he advanced his argument that Beeper was turning grossly insecure SMS messages between iPhone and Android users into secure, end-to-end encrypted chats. (CBS also interviewed James Gill, the 16-year-old whose work connecting to iMessage, using reverse-engineering methods, is the foundation of Beeper’s iMessage tech).

CBS Mornings‘ interview with Beeper co-founder Eric Migicovsky and James Gill, a teenage coder.

That interview lined up with another development: a bi-partisan foursome of US lawmakers, including Senator Amy Klobuchar (D-Minn.), sending a letter to the Department of Justice regarding “Apple’s potential anti-competitive treatment of the Beeper Mini messaging application.” Apple’s actions toward Beeper, the letter suggests, could “eliminate choices for consumers,” “discourage future innovation and investment” in messaging, and make Apple a “digital gatekeeper,” suggesting a need for review by the DOJ’s Antitrust Division. The move follows, and seems to echo, similar efforts by EU regulators to open up iMessage, which have been stalled so far.

Read 6 remaining paragraphs | Comments


Source: Ars Technica – Beeper’s esoteric fix for iMessage access suggests why it’s pushing politically

Apple is reportedly scrambling to update Apple Watch software to avoid a looming ban

Apple is scrambling to make software updates to Apple Watch algorithms that measure blood oxygen levels to avoid an impending ban on the smartwatch in the US over a patent dispute, Bloomberg reported. Changing how the Watch measures oxygen saturation, Apple believes, could help keep the Watch on shelves during the busy holiday shopping season.

The blood oxygen sensor, which was first introduced with the Apple Watch 6 in 2020, is at the heart of a patent dispute between Apple and Masimo, another California-based company that sued Apple in 2021. Masimo claimed that Apple’s sensor violated two patents related to light-based blood-oxygen monitoring that it owned. In October, the International Trade Commission (ITC) upheld a ruling, stating that Apple did, in fact, violate Masimo’s patents.

The case then went to the White House for a 60-day Presidential Review period, which ends next week. If President Biden doesn’t veto the ITC’s decision, Apple will be banned from selling the Apple Watch 9 and Apple Watch Ultra 2, which include blood oxygen sensing. Apple is complying preemptively with the ban and will stop selling both Apple Watch models on its website on December 21 and in retail stores on December 24 in case the veto doesn’t happen.

One way Apple could keep selling the watch is to settle with Masimo, but the company’s last-minute race to make software changes to the Watch suggests that it doesn’t plan to do so. The company told Bloomberg that it plans to submit its software workaround to the ITC for approval. Masimo’s CEO Joe Kiani, told Bloomberg that he would be open to settling with Apple, but the company hasn’t called him yet. “It takes two to tango,” he said.

He also doesn’t think that a software update to the Apple Watch would resolve the situation. “I don’t think that could work — it shouldn’t — because our patents are not about the software,” Kiani said. “They are about the hardware with the software.”

Overhauling Apple Watch hardware would, of course, be a lot more challenging for Apple than tweaking its software. Even if the ITC approves any potential hardware changes, manufacturing and shipping modified versions of the two Watch models could take upwards of three months, a person familiar with how Apple operates told the publication.

Apple and Masimo have a complicated history. Apple reportedly discussed acquiring the company in 2013 and hiring Kiani to work on the medical features on its smartwatch. That deal never went through. Instead, Kiani claimed that Apple hired more than 20 Masimo engineers, doubled some of their salaries, and made them develop the same kind of medical technology they were working on at Masimo at Apple. “This is not an accidental infringement — this is a deliberate taking of our intellectual property,” Kiani told Bloomberg.

Engadget has reached out to Apple for comment on Kiani’s statements. The company has previously called the ITC’s ruling “erroneous” and plans to appeal the decision to the Federal Circuit.

It’s not clear whether Apple will get immediate relief. The silver lining for the company is that the ban only applies to Apple Watch sales through the company’s own channels — its website and its retail stores — in the US. You should still be able to buy the Apple Watch through other retailers like Best Buy, Walmart and Target.

This article originally appeared on Engadget at https://www.engadget.com/apple-is-reportedly-scrambling-to-update-apple-watch-software-to-avoid-a-potential-ban-202710009.html?src=rss

Source: Engadget – Apple is reportedly scrambling to update Apple Watch software to avoid a looming ban

2023 Was the Weakest Year for Memes in History

For the last two decades, some of the weirdest and most creative things on the internet played out in images and GIFs. There have always been terrible memes, but for years, memes as a category were consistently funny, useful, inspiring, and even thought-provoking. They crossed over into all of the furthest reaches of…

Read more…


Source: Gizmodo – 2023 Was the Weakest Year for Memes in History

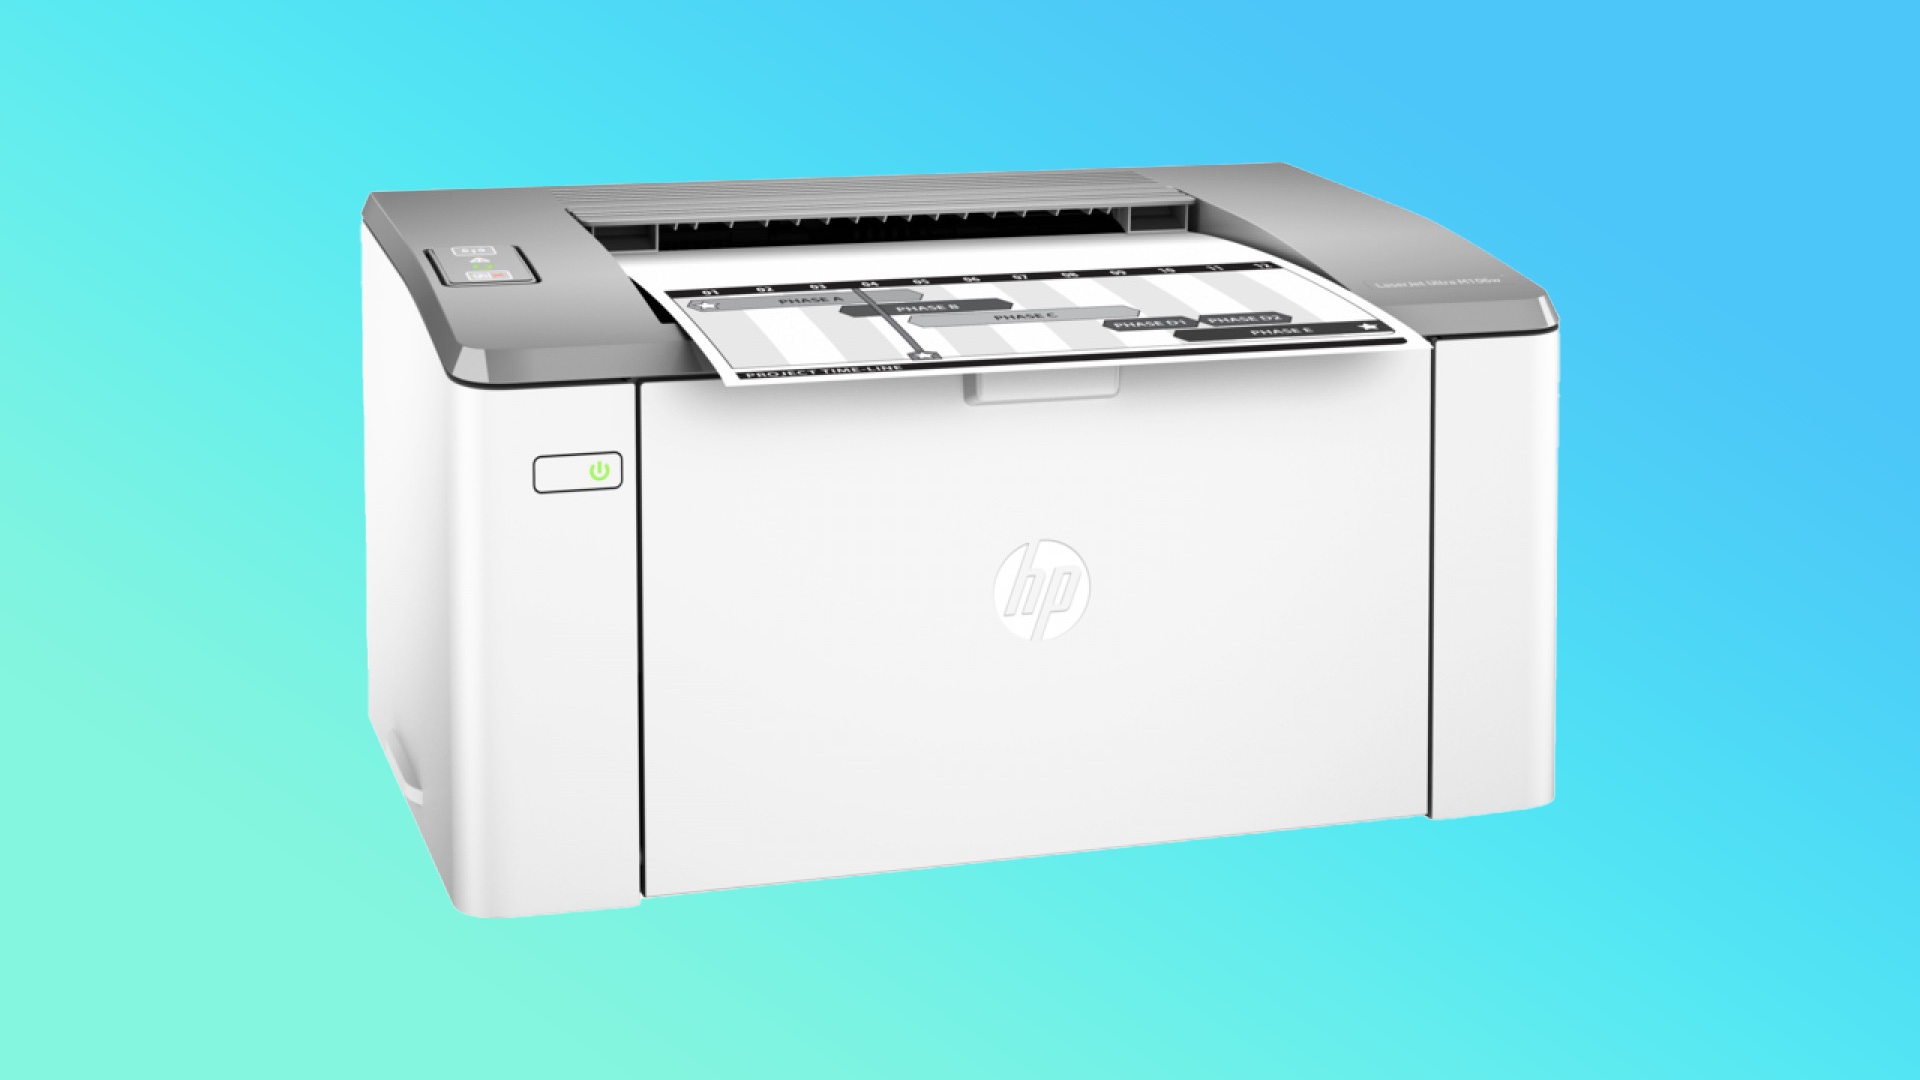
Microsoft releases downloadable tool to fix phantom HP printer installations

The HP LaserJet M106w is one of the printer models that is mysteriously appearing for some users in Windows 10 and 11.

Enlarge / The HP LaserJet M106w is one of the printer models that is mysteriously appearing for some users in Windows 10 and 11. (credit: HP)

Earlier this month, Microsoft disclosed an odd printer bug that was affecting some users of Windows 10, Windows 11, and various Windows Server products. Affected PCs were seeing an HP printer installed, usually an HP LaserJet M101-M106, even when they weren’t actually using any kind of HP printer. This bug could overwrite the settings for whatever printer the user actually did have installed and also prompted the installation of an HP Smart printer app from the Microsoft Store.

Microsoft still hasn’t shared the root cause of the problem, though it did make it clear that the problem wasn’t HP’s fault. Now, the company has released a fix for anyone whose PC was affected by the bug, though as of this writing it requires users to download and run a dedicated troubleshooting tool available from Microsoft’s support site.

The December 2023 Microsoft Printer Metadata Troubleshooter Tool is available for all affected Windows versions, and it will remove all references to the phantom HP LaserJet model (as long as you don’t actually have one installed, anyway). The tool will also remove the HP Smart app as long as you don’t have an HP printer attached and the app was installed after November 25, presumably the date that the bug began affecting systems. These steps should fix the issue for anyone without an HP printer without breaking anything for people who do use HP printers.

Read 2 remaining paragraphs | Comments


Source: Ars Technica – Microsoft releases downloadable tool to fix phantom HP printer installations

Beeper Mini’s latest iMessage for Android setup requires a Mac

Beeper Mini has a new “fix” coming for its broken iMessage on Android integration. However, the new method requires Mac access to send (and intermittently resend) “registration data” from an Apple-made desktop or laptop, calling into question how far users will stick with the app. The company says you’ll see the new functionality in an update to the Beeper Cloud Mac app on Wednesday, December 19.

Beeper’s current method requires identification info (“registration data”) sent from a physical Mac computer to authenticate iMessage connections on Android. The company’s latest plans now shift the Mac onus to users. “We have, up until now, been using our own fleet of Mac servers to provide this,” a Beeper spokesperson wrote in the app’s Reddit community. “Unfortunately, this has proven to be an easy target for Apple because thousands of Beeper users were using the same registration data.”

Beeper Mini launched to much fanfare, promising — and delivering — seamless iMessage chats on Android with only a phone number. However, in what seemed like an inevitable move, Apple squashed the app’s core functionality, forcing the startup to deploy new workarounds as it entered a cat-and-mouse game with the $3 trillion corporation.

Beeper says tomorrow’s update for Beeper Cloud on Mac will generate unique “1:1” registration data for individuals rather than thousands of accounts drawing on the same validation info on Beeper’s servers. The company says the new approach “makes the connection very reliable.” However, the registered Mac will still need to “periodically regenerate” the data after you’ve connected a Mac to Beeper Cloud, so it can’t just be a one-and-done connection to the computer.

If you don’t have a Mac and want to use Beeper Mini, the company says you can ask a friend to use their Apple computer for validation. “In our testing, 10-20 iMessage users can safely use the same registration data,” the company posted. The spokesperson said the update will restore chatting on iMessage with your Apple ID email if you don’t already have a phone number tied to your account.

SAN FRANCISCO, CA - SEPTEMBER 23:  Moderator Greg Kumparak speaks with Eric Migicovsky of Pebble onstage during TechCrunch Disrupt SF 2015 at Pier 70 on September 23, 2015 in San Francisco, California.  (Photo by Steve Jennings/Getty Images for TechCrunch)
Beeper CEO and co-founder Eric Migicovsky, formerly of Pebble smartwatch fame
Steve Jennings via Getty Images

It remains to be seen if Beeper Mini’s users will stick around for the more cumbersome setup. “At this point, I am willing to wait for Apple to come out with RCS support,” Redditor u/OldSalukiBandDude commented, referring to Apple’s promised support for the standard that will bring more iMessage-like features to chats between iPhones and Android handsets. “‘Fix’ is a strong word,” u/PredatorRanger added. “This is more like half-assing a workaround that requires more on the user’s end.”

Others were more open-minded about Beeper’s persistence in the face of Apple’s moves to squash the service. “Ppl are so whiney,” u/Waders411111 wrote. “This is a great bandaid to stop the bleeding and let ppl use beeper as intended.. as a way to integrate all your message apps in one place.” U/bb147 concurred: “Not the most user friendly fix but I am happy to have stable consolidated chats again even if I have to install something on a Mac, at least for now.”

In addition to the new setup method, Beeper says it’s open-sourcing its full iMessage bridge and the Mac code that generates registration data. The company linked to a Github tool that allows users to self-host the bridge, bypassing the company’s servers for those who want extra assurance.

This article originally appeared on Engadget at https://www.engadget.com/beeper-minis-latest-imessage-for-android-setup-requires-a-mac-200322777.html?src=rss

Source: Engadget – Beeper Mini’s latest iMessage for Android setup requires a Mac

Blue Origin returns to form with a successful rocket launch after being grounded for over a year

Blue Origin’s 24th mission is officially a success. The New Shepard rocket took off as planned this morning and the booster and crew capsule safely separated mid-flight and landed back on this great blue marble we call Earth.

This was an uncrewed mission, but it carried 33 science payloads into low orbit, more than half of them from NASA. The launch allowed for a few minutes of zero gravity in which researchers conducted remote studies on these payloads. For instance, a payload from Honeybee Robotics studied the strength of planetary soils under differing gravity conditions. The manifest also included 38,000 student postcards from the Club for the Future initiative.

To those following this mission, the original launch was scrapped on Monday due to a ground system issue that was, obviously, handled. There were no issues reported regarding today’s flight, though there was a slight holdup of a few minutes added to the countdown.

This mission was basically a do-over of a flight from last year that ended prematurely due to a malfunction of the New Shepard booster’s hydrogen-based rocket engine. This anomaly led to the suspension of Blue Origin launches until an investigation by the Federal Aviation Administration (FAA) was completed.

The FAA’s investigation ended in September, freeing up Blue Origin for more launches once it handled a suite of corrective actions mandated by the agency. This included a redesign of the booster’s engine and nozzle as well as some procedural changes. The company hasn’t announced any official plans for future crewed flights, but recently installed an elevator at the launch tower. This is to make future launches “more accessible to people with disabilities, and more people in general,” launch commentator Erika Wagner said during today’s livestream.

To that end, Blue Origin has begun ramping up promotions to attract customers for crewed flights. You can also apply to add a payload to a future launch.

This article originally appeared on Engadget at https://www.engadget.com/blue-origin-returns-to-form-with-a-successful-rocket-launch-after-being-grounded-for-over-a-year-193948312.html?src=rss

Source: Engadget – Blue Origin returns to form with a successful rocket launch after being grounded for over a year

Human brain cells put much more energy into signaling

Read 6 remaining paragraphs | Comments


Source: Ars Technica – Human brain cells put much more energy into signaling

Fantastic Gifts for the Skywatchers in Your life

Amateur astronomy is so hot right now, and it’s never been easier for backyard enthusiasts to gaze into the cosmos and contemplate their puny, meaningless existences. We’ve assembled a collection of exceptional gift ideas to help your favorite space enthusiast take their skywatching skills to the next level.

Read more…


Source: Gizmodo – Fantastic Gifts for the Skywatchers in Your life

Lego Is Officially Making a Twilight Set

Vampires are so hot right now. With Interview With the Vampire and Baldur’s Gate 3’s Astarion being anywhere and everywhere online, we’re in a toothsome renaissance not seen since the days of… well, Twilight’s cultural dominance. So it’s perhaps fitting that it itself returns for the occasion, although in a much…

Read more…


Source: Gizmodo – Lego Is Officially Making a Twilight Set

UK To Introduce Carbon Tax on Steel Imports from 2027

Imported raw materials such as steel and cement will incur a new carbon tax from 2027 under UK plans designed to support domestic producers and reduce emissions, but the government is facing criticism for not moving fast enough. From a report: The Treasury said the tax would help address the phenomenon of “carbon leakage,” in which UK manufacturers are undercut on price by foreign rivals whose governments do not impose levies on businesses that emit a lot of carbon. The result is that emissions are simply displaced to other countries, while greener UK producers lose out because they have to pay carbon-related charges. The chancellor, Jeremy Hunt, said: “This levy will make sure carbon intensive products from overseas — like steel and ceramics — face a comparable carbon price to those produced in the UK, so that our decarbonisation efforts translate into reductions in global emissions. “This should give UK industry the confidence to invest in decarbonisation as the world transitions to net zero.”

Read more of this story at Slashdot.


Source: Slashdot – UK To Introduce Carbon Tax on Steel Imports from 2027

Republicans slam broadband discounts for poor people, threaten to kill program

Senate Minority Whip John Thune gestures with his right hand while speaking to reporters.

Enlarge / Senate Minority Whip John Thune (R-S.D.) speaks to reporters after the weekly Senate Republican caucus lunch on November 14, 2023, in Washington, DC. (credit: Getty Images | Anna Rose Layden )

Republican members of Congress blasted a program that gives $30 monthly broadband discounts to people with low incomes, accusing the Federal Communications Commission of being “wasteful.” The lawmakers suggested in a letter to FCC Chairwoman Jessica Rosenworcel that they may try to block funding for the Affordable Connectivity Program (ACP), which is expected to run out of money in April 2024.

“As lawmakers with oversight responsibility over the ACP, we have raised concerns, shared by the FCC Inspector General, regarding the program’s effectiveness in connecting non-subscribers to the Internet,” the lawmakers wrote. “While you have repeatedly claimed that the ACP is necessary for connecting participating households to the Internet, it appears the vast majority of tax dollars have gone to households that already had broadband prior to the subsidy.”

The letter was sent Friday by Sen. John Thune (R-S.D.), Sen. Ted Cruz (R-Texas), Rep. Cathy McMorris Rodgers (R-Wash.), and Rep. Bob Latta (R-Ohio). Cruz is the top Republican on the Senate Commerce Committee and Thune is the top Republican on the Subcommittee on Communications, Media, and Broadband. McMorris Rodgers is chair of the House Commerce Committee, and Latta is chair of the House Subcommittee on Communications and Technology.

Read 16 remaining paragraphs | Comments


Source: Ars Technica – Republicans slam broadband discounts for poor people, threaten to kill program

Restored 478-key, 31-tone Moog synthesizer from 1968 sounds beautifully bizarre

Shadowed photo of the Moog-Rothenberg keyboard

Enlarge (credit: Ryan Young/Cornell University)

Mathematician and early AI theorist David Rothenberg was fascinated by pattern recognition algorithms. By 1968, he’d already done lots of work in missile trajectories (as one did back then), speech, and accounting, but he had another esoteric area he wanted to explore: the harmonic scale, as heard by humans. With enough circuits and keys, you could carve up the traditional music octave from 12 tones into 31 and make all kinds of between-tone tunes.

Happily, he had money from the Air Force Office of Scientific Research, and he also knew just the person to build this theoretical keyboard: Robert Moog, a recent graduate from Cornell University in Ithaca, New York, who was just starting to work toward a fully realized Moog Music.

The plans called for a 478-key keyboard, an analog synthesizer, a bank of oscillators, and an impossibly intricate series of circuits between them. Moog “took his time on this,” according to Travis Johns, instructional technologist at Cornell. He eventually delivers a one-octave prototype made from “1960s-era, World-War-II-surplus technology.” Rothenberg held onto the keyboard piece, hoping to one day finish it, until his death in 2018. His widow, Suhasini Sankaran, donated the kit to Cornell in 2022.

Read 6 remaining paragraphs | Comments


Source: Ars Technica – Restored 478-key, 31-tone Moog synthesizer from 1968 sounds beautifully bizarre

Microsoft Copilot can now make cute little songs on demand

Microsoft Copilot just rolled out a new feature that creates songs via text prompt, thanks to a partnership with AI-based music creation platform Suno. Microsoft says it gives users the ability to craft personalized songs, “regardless of musical background.” Suno has long been working with various algorithms to create an AI that can whip up entire songs and it looks like the company has struck gold.

When you access this tool, all you have to do is enter a prompt and let the algorithm do the rest. The end result should be “fun, clever and personalized” songs, complete with lyrics and singing voices. You can also make an instrumental tune, if that’s your bag. AI use has been ramping up in the music-making space, but most of those tools are intended to help musicians. This is primarily for non-musicians looking to make a tune for a birthday email or something.

To that end, Microsoft gives prompt examples like “create a pop song about adventures with your family” and “make a song that captures the spirit of growing up.” It looks like the Suno add-on will have access to any personal data accrued by Copilot during use, so these songs could, in theory, get pretty specific.

The feature begins rolling out today, but it’s a tiered release. In other words, it could be a few weeks before it reaches your update box. In the meantime, you’ll have to make do with the thousand other things that Copilot can do.

This article originally appeared on Engadget at https://www.engadget.com/microsoft-copilot-can-now-make-cute-little-songs-on-demand-182305372.html?src=rss

Source: Engadget – Microsoft Copilot can now make cute little songs on demand

Binance to pay $2.7 billion fine after hiding shady transactions from feds

Read 10 remaining paragraphs | Comments


Source: Ars Technica – Binance to pay .7 billion fine after hiding shady transactions from feds