FTC bans Rite Aid from using facial surveillance systems for five years

Rite Aid will not be able to use any kind of facial recognition security system for next five years as part of its settlement with the Federal Trade Commission, which accused it of “reckless use of facial surveillance systems.” The FTC said in its complaint that the drugstore chain deployed an artificial intelligence-powered facial recognition technology from 2012 to 2020 to identify customers who may have previously shoplifted or have engaged in problematic behavior. Apparently, the company had created a database with “tens of thousands” of customer images, along with their names, dates of birth and alleged crimes. Those photos were of poor quality, taken by its security cameras, employees’ phones and even from news stories. As a result, the system generated thousands of false-positive alerts.

Samuel Levine, Director of the FTC’s Bureau of Consumer Protection, said the technology’s use left Rite Aid’s customers “facing humiliation and other harms.” Employees would follow flagged customers around the store, the complaint said, would publicly accuse them of wrongdoing in front of friends and family and would sometimes get the police involved. Further, the system was more likely to generate false positives in predominantly Black and Asian communities. A Reuters investigation in 2020 revealed that the company used facial surveillance in “largely lower-income, non-white neighborhoods.” The FTC noted in its complaint that the technology and “Rite Aid’s failures were likely to cause substantial injury to consumers, especially to Black, Asian, Latino and women customers.”

In addition to prohibiting the use of facial surveillance technologies, the order also requires Rite Aid to delete the photos it collected, notify consumers when their information is registered in a database for security purposes and to provide conspicuous notices if it does use facial recognition or other types of biometric surveillance technologies. It also has to implement a proper data security program to protect the information it collects and will need to have a third party assess it. The proposed order will take effect after being approved by the bankruptcy court, since the company is currently going through bankruptcy proceedings.

Rite Aid, however, said that it “fundamentally disagree[s]” with the agency’s allegations and that it stopped using the surveillance technology years ago.

“We are pleased to reach an agreement with the FTC and put this matter behind us,” the drugstore chain said in a statement. “We respect the FTC’s inquiry and are aligned with the agency’s mission to protect consumer privacy. However, we fundamentally disagree with the facial recognition allegations in the agency’s complaint. The allegations relate to a facial recognition technology pilot program the Company deployed in a limited number of stores. Rite Aid stopped using the technology in this small group of stores more than three years ago, before the FTC’s investigation regarding the Company’s use of the technology began.

Rite Aid’s mission has always been and will continue to be to safely and conveniently serve the communities in which we operate. The safety of our associates and customers is paramount. As part of the agreement with the FTC, we will continue to enhance and formalize the practices and policies of our comprehensive information security program.”

This article originally appeared on Engadget at https://www.engadget.com/ftc-bans-rite-aid-from-using-facial-surveillance-systems-for-five-years-053134856.html?src=rss

Source: Engadget – FTC bans Rite Aid from using facial surveillance systems for five years

Death Stranding: Director's Cut for Mac and iPhone delayed to early 2024

If you were hoping to play Hideo Kojima’s Death Stranding: Director’s Cut on a Mac, iPhone or iPad before the year ends, I’m afraid you’ll now have to wait a bit longer. 505 Games, the publisher behind this port, announced on X that it needs “a little more time,” and that it will have “a new release date in early 2024.” Specifically, the Mac App Store now lists January 31, 2024 as the expected date for this post-apocalypse package delivery simulator, which is available for pre-ordering for $40. 

While the game itself is from 2019 (with the director’s cut released in 2021), Apple appears to be keen on leveraging such heavyweight titles to show off its own processors — M1 or later — and 3D graphics capabilities. If you prefer mobile, though, you’re limited to the iPhone 15 Pro line with their A17 Pro chip. Much like the PlayStation versions, this Apple flavor will also feature cross-over content from Cyberpunk 2077 and Half-Life.

Back in June, Kojima said his future games will also be available on the Apple platform, though it’s not clear if that includes Death Stranding 2. More recently, the gaming legend announced that the title will be adapted into a movie, with help from studio A24. “There are a lot of ‘game adaptation films’ out there but what we are creating is not just a direct translation of the game,” Kojima promised.

This article originally appeared on Engadget at https://www.engadget.com/death-stranding-directors-cut-for-mac-and-iphone-are-delayed-to-early-2024-045956107.html?src=rss

Source: Engadget – Death Stranding: Director’s Cut for Mac and iPhone delayed to early 2024

Elon Musk Draws the Ire of the Tesla Hoe

This week, Tesla made an abrupt change to its in-vehicle entertainment system interface, appearing to cut Disney+ out of the rotation of apps that could be accessed by users. Teslarati initially reported that the car company appeared “to have axed Disney+ from its vehicles.” The site later updated its reporting,…

Read more…


Source: Gizmodo – Elon Musk Draws the Ire of the Tesla Hoe

Blue Origin's Suborbital Rocket Flies For First Time In 15 Months

An anonymous reader quotes a report from Ars Technica: With redesigned engine components, Blue Origin’s New Shepard rocket took off from West Texas and flew to the edge of space on Tuesday with a package of scientific research and technology demonstration experiments. This was the first flight of Blue Origin’s 60-foot-tall (18-meter) New Shepard rocket since September 12, 2022, when an engine failure destroyed the booster and triggered an in-flight abort for the vehicle’s pressurized capsule. There were no passengers aboard for that mission, and the capsule safely separated from the failed booster and parachuted to a controlled landing.

The flight on Tuesday also didn’t carry people. Instead, Blue Origin, Jeff Bezos’s space company, lofted 33 payloads from NASA, research institutions, and commercial companies. Some of these payloads were flown again on Tuesday’s launch after failing to reach space on the failed New Shepard mission last year. Among these payloads were an experiment to demonstrate hydrogen fuel cell technology in microgravity and an investigation studying the strength of planetary soils under different gravity conditions. Blue Origin’s capsule, mounted on top of the rocket, also flew 38,000 postcards submitted by students through Club for the Future, the company’s nonprofit.

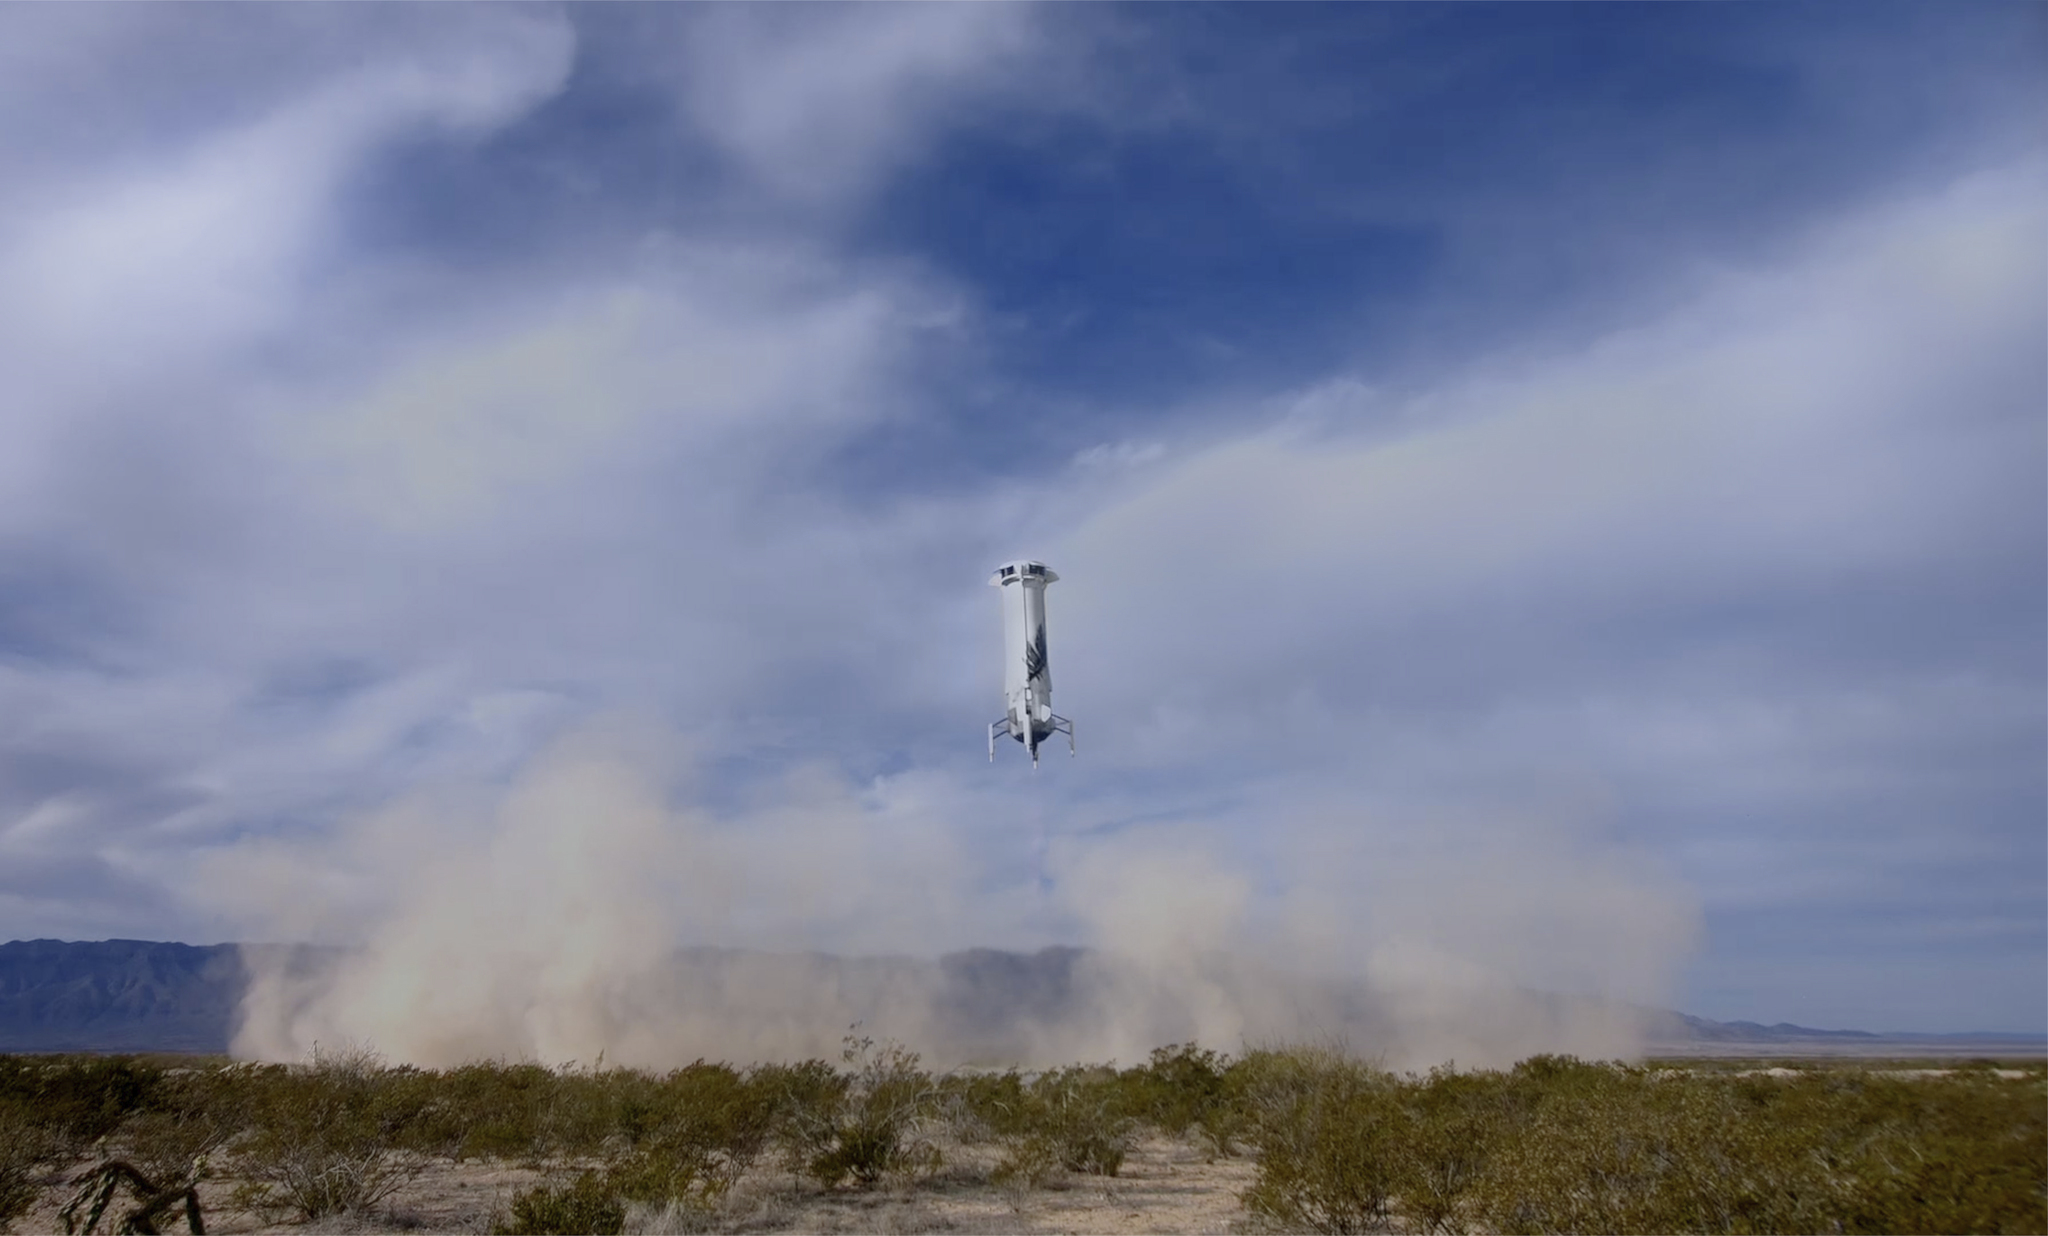
For Tuesday’s return-to-flight mission, the New Shepard rocket ignited its BE-3PM engine and climbed away from Blue Origin’s remote launch site near Van Horn, Texas, at 10:42 am CST (16:42 UTC). The hydrogen-fueled engine fired for more than two minutes, then shut down as scheduled as the rocket continued coasting upward, reaching an altitude of more than 347,000 feet (106 kilometers). The booster returned for a precision propulsive landing a short distance from the launch pad, and Blue Origin’s capsule deployed three parachutes to settle onto the desert floor, completing a 10-minute up-and-down flight. Blue Origin has launched 24 missions with its reusable New Shepard rocket, including six flights carrying people just over the Karman line, the internationally recognized boundary of space 100 kilometers above Earth.

Read more of this story at Slashdot.


Source: Slashdot – Blue Origin’s Suborbital Rocket Flies For First Time In 15 Months

Ministry of Justice Plans To Digitize Then Destroy 100 Million Historical Wills

“The Ministry of Justice is consulting on digitizing and then throwing away about 100 million paper originals of the last wills and testaments of British people dating back more than 150 years in an effort to save 4.5 million pounds a year,” reports Robert Booth via The Guardian. Leading historians are calling these plans “sheer vandalism” and “insane.” From the report: Ministers believe digitisation will speed up access to the papers, but the proposal has provoked a backlash among historians and archivists who took to X to decry it as “bananas” and “a seriously bad idea.” The government is proposing to keep the originals of some wills of “famous people” — likely including those of Charles Darwin, Charles Dickens and Diana, Princess of Wales — but others would be destroyed after 25 years and only a digital copy would be kept. It is feared that wills of ordinary people, some of whom may become historically significant in the future, risk being lost.

Wills are considered essential documents, particularly for social historians and genealogists, as they capture what people considered important at the time and reveal unknown family links. The proposal comes amid growing concern at the fragility of digital archives, after a cyber-attack on the British Library left the online catalogue and digitized documents unavailable to users since late October. “We are advocates of digitization but not at the cost of destroying originals,” says Natalie Pithers, interim co-chief executive of the Society of Genealogists. “In any digitization projects mistakes get made. We don’t know what further information could be gained in the future from the original documents. There could be somebody in there who did something extraordinary.”

Read more of this story at Slashdot.


Source: Slashdot – Ministry of Justice Plans To Digitize Then Destroy 100 Million Historical Wills

Canada Lays Out Plan To Phase Out Sales of Gas-Powered Cars, Trucks By 2035

“EVs mandates are coming to Canada whether you like it or not,” writes Slashdot reader Major_Disorder, sharing a report from the Canadian Broadcasting Corporation. “Here is what my Canadian brothers and sisters need to know.” From the report: New regulations being published this week by Environment Minister Steven Guilbeault will effectively end sales of new passenger vehicles powered only by gasoline or diesel in 2035. Guilbeault said the Electric Vehicle Availability Standard will encourage automakers to make more battery-powered cars and trucks available in Canada. “There’s no mistaking it. We are at a tipping point,” he said, noting sizable growth in EV sales in Canada and demand that has previously outstripped the available supply.

Automakers will have the next 12 years to phase out combustion engine cars, trucks and SUVs with a requirement to gradually increase the proportion of electric models they offer for sale each year. The electric-vehicle sales mandate regulations will be published later this week. They are setting up a system in which every automaker will have to show that a minimum percentage of vehicles they offer for sale are fully electric or longer-range plug-in hybrids. It will start with 20 per cent in 2026 and rise slightly to 23 per cent in 2027. After that, the share of EVs will begin to increase much faster, so that by 2028, 34 per cent of all vehicles sold will need to be electric — 43 per cent by 2029 and 60 per cent by 2030. That number keeps rising until it hits 100 per cent in 2035.

Guilbeault said the government is working to revise the national building code to encourage the spread of charging stations. The updated code would ensure that residential buildings constructed after 2025 have the electrical capacity to accommodate the charging stations. […] The policy will be regulated under the Canadian Environmental Protection Act and will issue credits to automakers for the EVs they sell. Generally, a fully electric model will generate one credit, with plug-in hybrids getting partial or full credit depending on how far they can go on a single charge. Manufacturers that sell more EVs than they need to meet each year’s target can either bank those credits to meet their targets in future years, or sell them to companies that didn’t sell enough. They can also cover up to 10 per cent of the credits they need each year by investing in public fast-charging stations. Every $20,000 spent on DC fast chargers that are operating before 2027 can earn the equivalent of one credit. Automakers that come up short for their sales requirements will be able to cover the difference by buying credits from others who exceed their targets, or by investing in charging stations. Automakers can start earning some credits toward their 2026 and 2027 targets over the next two years — a bid by the government to encourage a faster transition.

Read more of this story at Slashdot.


Source: Slashdot – Canada Lays Out Plan To Phase Out Sales of Gas-Powered Cars, Trucks By 2035

Next Beeper Mini Fix Requires Users To Have a Mac

Juli Clover reports via MacRumors: The developers behind Beeper Mini are continuing with their effort to make iMessage for Android function despite Apple’s mitigations, and the latest “fix” requires Beeper Mini users to have access to a Mac. On Reddit, the Beeper Mini team says that the Mac-based fix coming on December 20 stabilizes iMessage for Beeper Cloud and Mini, and it “works well” and “is very reliable.”

It is unclear how many Android users have a Mac or have a friend with a Mac to rely on, but the fix requires using a Mac to connect to iMessage on Beeper. According to Beeper Mini’s developers, registration data from an actual Mac has to be sent to Apple to use iMessage on Beeper. Beeper has been using its own Mac servers to provide that information to Apple, but that resulted in thousands of Beeper users having the same registration info, which was an “easy target for Apple.”

The Beeper update will instead generate unique registration data for each Mac, making it harder for Apple to tell which users are accessing iMessage through an Android device. The Beeper Mini team says that registration data is “only used to indicate that a Mac is available during registration” and that the Mac will not be given access to an account or messages: “If you do not have access to a Mac computer, but have a friend on Beeper with a Mac, you can ask them if you can use their registration data. In our testing, 10-20 iMessage users can safely use the same registration data.” With the fix, Beeper Cloud and Beeper Mini users will once again be able to use iMessage on Android, but only with email addresses and not with phone numbers.

Read more of this story at Slashdot.


Source: Slashdot – Next Beeper Mini Fix Requires Users To Have a Mac

TomTom Creates AI-Based Conversational Assistant For Vehicles With Microsoft

An anonymous reader writes: Digital mapping specialist TomTom said on Tuesday it has partnered with tech giant Microsoft to create an artificial intelligence (AI)-powered conversational assistant for vehicles. The assistant will allow users to “converse naturally with their vehicles” and enable voice interaction with infotainment, location search, and vehicle command systems, the company said.

TomTom, which competes with Google Maps and the world’s biggest mapping platform HERE, used various Microsoft services like its Azure OpenAI Service to create the voice assistant. The Microsoft Azure OpenAI Service allows enterprises to leverage ChatGPT maker OpenAI’s large language models (LLM). The voice assistant can be integrated into other automotive infotainment systems and is also built into TomTom’s Digital Cockpit, an open, modular in-vehicle infotainment platform, the Dutch map maker said. The company began working with Microsoft in 2016, when it first started powering Azure Maps location services.

Read more of this story at Slashdot.


Source: Slashdot – TomTom Creates AI-Based Conversational Assistant For Vehicles With Microsoft

Microsoft Releases Downloadable Tool To Remove Unwanted HP Printer Software

Longtime Slashdot reader UnknowingFool writes: Microsoft has released a new software tool to remove printer software from HP that was installed without user permission or system need. A few weeks ago, users noticed that Windows Update installed HP printer software even if they did not have HP printers or printers at all. Affecting Windows 10 and 11, consumers reported that this update sometimes caused problems as it could rename their non-HP printers as HP printers causing some printing features to be inaccessible. Microsoft has not disclosed the root cause of the issue. The fix released by Microsoft requires users to download and run a dedicated troubleshooting tool available from Microsoft’s support site. “There are four different versions of the troubleshooter, depending on whether you have the 32- or 64-bit version of an Arm or x86 version of Windows,” notes Ars Technica. “Microsoft will also release an additional recommended troubleshooting tool ‘in the coming weeks’ that will fix the problem in Windows 11 upon a user’s request without requiring the download of a separate tool.”

Read more of this story at Slashdot.


Source: Slashdot – Microsoft Releases Downloadable Tool To Remove Unwanted HP Printer Software

Xfinity waited 13 days to patch critical Citrix Bleed 0-day. Now it’s paying the price

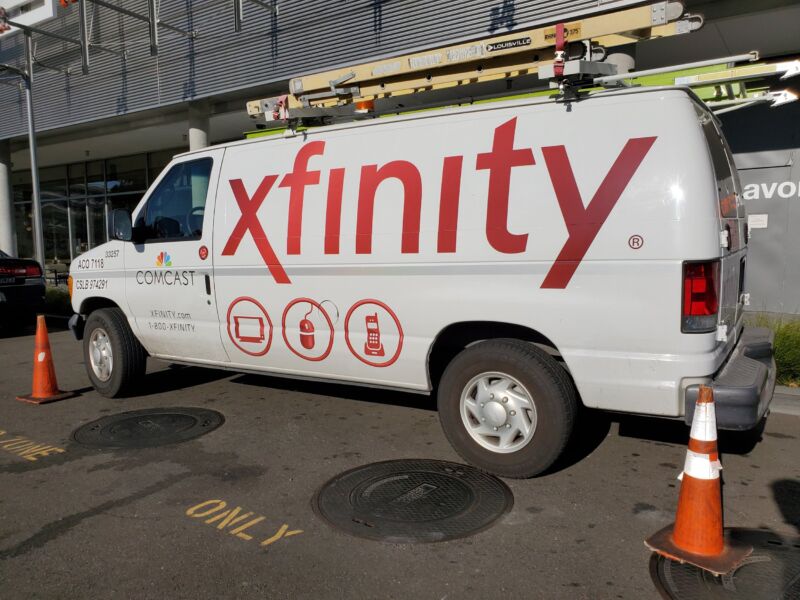
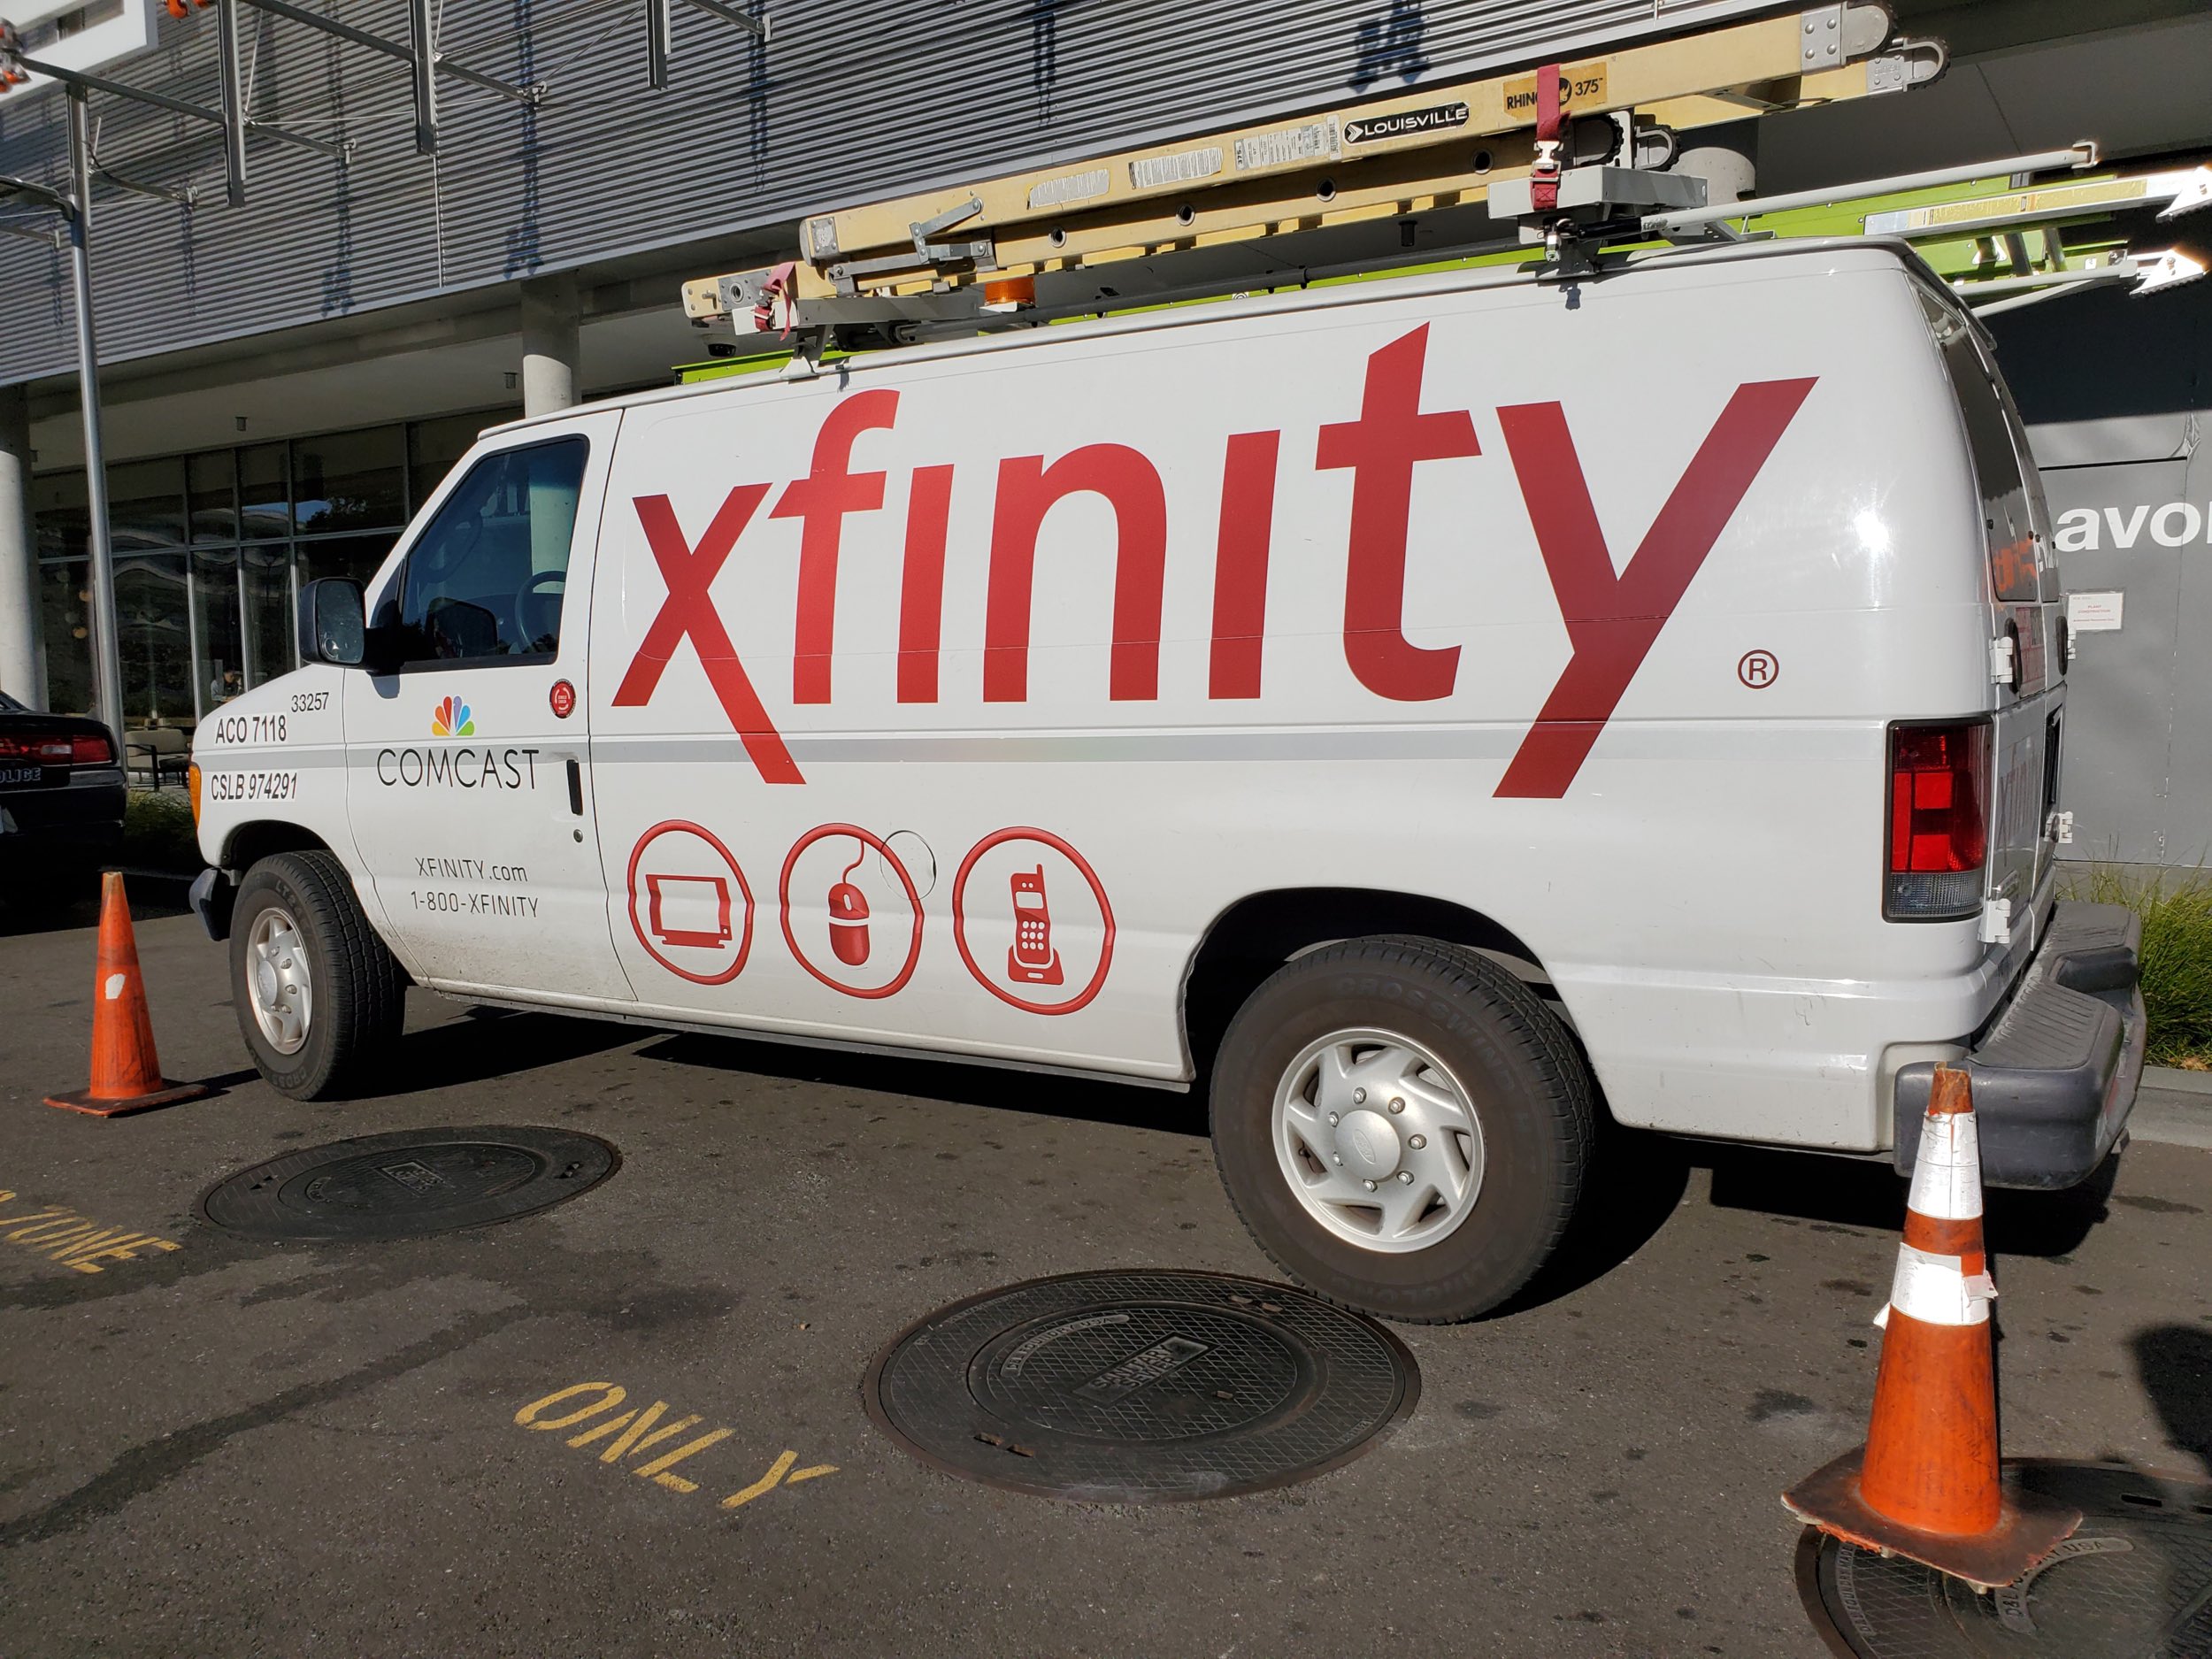
A parked Comcast service van with the

Enlarge / A Comcast Xfinity service van in San Ramon, California on February 25, 2020. (credit: Getty Images | Smith Collection/Gado )

Comcast waited 13 days to patch its network against a high-severity vulnerability, a lapse that allowed hackers to make off with password data and other sensitive information belonging to 36 million Xfinity customers.

The breach, which was carried out by exploiting a vulnerability in network hardware sold by Citrix, gave hackers access to usernames and cryptographically hashed passwords for 35.9 million Xfinity customers, the cable TV and Internet provider said in a notification filed Monday with the Maine attorney general’s office. Citrix disclosed the vulnerability and issued a patch on October 10. Eight days later, researchers reported that the vulnerability, tracked as CVE-2023-4966 and by the name Citrix Bleed, had been under active exploitation since August. Comcast didn’t patch its network until October 23, 13 days after a patch became available and five days after the report of the in-the-wild attacks exploiting it.

“However, we subsequently discovered that prior to mitigation, between October 16 and October 19, 2023, there was unauthorized access to some of our internal systems that we concluded was a result of this vulnerability,” an accompanying notice stated. “We notified federal law enforcement and conducted an investigation into the nature and scope of the incident. On November 16, 2023, it was determined that information was likely acquired.”

Read 6 remaining paragraphs | Comments


Source: Ars Technica – Xfinity waited 13 days to patch critical Citrix Bleed 0-day. Now it’s paying the price

Magic: The Gathering Formally Bans the Use of Generative AI in 'Final' Products

An error in judgement earlier this year—when a D&D artist confirmed they had used generative AI programs to finish several pieces of art included in the sourcebook Glory of the Giants—saw Wizards of the Coast publicly ban the use of AI tools in the process of creating art for the venerable TTRPG. Now, the publisher is…

Read more…


Source: Gizmodo – Magic: The Gathering Formally Bans the Use of Generative AI in ‘Final’ Products

10 Movies to Stream Tonight If You Can't Stand Christmas

Christmas horror movies are never not popular—but what about those holiday-themed dramas, film noirs, and action comedies that never seem to surface on festive watch lists? We’ve gathered 10 movies to stream if all the traditional titles make you want to gouge your eyes out with candy canes.

Read more…


Source: Gizmodo – 10 Movies to Stream Tonight If You Can’t Stand Christmas

Binance To Pay $2.7 Billion Fine To CFTC For Evading Federal Law

Binance will pay $2.7 billion to the Commodity Futures Trading Commission (CFTC) for evading federal law and operating an illegal derivatives exchange. Meanwhile, the cryptocurrency exchange’s founder, Changpeng “CZ” Zhao, will pay $150 million.

“The court finds Zhao and Binance violated the Commodity Exchange Act (CEA) and CFTC regulations, imposes a $150 million civil monetary penalty personally against Zhao, and requires Binance to disgorge $1.35 billion of ill-gotten transaction fees and pay a $1.35 billion penalty to the CFTC,” wrote the CFTC in a statement. CoinTelegraph reports: The approved settlement marks the conclusion of a long-running case against CZ and Binance by the CFTC. On Nov. 21, CZ agreed to step down from his role at the helm of Binance as part of a wider settlement with the U.S. Department of Justice, the Treasury Department and the CFTC. On the same day, Zhao pleaded guilty to several civil charges and one criminal charge relating to Anti-Money Laundering laws. On Dec. 7, CZ was ordered to remain in the U.S. until his Feb. 23, 2024 sentencing date. He faces up to 18 months in prison on money laundering charges and has agreed not to appeal any potential sentence up to that length.

As part of the settlement, both CZ and Binance have agreed to take further steps to ensure Know Your Customer measures are maintained on the exchange as well as requiring Binance to implement a formalized corporate governance structure, including a board of directors with independent members, a compliance committee and an audit committee. The court also made a separate order for Binance’s former chief compliance officer, Samuel Lim, to pay a $1.5 million civil monetary penalty for “aiding and abetting Binance’s violations and engaging in activities outside of the U. S. to willfully evade or attempt to evade U.S. law.”

Read more of this story at Slashdot.


Source: Slashdot – Binance To Pay .7 Billion Fine To CFTC For Evading Federal Law

Blue Origin’s suborbital rocket flies for first time in 15 months

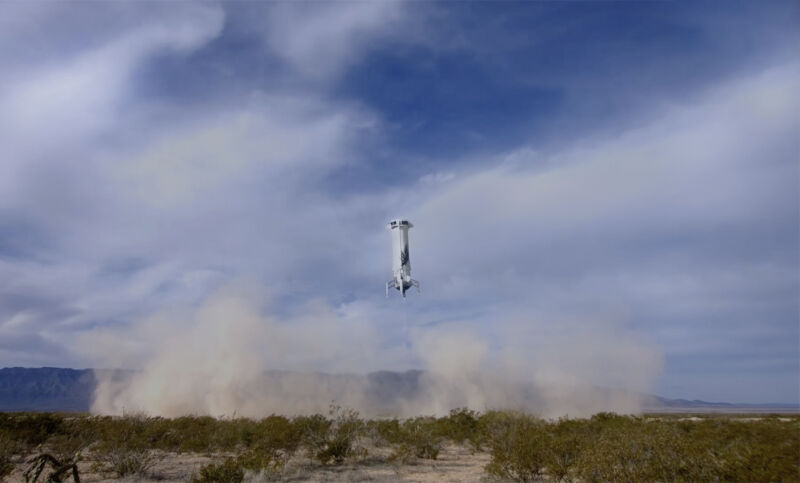
Blue Origin's New Shepard booster comes in for landing in West Texas at the conclusion of Tuesday's suborbital flight.

Enlarge / Blue Origin’s New Shepard booster comes in for landing in West Texas at the conclusion of Tuesday’s suborbital flight. (credit: Blue Origin)

With redesigned engine components, Blue Origin’s New Shepard rocket took off from West Texas and flew to the edge of space on Tuesday with a package of scientific research and technology demonstration experiments.

This was the first flight of Blue Origin’s 60-foot-tall (18-meter) New Shepard rocket since September 12, 2022, when an engine failure destroyed the booster and triggered an in-flight abort for the vehicle’s pressurized capsule. There were no passengers aboard for that mission, and the capsule safely separated from the failed booster and parachuted to a controlled landing.

The flight on Tuesday also didn’t carry people. Instead, Blue Origin, Jeff Bezos’s space company, lofted 33 payloads from NASA, research institutions, and commercial companies. Some of these payloads were flown again on Tuesday’s launch after failing to reach space on the failed New Shepard mission last year. Among these payloads were an experiment to demonstrate hydrogen fuel cell technology in microgravity and an investigation studying the strength of planetary soils under different gravity conditions.

Read 15 remaining paragraphs | Comments


Source: Ars Technica – Blue Origin’s suborbital rocket flies for first time in 15 months

INTERPOL Arrests 3,500 Suspects in Sweeping Cybercrime Operation

Interpol, an international police organization, has arrested nearly 3,500 people allegedly connected to cybercrime in a sweeping operation announced on Tuesday. $300 million worth of assets across 34 countries were reportedly seized. The operation, Haechi IV, blocked over 80,000 suspicious bank accounts and warned…

Read more…


Source: Gizmodo – INTERPOL Arrests 3,500 Suspects in Sweeping Cybercrime Operation

Meta says a bug briefly blocked news for Canadian users on Threads

Meta has fixed a bug that temporarily prevented some Threads users in Canada from reading and sharing news on the app, a company spokesperson told Engadget. Even though Meta pulled news content from Canadian users’ Facebook and Instagram feeds earlier this year, the block hasn’t carried over to Threads.

But a number of Threads users wondered if that had changed when they began to see alerts that suggested otherwise. “People in Canada can’t view this content,” a notice with Threads branding read. “Content from news publishers can’t be viewed in Canada in response to Canadian government legislation.”

It’s unclear how widespread the bug was or how long it was happening. Reports of the issue seemed to crop up on Monday, with some users still unable to view links as of Tuesday morning. “Well… that sucks. @meta is escalating their news blocking in Canada, previously only on Facebook and Instagram, now on Threads,” Pedro Marques wrote in a post Monday.

Threads appeared to briefly block news for users in Canada. Meta says it was a big.
Screenshot via Threads

A Meta spokesperson told Engadget that the Online News Act’s framework doesn’t apply to Threads, at least for now. Still, the fact that the notice appeared at all has prompted speculation that the company could eventually block news content on Threads as well.

Over the last few years, the world’s largest tech companies have tussled with countries about paying for news. In 2021, for instance, Facebook stopped people in Australia from sharing news links, while Google threatened to stop showcasing content from Australian news publishers on Google News. Both companies, however, eventually reached agreements and agreed to start paying Australian news organizations.

In August, Meta started blocking news on Facebook and Instagram in Canada in response to the country’s Online News Act that requires platforms to pay news organizations to make up for lost advertising revenue. Google, which had earlier pledged to block news links in the country, eventually reached a deal with the country’s government and agreed to pay Canadian publishers around $100 million a year, according to the Canadian Broadcasting Corporation.

Though Meta has downplayed the significance of news on Threads — Instagram head Adam Mosseri said earlier this year the company didn’t want to “amplify news” on the platform — blocking news on Threads could have a more dramatic impact on Threads than it has in Instagram and Facebook. The app has grown to about 100 million users as more people look for Twitter alternatives.

Blocking news, though, could make the app a lot less useful for users and publishers, who have started to see more engagement from the service. “How will Threads replace Twitter when I can’t even click on a news story in Canada without getting blocked by Meta,” a Threads user named dexter wrote after encountering the bug.

This article originally appeared on Engadget at https://www.engadget.com/meta-says-a-bug-briefly-blocked-news-for-canadian-users-on-threads-220230063.html?src=rss

Source: Engadget – Meta says a bug briefly blocked news for Canadian users on Threads

Meta's News Ban In Canada Remains As Online News Act Goes Into Effect

An anonymous reader quotes a report from the BBC: A bill that mandates tech giants pay news outlets for their content has come into effect in Canada amid an ongoing dispute with Facebook and Instagram owner Meta over the law. Some have hailed it as a game-changer that sets out a permanent framework that will see a steady drip of funds from wealthy tech companies to Canada’s struggling journalism industry. But it has also been met with resistance by Google and Meta — the only two companies big enough to be encompassed by the law. In response, over the summer, Meta blocked access to news on Facebook and Instagram for Canadians. Google looked set to follow, but after months of talks, the federal government was able to negotiate a deal with the search giant as the company has agreed to pay Canadian news outlets $75 million annually.

No such agreement appears to be on the horizon with Meta, which has called the law “fundamentally flawed.” If Meta is refusing to budge, so is the government. “We will continue to push Meta, that makes billions of dollars in profits, even though it is refusing to invest in the journalistic rigor and stability of the media,” Prime Minister Justin Trudeau told reporters on Friday. According to a study by the Media Ecosystem Observatory, the views of Canadian news on Facebook dropped 90% after the company blocked access to news on the platform. Local news outlets have been hit particularly hard.

“The loss of journalism on Meta platforms represents a significant decline in the resiliency of the Canadian media ecosystem,” said Taylor Owen, a researcher at McGill and the co-author of the study. He believes it also hurts Meta’s brand in the long run, pointing to the fact that the Canada’s federal government, as well as that of British Columbia, other municipalities and a handful of large Canadian corporations, have all pulled their advertising off Facebook and Instagram in retaliation.

Read more of this story at Slashdot.


Source: Slashdot – Meta’s News Ban In Canada Remains As Online News Act Goes Into Effect

The Google Play Store Ruling Is Bad News for Longtime Android Phone Users

Last week, Epic won a years-long suit against Google for anti-competitive practices within the Play Store. We were all left wondering: what would happen to Android’s app store moving forward?

Today, Google laid out what’s happening in its Keyword blog, and it’s all in time for the holiday when we can finally slow down…

Read more…


Source: Gizmodo – The Google Play Store Ruling Is Bad News for Longtime Android Phone Users

Wolverine-developer Insomniac Games sees 1.67TB of secrets leaked in data breach

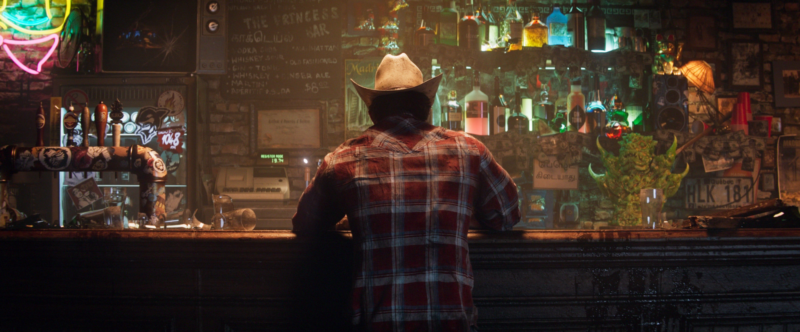
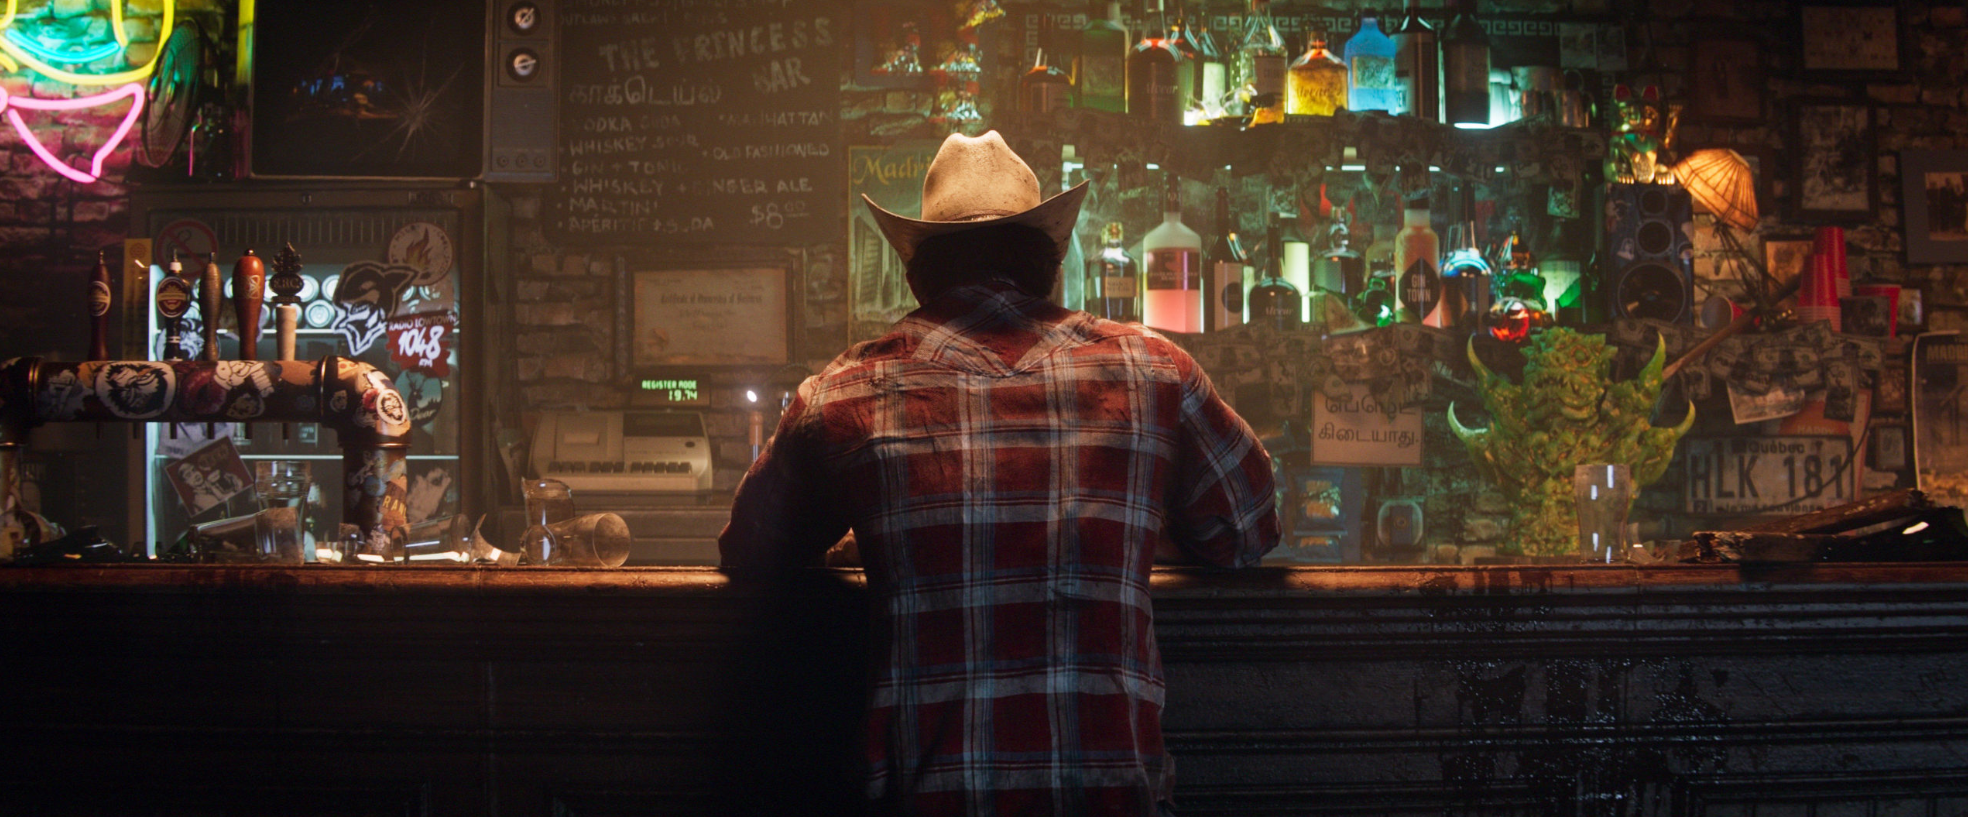
Wolverine sits at a bar in a game screenshot

Enlarge / An officially released image for Insomniac Games’ upcoming game Wolverine. (credit: Insomniac Games)

Acclaimed Sony-owned game development studio Insomniac Games became the victim of a large-scale ransomware attack this week, as initially reported by Cyber Daily. Ransomware group Rhysida dumped 1.67TB of data, including assets and story spoilers from unreleased games, a road map of upcoming titles, internal company communications, employees’ personal data such as passport scans and compensation figures, and much more.

The gang said it chose Insomniac because, as a large and successful studio, it made an attractive target for a money grab. The ransom was $2 million, and Insomniac refused to pay it.

As a result, a trove of emails, Slack messages, slideshow presentations, and more hit the web. Notably, these included screenshots and assets from the studio’s upcoming Wolverine game, as well as confirmation that Wolverine is planned to be the first in a trilogy of games starring X-Men characters. The materials also revealed that the company is working on another Ratchet & Clank game and a new Spider-Man sequel.

Read 7 remaining paragraphs | Comments


Source: Ars Technica – Wolverine-developer Insomniac Games sees 1.67TB of secrets leaked in data breach