Discover the top 5 free and open source HTML linter tools to enhance your web development process. Improve code quality and ensure standards compliance today!
The post 5 Best Free and Open Source HTML Linter Tools appeared first on Linux Today.

Discover the top 5 free and open source HTML linter tools to enhance your web development process. Improve code quality and ensure standards compliance today!
The post 5 Best Free and Open Source HTML Linter Tools appeared first on Linux Today.
Attempted exploit was a feeble effort to target Windows usersSomeone managed to insert a compromised file into the downloads section of the website for Xubuntu, the official Ubuntu flavor with the Xfce desktop environment. The malware was designed to steal cryptocurrency, but so far, there are no reports of actual theft.…
SpaceX surpassed the 10,000-satellite milestone for its Starlink constellation after two Falcon 9 launches on Oct. 19 added 56 more satellites to orbit. The company now operates about two-thirds of all active satellites worldwide and continues to break reuse records. Space.com reports: A Falcon 9 rocket carrying 28 Starlink internet satellites lifted off from California’s Vandenberg Space Force Base today at 3:24 p.m. EDT (1924 GMT; 12:24 p.m. local California time). Those 28 included the 10,000th Starlink spacecraft ever to reach orbit, which a SpaceX employee noted on the company’s launch webcast: “From Tintin to 10,000! Go Starlink, go Falcon, go SpaceX!”
It was also the 132nd Falcon 9 liftoff of the year, equaling the mark set by the rocket last year — and there are still nearly 2.5 months to go in 2025. […] This launch was the second of the day for SpaceX; less than two hours earlier, another Falcon 9 sent 28 more Starlink satellites up from Florida’s Space Coast. That earlier liftoff was the 31st for that Falcon 9’s first stage, setting a new reuse record.


Read more of this story at Slashdot.
Imagine being a Web surfer trying to locate actual journalism about “linux” this week.
An anonymous reader quotes a report from Wired: The National Transportation Safety Board confirmed Sunday that it is investigating an airliner that was struck by an object in its windscreen, mid-flight, over Utah. “NTSB gathering radar, weather, flight recorder data,” the federal agency said on the social media site X. “Windscreen being sent to NTSB laboratories for examination.” The strike occurred Thursday, during a United Airlines flight from Denver to Los Angeles. Images shared on social media showed that one of the two large windows at the front of a 737 MAX aircraft was significantly cracked. Related images also reveal a pilot’s arm that has been cut multiple times by what appear to be small shards of glass.
The captain of the flight reportedly described the object that hit the plane as “space debris.” This has not been confirmed, however. After the impact, the aircraft safely landed at Salt Lake City International Airport after being diverted. Images of the strike showed that an object made a forceful impact near the upper-right part of the window, showing damage to the metal frame. Because aircraft windows are multiple layers thick, with laminate in between, the window pane did not shatter completely. The aircraft was flying above 30,000 feet — likely around 36,000 feet — and the cockpit apparently maintained its cabin pressure.


Read more of this story at Slashdot.
HackerBox has released Issue 0119, titled “Geopositioning.” This edition marks ten years of the subscription series and focuses on satellite positioning and mapping through the ESP-WROOM-32 system-on-chip and the Thrifty Yeti Locator (TYL) platform. The kit combines hardware assembly with firmware development in the Arduino IDE to demonstrate GNSS and geolocation principles. According to the […]
The mysterious impact of a United Airlines aircraft in flight last week has sparked plenty of theories as to its cause, from space debris to high-flying birds.
However the question of what happened to flight 1093, and its severely damaged front window, appears to be answered in the form of a weather balloon.
“I think this was a WindBorne balloon,” Kai Marshland, co-founder of the weather prediction company WindBorne Systems, told Ars in an email on Monday evening. “We learned about UA1093 and the potential that it was related to one of our balloons at 11 pm PT on Sunday and immediately looked into it. At 6 am PT, we sent our preliminary investigation to both NTSB and FAA, and are working with both of them to investigate further.”
The most unexpected surprise today was AMD releasing ROCm 7.9 as a new technology preview / development branch for the open-source ROCm GPU compute stack just one month after formally releasing ROCm 7.0. While not a fan of how they handled the version discontinuity, ROCm 7.9 has been working out well in my very initial tests on AMD Ryzen AI Max “Strix Halo”…
It was to much surprise waking up this morning and seeing the Servo 0.0.1 release for this Rust-based web layout engine that began as a Mozilla project and is now being developed independently via Linux Foundation Europe and other parties…
Investigators recovered the OceanGate Titan sub’s underwater camera nearly intact, discovering a SanDisk SD card that survived the 2023 implosion and still contained 12 images and 9 videos. TechSpot reports: Scott Manley, the science communication YouTuber, gamer, astrophysicist, and programmer, posted about the latest find: a hardened SubC-branded Rayfin Mk2 Benthic Camera containing the undamaged SD card. The titanium and synthetic sapphire crystal camera is rated to withstand depths of up to 6,000 meters (19,685 feet) — the Titan imploded at around 3,300 meters (10,827 feet). The casing is intact, though the lens is shattered and the PCBs are slightly damaged.
Incredibly the SD card inside the camera was undamaged. Tom’s Hardware reports that it’s almost certainly a SanDisk Extreme Pro 512GB, which costs around $62 on Amazon. The camera’s SD card was found to be fully encrypted, divided into a small partition for operating system updates and a larger one for user data. Due to impact damage from the accident, several components of the system-on-module (SOM) board — including connectors and the microcontroller — were broken, complicating the data extraction process. […] After determining the data wasn’t encrypted beyond the file system level, they successfully accessed the SD card contents using the manufacturer’s proprietary equipment and procedures.


Read more of this story at Slashdot.
MAAP has launched its latest jersey, the Pro Aero, which it claims will save you between 6 and 8 watts, equivalent to as much as 60 seconds over 100km, thanks to its aero features.
The new jersey has been developed alongside the Jayco AlUla men’s and Liv AlUla Jayco women’s WorldTour pro teams, which are kitted out by MAAP.
Between them, the two teams have scored four victories during the 2025 season, including Ben O’Connor’s summit win on the Col de la Loze on Stage 18 of the Tour de France.
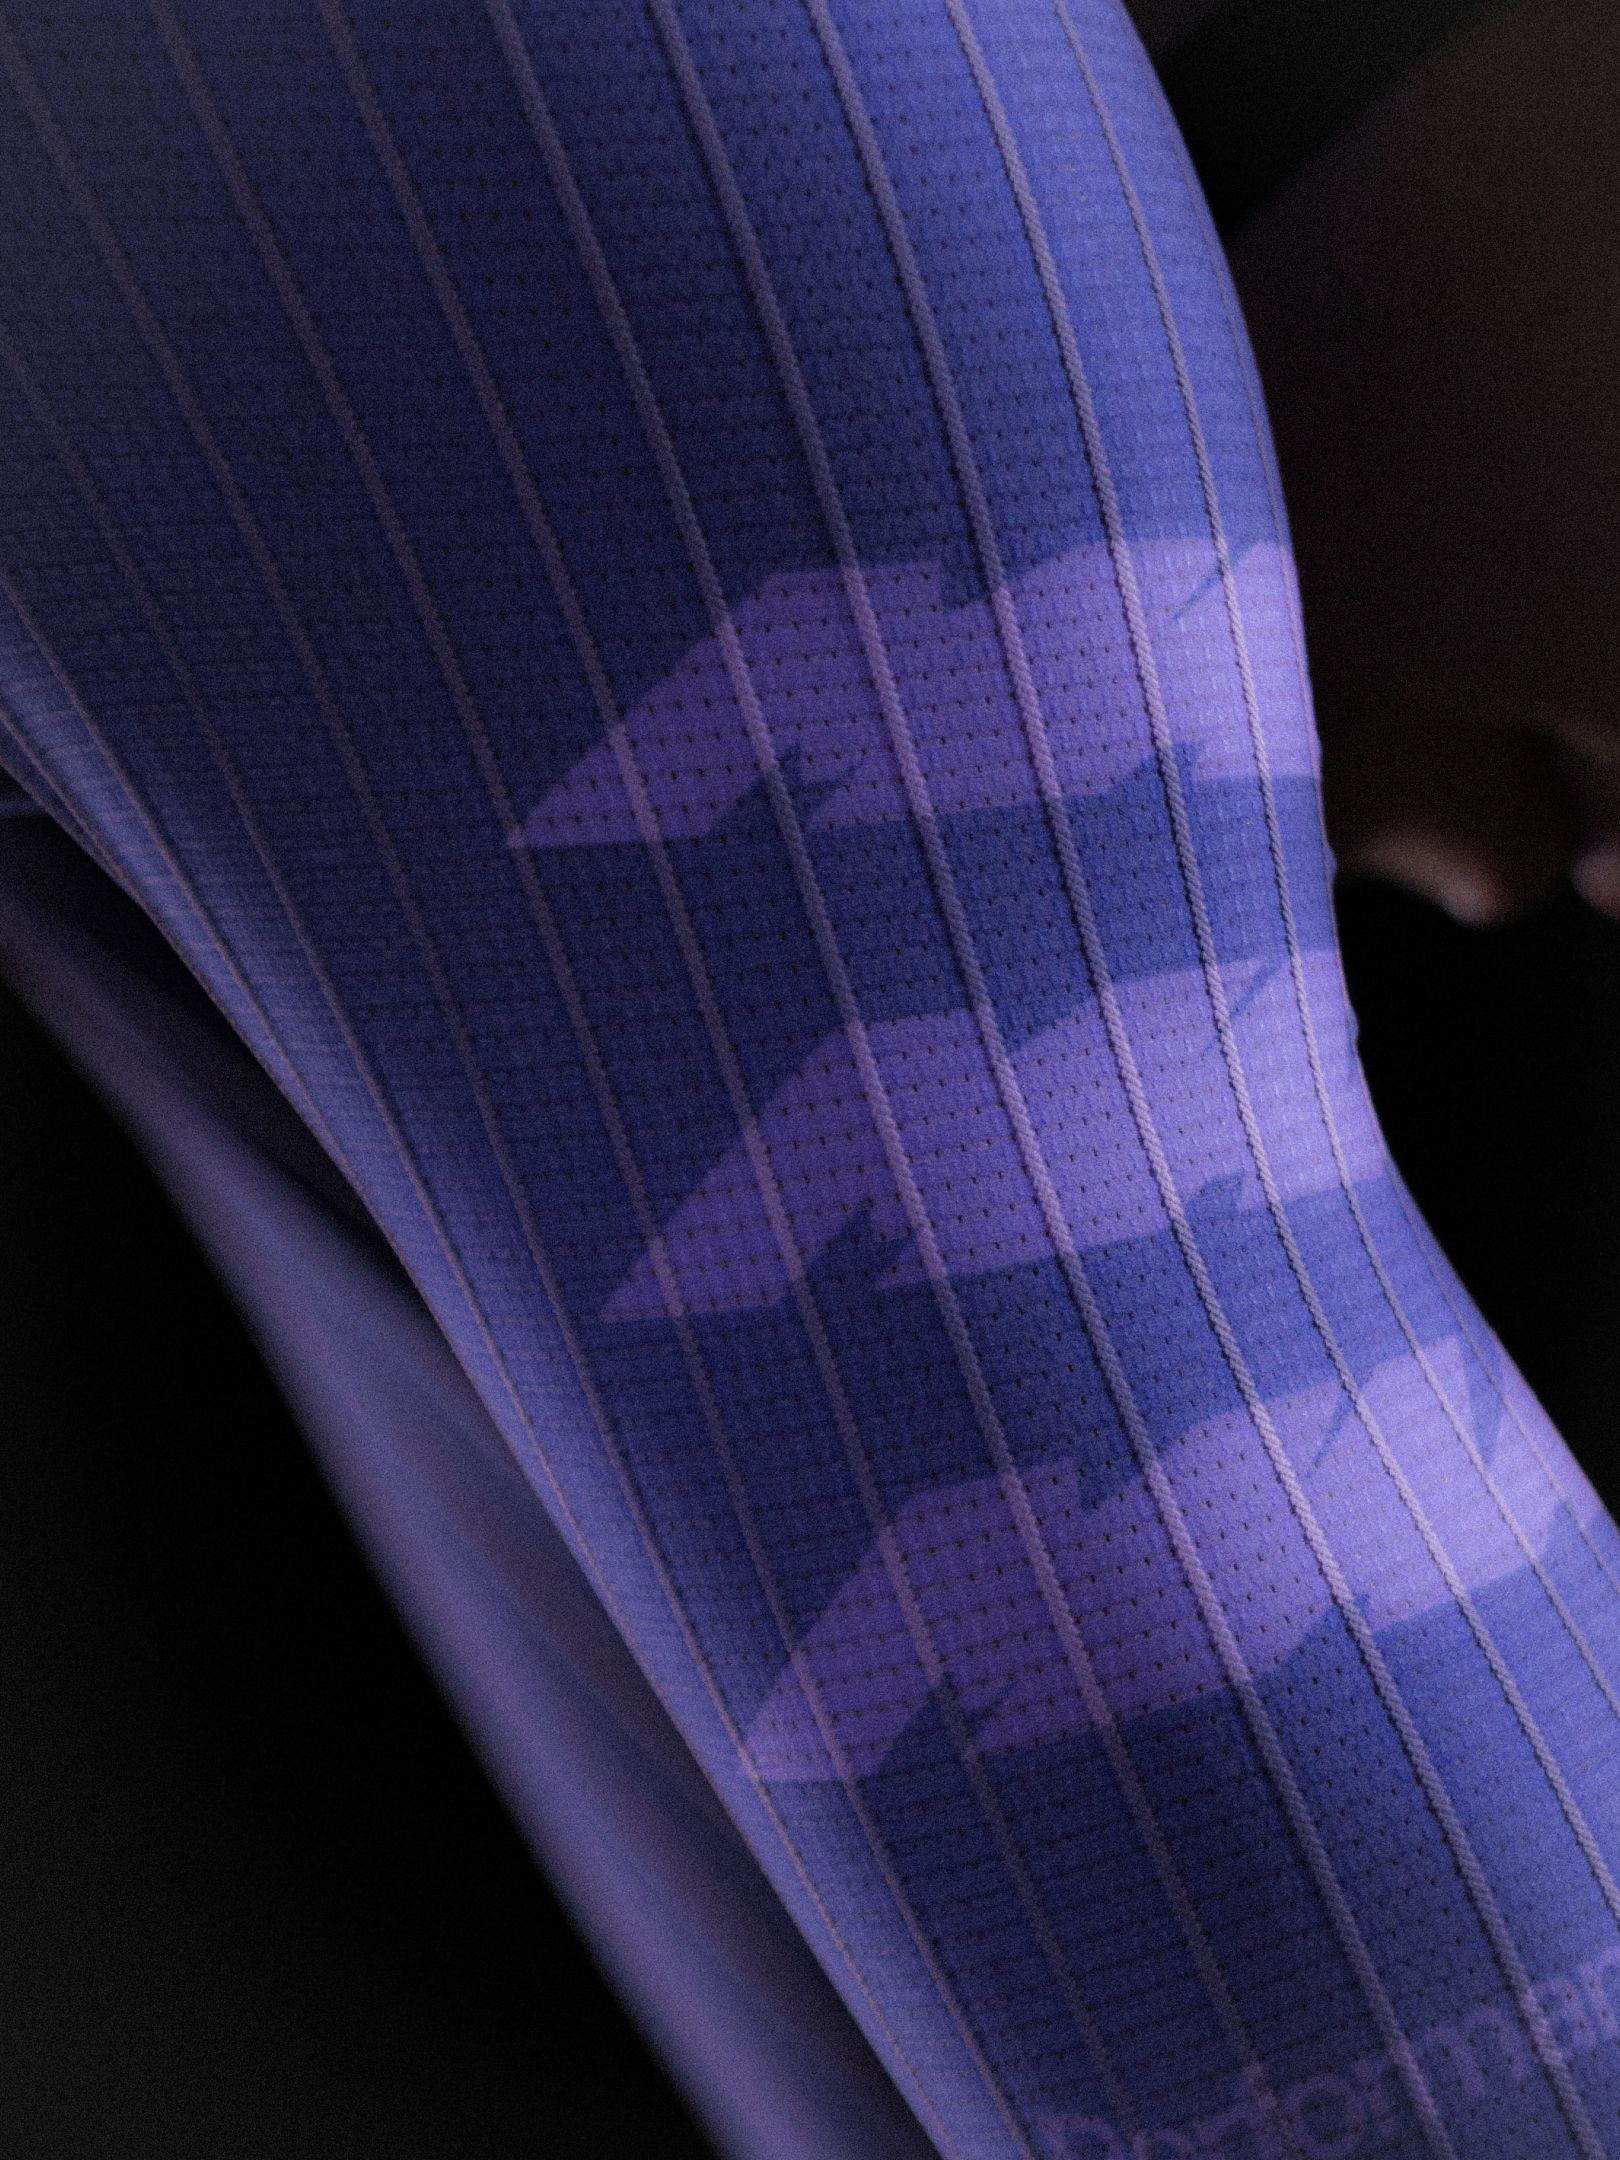
MAAP uses a proprietary thin aero fabric, which it calls Aatero Flyte, which includes woven ribs in the sleeves that it claims reduce airflow turbulence.
MAAP says its new fabric was the culmination of testing of 16 prototypes and is only 20 microns thick, with a weight of 100g/m2.
The bad news is MAAP says the aero gains are only achieved at riding speeds of over 40km/h. The good news is it states the aero features are woven into the fabric, and so are permanent and won’t wear out or degrade over time.
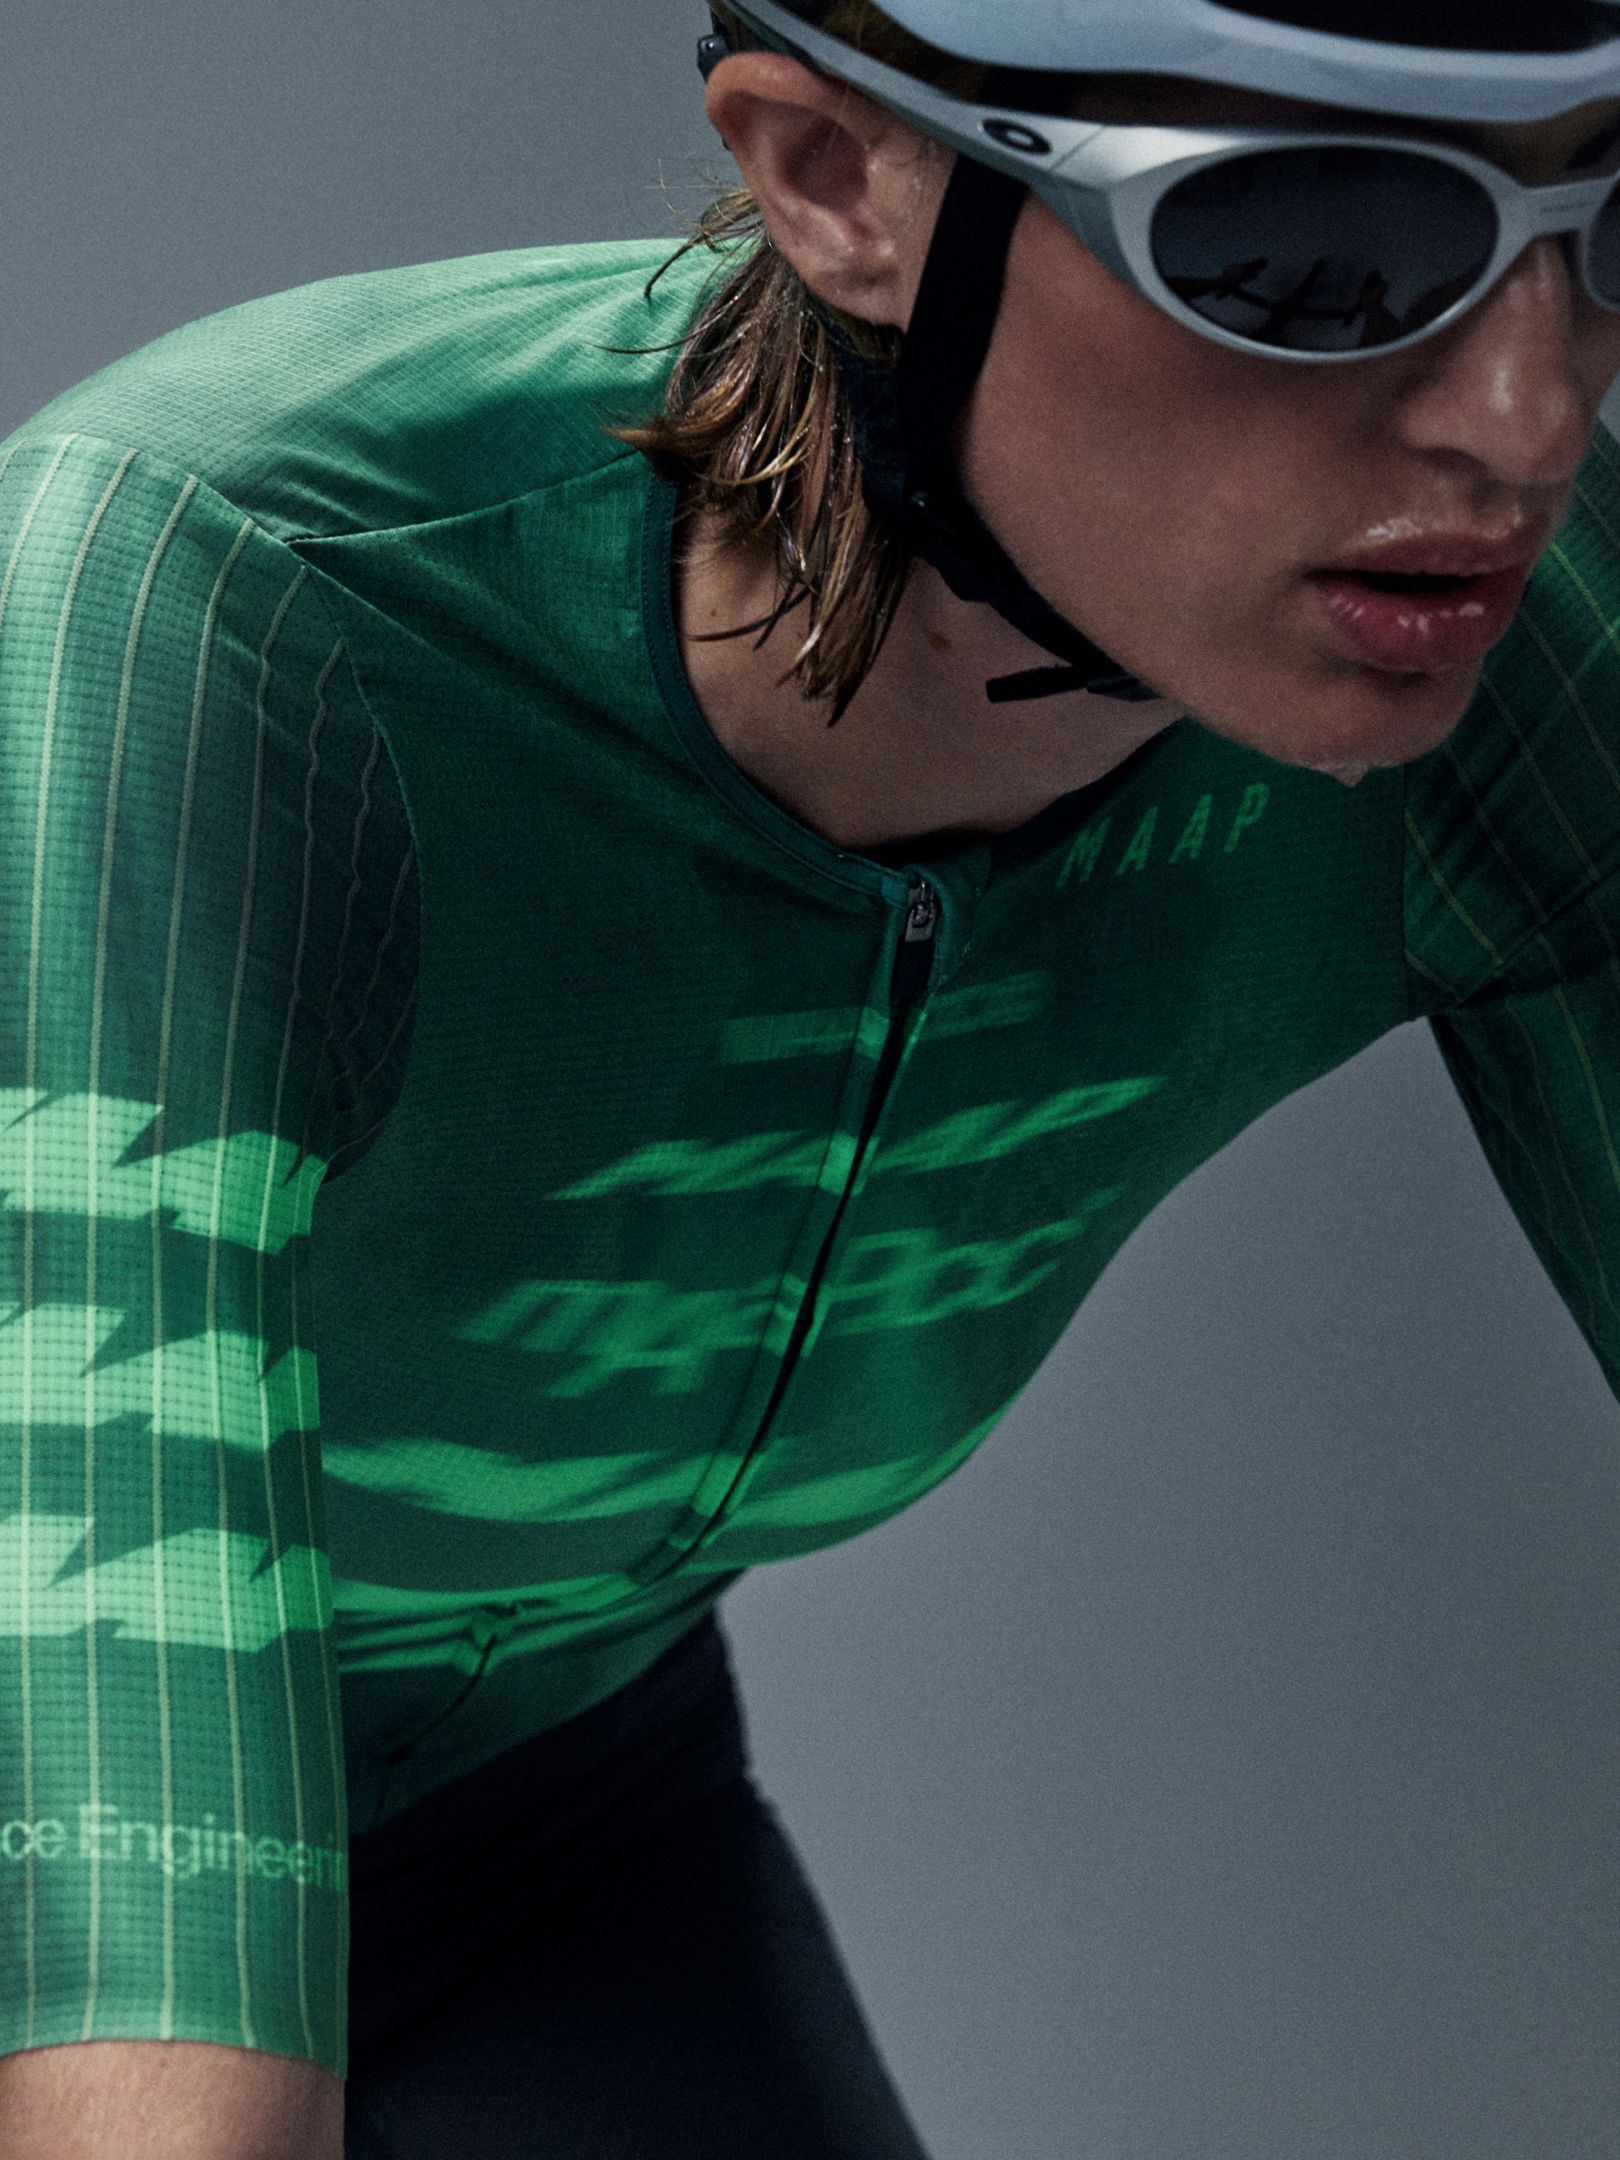
Other features designed to make you faster include raw hems to the sleeves with internal silicone grippers, hydrophobic fibres to increase evaporative cooling, an ergonomic collar and bonded rear pockets.
MAAP says the new jersey, made in Italy, has a lower environmental impact too, thanks to an elastomer made without solvents that reduces chemical use during production, and is more durable and more easily recycled.
You can purchase the MAAP Pro Aero jersey from MAAP’s site, its Lab stores and retailers of its clothing, priced at £210 / $265 / €220 / AU$345. It’s available in MAAP’s usual men’s S to XXL and women’s XXS to XL sizing, and in the purple and green colours shown.
Foreign hackers breached the National Nuclear Security Administration’s Kansas City National Security Campus (KCNSC) by exploiting unpatched Microsoft SharePoint vulnerabilities. The intrusion happened in August and is possibly linked to either Chinese state actors or Russian cybercriminals. CSO Online notes that “roughly 80% of the non-nuclear parts in the nation’s nuclear stockpile originate from KCNSC,” making it “one of the most sensitive facilities in the federal weapons complex.” From the report: The breach targeted a plant that produces the vast majority of critical non-nuclear components for US nuclear weapons under the NNSA, a semi-autonomous agency within the Department of Energy (DOE) that oversees the design, production, and maintenance of the nation’s nuclear weapons. Honeywell Federal Manufacturing & Technologies (FM&T) manages the Kansas City campus under contract to the NNSA. […] The attackers exploited two recently disclosed Microsoft SharePoint vulnerabilities — CVE-2025-53770, a spoofing flaw, and CVE-2025-49704, a remote code execution (RCE) bug — both affecting on-premises servers. Microsoft issued fixes for the vulnerabilities on July 19.
On July 22, the NNSA confirmed it was one of the organizations hit by attacks enabled by the SharePoint flaws. “On Friday, July 18th, the exploitation of a Microsoft SharePoint zero-day vulnerability began affecting the Department of Energy,” a DOE spokesperson said. However, the DOE contended at the time, “The department was minimally impacted due to its widespread use of the Microsoft M365 cloud and very capable cybersecurity systems. A very small number of systems were impacted. All impacted systems are being restored.” By early August, federal responders, including personnel from the NSA, were on-site at the Kansas City facility, the source tells CSO.


Read more of this story at Slashdot.
Over the weekend we wrote about the visually-impressive Tellusim Core SDK being posted to GitHub as a C++ SDK for high-end graphics and compute. The downside was that the Tellusim Core SKD was rather restrictive in only being free for education, free for companies with less than $200k USD in annual revenue, and evaluation purposes. Or you needed to obtain a negotiated license for the software. As a pleasant surprise, OSI-approved open-source projects not backed by for-profit organizations can now openly use this superb graphics SDK…
OpenAI Whisper is a powerful speech recognition system that can transcribe audio files with impressive accuracy. When combined with NVIDIA GPU acceleration through CUDA, Whisper can process audio files significantly faster than CPU-only processing. This guide demonstrates how to install and use Whisper with GPU support on Debian and Ubuntu Linux systems.
An anonymous reader quotes a report from MacRumors: With the fourth betas of iOS 26.1, iPadOS 26.1, and macOS 26.1, Apple has introduced a new setting that’s designed to allow users to customize the look of Liquid Glass. The toggle lets users select from a clear look for Liquid Glass, or a tinted look. Clear is the current Liquid Glass design, which is more transparent and shows the background underneath buttons, bars, and menus, while tinted increases the opacity of Liquid Glass and adds more contrast.
Apple says that the new toggle was added because during the beta testing period over the summer, user feedback suggested that some people would prefer to have a more opaque option for Liquid Glass. The added setting provides additional customization in iOS 26.1, iPadOS 26.1, and macOS Tahoe 26.1. Increasing opacity and adding contrast applies to Liquid Glass throughout the operating system, including in apps and Lock Screen notifications.


Read more of this story at Slashdot.
U.S. Grandmaster and beloved chess commentator Daniel Naroditsky has tragically passed away at the age of 29. “The news has sent shockwaves around the chess community, which is grieving the loss of one of the most beloved and influential voices,” reports Chess.com. From the report: The devastating news was first shared by Naroditsky’s club, Charlotte Chess Center, on Monday, and confirmed by Chess.com with multiple sources: “It is with great sadness that we share the unexpected passing of Daniel Naroditsky. Daniel was a talented chess player, educator, and cherished member of the chess community. He was also a loving son, brother, and loyal friend. We ask for privacy for Daniel’s family during this extremely difficult time. Let us honor Daniel by remembering his passion for chess and the inspiration he brought to us all.”
Naroditsky, who was three weeks away from turning 30, has long been known as one of United States’ most talented players. He achieved his grandmaster title at the age of 18 in 2013, and placed fifth among the highest-ranked juniors in 2015. His last FIDE-rating is 2619, which places him among the top 150 in the world, or the 17th highest-ranked in the United States. He has a peak rating of 2647 from 2017. He leaves a legacy that spans strong over-the-board competition and highly popular chess instruction and commentary on streaming platforms.


Read more of this story at Slashdot.
This is a video of Philip Kaplan discussing the headphones he built with an integrated CD player on top. You can also store extra CDs on spindles attached to the earphones. It includes a remote control, battery pack, LCD display, and a spot to display the CD case of what you’re currently playing so everybody can know what the crazy person is listening to. Now that — that’s a quality product. Would I wear it at the gym? No, but only because I don’t wear over-ear headphones at the gym. I like to hear all the farting so I know where to avoid walking.
Florida Attorney General James Uthmeier has issued criminal subpoenas to Roblox, calling it a “breeding ground for predators” and accusing the platform of profiting while failing to protect children. NBC News reports: The subpoenas will allow prosecutors to gather more information about the alleged criminal activity on the platform, including evidence related to suspected predators and victims, according to Uthmeier. The concerns prompted Roblox to invest heavily in protecting younger users on its platform by tightening messaging rules for children under 13, intensive content moderation and AI-powered monitoring.
In an emailed statement to Reuters, Roblox said it prohibits sharing images and videos in chat, uses filters designed to block the exchange of personal information, and is working to implement age estimation for all users accessing chat features. “While no system is perfect, our trained teams and automated tools continuously monitor communications to detect and remove harmful content,” a Roblox spokesperson said.


Read more of this story at Slashdot.
Home products company Kohler is launching a new Kohler Health division, and its first product is a $599 camera for your toilet. The item, dubbed Dekoda, is equipped with sensors that analyze whatever liquid or solid waste goes into the toilet bowl with “validated machine learning algorithms.” The data, which can offer insights on hydration and gut health as well as detecting the presence of blood, then goes to Kohler Health’s iPhone app, although Android support is in the works. It comes with a magnetic charging pad and a wall-mounted remote that can optionally use Bluetooth fingerprint authorization so that you don’t learn way more than you want to about your guests.
I must salute the PR person who came up with this gem from the release: “By turning the bathroom into a connected, data-informed health and wellness hub, Kohler Health empowers individuals to turn ordinary routines into proactive, personalized experiences.” Because who doesn’t want to be proactive about pee? Health data is great, no arguments here. But this seems like a pretty extreme and expensive way to figure out if you’re drinking enough water. Maybe I’m in the minority with my skepticism, however, because this isn’t the first instance we’ve seen of toilet-bowl tech for better health. Withings introduced a monitor a few years back for analyzing urine streams, which you can buy for a mere $500.
If you’re just that passionate about tracking your biometrics, Dekoda products are expected to ship starting tomorrow. You’ll also need to sign up for a Kohler Health subscription on top of the product cost, and there are individual and family plan options.
This article originally appeared on Engadget at https://www.engadget.com/home/kohlers-dekoda-is-600-camera-for-your-toilet-225942144.html?src=rss
X is finally following through on its long-rumored plans to sell old user handles, and some of the most sought-after usernames could fetch millions of dollars. The company shared more details about and opened a waitlist for its “handle marketplace,” that will enable paying subscribers to request and buy “inactive” handles.
According to the company, X will make two types of “inactive’ handles available: “priority” usernames that may include “full names, multi-word phrases, or alphanumeric combinations” and “rare” handles that consist of “short, generic, or culturally significant names.” Subscribers to X’s Premium+ and Premium Business tiers will eventually be able to request some “priority” handles as part of their subscription. The company says @PizzaEater and @GabrielJones are possible examples of such handles. Notably, this process requires what essentially amounts to an indefinite subscription to X Premium, as the company says it will revoke priority handles if an account’s subscription lapses.
The X Handle Marketplace is our industry-first solution to redistribute handles that are no longer in use.
Eligible Premium subscribers will be able to search and make requests, with both complimentary and paid options available.
— Handle Marketplace (@XHandles) October 19, 2025
The process for acquiring a “rare” handle is a lot less clear. X says that it will offer some rare handles through “public drops” and that those will be given away for free “based on merit” and that multiple users will be able to apply. X will take a user’s engagement and “past contributions” to the platform into account when deciding who gets these handles. The company will also make some handles available for sale via an invitation-only process. These prices will be “fixed” and “determined by a number of factors including popularity of word, character length, and cultural significance.” These usernames could include common one-word usernames like @one, @fly or @compute, according to examples provided by X. They could also be incredibly expensive.
“Some handles are included with a Premium+ or Premium Business subscription,” X wrote in an FAQ. “Others – especially Rare handles – may be priced anywhere from $2,500 to over seven figures, depending on demand and uniqueness.” People who buy a supposedly rare handle will need to have a Premium+ or Premium Business subscription in order to start the process, but won’t be required to maintain one in order to keep the handle.
In a separate “handle transfer agreement,” X describes its handle-buying scheme as an “evolving initiative” that it hopes will be adopted by other social media companies in the future. “We are establishing a new standard for social media handles—a framework we hope the broader industry will adopt, similar to how Community Notes has influenced online transparency,” the company wrote.
Andrew Allemann, the publisher of Domain Name Wire, a publication that tracks the domain name industry, says that there are some similarities between X’s plan to sell handles and the marketplace for expired domains. “For a long time, people have been buying and selling handles off of X, and X hasn’t been getting a cut of that,” he told Engadget. “So in some ways, I think this will get some of the better handles to be more used on the platform.”
But he said he would have concerns about some of the terms in X’s policies, which allow it to “reclaim” handles if they become inactive. The company’s current “inactive account policy” defines an inactive account as one that hasn’t been logged into for 30 days. “I would definitely want a firmer contract if I were to pay money for a handle,” Allemann says. “I would want some rights baked into a contract that says it can’t just be taken away. I certainly want a longer period of inactivity before it can be taken away.”
X also has a history of commandeering desirable handles from users that were actively using them. The company took the @X handle from a San Francisco photographer in 2023 without compensating him, though he was offered “merch” and a tour of X’s headquarters. That same year, it also took the @music handle from a longtime user with more than a half million followers. Last year, the company swiped the @America handle from a reported Donald Trump critic. The handle is now used by Musk’s super PAC.
X’s plan to give away handles based on “merit” raises additional questions about who the platform could decide to reward and penalize. The company didn’t immediately respond to a request for comment.
Allemann says that all social media users should remember they don’t own any of the content they publish on company platforms. “If you create your website, you control it, and people can always come to it. On social media, the single billionaire owner of it could decide they don’t like you, and it’s pretty much within their rights to kick you off, or demote you, or change the algorithm to impact you as well.”
This article originally appeared on Engadget at https://www.engadget.com/social-media/xs-handle-marketplace-will-sell-some-rare-usernames-for-millions-of-dollars-224852740.html?src=rss