
Cerebro is an upcoming clusterboard platform launching on Kickstarter, designed for AI, edge computing, and embedded development. It supports a range of compute modules including Raspberry Pi CM4 and CM5, NVIDIA Jetson, and Radxa CM5, providing a modular base for scalable systems. The board can host up to four compute nodes and includes an onboard, […]
Category Archives: Unfiltered RSS
Trump Threatens 100% Tariff On Foreign-Made Films
Donald Trump has announced plans to impose a 100% tariff on all foreign-made films, citing national security concerns and accusing other countries of luring U.S. film production abroad with incentives. PBS reports: “The Movie Industry in America is DYING a very fast death,” he wrote [on his Truth Social platform], complaining that other countries “are offering all sorts of incentives to draw” filmmakers and studios away from the U.S. “This is a concerted effort by other Nations and, therefore, a National Security threat. It is, in addition to everything else, messaging and propaganda!”
It wasn’t immediately clear how any such tariff on international productions could be implemented. It’s common for both large and small films to include production in the U.S. and in other countries. Big-budget movies like the upcoming “Mission: Impossible — The Final Reckoning,” for instance, are shot around the world.
Incentive programs for years have influenced where movies are shot, increasingly driving film production out of California and to other states and countries with favorable tax incentives, like Canada and the United Kingdom. Yet Trump’s tariffs are designed to lead consumers toward American products. And in movie theaters, American-produced movies overwhelming dominate the domestic marketplace. “Other nations have been stealing the movie-making capabilities from the United States,” Trump told reporters at the White House on Sunday night after returning from a weekend in Florida. “If they’re not willing to make a movie inside the United States we should have a tariff on movies that come in.”


Read more of this story at Slashdot.
Man pleads guilty to using malicious AI software to hack Disney employee
A California man has pleaded guilty to hacking an employee of The Walt Disney Company by tricking the person into running a malicious version of a widely used open source AI image generation tool.
Ryan Mitchell Kramer, 25, pleaded guilty to one count of accessing a computer and obtaining information and one count of threatening to damage a protected computer, the US Attorney for the Central District of California said Monday. In a plea agreement, Kramer said he published an app on GitHub for creating AI-generated art. The program contained malicious code that gave access to computers that installed it. Kramer operated using the moniker NullBulge.
Not the ComfyUI you’re looking for
According to researchers at VPNMentor, the program Kramer used was ComfyUI_LLMVISION, which purported to be an extension for the legitimate ComfyUI image generator and had functions added to it for copying passwords, payment card data, and other sensitive information from machines that installed it. The fake extension then sent the data to a Discord server that Kramer operated. To better disguise the malicious code, it was folded into files that used the names OpenAI and Anthropic.
Gears of War is coming to PlayStation for the first time on August 26
Yet another high-profile Xbox franchise is making the leap to PlayStation. While Halo isn’t yet making the transition, Gears of War is about to join the likes of Forza Horizon 5 in crossing the divide. Gears of War: Reloaded, a remaster of the first game in the series from 2006, is coming to PS5, PC (on the Xbox PC app and Steam) and, naturally, Xbox Series X/S on August 26. However, it’s not making its way to Nintendo Switch 2, at least for the time being.
The game costs $40, though it will also be on Game Pass Ultimate and PC Game Pass on day one. Those who bought the digital version of Gears of War: Ultimate Edition before the remaster announcement will get a free upgrade. Game Pass Ultimate subscribers will also be able to play the third-person shooter on Xbox Cloud Gaming.
The Coalition, an Xbox studio that focuses on Gears of War, worked on the remaster with Sumo Interactive and Disbelief. The game includes all of the Gears of War DLC at no extra cost, including a bonus act for the campaign and all multiplayer features. There will be some characters and cosmetic items that you unlock through progression.
As ever, you can play through the campaign with a friend either online or in classic split-screen co-op. There’s cross-play for all platforms with support for up to eight players in the versus multiplayer mode. If you sign in with a Microsoft account (which isn’t required), you can enable cross-progression. So if you pick up Gears of War: Reloaded on PS5 and play the campaign or multiplayer there, you can continue where you left off on a phone or tablet via Xbox Cloud Gaming, for instance.
Along with “platform-specific features,” Gears of War: Reloaded includes support for 4K HDR visuals, framerates of 60 fps in the campaign and 120 fps in multiplayer modes, Dolby Vision, Dolby Atmos and other visual, audio and performance enhancements. Microsoft is also promising that the campaign will have zero loading screens.
The Coalition has another Gears of War project in the pipeline. During last June’s Xbox Games Showcase, Gears of War: E-Day was revealed. Outriders studio People Can Fly is co-developing the game, which does not yet have a release window.
This article originally appeared on Engadget at https://www.engadget.com/gaming/gears-of-war-is-coming-to-playstation-for-the-first-time-on-august-26-000159326.html?src=rss
Heartbreaking video shows deadly risk of skipping measles vaccine
In a hard-to-watch video, a healthy-looking 4-year-old boy lies on a bed as doctors lift his eyelids to watch his big brown eyes erratically swirl and roll backward. His head jerks, and his little limbs weakly twitch and spasm. A small bit of foam pushes past his lips.
The video, captured by neurologists in India and published today in JAMA Neurology, shows what it looks like when the measles virus is allowed to ravage a child’s brain. (The video can be viewed here.)
The boy was never vaccinated and developed a rare complication from measles called subacute sclerosing panencephalitis (SSPE). The condition occurs when the measles virus quietly sneaks into the central nervous system. It often lurks for years after an initial infection before it begins wreaking havoc, triggering damaging inflammation, destroying neurons, and causing brain lesions.
Waymo Plans To Double Robotaxi Production At Arizona Plant By End of 2026
Waymo and Magna International plan to double production of Waymo’s robotaxis at their Mesa, Arizona facility by the end of 2026, aiming to assemble over 2,000 Jaguar I-PACE vehicles and eventually tens of thousands annually, including next-gen models. CNBC reports: The “Waymo Driver Integration Plant,” a 239,000 square foot facility outside of Phoenix, will assemble more than 2,000 Jaguar I-PACE robotaxis, the Alphabet company said in a statement. Waymo will add those self-driving vehicles to its existing fleet that already includes around 1,500 robotaxis. The plant will be “capable of building tens of thousands of fully autonomous Waymo vehicles per year,” when it is fully built out, Waymo said. The company also said it plans to build its more advanced Geely Zeekr RT robotaxis that feature its “6th-generation Waymo Driver” technology later this year at the plant.
Waymo and Magna opened the Mesa plant in October, Forbes reported Monday. The Alphabet-owned company started its commercial robotaxi service in Phoenix in 2020 and now calls the area its domestic manufacturing home. Already, Waymo is conducting 250,000 paid, driverless rides per week across its service areas in Austin, the San Francisco Bay area, Los Angeles and Phoenix, and the company is planning to begin serving the Atlanta; Miami; and Washington, D.C., markets in 2026.


Read more of this story at Slashdot.
Here’s Why Microsoft Is Ditching Passwords for New Accounts
Microsoft is taking another big step toward eliminating passwords with a “passwordless by default” setting for new accounts. New users will be prompted to set up passkeys when creating their Microsoft logins, leaving passwords behind.
The company has had passwordless sign-in options for Windows 11 and Microsoft accounts for several years, and in 2024 expanded passkey support across Windows, Android, and iOS. This is a big change, but not one without reason. In fact, it may make Microsoft accounts more secure, and render many scammers’ phishing tactics obsolete.
The benefits of passkeys
Passkeys are not only easier to use than passwords combined with other forms of two-factor authentication (2FA) like SMS codes and authenticator apps—they’re also more secure. Passkeys are cryptographically generated, stored on your device, and encrypted by default, making them immune to phishing and other cyberattacks. Without access to your device, bad actors can’t hack your accounts.
Instead of creating a complex password, which you then have to securely store (or remember), a device-based passkey allows you to quickly log into your accounts using biometrics like your face or fingerprint, or credentials like your PIN or password.
Passkeys are the default on new Microsoft accounts
Going forward, new Microsoft accounts will be “passwordless by default.” When you sign up for the first time, you’ll be asked to enter your email address and verify it with a one-time code—without any need to create and save a password. Once you enter the one-time code, you’ll be prompted to add a passkey using your face, fingerprint, or PIN. The next time you log in, you’ll do so with with your chosen passkey.
You can choose to skip passkey setup and return to it later (tap Skip for now on the pop-up). Microsoft will set the “best available” passwordless sign-in method for your account as the default, which could be a one-time code or an enabled passkey.
Existing Microsoft users can manage passkeys and delete passwords in the Settings app under Accounts > Passkeys. According to Microsoft’s announcement detailing the change, the company aims to eventually remove password support completely.
Raw Dating App Left User Data Unprotected, Exposing Private Details For All To See
Data breaches, whether due to the nefarious activities of hackers or inadequate security measures, are a major concern due to the harm they can cause to affected users. In this latest breach, a report claims that the dating app Raw left user data unprotected, exposing private details for all to see.
Raw was launched in 2023. The app encourages
How To Remove Unused Flatpak Apps To Free Up Disk Space In Linux
This tutorial explains how Flatpak consumes disk space and the effective commands and techniques to remove unused flatpak apps to reclaim that space.
[$] Injecting speculation barriers into BPF programs
The disclosure of the Spectre
class of hardware vulnerabilities created a lot of pain for kernel
developers (and many others). That pain was especially acutely felt in the
BPF community. While an attacker might have to painfully search the kernel
code base for exploitable code, an attacker using BPF can simply write and
load their own speculation gadgets, which is a much more efficient way of
operating. The BPF community reacted by, among other things, disallowing
the loading of programs that may include speculation gadgets. Luis
Gerhorst would like to change that situation with this patch
series that takes a more direct approach to the problem.
“Knights of the Roundabout” Route Details
Google is reportedly getting back into film and TV with a tech-friendly production initiative
Google plans to start producing its own films and television shows via a “production initiative” called 100 Zeros, Business Insider reports. The company is working with Range Media Partners, a talent management and production company, to identify projects that appeal to younger audiences and could “promote a positive view of [Google’s] products.”
Besides the obvious opportunity for product placement, the larger goal of the initiative is to fund projects that have a positive view of technology, and to get the creative industry interested in using Google’s products. Immersive View, Google’s 3D aerial scans featured in Google Maps, could be a tool it pushes, Business Insider writes. Veo 2, Google’s AI video model, seems like a natural candidate, too. Whichever way the company goes, 100 Zeros already has a movie under its belt: The initiative reportedly helped pay for the marketing for the indie horror movie Cuckoo.
Engadget has reached out to Google to confirm the details of Business Insider‘s report and share more information about 100 Zeros. We’ll update this article if we hear back.
Google has some experience in the entertainment industry through its defunct YouTube Red Originals program. When YouTube first launched YouTube Red, the subscription service now called YouTube Premium, it did so alongside a slate of original content featuring notable YouTube talent. The program produced a number of shows and films, including popular series that found homes on other streaming services, like Cobra Kai, but never became a true competitor to Netflix.
100 Zeros doesn’t sound like another YouTube Red, and instead, a more traditional play to make original content and sell it to other distributors — just with a potentially Google-y flavor.
This article originally appeared on Engadget at https://www.engadget.com/entertainment/tv-movies/google-is-reportedly-getting-back-into-film-and-tv-with-a-tech-friendly-production-initiative-185138762.html?src=rss
Half-Life 3 Hype Intensifies On Report Of A Fully Playable Build And Imminent Launch
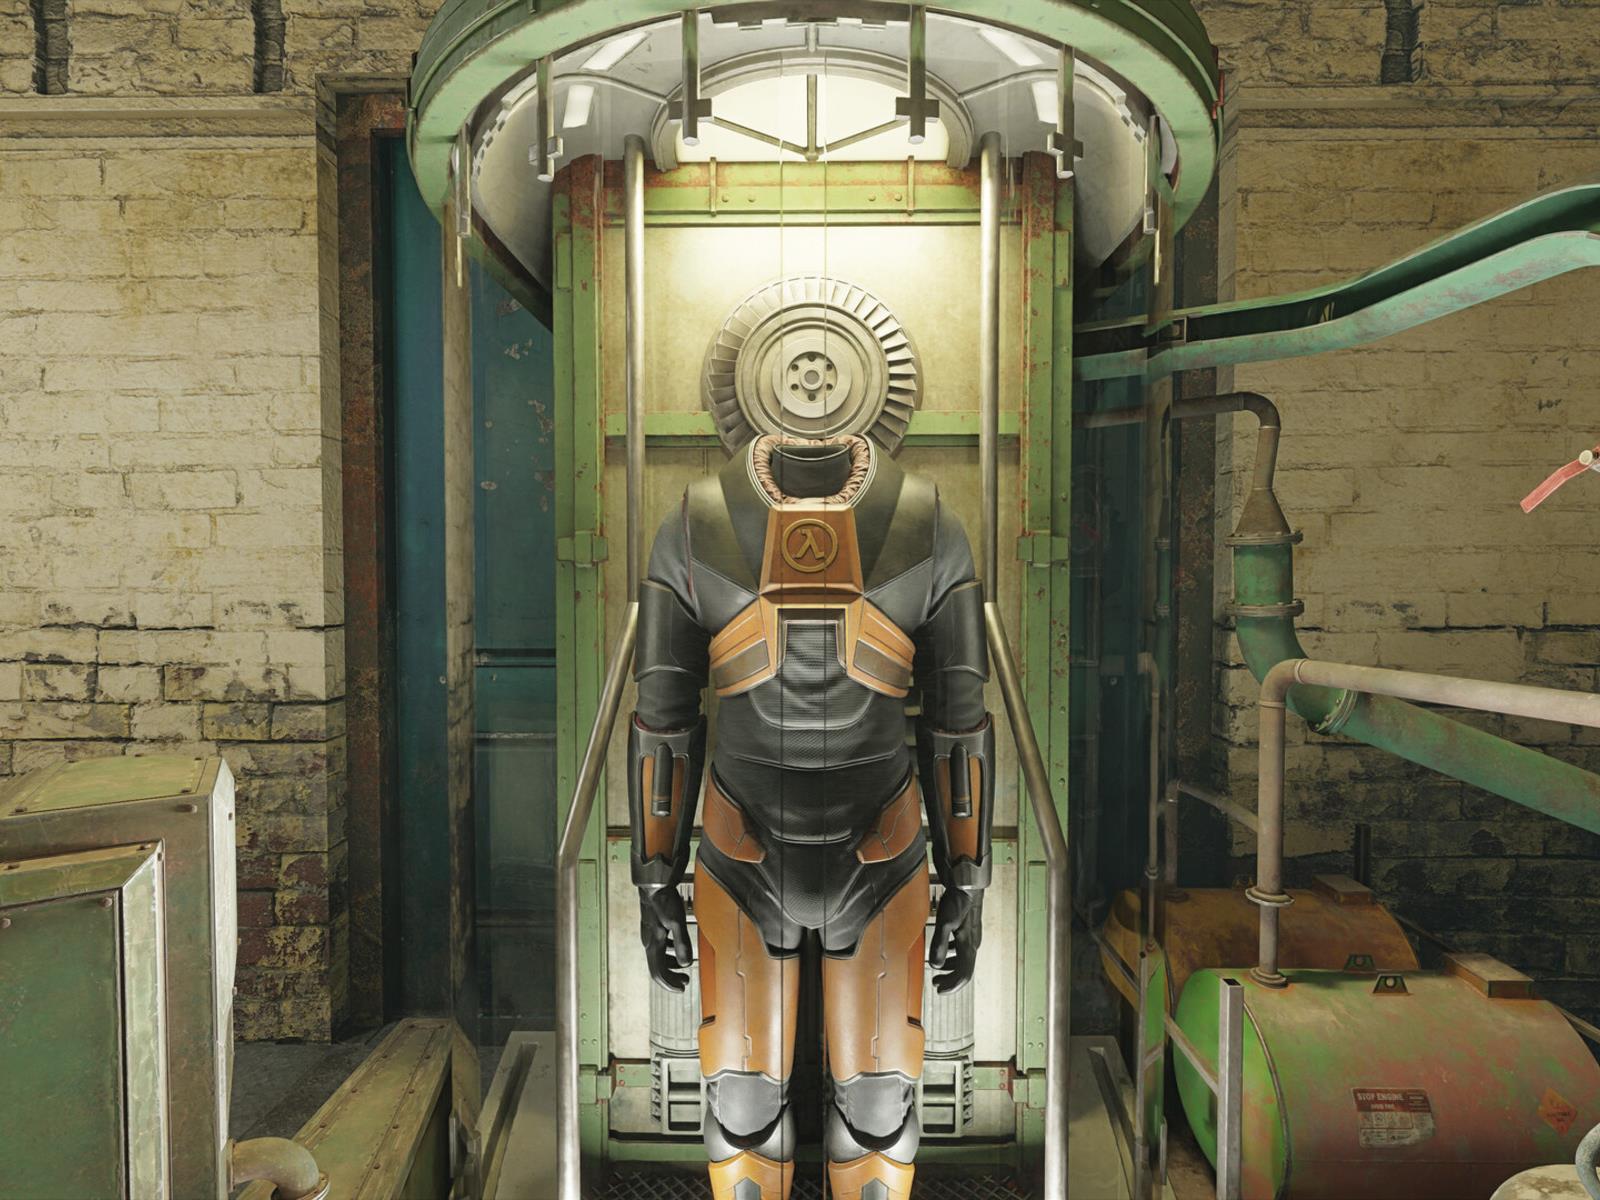
The dream of finally playing Half-Life 3 remains alive and well. Even though fans have gotten Black Mesa, which modernizes the original game, and have a gorgeous remasteed Half-Life 2 in the pipeline, there’s still a yearning for a new adventure featuring Gordon Freeman. If an insider is to be believed, this might come to fruition sooner rather
TeleMessage, a Signal clone the Trump administration uses, has been hacked
A hacker has exploited a vulnerability in TeleMessage to breach the service and steal data, according to reporting by 404 Media. TeleMessage is an Israeli company that provides modded versions of encrypted messaging apps like Signal and Telegram.
It was revealed last week that former US National Security Adviser Mike Waltz used TeleMessage’s modified version of Signal to archive messages. Today’s report indicated the presence of other high-ranking government officials in archived chats on the app, including Marco Rubio, Tulsi Gabbard and Vice President JD Vance.
The unnamed hacker was able to access archived chats, but it doesn’t look like they got into any of Waltz’s conversations. The hack does, however, prove that the app’s message archiving service is not end-to-end encrypted.
The hacker also accessed contact information of government officials, login credentials for TeleMessage and data pertaining to the US Customs and Border Protection agency. Some businesses who use the service, like Coinbase and Scotiabank, were also hacked. 404 Media spoke to the anonymous hacker, who said the whole thing only “took about 15-20 minutes” and that it “wasn’t much effort at all.” TeleMessage’s parent company Smarsh has yet to comment on the matter.
All of this happened after Waltz accidentally revealed he used TeleMessage during a cabinet meeting last week. This led people to question what kind of information was being shared on the app and how it was being secured. Now we know it wasn’t secured all that well.
Of course, it’s only been a few weeks since Signalgate, in which it was revealed that top US officials were using the messaging app Signal to discuss active combat operations. Prior to the Trump administration, government officials typically avoided consumer-grade messaging apps to hash out military plans. Instead, they used Sensitive Compartmented Information Facilities (SCIFs) and in-house encrypted communication channels.
This article originally appeared on Engadget at https://www.engadget.com/big-tech/telemessage-a-signal-clone-the-trump-administration-uses-has-been-hacked-183606147.html?src=rss
Redox OS Seeing More Software Porting, Many Internal Improvements
The open-source, Rust-based Redox OS operating system has published their April 2025 status report to outline interesting changes made over the past several weeks to this innovative project…
Open Home Foundation Marks Second Year with Structural Changes and Home Assistant 2025.4 Update
April 2025 marked the start of the Open Home Foundation’s second year. Since its launch at the State of the Open Home 2024 event, the Foundation has grown rapidly, gaining broad community and industry support. Last month’s 2025 event highlighted key milestones from its first year and outlined plans for continued development. Over the past […]
Microsoft Cracks Down On Bulk Email With Strict New Outlook Rules
BrianFagioli writes: Microsoft has officially begun rejecting high-volume emails that don’t meet its new authentication rules.
Here’s the deal. If you send more than 5,000 messages per day to Outlook.com addresses (including hotmail.com and live.com) and you’re not properly set up with SPF, DKIM, and DMARC, your emails may never arrive.


Read more of this story at Slashdot.
The US Government’s Signal Situation Just Got Worse
If you’re looking to send personal messages securely, Signal is a great option. If you’re a government official discussing classified information? Not so much.
So is the case with Trump administration officials: Last month, we learned that highly sensitive war plans were being discussed in Signal group chats, after Jeffrey Goldberg, editor-in-chief of The Atlantic, was accidentally added to the conversation by then-U.S. National Security Advisor Mike Waltz. (Trump has since fired Waltz—and then nominated him to be U.N. ambassador.)
‘Signalgate’ continues
There are many reasons why the administration’s “Signal strategy” is problematic, but the issues didn’t end there. On Thursday, Reuters posted a photograph of Mike Waltz during a cabinet meeting at the White House. While there are plenty of important people in the photograph to pay attention to, 404 Media zeroed in on Waltz—specifically, his iPhone. The outlet spotted that Waltz had what appeared to be a thread opened with officials like Tulsi Gabbard (Director of National Intelligence), Marco Rubio (Secretary of State), and JD Vance (Vice President), with the PIN verification message that Signal will routinely send to users to keep their credentials fresh in their minds.
However, 404 Media spotted that this wasn’t Signal’s usual PIN verification pop-up: The message says “TM SGNL PIN,” which is the PIN verification screen for TeleMessage, a Signal “clone” that advertises itself as a way to archive your Signal messages. While the app claims it does not break Signal’s secure messaging system to archive messages, 404 Media reports that the service as advertised has many security vulnerabilities.
It didn’t take long for those vulnerabilities to manifest in disaster, either. On Sunday, 404 Media reported a hacker broke into TeleMessage’s networks and stole customer data. While the hacker didn’t take everything, they did obtain some DMs and group chats, in addition to data of modified versions of other chat apps, like WhatsApp, Telegram, and WeChat, all in about 15 to 20 minutes of hacking. 404 Media says the hacker did not access Waltz’ chats or the conversations of any cabinet members, but they did access government officials’ names and contact information, credentials to log into TeleMessage’s backend panel (the tool that lets TeleMessage admins manage the service), as well as information that points to which agencies might use TeleMessage.
Some of the stolen messages appeared to show a discussion about an ongoing effort to whip up votes in support of a cryptocurrency bill. One text read, “Just spoke to a D staffer on the senate side – 2 cosponsors (Alsobrooks and gillibrand) did not sign the opposition letter so they think the bill still has a good chance of passage the senate with 5 more Ds supporting it.” The hack didn’t expose classified information, but it did reveal political conversations that the senders likely never intended to be printed in the press.
Why is TeleMessage insecure?
To understand why TeleMessage is not a secure service—and why it is unbelievable that a government agency would rely on it for classified conversations—you need to understand what makes Signal secure.
Signal chats are end-to-end encrypted. That means when you talk to someone over the app, only you and the recipient can access the conversation. When you send a message, that text is encrypted in transit, and decrypted when it reaches the other user’s device. If someone were to intercept the message in transit, it would look like a scramble of code—only the devices of the people in the chat can decrypt the message and return it to a readable form.
Because of this setup, not even Signal can access your messages. No authority can compel Signal to release your messages, since the company itself doesn’t have access to the only thing that can decrypt the messages: your device. Even if someone hacked Signal’s database, they’d be out of luck.
TeleMessage, on the other hand, breaks that security chain. In order to archive those messages, TeleMessage must first intercept them as plain-text and store them. While the company says that they do so while maintaining security, the fact that this hacker was able to obtain DMs proves end-to-end encryption is broken. The stolen information was taken from data captured for “debugging purposes,” an unintended leak of decrypted data in TeleMessage’s security chain. It doesn’t matter if the service stores all messages in an encrypted archive: The company handles decrypted data in insecure ways, which leaves it open for hackers to access.
Even before the hack, 404 Media was skeptical of the service’s security, since they advertised archiving these “end-to-end encrypted” messages in Gmail, a platform that is infamously not end-to-end encrypted. (Though TeleMessage said the Gmail aspect was just for a “demo.”) The outlet also highlights how Signal does not guarantee the privacy and security of unofficial versions of their app.
Signal is great for personal use—not classified information
Signal—and other end-to-end encrypted services like it—are great for personal security. Your messages cannot be accessed by anyone without physical access to the trusted devices involved, which goes a long way toward protecting your digital privacy.
But encryption isn’t the only security concern here. There are still plenty of vulnerabilities and weak points when it comes to digital communication of any kind—end-to-end encryption included.
Hackers know that these messages can only be decrypted by the devices involved. So, a great way to break that security is to hack the devices themselves. Hackers use malware like “Pegasus” to silently stow away onto a target’s device and access sensitive data—encrypted data included.
Hackers routinely target high-profile individuals with this type of malware, so much so that Apple issues a regular warning to affected users. Waltz is no exception: In the view of Mike Casey, the former director of National Counterintelligence and Center, there’s a “zero percent chance that someone hasn’t tried to install Pegasus or some other spyware on [Mike Waltz’s] phone…he is one of the top five, probably, most targeted people in the world for espionage.”
Of course, that’s just the concern with your own personal device. You also have to worry about the other end of the conversation. If you’re chatting with someone over an encrypted chat app, and their phone is compromised, it doesn’t matter how secure you are: Your messages are vulnerable. They don’t even need to be hacked: They could leave their phone unlocked for anyone to pick up and access. And if you’re talking in group chats—like Trump administration officials have been—the security implications only multiply.
There is risk involved in all digital communication: It’s up to you to decide what risk level the data you’re transferring is worth. For most personal conversations, you’re probably just fine sticking with an encrypted service like Signal. If you’re discussing details that could put lives at risk, however, it might be best to keep it in the SCIF.
Destiny 2: Year Of The Prophecy Release Date, $275 Bundle And More Revealed In Major Leak
Bungie is working towards the release of Marathon, which the company hopes will be its next big blockbuster, it’s still supporting Destiny 2 with new content updates despite a shrinking team. Unfortunately for the studio, it’s big reveal event for Destiny’s The Edge of Fate expansion, along with the details of an upcoming collector’s edition,
RIP Skype (2003–2025), survived by multiple versions of Microsoft Teams
Today is the day: Microsoft has formally shuttered the Skype app and service after announcing in February that Skype was being axed in favor of Microsoft Teams, the company’s Slack competitor.
The Skype apps have all been advertising the end of the service and pointing users to Teams for weeks now. As of today, if you open the app or navigate to the Skype site, you’ll be directed to use Teams instead. The last active vestige of Skype is the Skype Dial Pad, which Skype subscribers and members with Skype Credits can still use to make calls to traditional telephone numbers (the Dial Pad is also incorporated into Microsoft Teams Free).
It’s an unceremonious end for an app that was once synonymous with video calls. Microsoft originally bought Skype for $8.5 billion in 2011; it was also owned by eBay from 2005 to 2009 and by a group of venture capital firms between 2009 and 2011. Ironically, Microsoft bought the app to replace its own first-party communication client at the time, Windows Live Messenger (which itself had grown out of the old MSN Messenger).